
API-SPY-API-PROBE
A powerful directory brute-force tool that's tailored for recursive/multiplex operations, API discovery and enumeration, JS file scraping, and lists…

A powerful directory brute-force tool that's tailored for recursive/multiplex operations, API discovery and enumeration, JS file scraping, and lists…

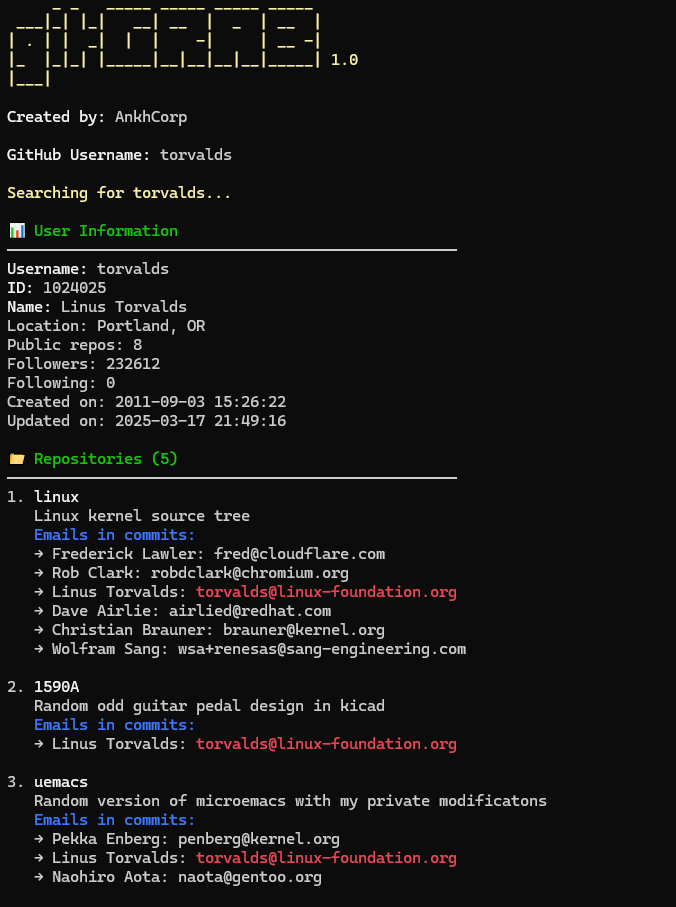
This tool is designed to interact with the GitHub API and retrieve specific user details, repository information, and commit emails for a given user.

Multi-threaded scanner for detecting exposed Swagger/OpenAPI endpoints across web domains and subdomains, with automatic XSS detection, PoC…

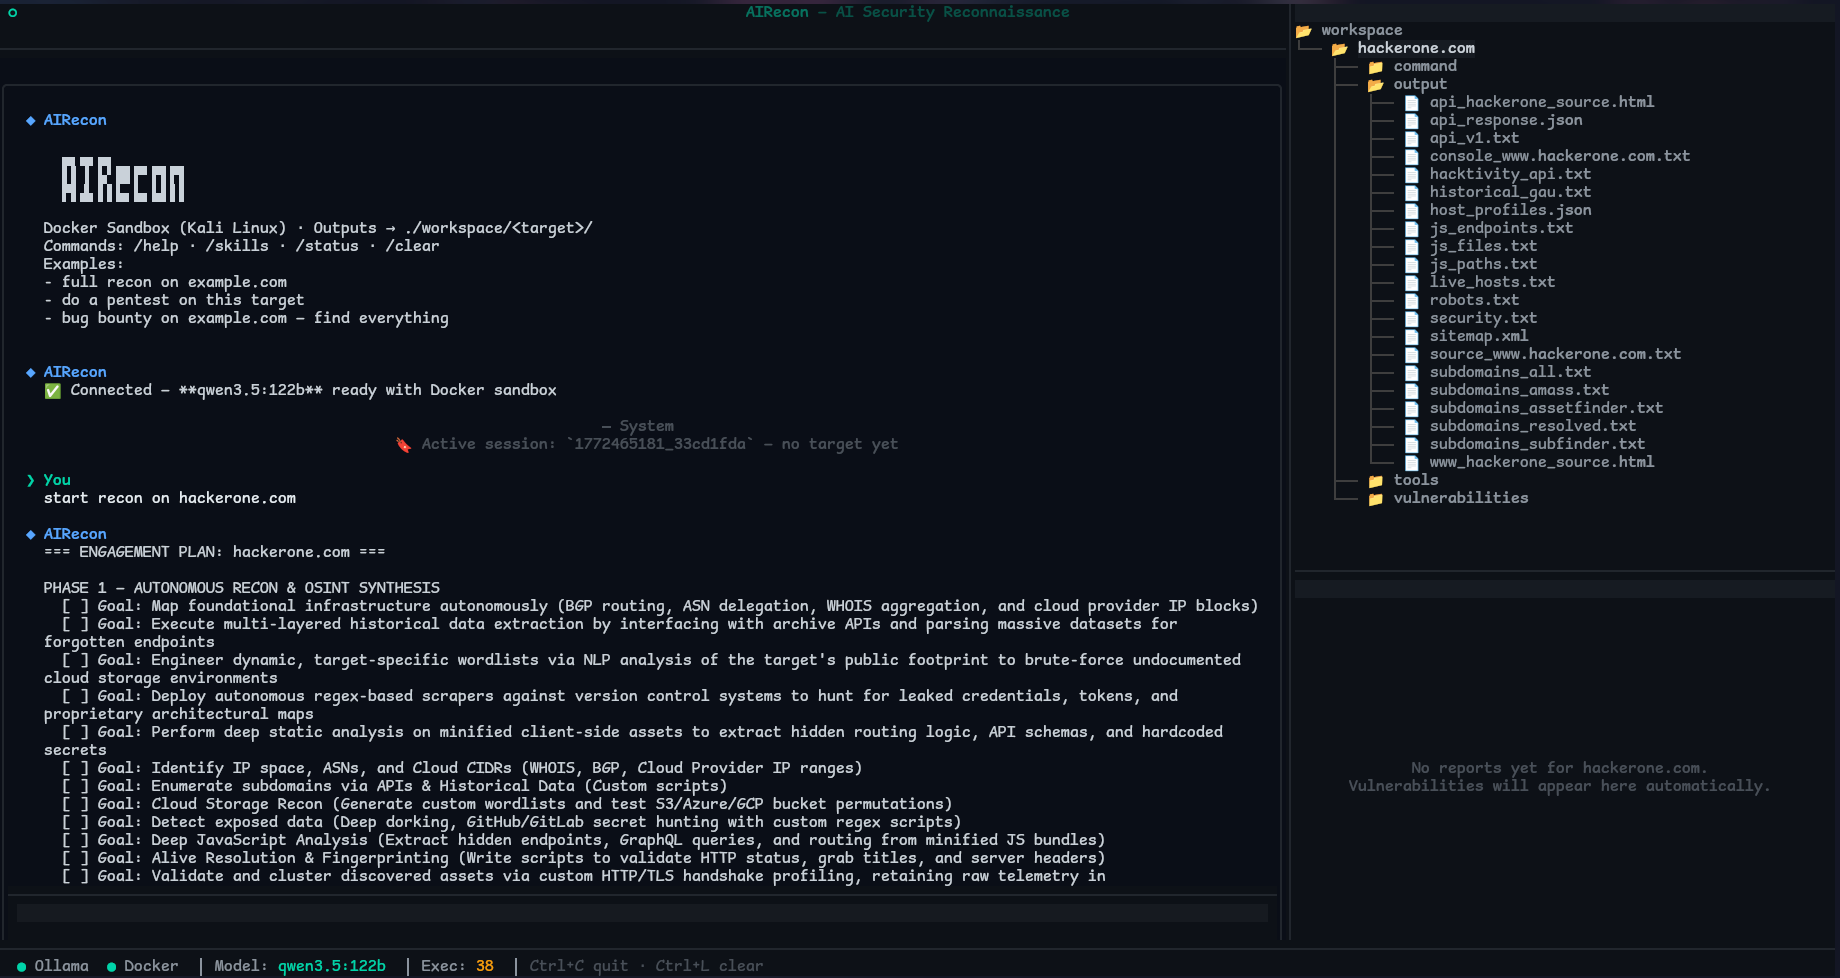
AIRecon is an autonomous cybersecurity agent that combines a self-hosted Large Language Model (Ollama) with a Kali Linux Docker sandbox and a Textual…

jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…

Concurrent CLI tool for discovering secrets, API keys, and links in JavaScript files during web reconnaissance, with custom regex pattern support and…

Passive subdomain discovery tool that aggregates results from multiple online sources via CLI, supporting stdin/stdout, JSONL output, and API key…

Osinton Its an open-source project running using SERP API and ollama mistral

Incredibly fast crawler designed for OSINT.

reconFTW is a tool designed to perform automated recon on a target domain by running the best set of tools to perform scanning and finding out…

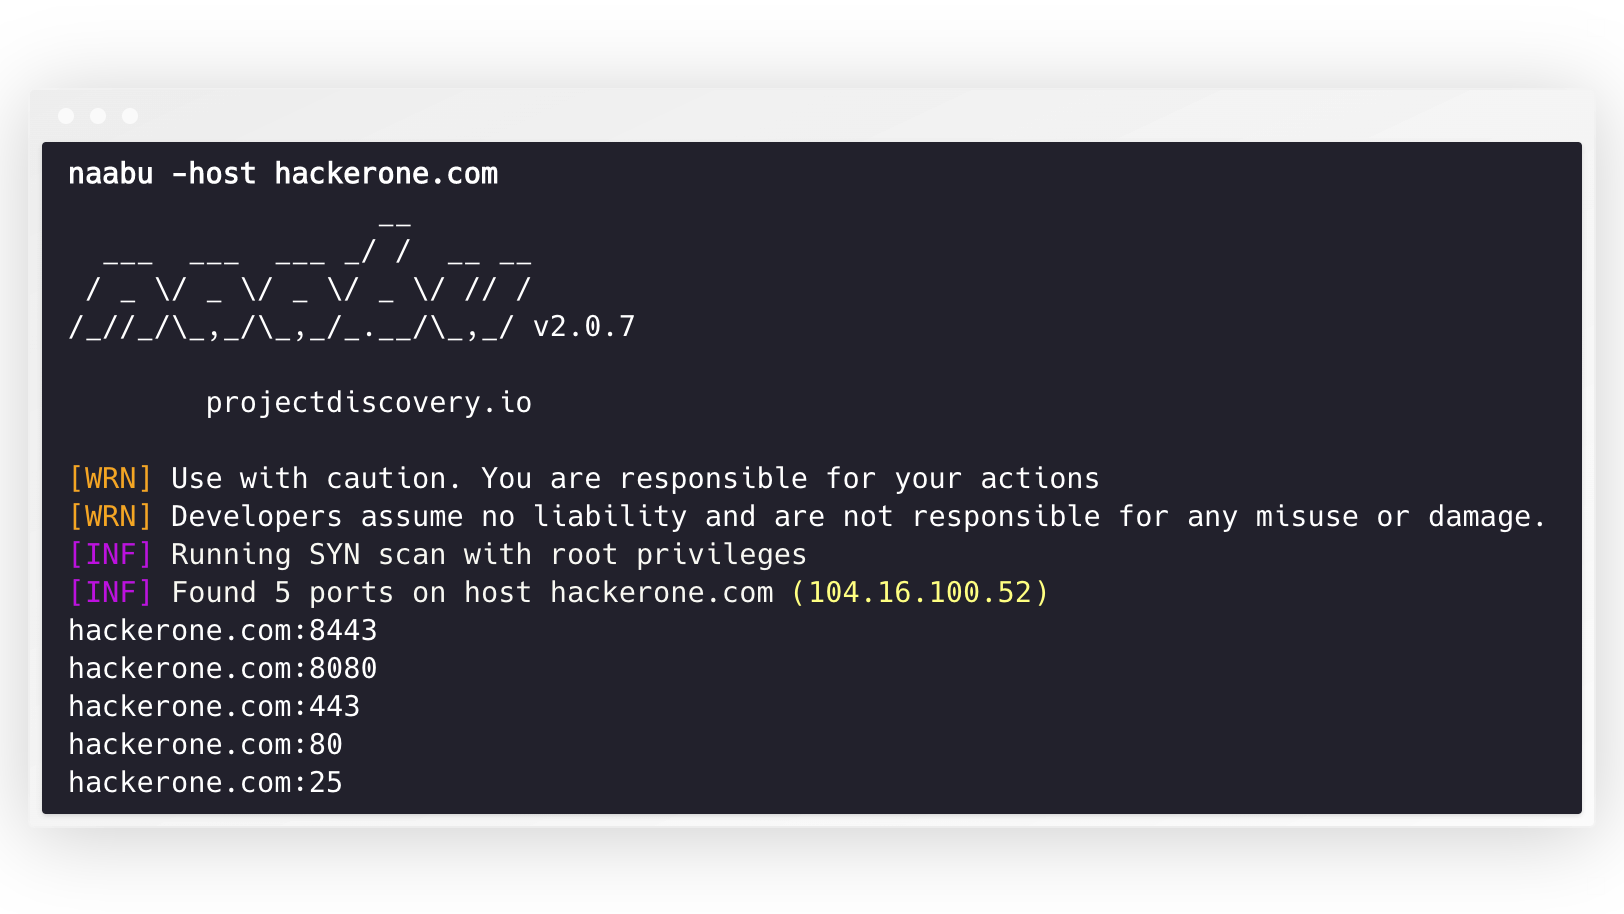
A fast port scanner written in go with a focus on reliability and simplicity. Designed to be used in combination with other tools for attack surface…

HikvisionExploiter is a Python-based utility designed to automate exploitation and directory accessibility checks on Hikvision network cameras…

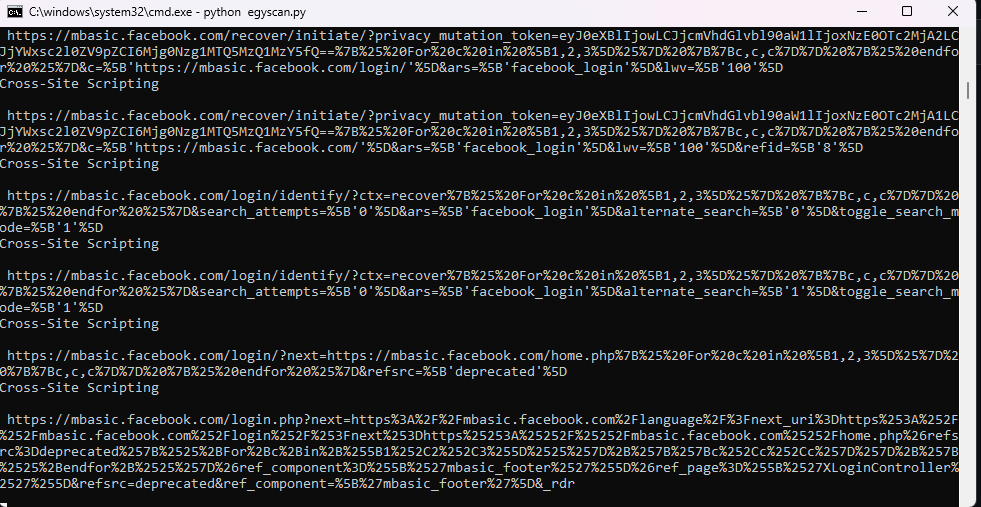
Egyscan The Best web vulnerability scanner; it's a multifaceted security powerhouse designed to fortify your web applications against malicious…

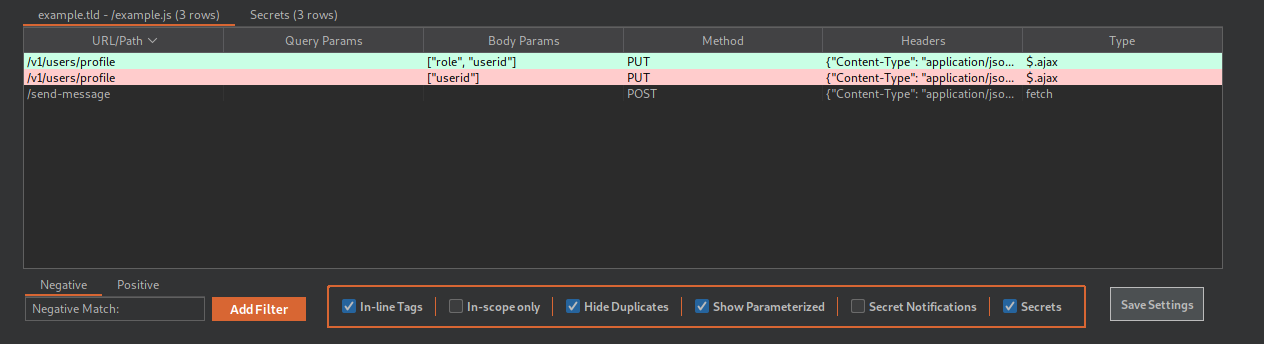
jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice

EvilMist is a collection of scripts and utilities designed to support cloud penetration testing & red teaming. The toolkit helps identify…

A tool designed to exploit bad implementations of decryption mechanisms in Laravel applications.

Moxy is an open-source DAST tool designed for modern web application security testing. It provides an easy-to-use interface with agentic capabilities…

PhantomRecon is a CLI-based, modular, agent-driven red team automation tool designed to demonstrate autonomous offensive security workflows powered…