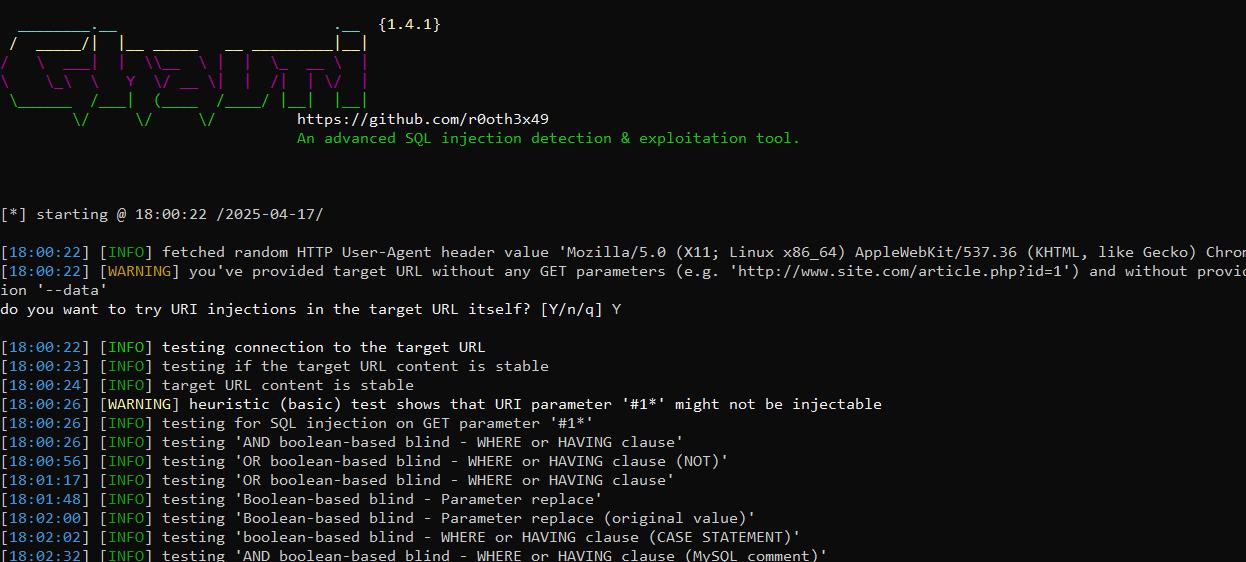
Geoserver-CVE-2023-25157

Python-based exploit and detector for GeoServer SQL injection vulnerability CVE-2023-25157, enabling automated target scanning and exploitation.

Python-based exploit and detector for GeoServer SQL injection vulnerability CVE-2023-25157, enabling automated target scanning and exploitation.

A C# MS SQL toolkit designed for offensive reconnaissance and post-exploitation.

A C# MS SQL toolkit designed for offensive reconnaissance and post-exploitation.

👾 CVE-2026-58048 – cPanel Root SQL Execution Toolkit (CVSS 9.4) | Full Red/Blue Team Toolkit suite for unpatched cPanel & WHM 11.x. 2 tools: Safe…

Multi-threaded time-based blind SQL injection exploit for CVE-2026-14762 targeting Hotel & Tourism Reservation 1.0. Enumerates databases, tables,…

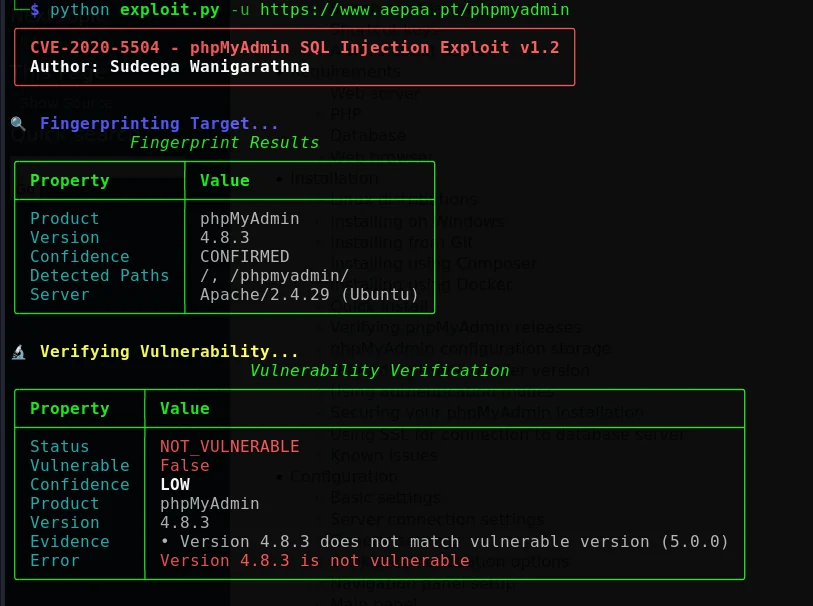
Authorized SQL injection exploitation framework for CVE-2020-5504 in phpMyAdmin, featuring automated database enumeration, blind injection, proxy…

Semi-passive scanner that detects Drupal installations vulnerable to CVE-2026-9082 (PostgreSQL SQL injection) via fingerprinting, version detection,…

This tool extracts Credit card numbers, NTLM(DCE-RPC, HTTP, SQL, LDAP, etc), Kerberos (AS-REQ Pre-Auth etype 23), HTTP Basic, SNMP, POP, SMTP, FTP,…

Barcha is your Swiss‑Army knife for SQL Injection reconnaissance 🔍. Written in Go, it automates: Shodan enumeration of SSL hosts 🕵️♂️ Liveness &…

Joomla 3.7 SQL injection (CVE-2017-8917)

CVE-2024-3495 Country State City Dropdown CF7 <= 2.7.2 - Unauthenticated SQL Injection

Scans host lists for GeoServer endpoints vulnerable to CVE-2023-25157 SQL injection, verifies exposed paths with keyword checks, and logs confirmed…

Python 3 PoC scanner and exploit for CVE-2026-88854, an unauthenticated SQL injection in OrdaSoft Joomla Gallery, with mass check and EXTRACTVALUE…

Home-lab penetration test report of Metasploitable3 covering Nmap recon, Drupalgeddon RCE, SQL injection, SSH credential reuse, sudo privilege…

Python checker for CVE-2026-48842, a pre-auth SQL injection in Roundcube Webmail's virtuser_query plugin. Detects version, plugin path, and verifies…

PoC detector & safe validator for the WP2Shell WordPress vulnerability chain: CVE-2026-63030 (REST batch-route confusion) + CVE-2026-60137…

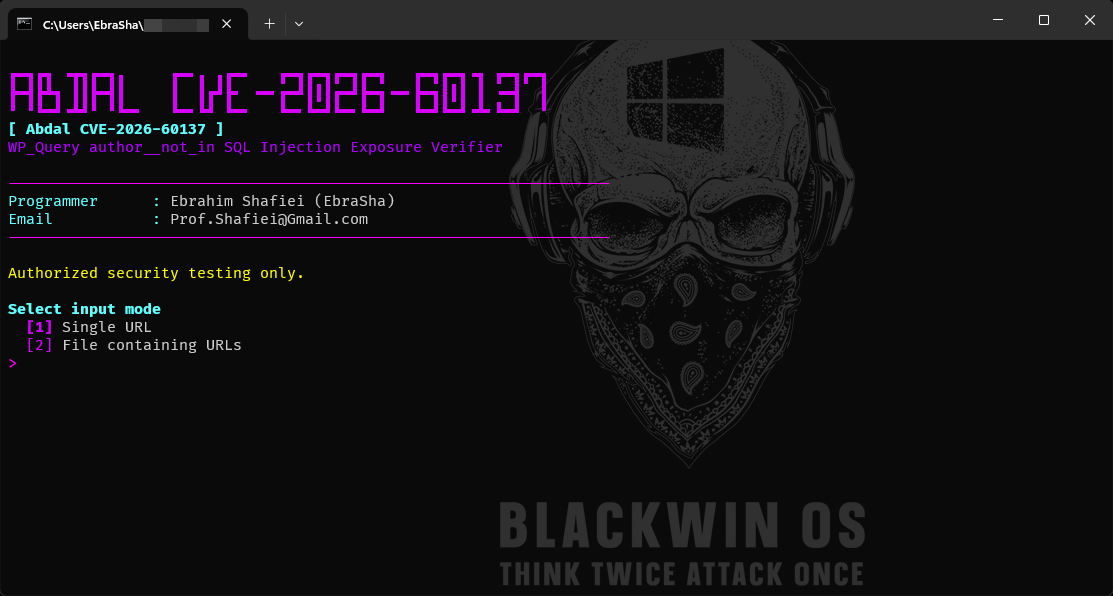
Abdal CVE-2026-60137 is an advanced WordPress security scanner for identifying systems potentially affected by the CVE-2026-60137 SQL Injection…

Modular WordPress pre-auth exploit framework chaining SQL injection and authentication bypass to deliver remote code execution, interactive shells,…