Joomla-CMS-Full-Lifecycle-Pentest

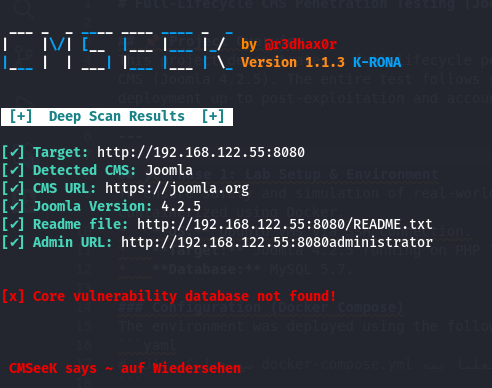
A comprehensive full-lifecycle penetration testing project on Joomla 4.2.5 exploiting CVE-2023-23752 inside a Dockerized lab environment

A comprehensive full-lifecycle penetration testing project on Joomla 4.2.5 exploiting CVE-2023-23752 inside a Dockerized lab environment

Open Source Intelligence gathering tool aimed at reducing the time spent harvesting information from open sources.

Public PoC + Scanner and research for CVE-2025-68613: Critical RCE in n8n Workflow Automation via Expression Injection (CVSS 10.0). Includes…

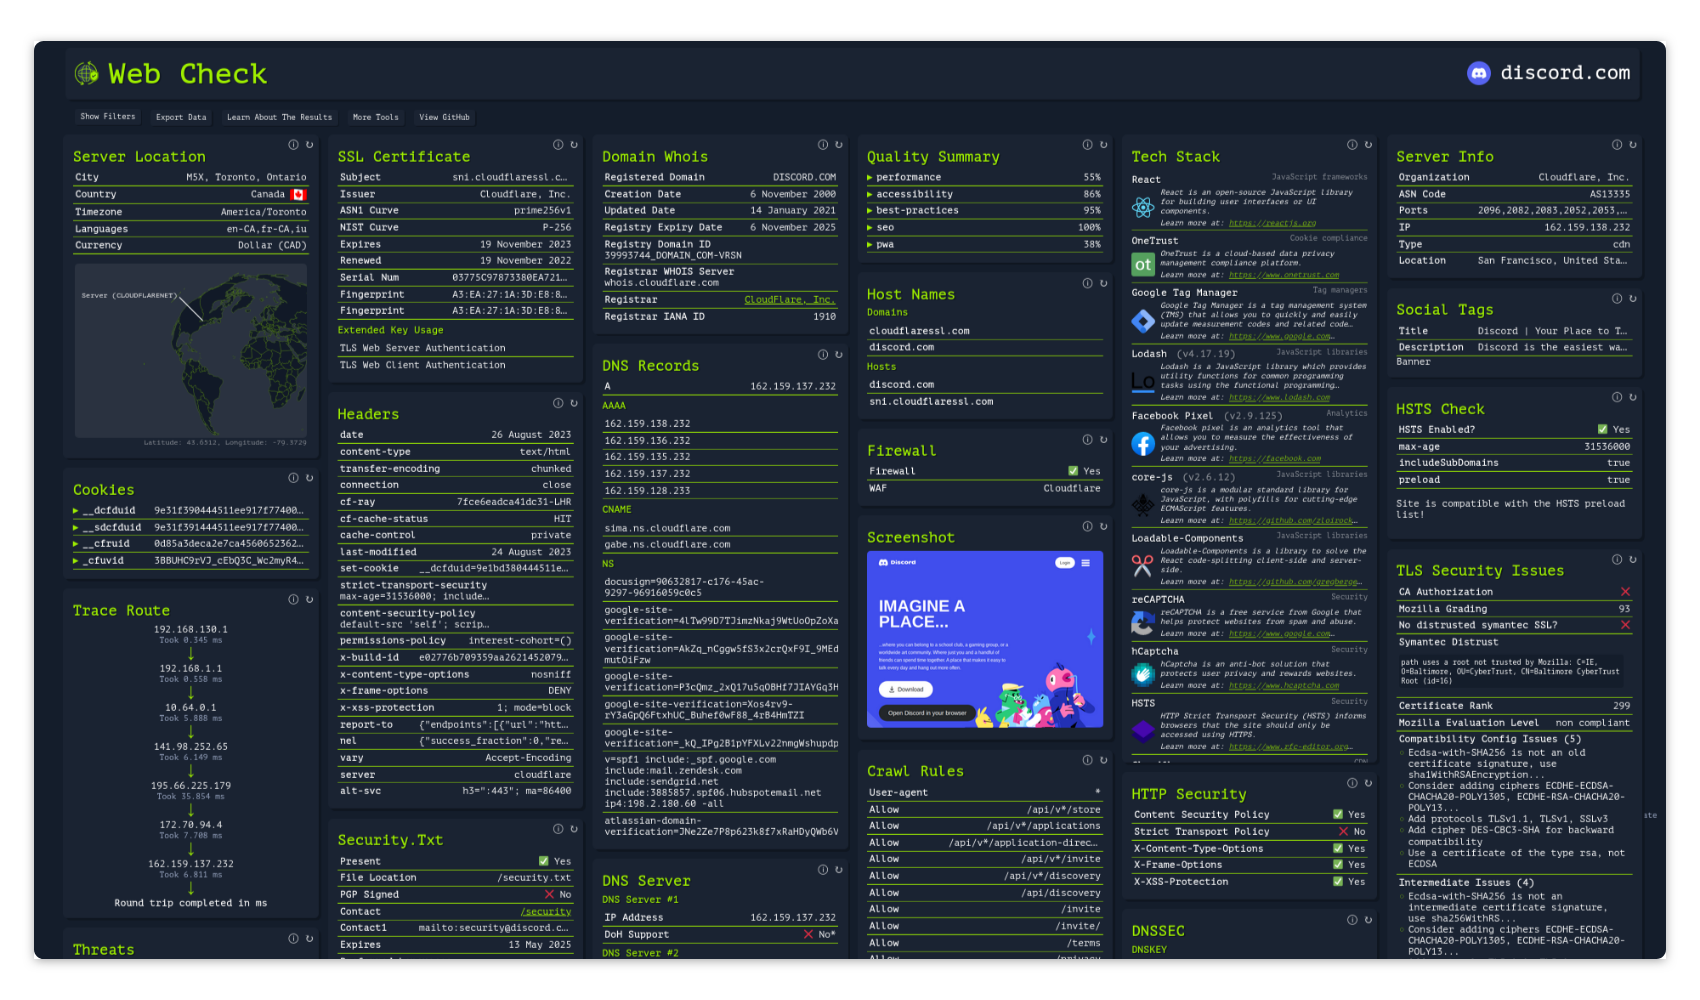
🕵️♂️ All-in-one OSINT tool for analysing any website

🕷️ A `.git` folder exploiting tool that is able to restore the entire Git repository, including stash, common branches and common tags.

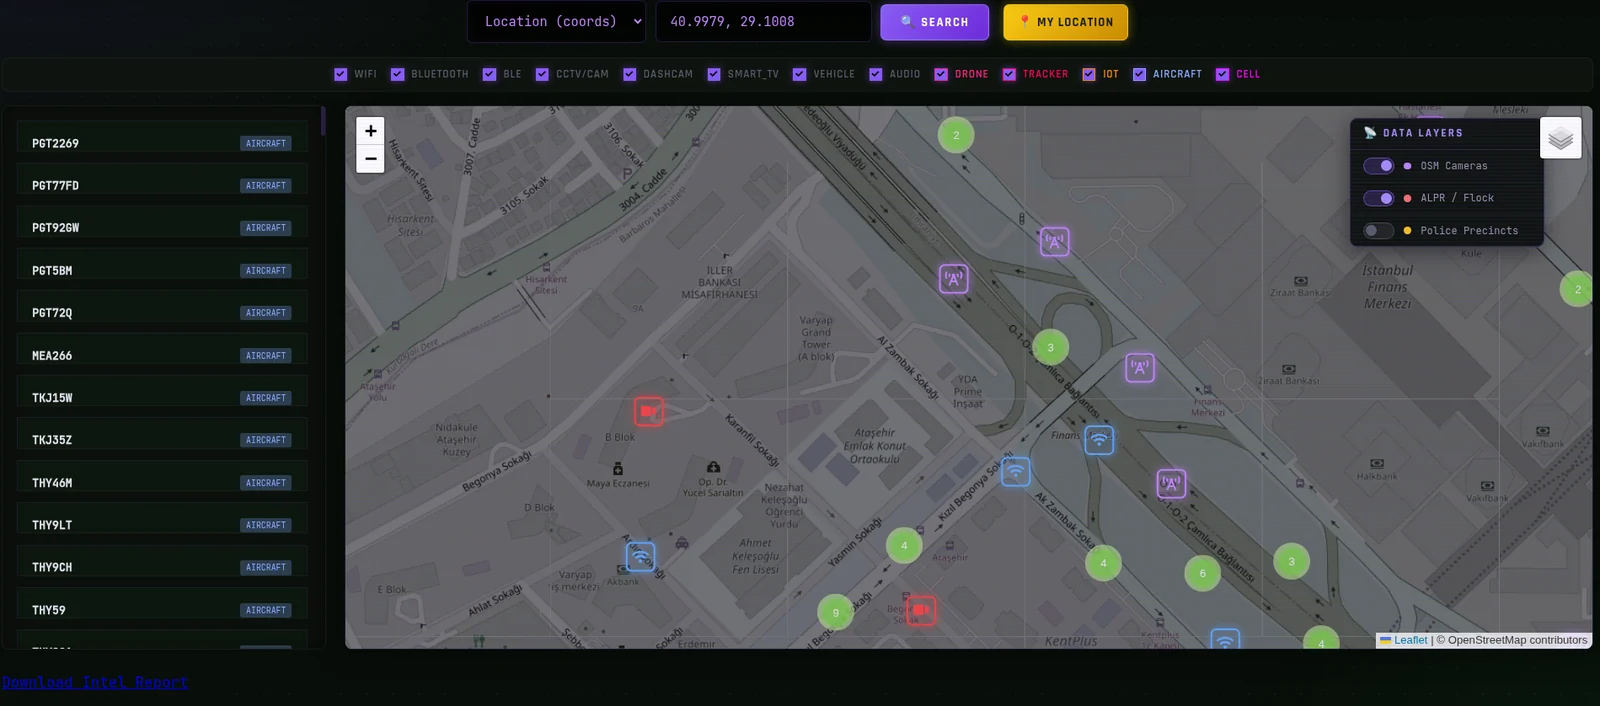
All-source intelligence fusion dashboard — WiFi, cellular, CCTV, ADS-B, orbital & SDR feeds unified into a single tactical map. Security research…

ES File Explorer Open Port Vulnerability - CVE-2019-6447

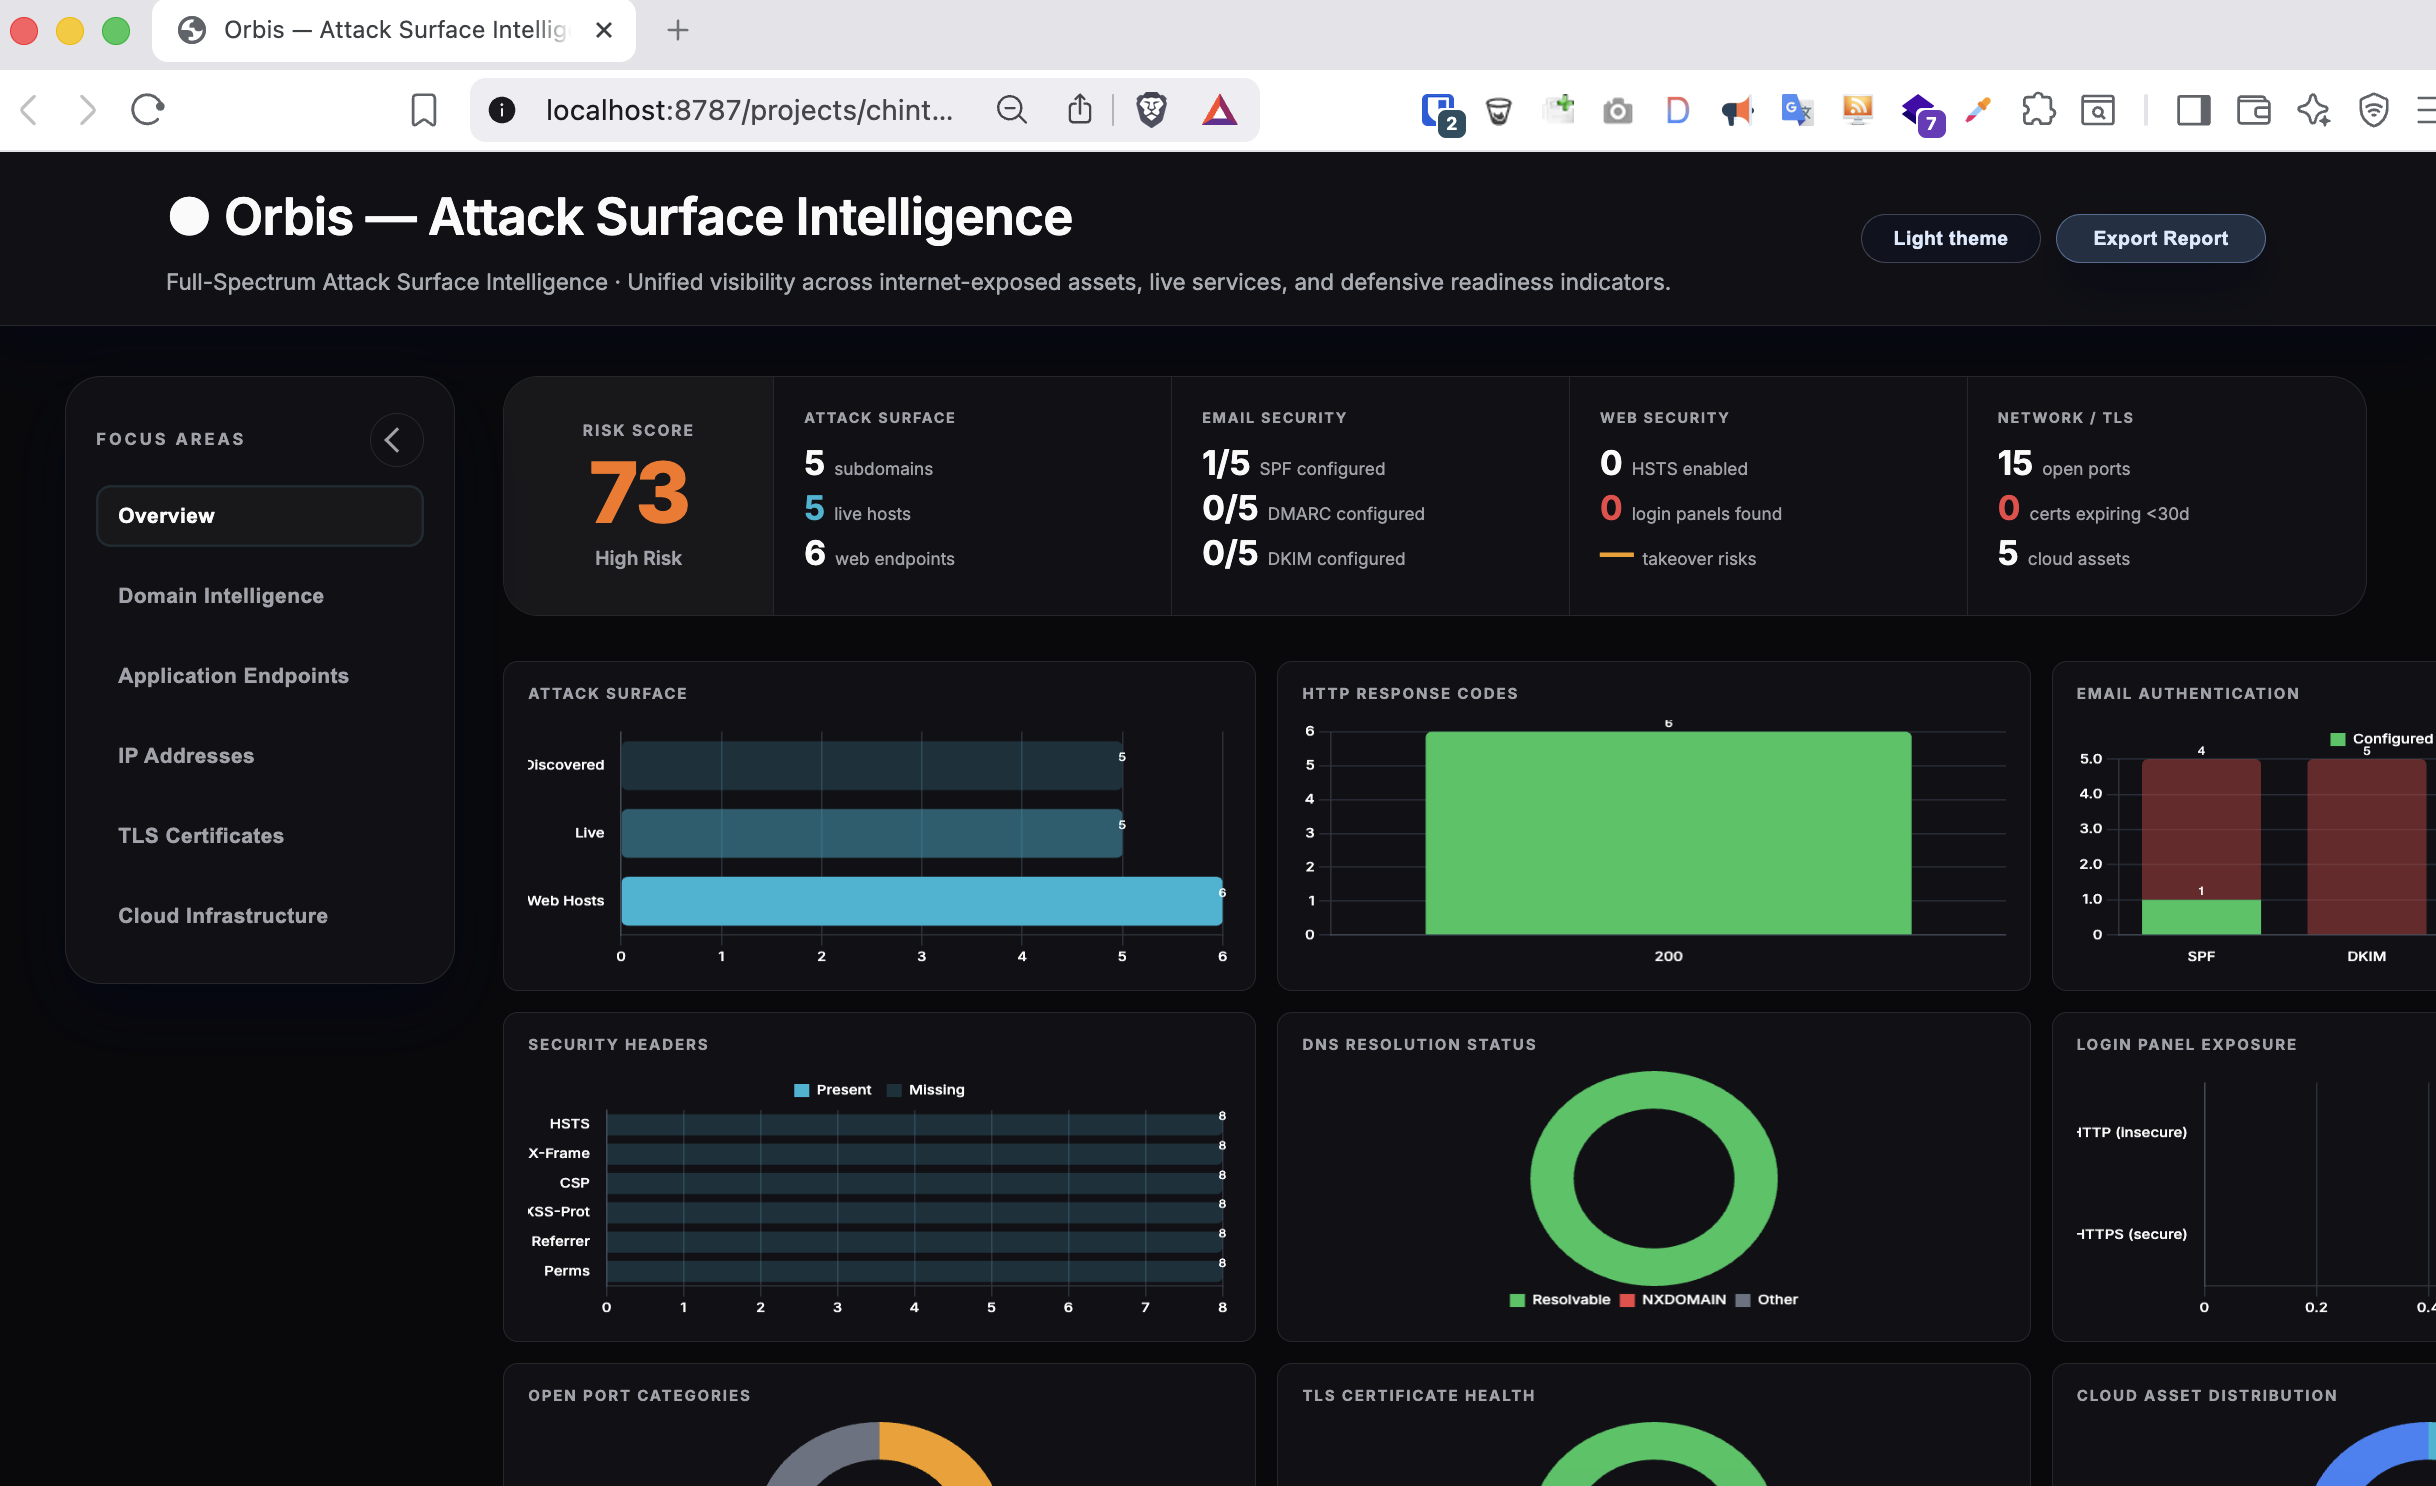
Orbis is an full spectrum automated external attack surface intelligent toolkit.

Passive recon & attack surface mapper — zero requests sent

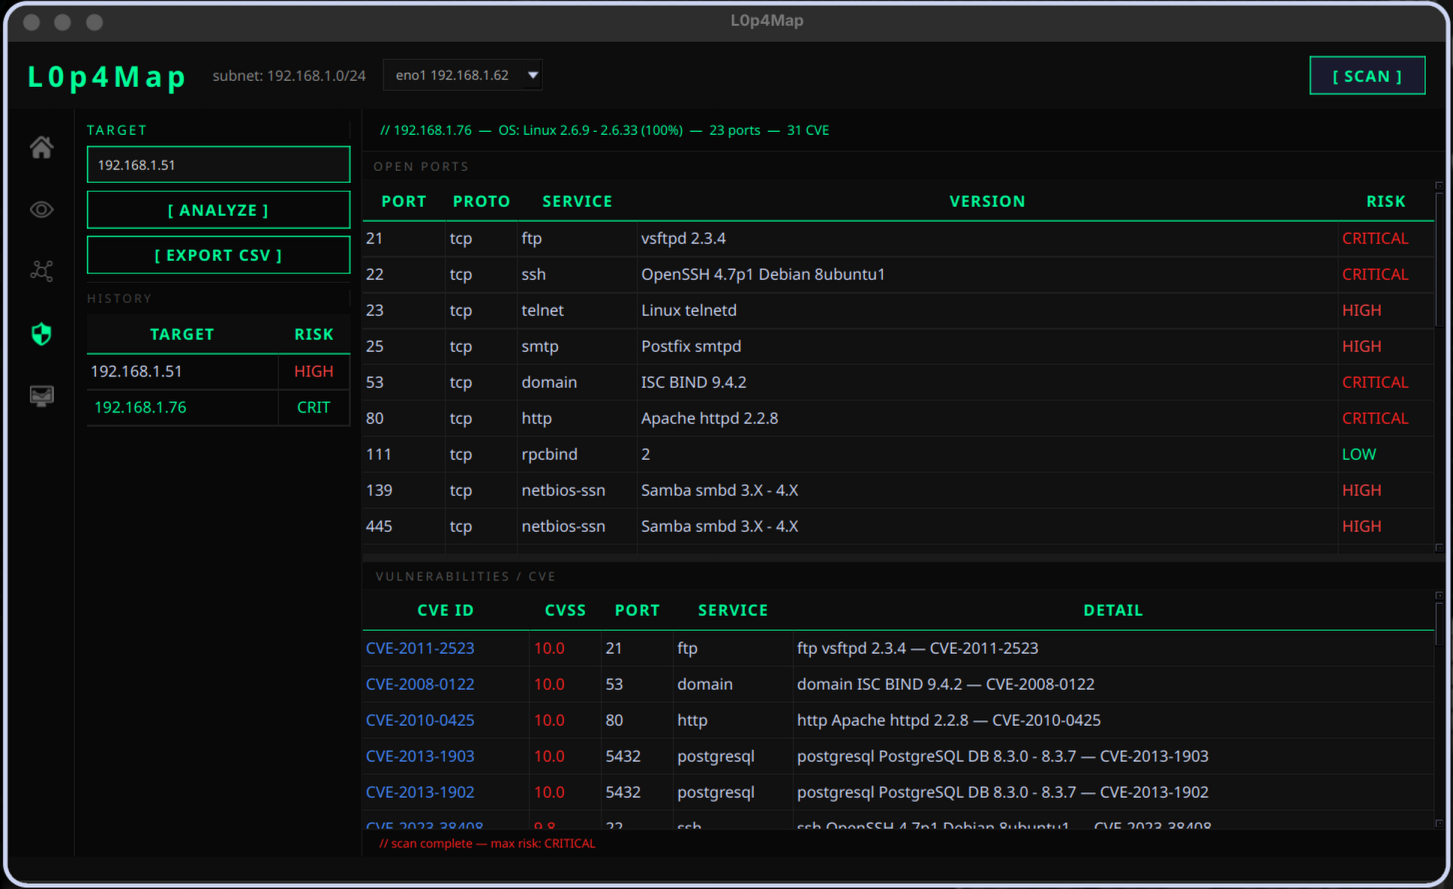
Professional network monitoring & visualization tool. L0P4Map combines high-speed ARP discovery with full nmap integration and a real-time…

Fast IIS short filename enumeration tool that identifies hidden files and directories via tilde vulnerability, with automatic full filename…

Information released publicly by NCC Group's Full Spectrum Attack Simulation (FSAS) team.

Omnisci3nt is an open-source web reconnaissance and intelligence tool for extracting deep technical insights from domains, including subdomains, SSL…

Recon is a script to perform a full recon on a target with the main tools to search for vulnerabilities. Created based on @ofjaaah and @Jhaddix…

👾 CVE-2026-58048 – cPanel Root SQL Execution Toolkit (CVSS 9.4) | Full Red/Blue Team Toolkit suite for unpatched cPanel & WHM 11.x. 2 tools: Safe…

Description Professional penetration testing assessment of the Sunset: Noontide VulnHub machine, covering reconnaissance, service enumeration,…

A Tkinter GUI that scans a local IPv4 network (ARP + nmap probing), shows devices, lets you run full port scans, and export results.

Full VAPT writeup of OWASP CICD-Goat — 9 CTFd flags captured, 4 critical + 5 high findings (incl. CVE-2024-23897) mapped to the OWASP Top 10 CI/CD…