CVE-2024-7029-EXPLOIT

Exploit code for CVE-2024-7029, a web application vulnerability, providing proof-of-concept implementation for security testing and research.

Exploit code for CVE-2024-7029, a web application vulnerability, providing proof-of-concept implementation for security testing and research.

Batch vulnerability detection tool for CVE-2022-35914. Scans multiple URLs from a target file to identify exploitable instances of this specific web…

Exploit script for CVE-2022-29469, a web application vulnerability, providing automated exploitation for penetration testing and security assessment.

Proof-of-concept exploit for CVE-2025-53770, demonstrating exploitation of a web application vulnerability for security testing and validation.

Python exploit script for CVE-2022-46169 targeting a specific web application vulnerability. Designed for penetration testers to verify and…

Proof-of-concept exploit for CVE-2021-22145, demonstrating a web application vulnerability with automated exploitation logic for security testing and…

Proof-of-concept exploit for CVE-2023-0297, demonstrating a specific vulnerability in a web application for security testing and validation purposes.

Proof-of-concept exploit for CVE-2022-30075, demonstrating a remote code execution vulnerability in a web application. Includes Python-based payload…

Exploit PoC of CVE-2026-6356

Security research tool for detecting and testing CVE-2025-64446 (FortiWeb Path Traversal RCE vulnerability)

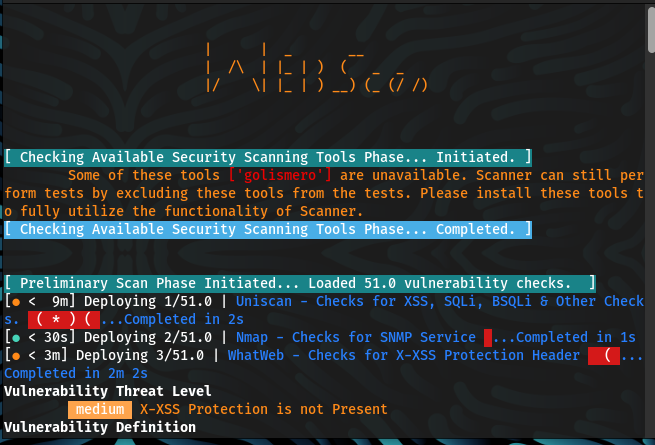
A Web Vulnerability Scanner and Patcher

A Directory Traversal attack (also known as path traversal) aims to access files and directories that are stored outside the intended folder.

This Proof of Concept (PoC) demonstrates an exploit for CVE-2024-42009, leveraging a cross-site scripting (XSS) vulnerability to extract emails from…

Apache Struts 2.0 RCE vulnerability - Allows an attacker to inject OS commands into a web application through the content-type header

CLI scanner for CVE-2006-2842 (PHP include() path truncation) vulnerability. Scans single or multiple URLs to detect this specific web application…

The objective is to conduct a full-scale security assessment of a WordPress-based web application, culminating in a complete server compromise. The…

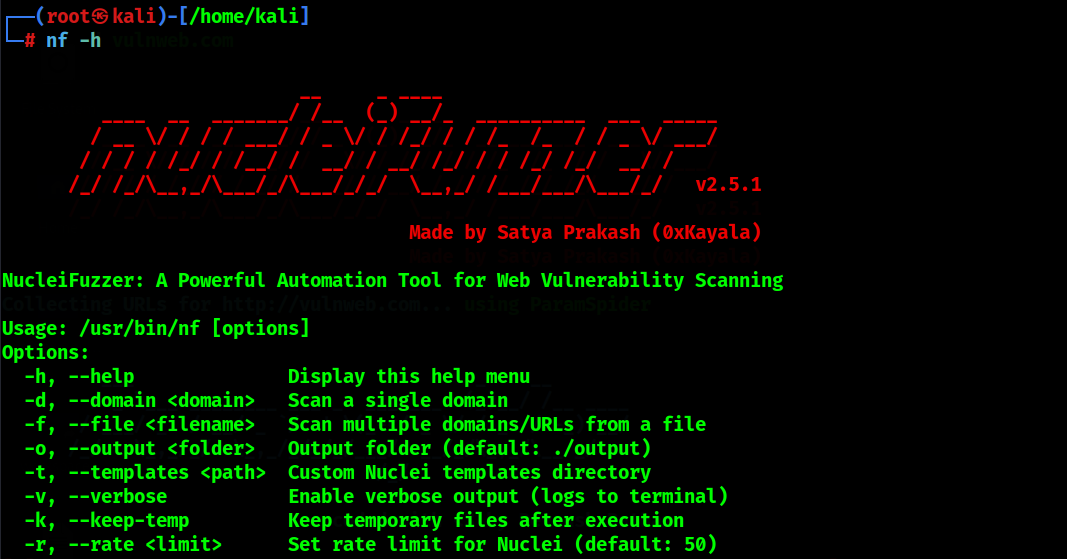
Automated web vulnerability scanner combining URL discovery tools (ParamSpider, waybackurls, gauplus, hakrawler, katana) with Nuclei fuzzing…

Optiva-Framework 🔎 Web Application Scanner🕵️