Blackash-CVE-2025-20393
 redpack-kr/blackash-cve-2025-20393
CVE-2025-20393
exploitationinformation-gatheringpenetration-testing+3
redpack-kr/blackash-cve-2025-20393CVE-2025-20393
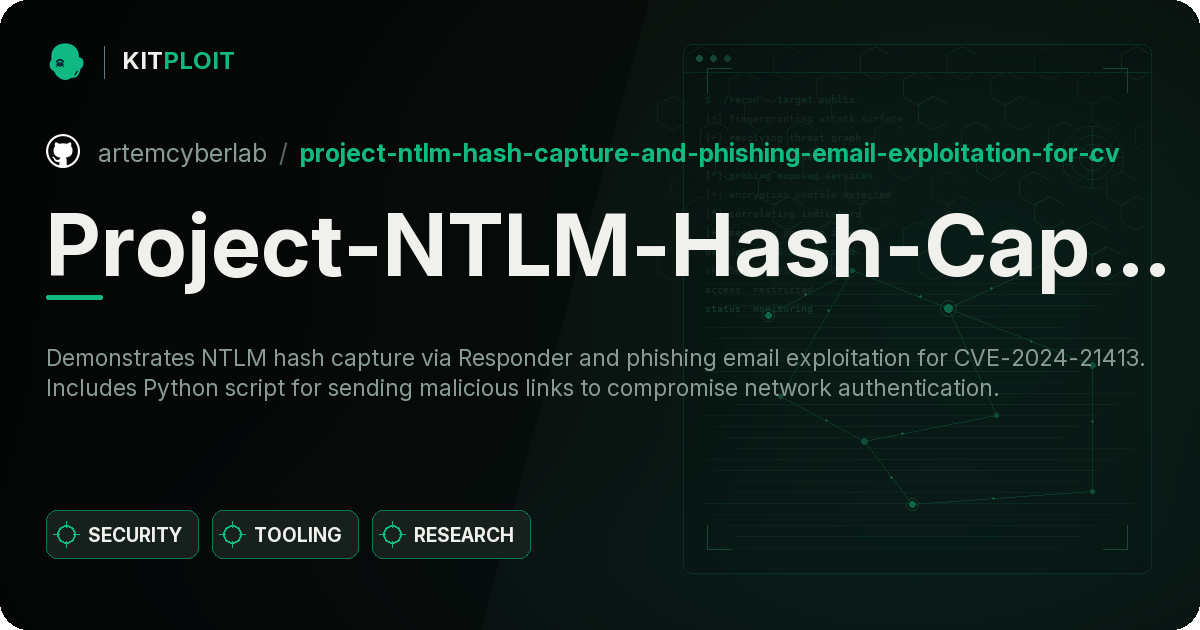 artemcyberlab/project-ntlm-hash-capture-and-phishing-email-exploitation-for-cve-2024-21413
Demonstrates capturing NTLM hashes via Responder and executing phishing emails exploiting CVE-2024-21413 to compromise systems.
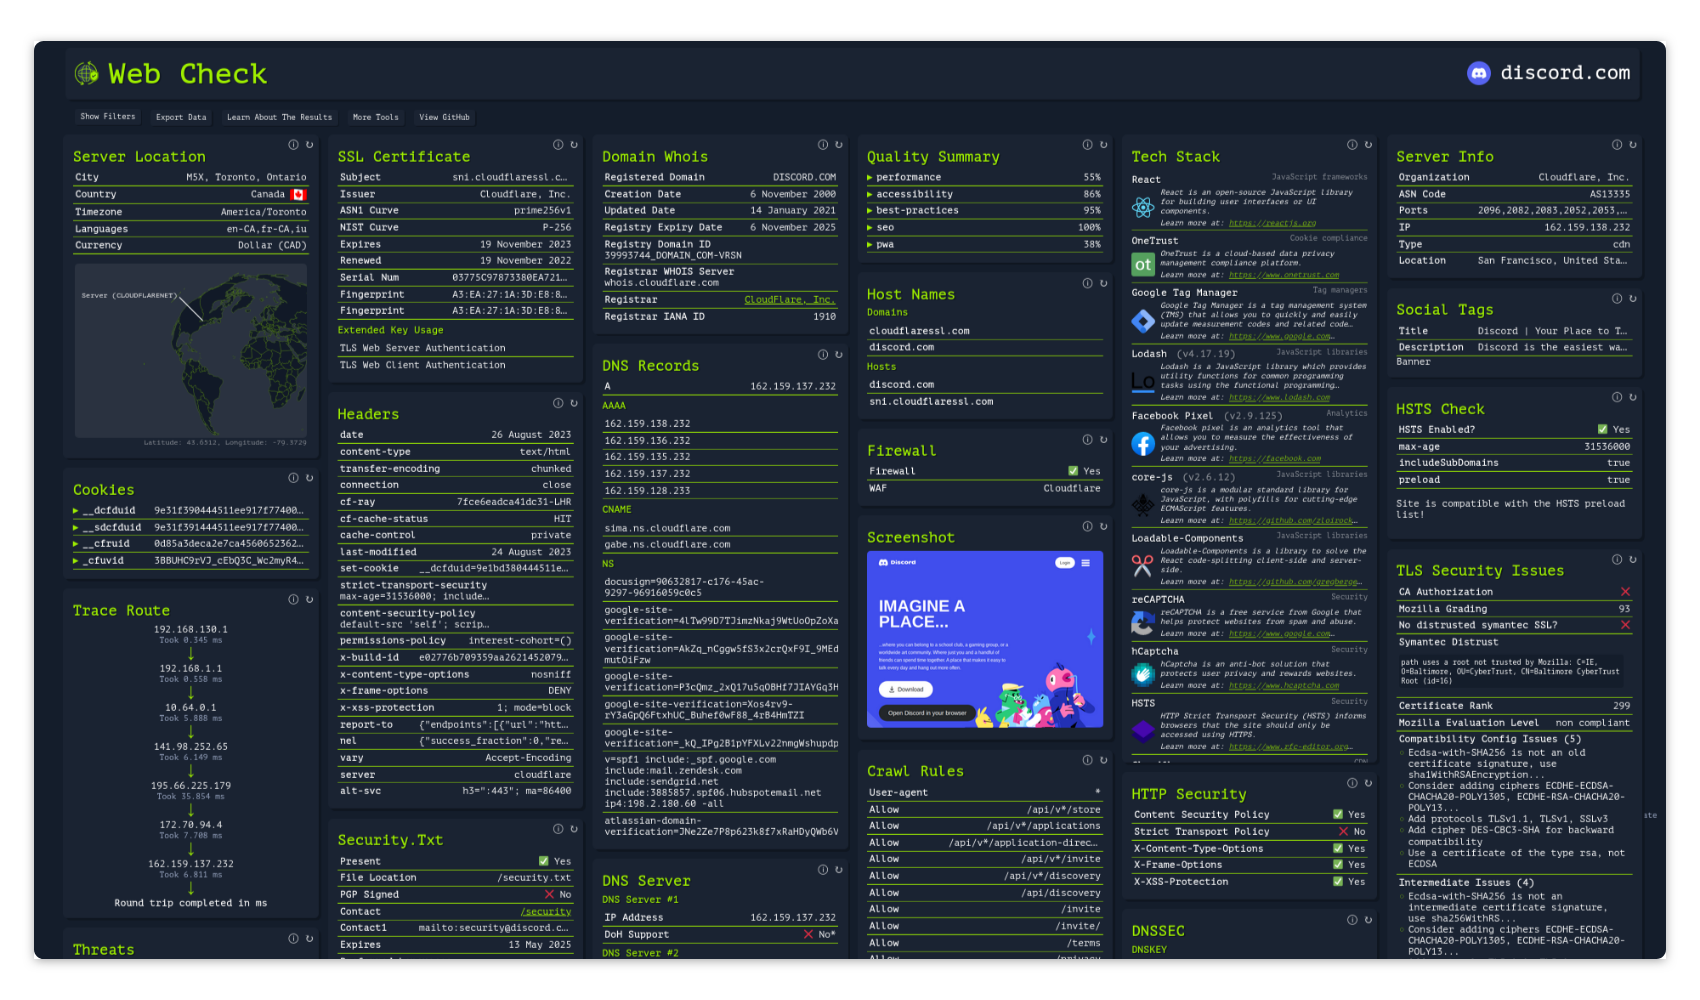 lissy93/web-check
🕵️♂️ All-in-one OSINT tool for analysing any website
 sundowndev/phoneinfoga
Information gathering framework for phone numbers
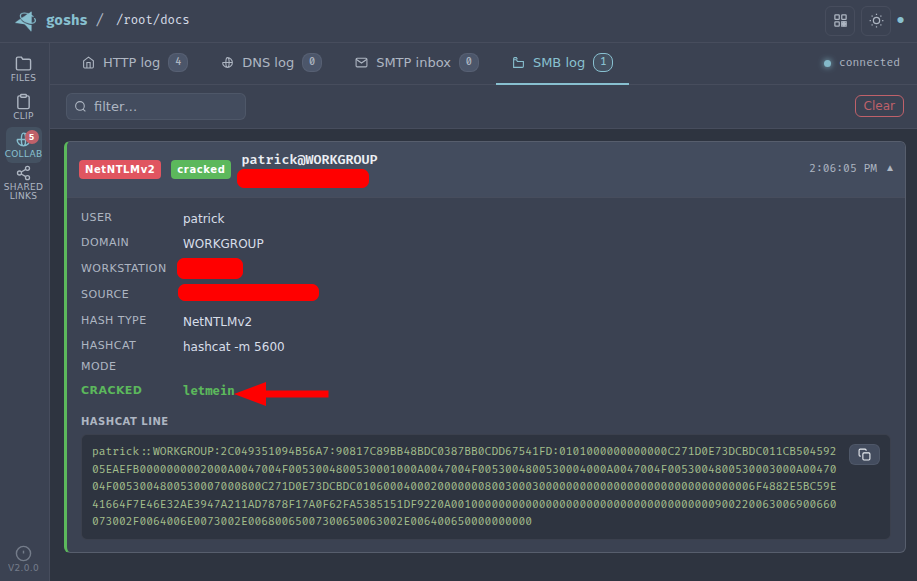 a-poc/redteam-tools
Tools and Techniques for Red Team / Penetration Testing
 webbreacher/whatsmyname
Community-maintained dataset of 700+ websites for finding accounts by username — powers OSINT and digital footprint tools.
 kpcyrd/sn0int
Semi-automatic OSINT framework and package manager
 josh0xa/darkdump
Open Source Intelligence Interface for Deep Web Scraping
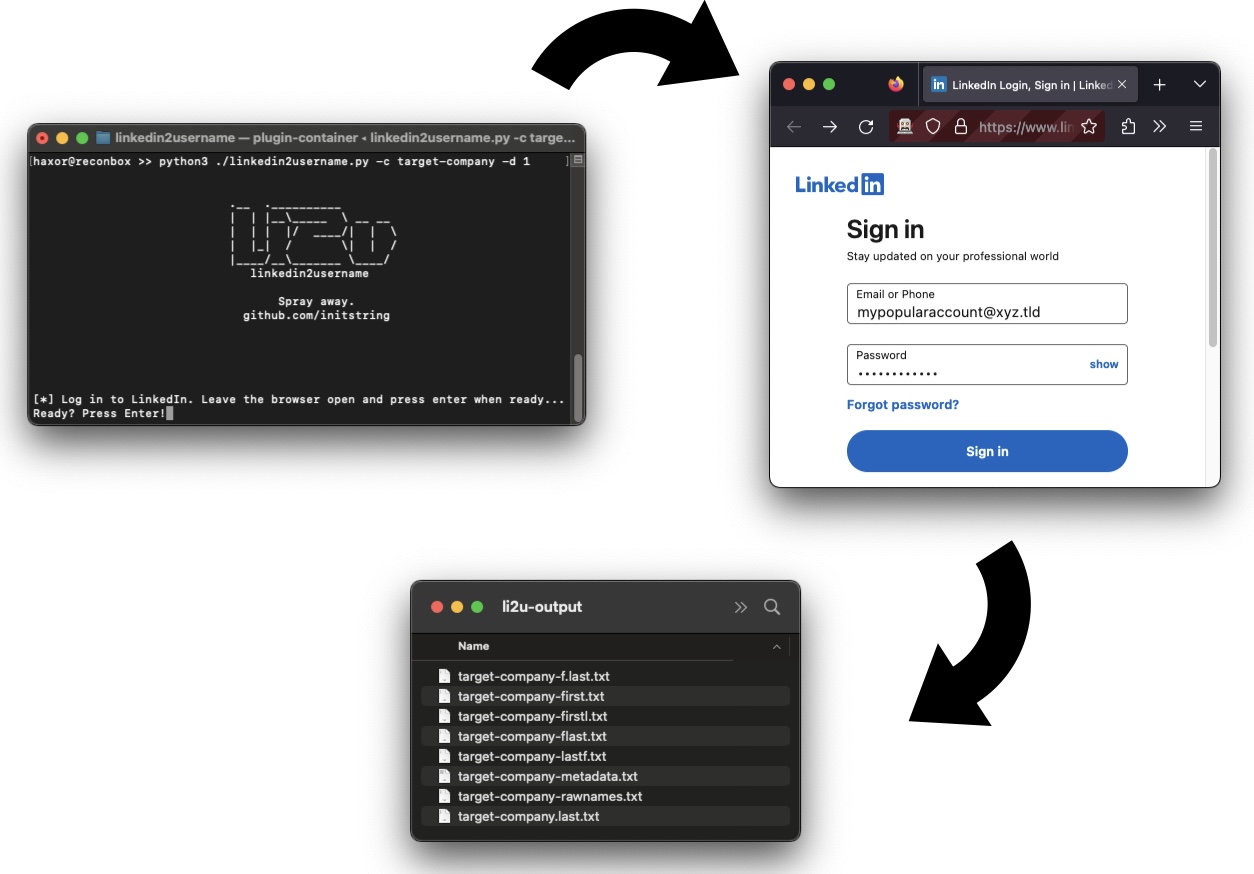 initstring/linkedin2username
OSINT Tool: Generate username lists for companies on LinkedIn
 googleinurl/scanner-inurlbr
Advanced search in search engines, enables analysis provided to exploit GET / POST capturing emails & urls, with an internal custom validation…
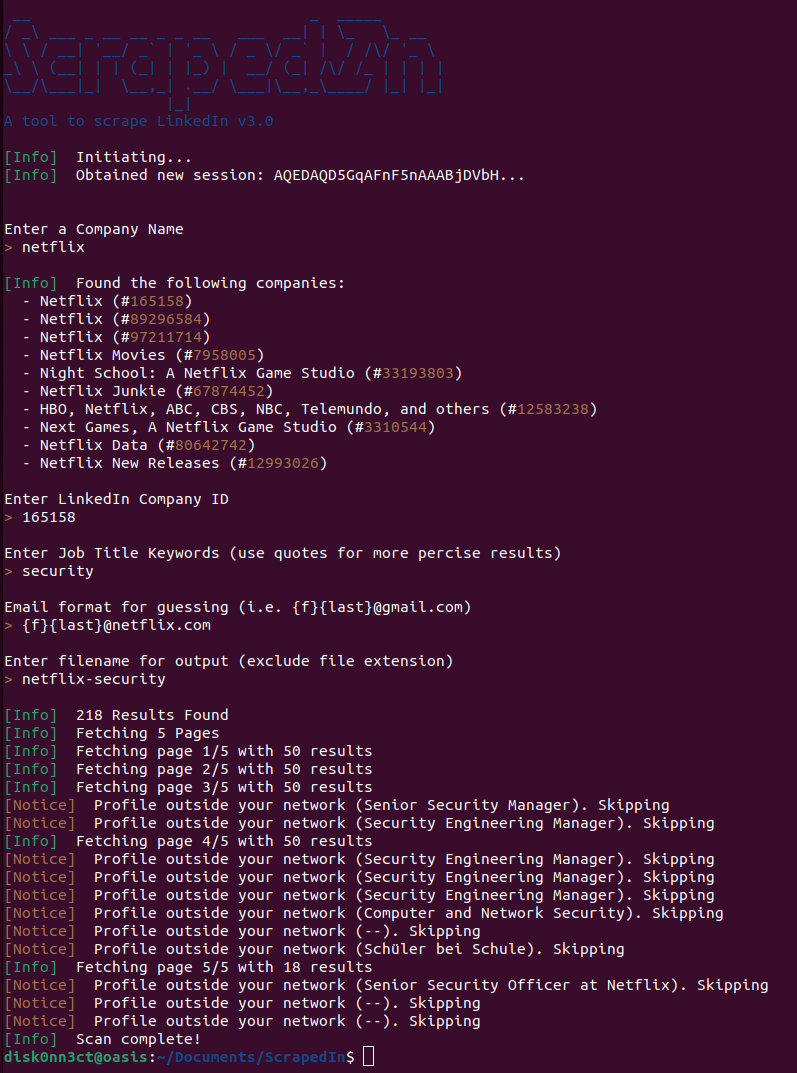 dchrastil/scrapedin
A tool to scrape LinkedIn without API restrictions for data reconnaissance
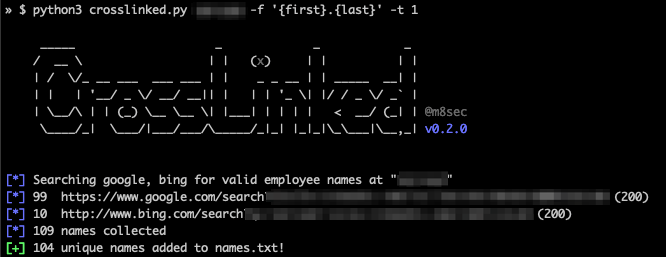 m8sec/crosslinked
LinkedIn enumeration tool to extract valid employee names from an organization through search engine scraping
 sairson/yasso
强大的内网渗透辅助工具集-让Yasso像风一样 支持rdp,ssh,redis,postgres,mongodb,mssql,mysql,winrm等服务爆破,快速的端口扫描,强大的web指纹识别,各种内置服务的一键利用(包括ssh完全交互式登陆,mssql提权,redis一键利用,mysql数据库…
 kevin-robertson/inveighzero
.NET IPv4/IPv6 machine-in-the-middle tool for penetration testers
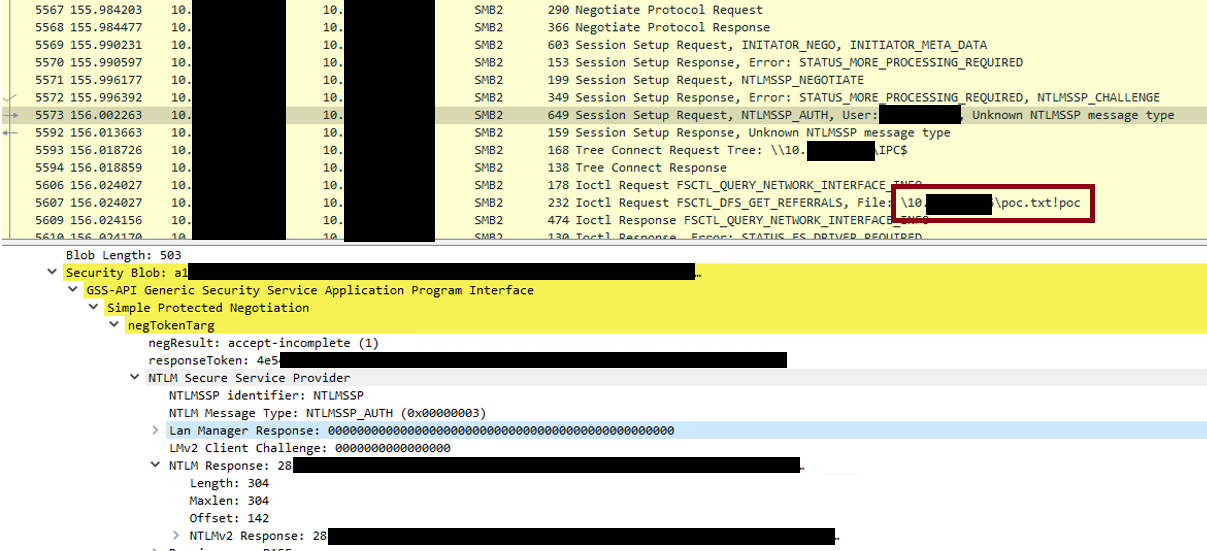 xaitax/cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Microsoft-Outlook-Remote-Code-Execution-Vulnerability
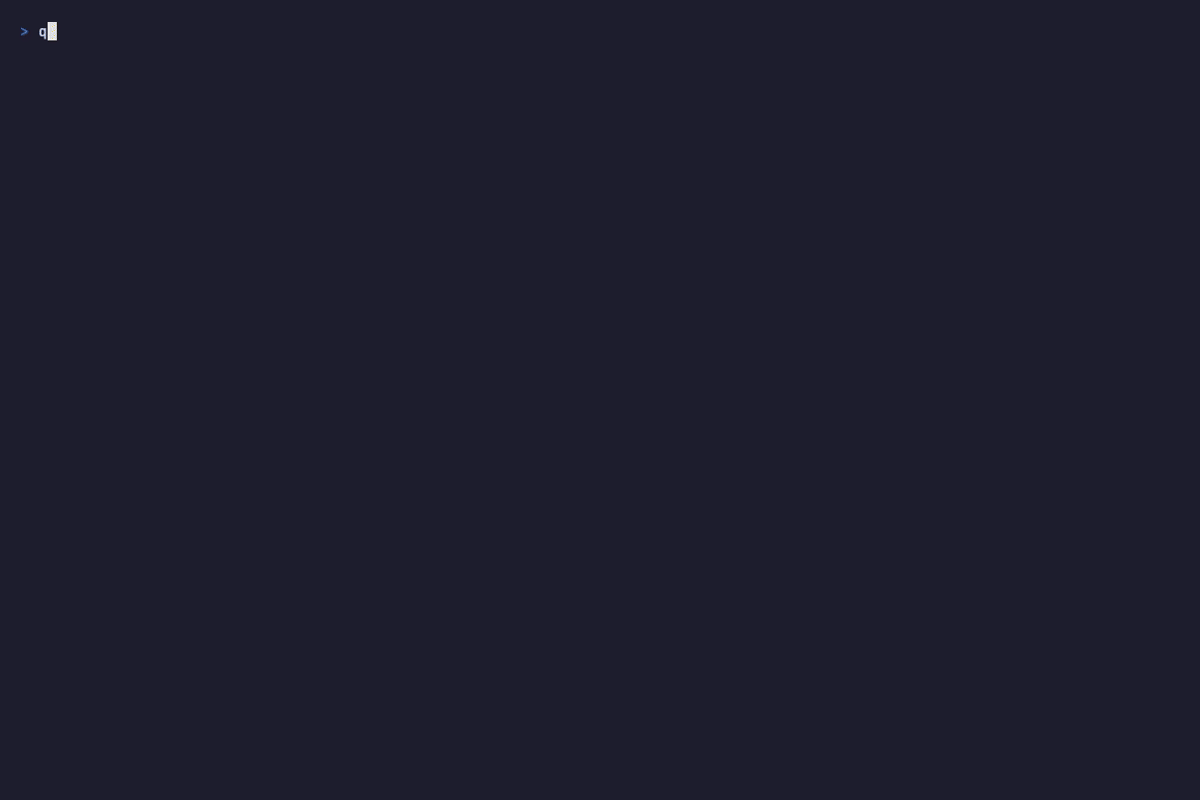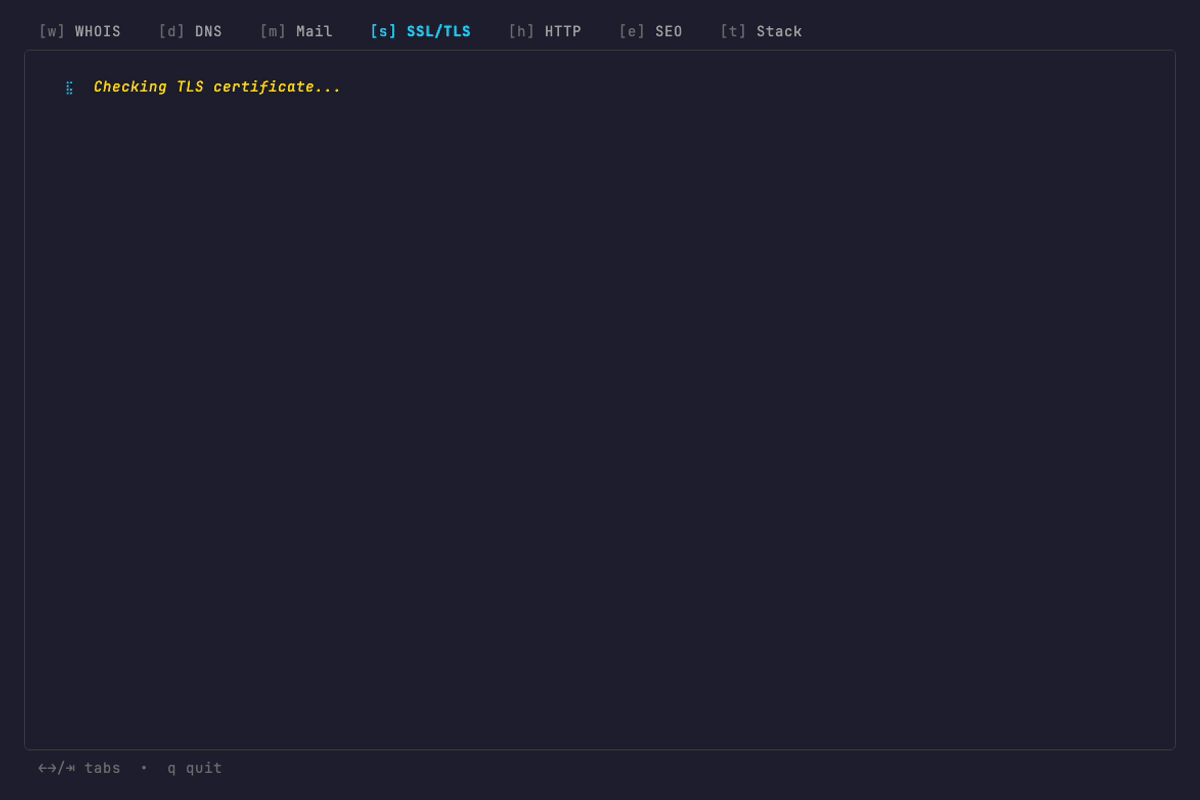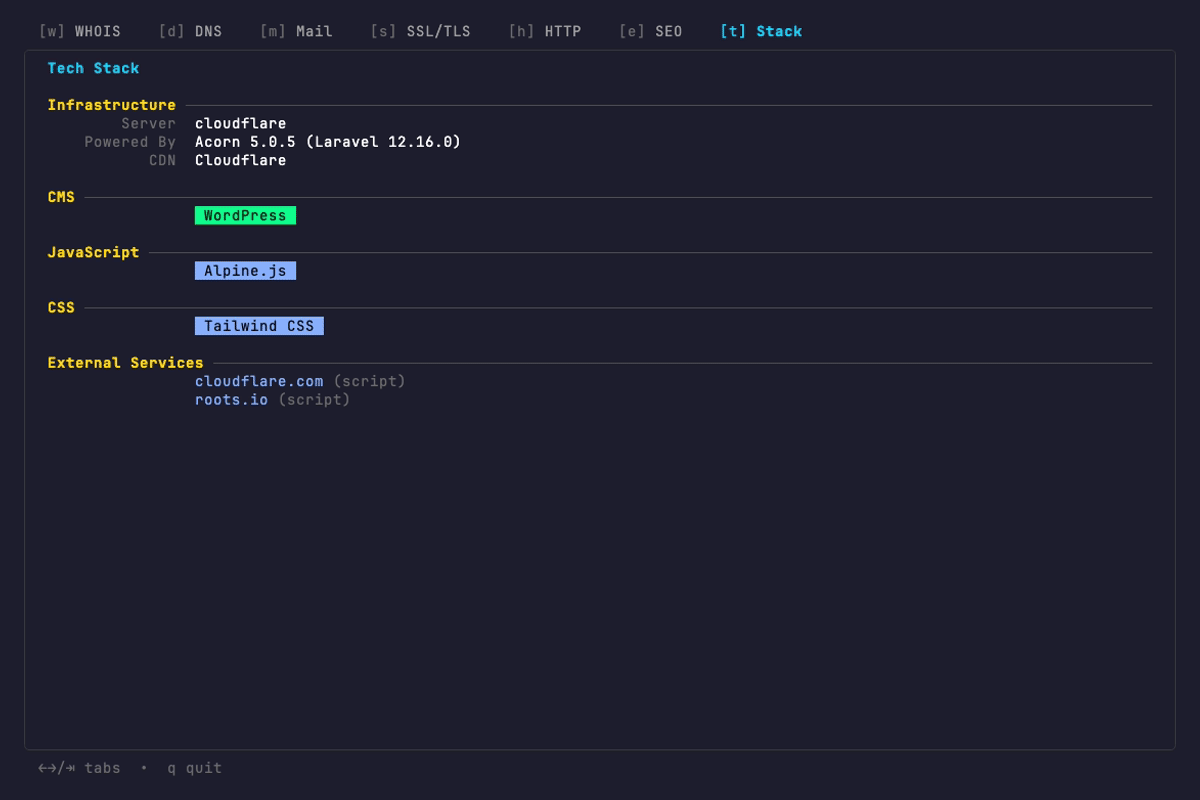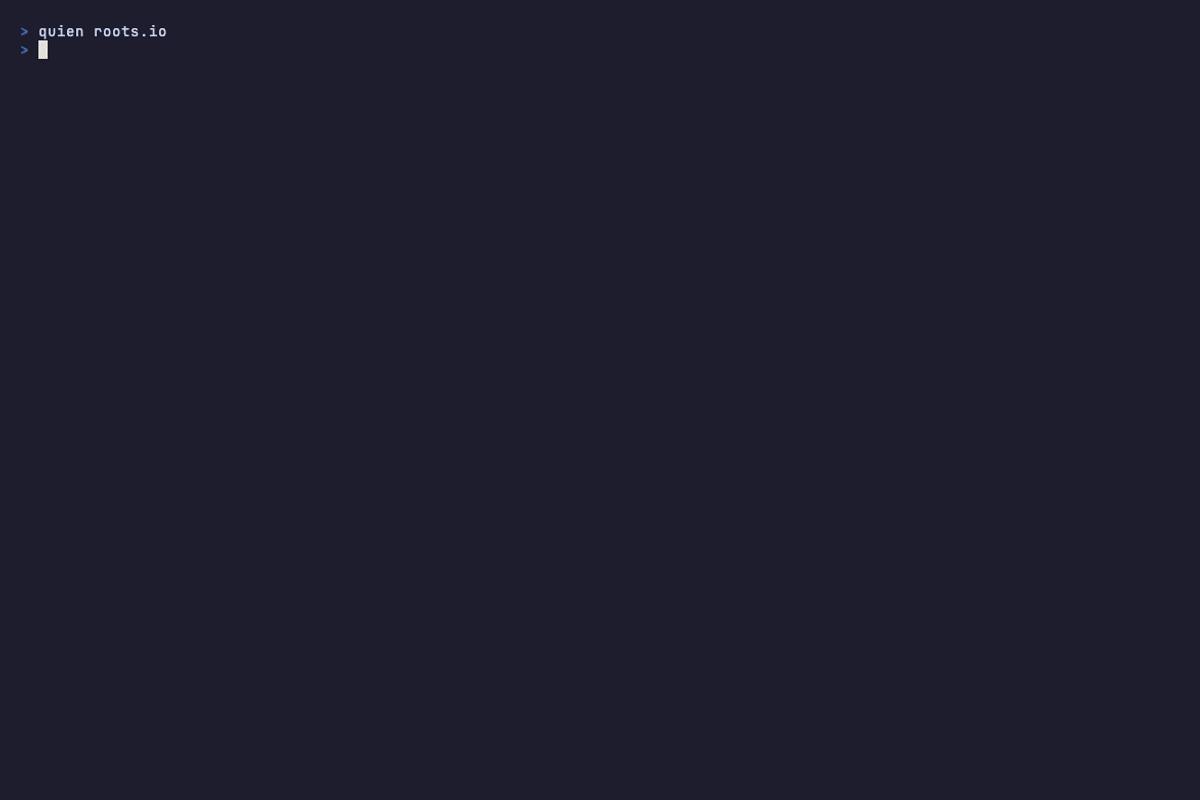 retlehs/quien
A better whois and domain intelligence toolkit