CVE-2002-0347
 alt3kx/cve-2002-0347
Directory traversal vulnerability in Cobalt RAQ 4 allows remote attackers to read password-protected files, and possibly files outside the web root,…
exploitationinformation-gatheringreconnaissance+2
alt3kx/cve-2002-0347Directory traversal vulnerability in Cobalt RAQ 4 allows remote attackers to read password-protected files, and possibly files outside the web root,…
 gcatt-as/cve-2024-48590
Disclosure of a Server-Side Request Forgery (SSRF) vulnerability in Inflectra SpiraTeam 7.2.00, detailing the attack vector, impacts, and vendor…
 r00thunter/log4shell-scanner
Python script to detect Log4Shell Vulnerability CVE-2021-44228
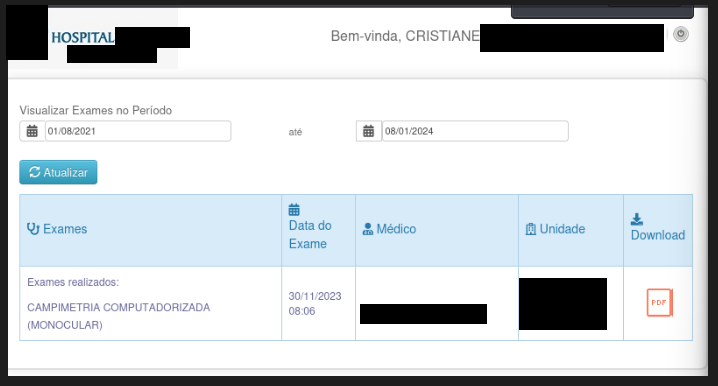 louiselalanne/cve-2024-23747
Moderna Sistemas ModernaNet Hospital Management System 2024 is susceptible to an Insecure Direct Object Reference (IDOR) vulnerability
 mauricelambert/exchangeweaknesstest
This script test the CVE-2021-26855 vulnerability on Exchange Server.
 aleongx/cve-2025-24071
Windows File Explorer Spoofing Vulnerability (CVE-2025-24071)
 baarai/artex
LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and…
 r3curs1v3-pr0xy/sub404
A python tool to check subdomain takeover vulnerability
 r0xdb/cve-2021-26855
CVE-2021-26855, also known as Proxylogon, is a server-side request forgery (SSRF) vulnerability in Exchange that allows an attacker to send arbitrary…
 bytereaper77/cve-2025-6907
a standalone C-based SQL Injection exploit targeting the CVE‑2025‑6907 vulnerability in the CODE_PROJECT service.
 diverto/nse-exchange
Nmap scripts to detect exchange 0-day (CVE-2022-41082) vulnerability
 zhzyker/exphub
Exphub[漏洞利用脚本库] 包括Webloigc、Struts2、Tomcat、Nexus、Solr、Jboss、Drupal的漏洞利用脚本,最新添加CVE-2020-14882、CVE-2020-11444、CVE-2020-10204、CVE-2020-10199、CVE-2020-1938…
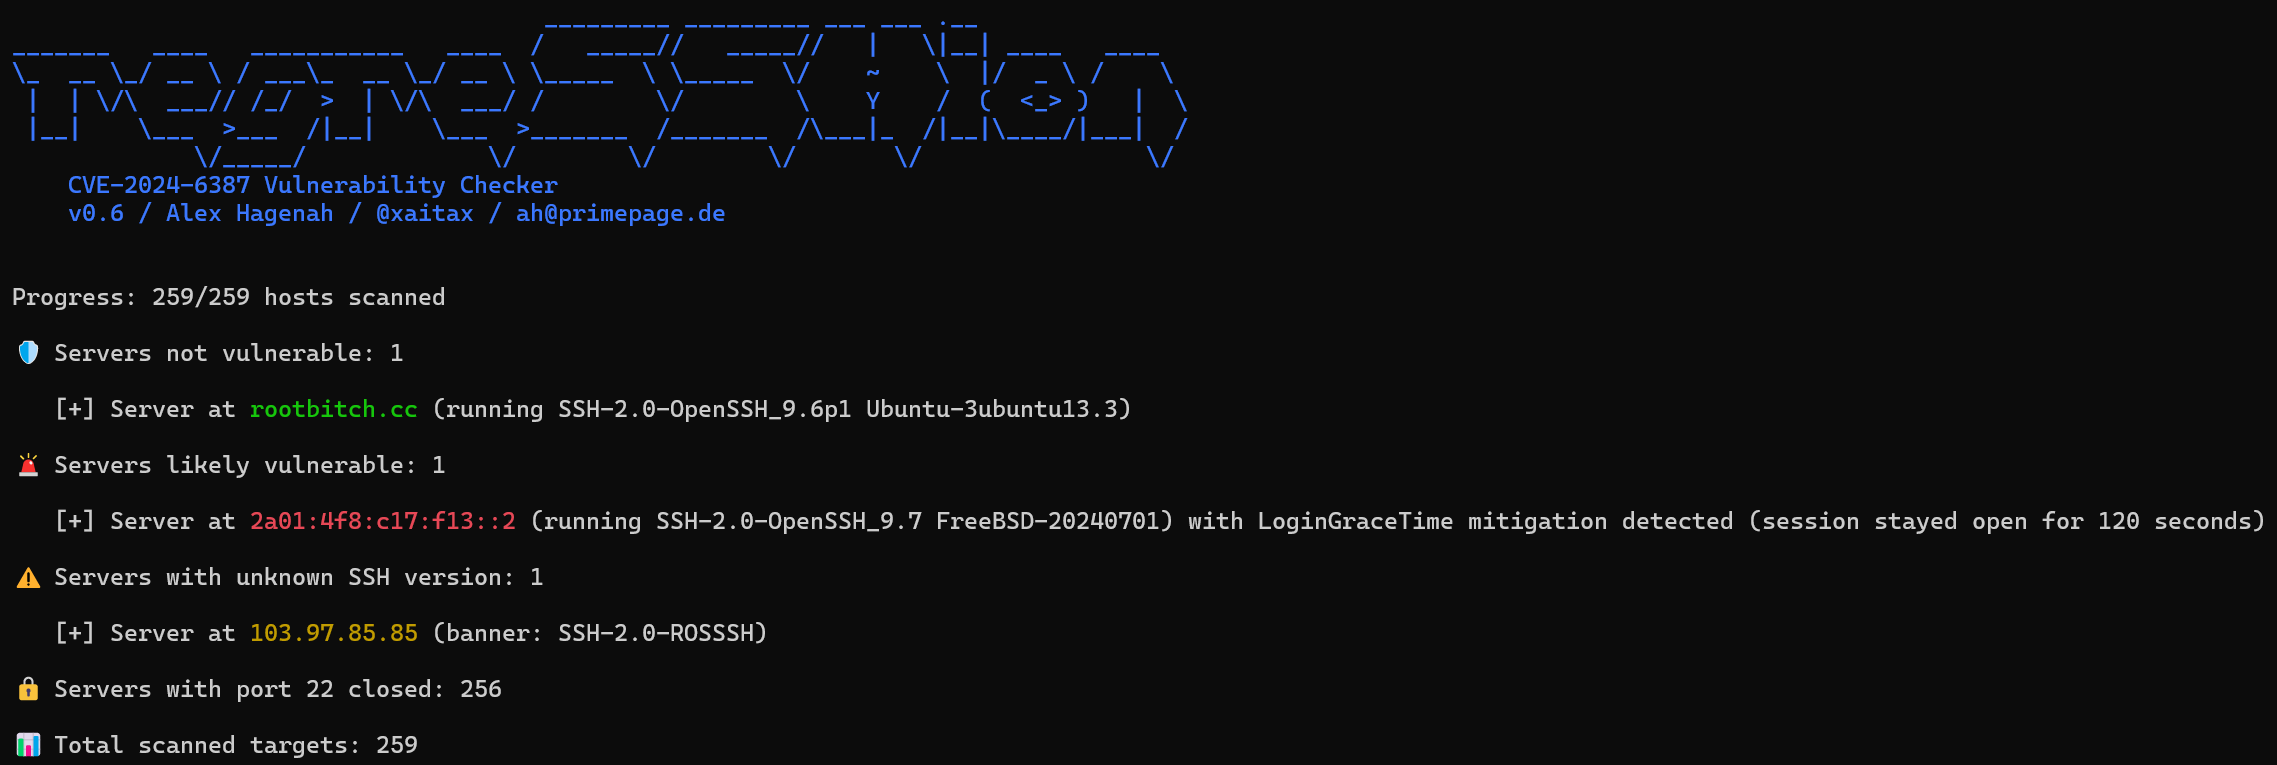 xaitax/cve-2024-6387_check
CVE-2024-6387_Check is a lightweight, efficient tool designed to identify servers running vulnerable versions of OpenSSH
 joker25000/optiva-framework
Optiva-Framework 🔎 Web Application Scanner🕵️
 treebuilder/aad-sso-enum-brute-spray
POC of SecureWorks' recent Azure Active Directory password brute-forcing vuln