
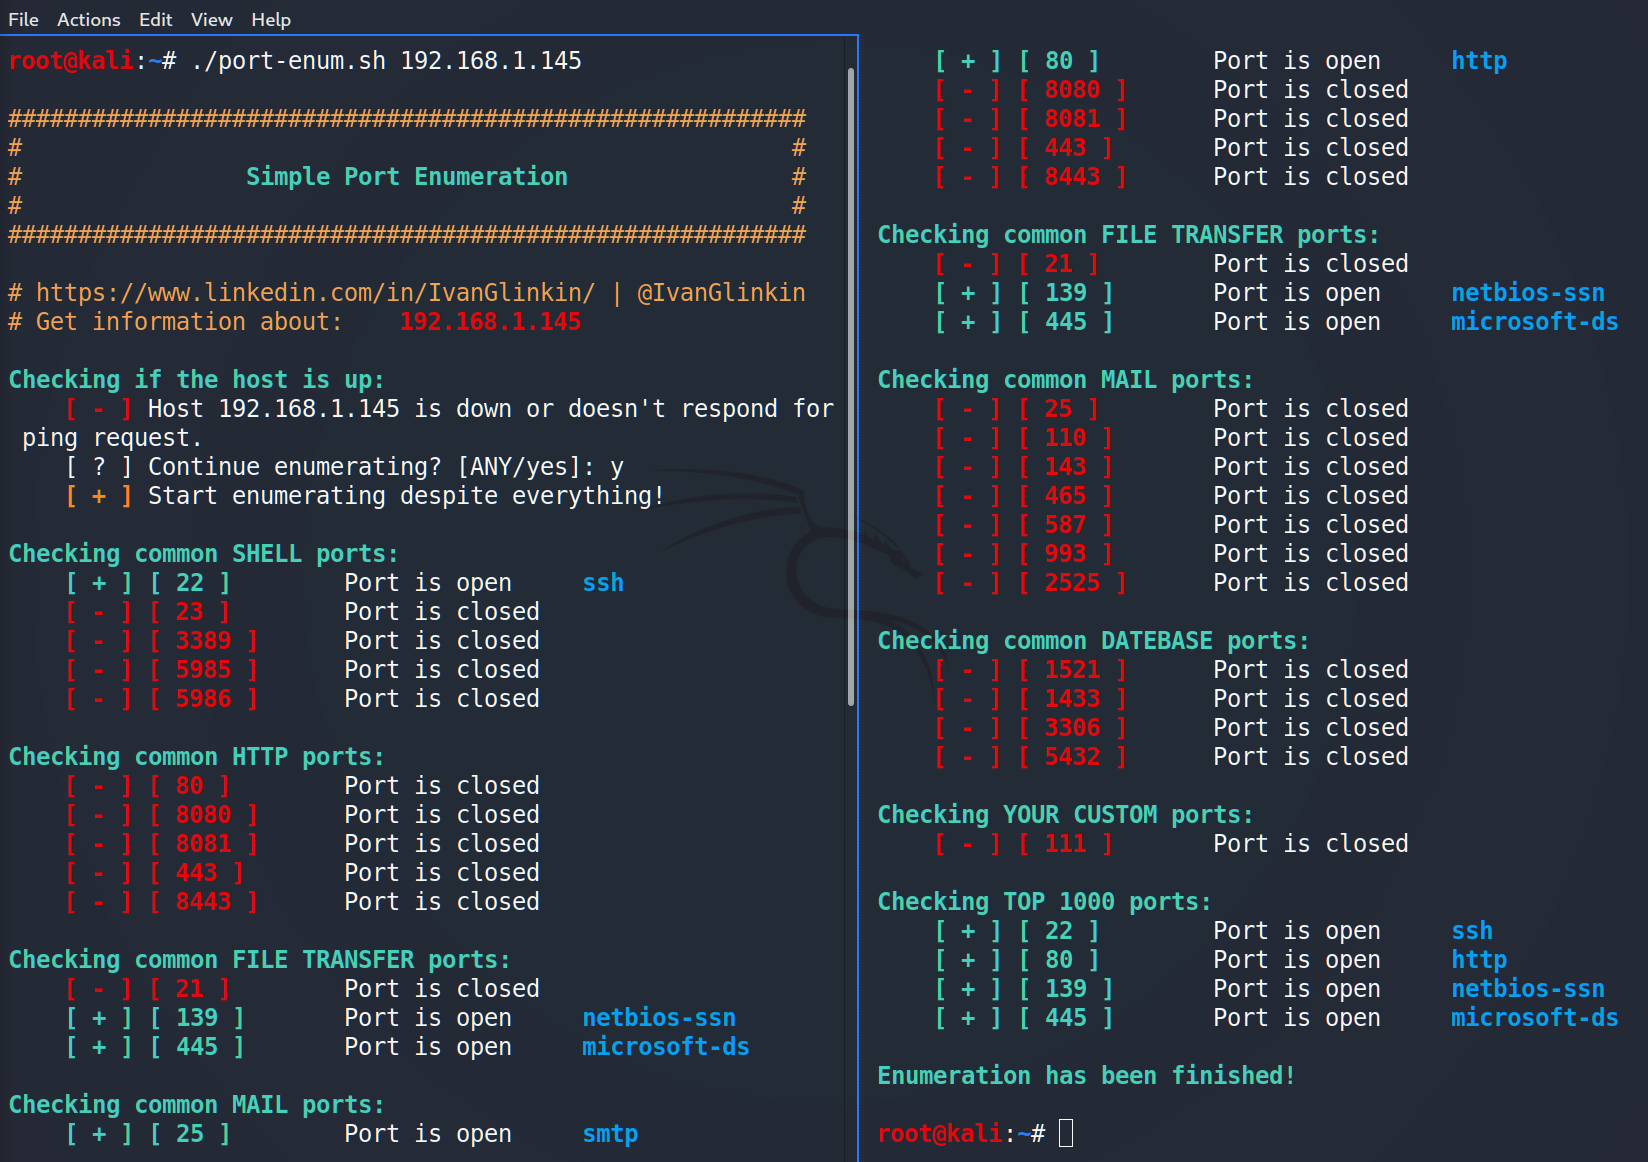
Port-enumeration
 ivanglinkin/port-enumeration
Have you ever faced with the lack of possibility of using NMap? For instance if you have reverse shell as an unprivileged user and there are no…
network-securitypenetration-testingport-scanning+1
33
ivanglinkin/port-enumerationHave you ever faced with the lack of possibility of using NMap? For instance if you have reverse shell as an unprivileged user and there are no…
 tc4dy/cve-2026-14762-poc-exploit
Multi-threaded time-based blind SQL injection exploit for CVE-2026-14762 targeting Hotel & Tourism Reservation 1.0. Enumerates databases, tables,…
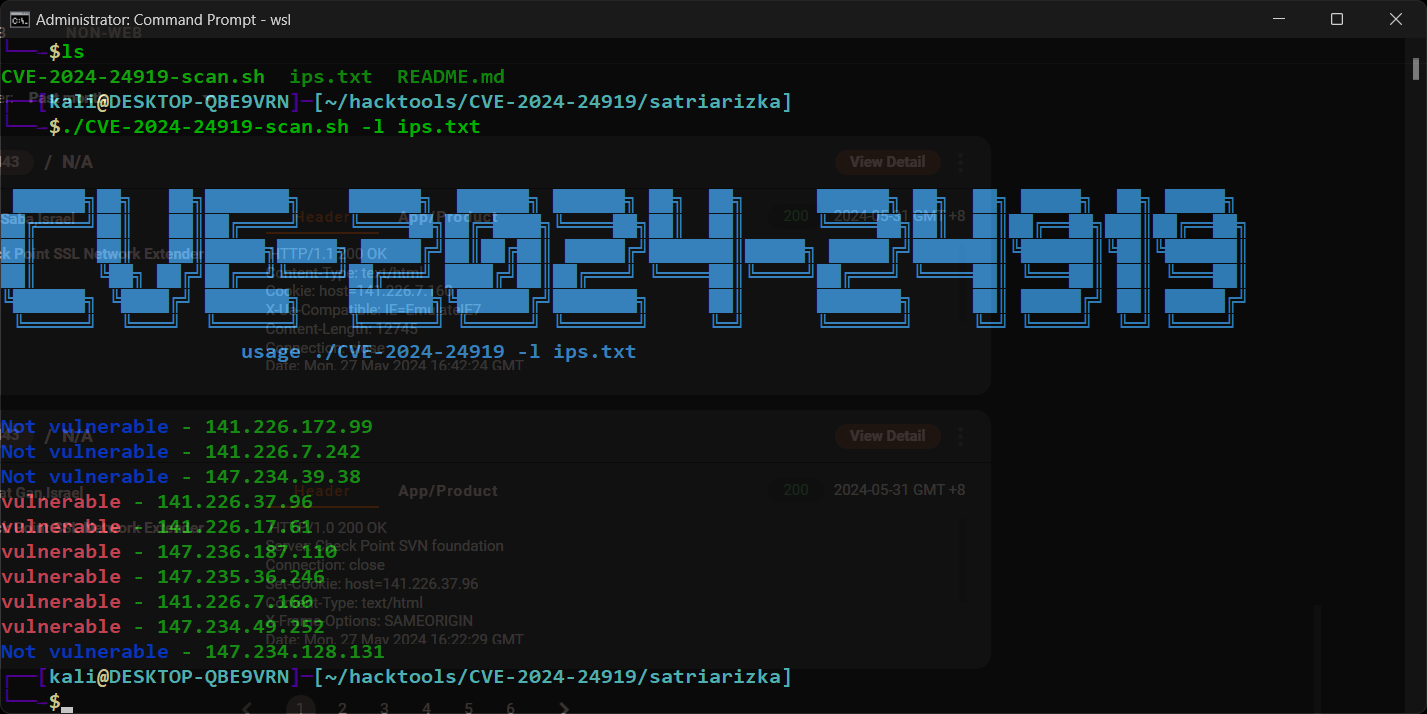 satriarizka/cve-2024-24919
A simple bash and python script to check for the vulnerability CVE-2024-24919

 r3dteam/casper-shell
Casper@shell:~# is an enhanced, more user-friendly version of p0wny shell with many new features.
 gwen001/github-search
A collection of tools to perform searches on GitHub.
 x1mdev/reconpi
ReconPi - A lightweight recon tool that performs extensive scanning with the latest tools.
 paulameg/simplectf-thm-walkthrough
First CTF successfully completed! This repo documents my walkthrough of TryHackMe's Simple CTF. It covers network reconnaissance (Nmap), web…
 ynsmroztas/nextrce
React Shell & Next.js RSC Exploit Tool (CVE-2025-55182)
 kr0no/bloodhound-shell
An interactive command-line shell for BloodHound API.
 rpranshu/eternalview
EternalView is an all in one basic information gathering and vulnerability assessment tool
 3ndg4me/cve-2020-3452-exploit
Just basic scanner abusing CVE-2020-3452 to enumerate the standard files accessible in the Web Directory of the CISCO ASA applicances.
 datalux/osintgram
Osintgram is a OSINT tool on Instagram. It offers an interactive shell to perform analysis on Instagram account of any users by its nickname
 ynsmroztas/nextssrf
CVE-2026-44578 scanner and exploit tool for SSRF in Next.js WebSocket upgrade handler. Detects vulnerable versions, extracts cloud metadata, and…
 imbas007/cve-2026-42533
Exploit for nginx heap buffer overflow (CVE-2026-42533) providing pre-auth RCE via two-pass capture clobbering. Includes info leak, heap spray, and…
 rebellionxkid/nowrecon
Subdomain enumeration and recon console for red team work. Passive + active collection, deep correlation, bucket discovery, msfconsole-style…
 ajutamangdev/hatiyar
Modular penetration testing framework with a Metasploit-like interactive shell, pre-built CVE exploit modules, and cloud/network reconnaissance…
 ynsmroztas/gitlabsniper
Single-file Python scanner and exploit for CVE-2026-85706, an unauthenticated arbitrary file read in self-managed GitLab CE/EE, with project…
 amitr12/cybersec
Single-file HTML cheat sheet for red teamers and pentesters with auto-injecting attacker/target variables, OS-aware reverse shell generator, and…