Claude-BugHunter
A Claude Code skill bundle for bug hunting and external red-team work - 82 skills, 15 slash commands, 681 disclosed-report patterns curated across 24…

A Claude Code skill bundle for bug hunting and external red-team work - 82 skills, 15 slash commands, 681 disclosed-report patterns curated across 24…

A curated list of awesome search engines useful during Penetration testing, Vulnerability assessments, Red/Blue Team operations, Bug Bounty and more

AI-powered penetration testing assistant that automates reconnaissance, vulnerability analysis, and note-taking via integrated LLMs and CLI tool…

Modern CLI for exploring vulnerability data with powerful search, filtering, and analysis capabilities.


Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Autonomous AI pentesting agents — real-time reconnaissance, vulnerability detection, and exploitation orchestration. Go + TypeScript.

Autonomous AI pentesting agents — real-time reconnaissance, vulnerability detection, and exploitation orchestration. Go + TypeScript.

Burp Suite extension for detecting CVE-2025-55182 (React2Shell) unsafe deserialization vulnerability. Features safe digest check, PoC redirect mode,…

Python-based checker and exploit for BlueKeep (CVE-2019-0708) RDP vulnerability. Scans multiple IPs to identify unpatched Windows systems and enables…

NetLogic is an advanced network analysis and cybersecurity toolkit for traffic inspection, packet analysis, and threat detection

CVE-2025-14847

Python wrapper around masscan and nmap for large-scale port discovery, host discovery, banner grabbing, and NSE-based vulnerability scanning across…

A tool for retrieving login credentials from Netwave IP cameras using a memory dump vulnerability (CVE-2018-17240)

Demonstrate the unauthenticated remote code execution vulnerability in the RSFiles! Joomla component through an arbitrary file upload.

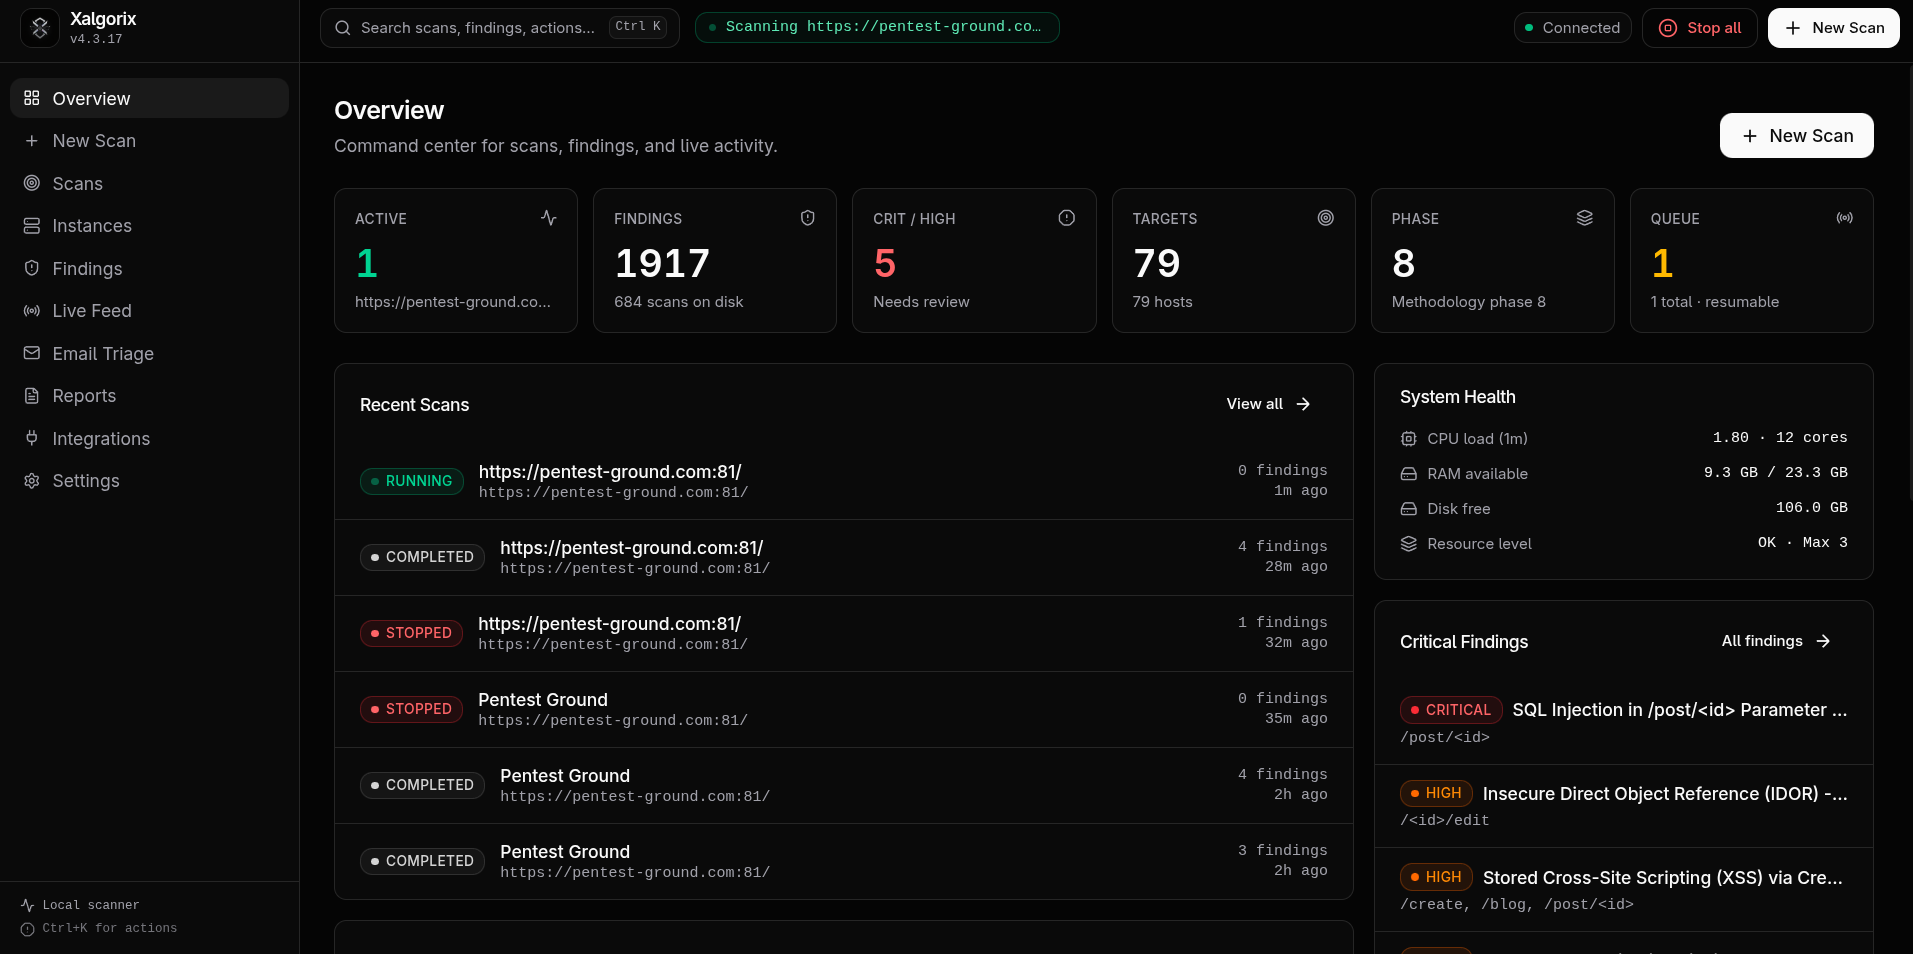
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.

Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management

Curated directory of bug bounty tools organized by category: reconnaissance, subdomain enumeration, port scanning, content discovery, exploitation,…