

akca
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
api-security-testingdefensive-toolsdynamic-analysis-sandboxing+9
242
akha-security/akcaEvidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 wpscanteam/wpscan
WordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…
 irsaattiquecyber/systemvulnerabilitychecklist_project4_decodelabs
System Vulnerability Checklist & Network Security Hardening project featuring reconnaissance, vsFTPd backdoor analysis (CVE-2011-2523), and active…
 raptoratack/copyfail-scanner-cve-2026-31431
Scans systems for CVE-2026-31431 (CopyFile vulnerability), enumerates system details, evaluates exposure, reports vulnerable status, and optionally…
 penguinsecq/cve-2026-6355
Exploit PoC of CVE-2026-6356
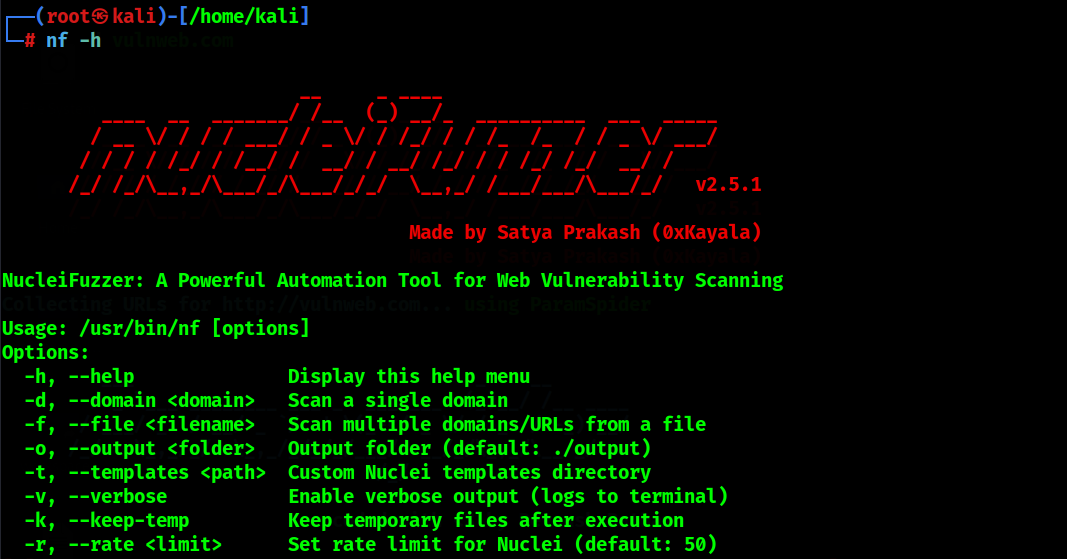 0xkayala/nucleifuzzer
Automated web vulnerability scanner combining URL discovery tools (ParamSpider, waybackurls, gauplus, hakrawler, katana) with Nuclei fuzzing…
 an5i/cve-2025-64446-fortiweb-exploit
Security research tool for detecting and testing CVE-2025-64446 (FortiWeb Path Traversal RCE vulnerability)
 artemcyberlab/project-project-chimera-exploiting-a-modern-wordpress-xxe-to-pillage-secrets-
The objective is to conduct a full-scale security assessment of a WordPress-based web application, culminating in a complete server compromise. The…
 r3xbugbounty/cve-2025-53770
Proof-of-concept exploit for CVE-2025-53770, demonstrating exploitation of a web application vulnerability for security testing and validation.
 nu11secur1ty/cisco
Security auditing toolkit for Cisco network devices, focusing on configuration review, vulnerability detection, and penetration testing of enterprise…
 bhanunamikaze/cve-2024-42009
This Proof of Concept (PoC) demonstrates an exploit for CVE-2024-42009, leveraging a cross-site scripting (XSS) vulnerability to extract emails from…
 malwareman007/scanner-and-patcher
A Web Vulnerability Scanner and Patcher
 kov404/cve-2024-51358
Proof-of-concept exploit for CVE-2024-51358, a server-side request forgery (SSRF) vulnerability in Heimdall 2.6.1, enabling remote HTTP requests to…
 bigherocenter/cve-2024-7029-exploit
Exploit code for CVE-2024-7029, a web application vulnerability, providing proof-of-concept implementation for security testing and research.
 grupooruss/cve-2024-6387
Python script to scan and secure SSH configurations against the CVE-2024-6387 race condition vulnerability, with automated LoginGraceTime adjustment…
 trackflaw/cve-2023-25203
CVE-2023-25203: Application Vulnerable to SSRF (Server Side Request Forgery) Attacks
 karthi-the-hacker/cve-2006-2842
CLI scanner for CVE-2006-2842 (PHP include() path truncation) vulnerability. Scans single or multiple URLs to detect this specific web application…
 zunak/cve-2023-49471
Proof-of-concept exploit for a Blind Server-Side Request Forgery (SSRF) vulnerability in Bar Assistant < 3.2.0, enabling authenticated attackers to…