
BloodHound
 specterops/bloodhound
Six Degrees of Domain Admin
defensive-toolsidentity-access-managementinformation-gathering+4
3.5k17h 15m ago
specterops/bloodhoundSix Degrees of Domain Admin
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
 go-appsec/toolbox
Collaborative application security testing between humans and agents via CLI and MCP
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 thomaspoppelgaard/netscaler-ctx697096-checker
Read-only checker for Citrix NetScaler CTX697096 (CVE-2026-88771–88778): verifies build, CVE preconditions and upgrade risks, and sweeps public IoCs…
 leo4j/invoke-adenum
Automated Active Directory auditing and enumeration tool that generates detailed HTML audit reports with CSV/XLSX export, designed for security…
 joda32/adit
Active Directory recon and read-only security audit over ADWS (net.tcp/9389), in Go
 owasp-noir/alibi
Cross-check the views of your attack surface and find the endpoints that cannot corroborate each other.
 abraxas/signal-server-dropwizard-admin
Signal-Server v20261007.0.0 - High - Remote - Privilege leftover - unauth Dropwizard admin :8081
 wpscanteam/wpscan
WordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…
 furkankayapinar/cve-2026-94127
Read-only defensive detector for CVE-2026-94127 in F5 BIG-IP APM. Fingerprints hosts, checks versions via iControl REST, and verifies OAuth…
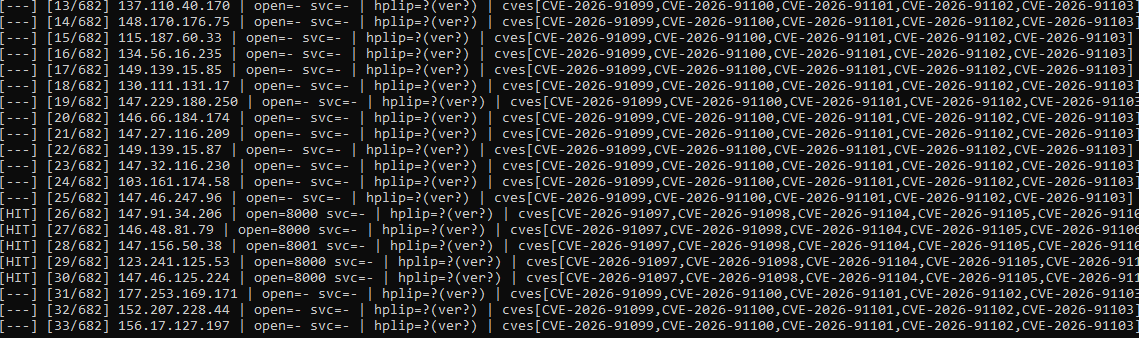 murrez/hp-hplip-mass-cve-checker-2026-09-
Mass check/research exploit for HP HPLIP CVE-2026-91097–91106 (<3.26.6), PAPPL :8000 IPP probes + hpssd templates
 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
 duriantaco/ravage
Evidence first autonomous web security testing for controlled, authorized targets. With reproducible labs, audit trails, reports, and XBEN…
 ammarion/waf-detector
🛡️ High-performance WAF & CDN detection tool. Identify protection layers (Cloudflare, Akamai, AWS, Fastly, and more), run effectiveness and…
 foxvr-sudo/bug-bounty-arsenal-v.3
Full-stack platform for authorized web application security scanning with a detector-based engine, async Celery workers, and a React dashboard for…
 xcoy0te/cve-2026-83548-checker
Non-intrusive detector for SonicWall SMA 1000 exposure to CVE-2026-83548/-83549 (version/patch-state check; no exploitation)
 p0dalirius/sharehound
A python tool to map the access rights of network shares into a BloodHound OpenGraphs easily