
go-exploit-cache
 vulncheck-oss/go-exploit-cache
A utility for producing an HTTP cache database to use with go-exploit
exploitationinformation-gatheringosint+6
9
vulncheck-oss/go-exploit-cacheA utility for producing an HTTP cache database to use with go-exploit
 arxhr007/aliens_eye
Hunt down 840+ social media accounts using AI
 apify/crawlee
Node.js web scraping and browser automation library for building reliable crawlers with HTTP and headless browser support, proxy rotation, and…
 darkrx1/rxscan
Rust CLI for bounded network reconnaissance: TCP/UDP port discovery, service identification, DNS/TLS/HTTP evidence collection, and public-source…

 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
 cyeezy08/kimai-cve-2026-52824-poc
PoC exploits for CVE-2026-52824 (GHSA-jr9p-4h4j-6c58) — Kimai time-tracking default APP_SECRET authentication bypass affecting versions ≤ 2.57.0
 qyvora/qyvora-anansi
Terminal-first attack surface intelligence engine. Built for speed, portability, and raw technical signal.
 albertrg99/redditosint
Reddit OSINT by username. Discover indexed posts, comments, deleted and live content, activity patterns, exposed identifiers, and an overall exposure…
 andresriancho/enumerate-iam
Enumerate the permissions associated with AWS credential set
 ferpalma21/nextjs-scanner
This script scans a list of URLs to detect if they are using **Next.js** and determines whether they are vulnerable to **CVE-2025-29927**. It…
 bsysop/servicenow
Scans ServiceNow instances for widget-simple-list plugin misconfigurations that expose data via the API, supporting single URLs, URL lists,…
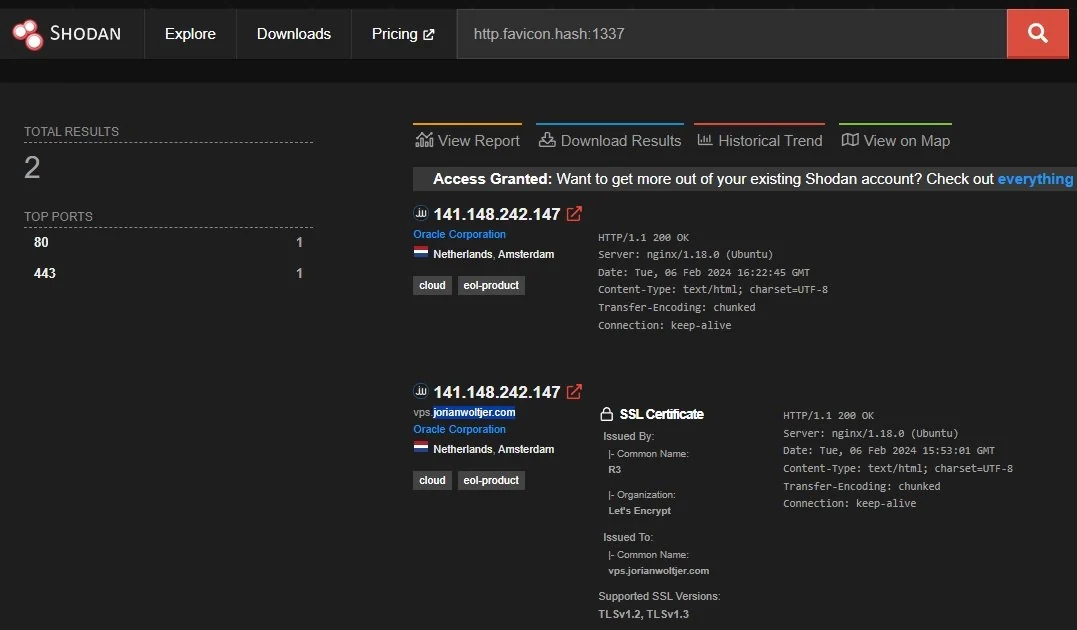 jorianwoltjer/shodan-favicon-preimage
Generate a favicon that results in any target hash on Shodan
 thomaspoppelgaard/netscaler-ctx697096-checker
Read-only checker for Citrix NetScaler CTX697096 (CVE-2026-88771–88778): verifies build, CVE preconditions and upgrade risks, and sweeps public IoCs…
 piratesshield/apiharvester
The one shot API attacker tool - finds the API url from the given root simulate the automated attacks
 jankoboy88/higernes
a passive OSINT toolkit in python - usernames, emails, domains, ips, phones, hashes. no keys, no logins.
 vqkro/higernes
a passive OSINT toolkit in python usernames, emails, domains, ips, phones, hashes. no keys, no logins.
 ankhcorp/nuke.sh
Bash-based passive reconnaissance + attack surface mapping script using only public APIs + stock Linux tools (curl, dig, openssl, nmap, python3).
 murrez/cve-2026-102425
Python PoC for CVE-2026-102425: unauthenticated RCE in Joomla Balbooa Forms (com_baforms) via field shortcode injection in post-submission PHP…