CVE-2026-121529-Toolkit

Red/blue team toolkit for CVE-2026-121529 FortiClient CORS origin validation flaw: RCE exploit with interactive shell, browser payload server, mass…

Red/blue team toolkit for CVE-2026-121529 FortiClient CORS origin validation flaw: RCE exploit with interactive shell, browser payload server, mass…

Python PoC driver for CVE-2026-122051, a pre-auth command injection in the Edimax BR-6208AC /goform/mp handler, with firmware emulation recipe, bulk…

Subdomain enumeration and recon console for red team work. Passive + active collection, deep correlation, bucket discovery, msfconsole-style…

Detection and exploitation toolkit for the FreeSWITCH SIP MESSAGE command injection (CVE-2026-116779), with API execution, DNS OAST shell output,…

Hands-on cybersecurity and CTF labs covering port reconnaissance, CMS stack discovery, VulnCMS, CVE-2026-58225, shell-to-root paths, Python, sudo,…

Python check/exploit PoC for CVE-2026-94132: detects AcyMailing for Joomla versions, probes the media/com_acym/upload directory, and verifies…

Python mass exploitation scanner for CVE-2026-93399 in the Bookly WordPress plugin: version detection, unauthenticated IDOR order-token enumeration,…

Python3 tool that detects and exploits Local File Inclusion vulnerabilities, with crawling, path traversal and filter bypass payloads, and automated…

An interactive command-line shell for BloodHound API.

Single-file Python scanner and exploit for CVE-2026-85706, an unauthenticated arbitrary file read in self-managed GitLab CE/EE, with project…

Multi-module offensive security toolkit for SOCKS5 proxy chaining, port scanning, DNS enumeration, hash cracking, reverse shell generation,…

Automated exploit toolkit and detection template for CVE-2024-21546, an unauthenticated RCE in UniSharp Laravel Filemanager, with WAF evasion and…

Exploit for Marimo pre-auth RCE via terminal WebSocket, providing command execution, interactive PTY shell, and reverse shell capabilities for…

Proof-of-concept exploit for CVE-2026-41940 targeting cPanel, enabling account enumeration, command execution, and interactive shell access on…

AsyncIO Scanner & Exploitation Framework for CVE-2026-24061 (Telnet NEW_ENVIRON Auth Bypass). Features high-concurrency discovery, passive…

Automated exploit tool for CVE-2026-1357, an unauthenticated RCE in WPvivid Backup & Migration. Scans WordPress targets, bypasses WAF/403, uploads a…

Secure, modular MCP server wrapping nmap, nuclei, gobuster, subfinder, httpx, nikto, sqlmap for AI-powered pentesting

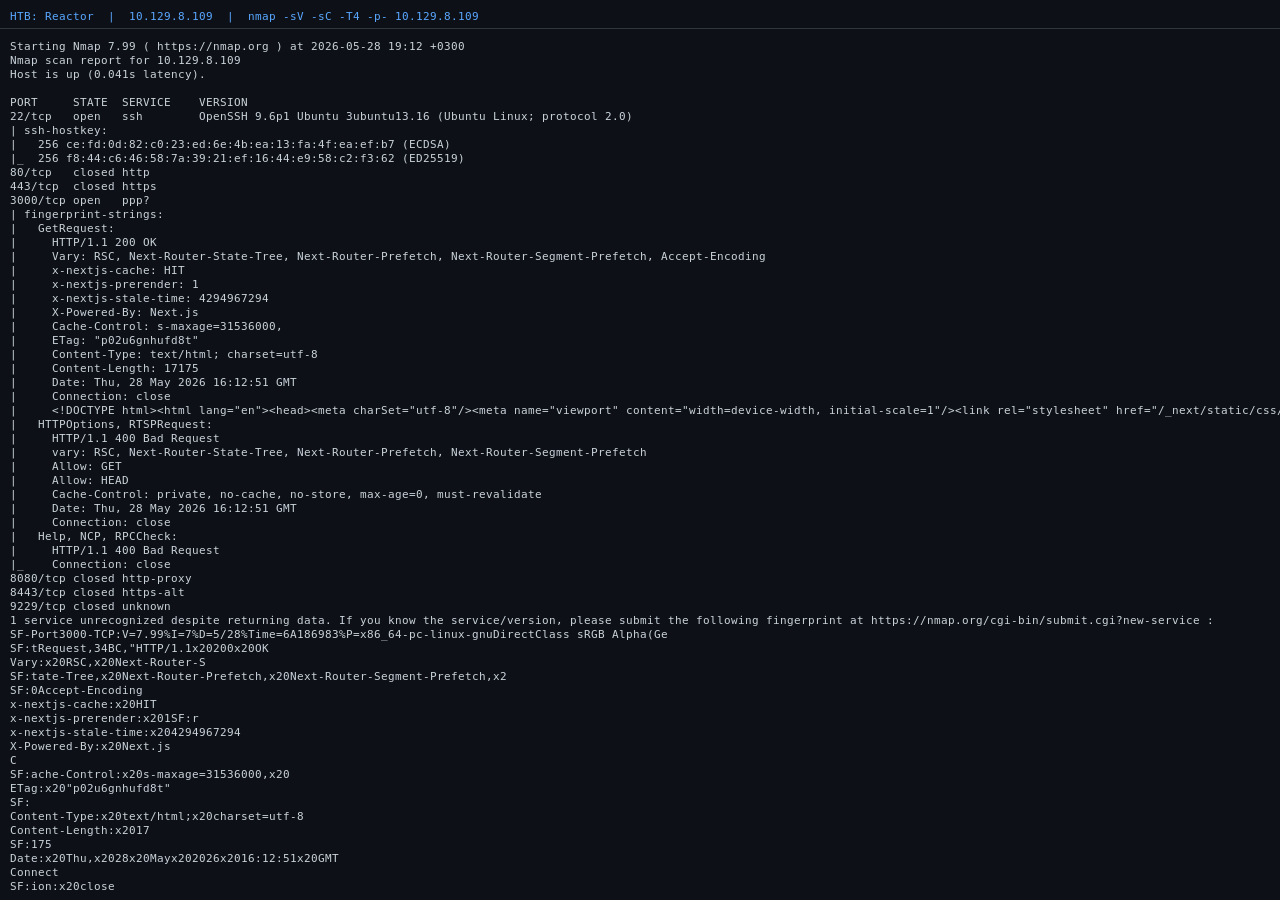
Full walkthrough of HTB's Reactor machine — exploit CVE-2025-55182 to gain a shell, then get root via an exposed Node.js debugger. Step-by-step with…