

Vigil
 vigiloss/vigil
AI harness for long-running code audits, web pentests, and bug bounty hunting, built around how real investigations fail: anchored hypotheses, false…
ai-securitycode-analysisexploitation+9
31
vigiloss/vigilAI harness for long-running code audits, web pentests, and bug bounty hunting, built around how real investigations fail: anchored hypotheses, false…

 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
 andresriancho/enumerate-iam
Enumerate the permissions associated with AWS credential set
 fckoo/nanwinata-cve-2024-52301
Scans for CVE-2024-52301, an argument injection vulnerability in Laravel, using subfinder and httpx to identify affected web applications.
 wattocyber/custom-oscp-tooling
OSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…
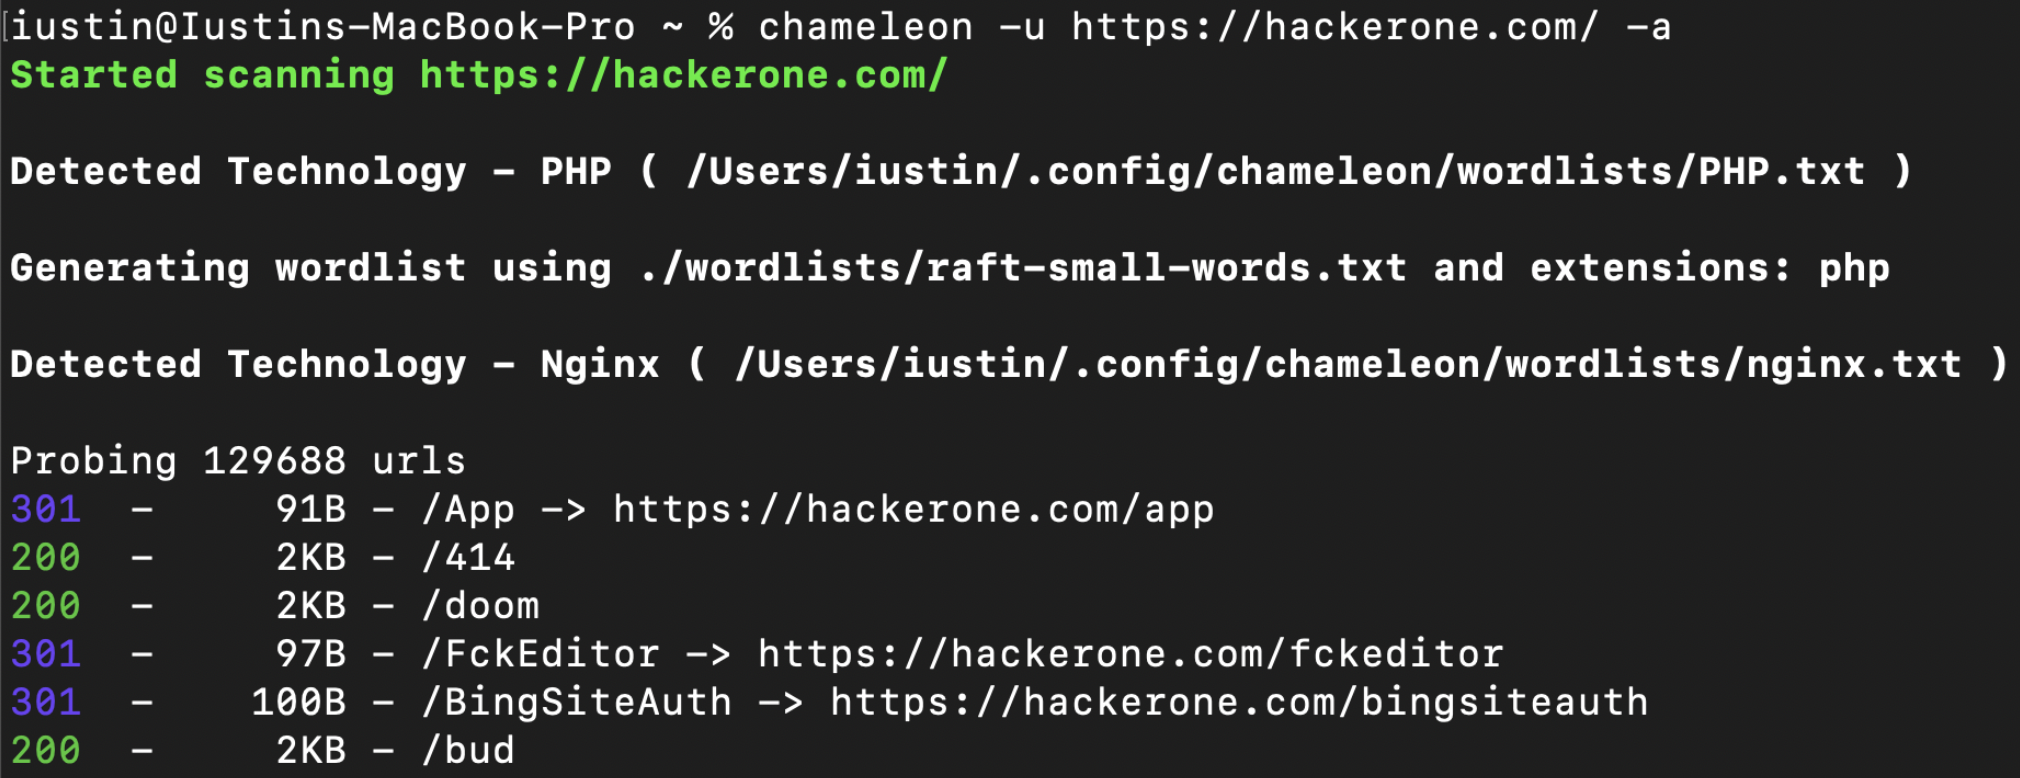 iustin24/chameleon
Technology-aware web content discovery scanner: detects Wappalyzer fingerprints, adapts wordlists/extensions, and performs fast directory bruteforce…
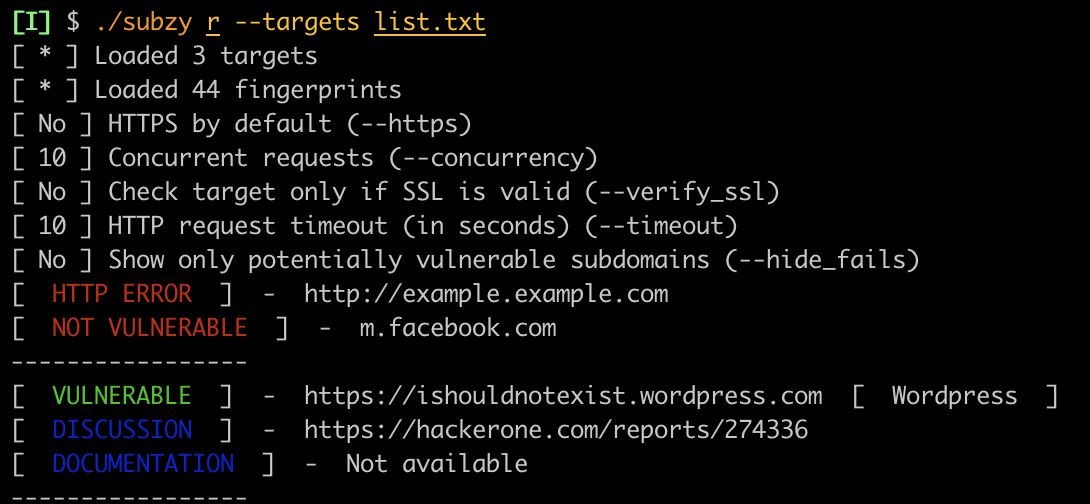 pentestpad/subzy
Subdomain takeover vulnerability checker
 nccgroup/upnp-pentest-toolkit
UPnP Pentest Toolkit for Windows
 pepelux/sippts
Set of tools to audit SIP based VoIP Systems
 projectdiscovery/chaos-client
Go client to communicate with Chaos DB API.
 moneertv/cve-2023-23397
CVE-2023-23397 C# PoC
 sardine-web/cve-2024-6387_check
A security regression (CVE-2006-5051) was discovered in OpenSSH's server (sshd). There is a race condition which can lead to sshd to handle some…
 nanaao/cve-2022-33891
PoC for CVE-2022-33891
 iveresk/cve-2022-1388-1veresk
Simple shell script for the exploit
 castaldio86/detect-cve-2019-19781
Detects if a server is vulnerable to CVE-2019-19781 by checking a specified IP address, providing a quick security assessment for this known…
 abdullahmaqbool22/explosive-as-hell-mcs-qualifer-web-500
[First-Blood-XO] React Server Component endpoint vulnerable to CVE-2025-55182 (RCE) → enumerated SUID binaries → /usr/bin/perl had SUID set → used…
 ransc0rp1on/icmp-timestamp-poc
A reconnaissance tool to detect CVE-1999-0524 (ICMP Timestamp Disclosure) by automating timestamp extraction via nping or hping3. Converts raw ICMP…
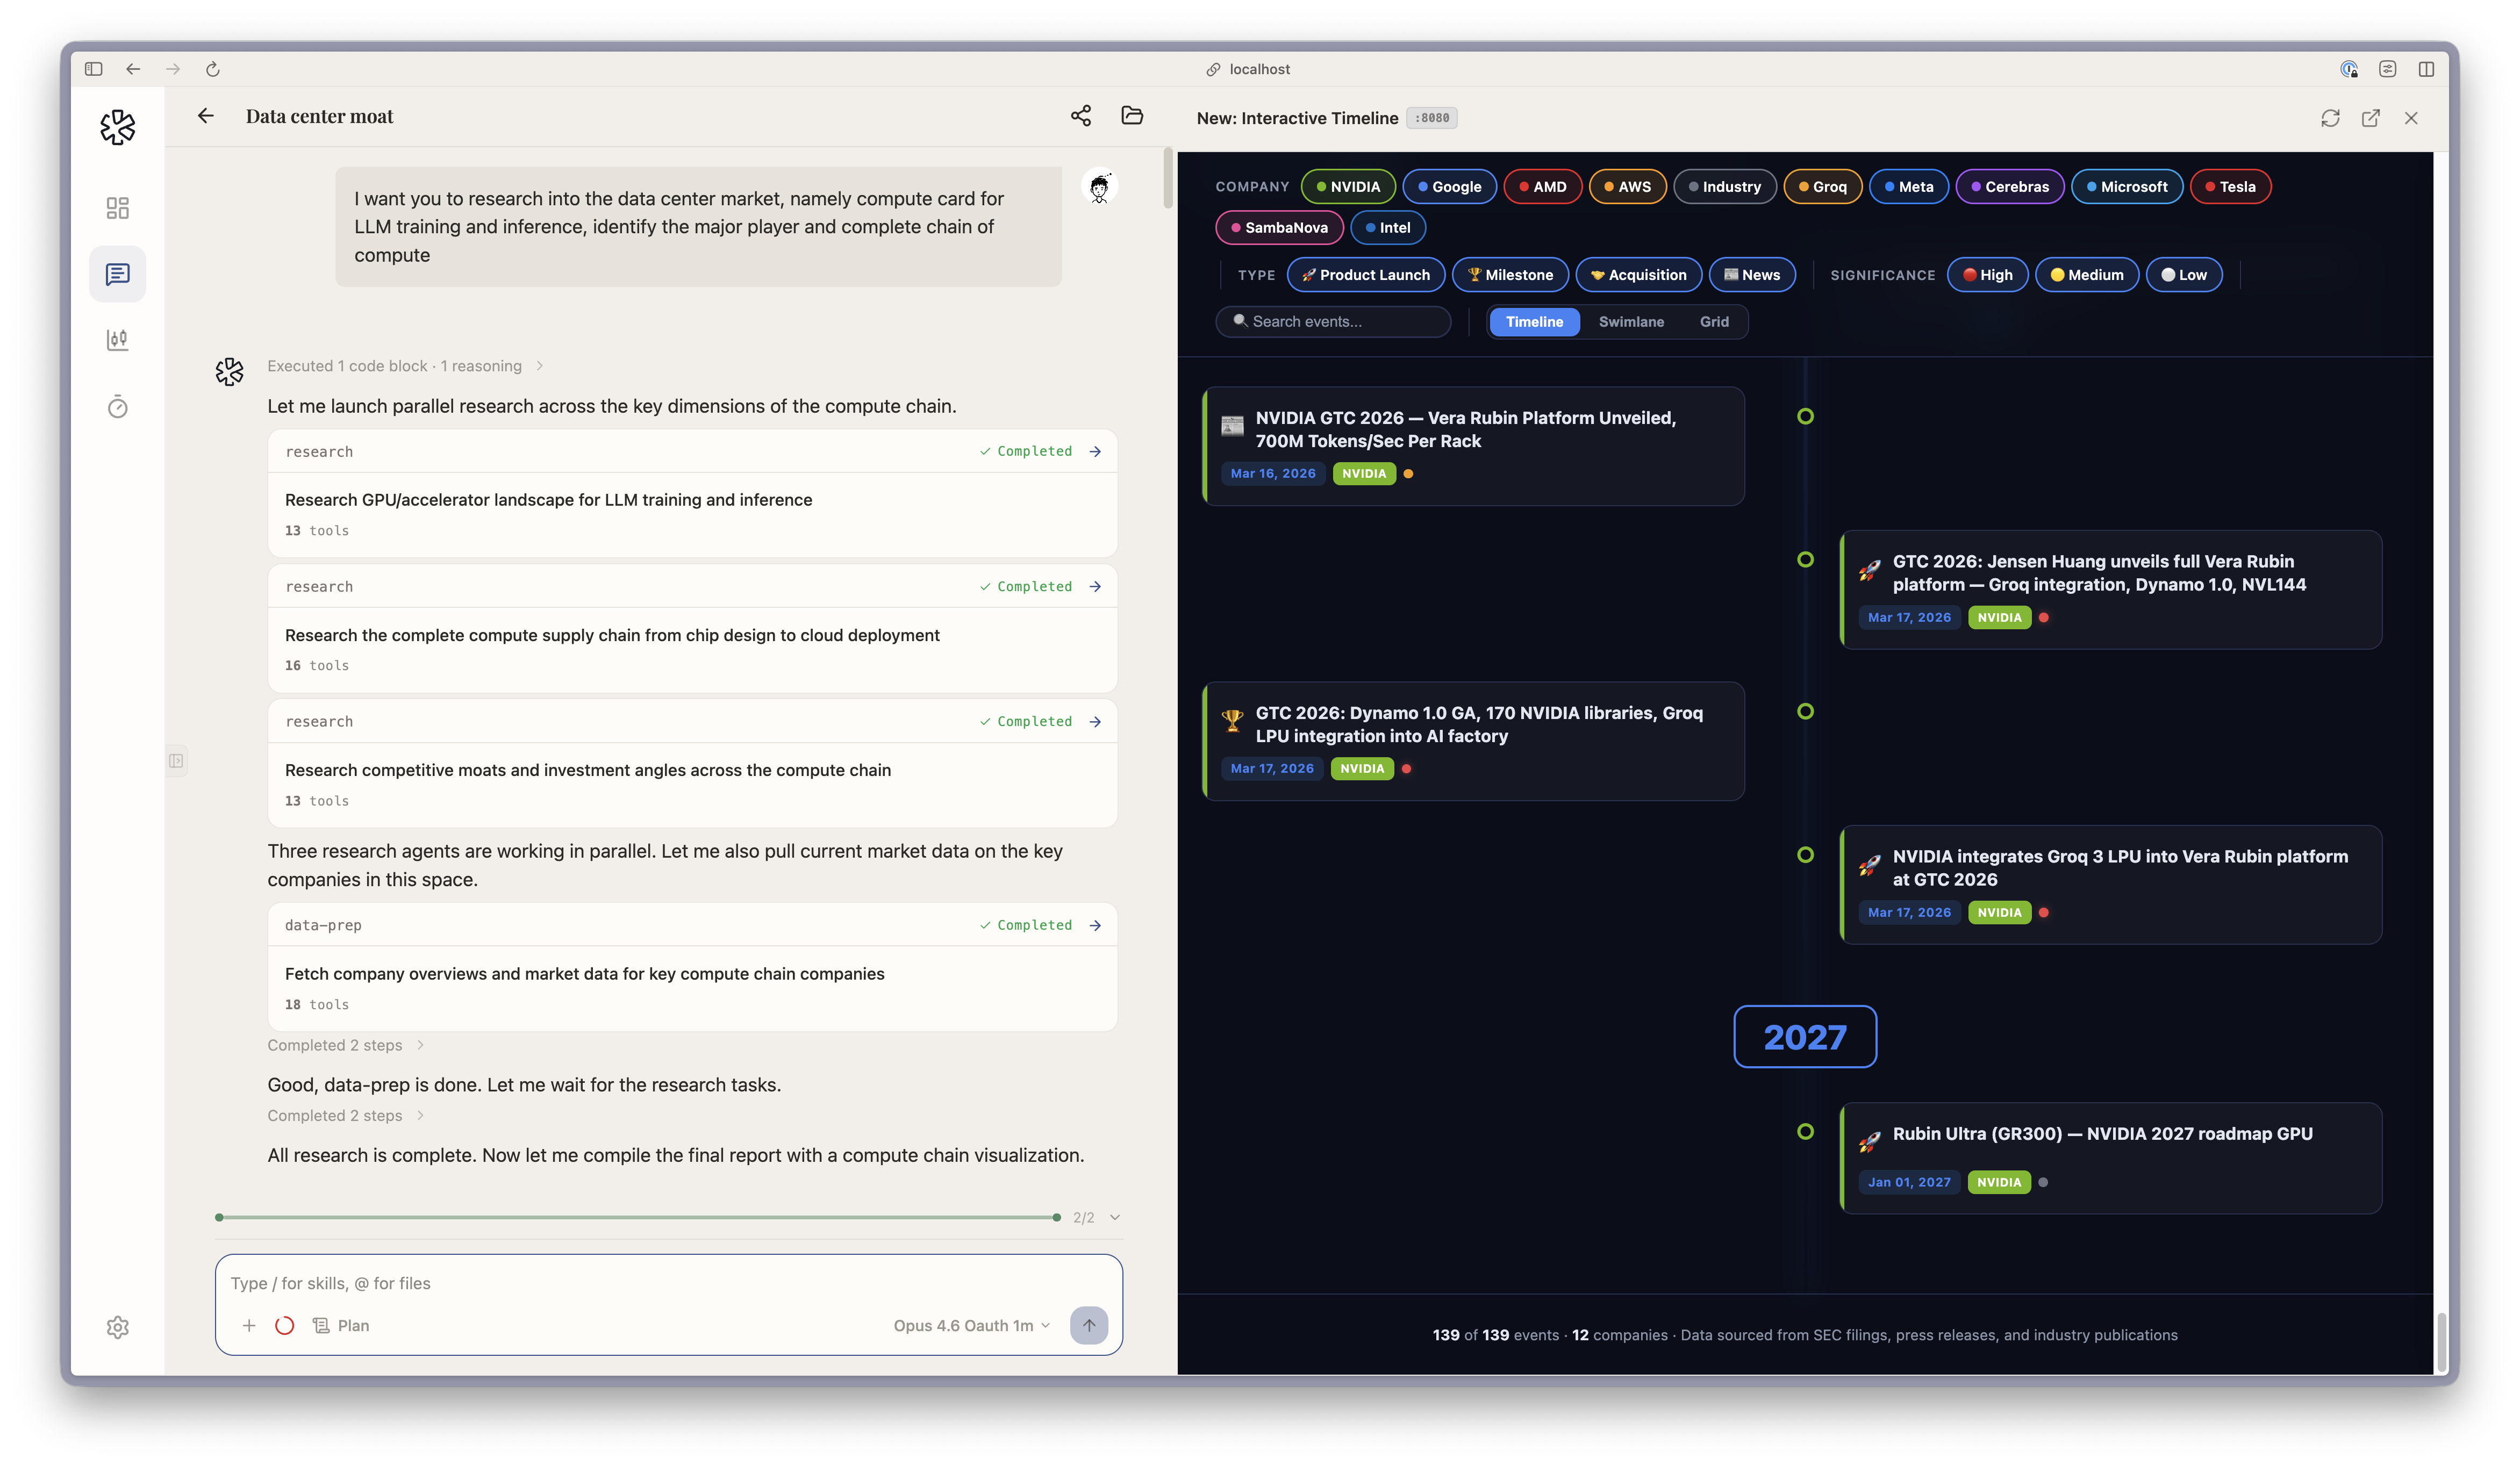 ginlix-ai/langalpha
Automated OSINT framework for reconnaissance, data harvesting, and threat intelligence gathering with modular crawlers, scanners, and extraction…