

bettercap
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
bluetooth-securitydata-exfiltrationfingerprint-spoofing+16
19.8k
bettercap/bettercapThe Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 buybitart/cyclepatrol
Bash tool for on-foot Wi-Fi security checks in a loop, with evidence reports. (re-invented wifi WarDriving)

 phantom-brigade1/wifisting
GTK4 and CLI wireless security toolkit with 57 standalone modules for Wi-Fi, Bluetooth, 802.15.4, SDR/RF, NFC and router-side or network MITM testing…
 emrekybs/signalops
All-source intelligence fusion dashboard — WiFi, cellular, CCTV, ADS-B, orbital & SDR feeds unified into a single tactical map. Security research…
 ghostop14/sparrow-wifi
Next-Gen GUI-based WiFi and Bluetooth Analyzer for Linux
 wiglenet/wigle-wifi-wardriving
Nethugging client for Android, from wigle.net
 ets-polito/esp32-sniffer
ESP32 firmware that sniffs PROBE REQUEST packets sent by smartphones searching for Wi-Fi connection to extract different types of information
 h9zdev/wiretapper
Passive wireless OSINT platform that detects and maps Wi-Fi, Bluetooth, CCTV, IoT devices, and cell towers using radio signal intelligence for…
 skyplabs/probequest
Toolkit for Playing with Wi-Fi Probe Requests
 veteranop/trackem
Passive Device Tracker (Android)TrackEm Mobile is a real-time, passive Wi-Fi + Bluetooth LE probe-request scanner designed for OSINT, red-team ops,…
 momenbasel/autowifi
Wireless penetration testing framework. Automates WPA/WPA2/WEP/WPS attacks - recon to exploitation in one command. aircrack-ng + hashcat + PMKID.
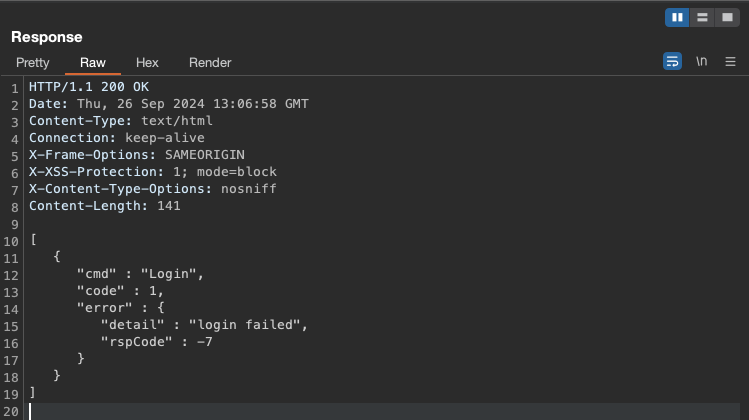 rosembergpro/cve-2024-48644
Reolink Duo 2 WiFi v1.0.280 - Account Enumeration Vulnerability
 rfidtool/esp-rfid-tool
A tool for logging data/testing devices with a Wiegand Interface. Can be used to create a portable RFID reader or installed directly into an existing…
 calebmadrigal/trackerjacker
Like nmap for mapping wifi networks you're not connected to, plus device tracking
 tw-d/wifi-pineapple-mk7_rest-client
WiFi Hacking Workflow with WiFi Pineapple Mark VII API
 riccardocataldi/access-point
Rogue open Wi-Fi AP for controlled traffic capture using hostapd, dnsmasq, and iptables NAT. Enables real-time client monitoring, DNS/DHCP logging,…
 ottoyrocky/phantom-brain
Red portatil de reconocimiento inteligente con IA offline
 xdavidhu/probesniffer
🔍 A tool for sniffing unencrypted wireless probe requests from devices.