
CVE-2024-23897-Arbitrary-file-read
 pulentoski/cve-2024-23897-arbitrary-file-read
Un script realizado en python para atumatizar la vulnerabilidad CVE-2024-23897
exploitationinformation-gatheringpenetration-testing+3
1
pulentoski/cve-2024-23897-arbitrary-file-readUn script realizado en python para atumatizar la vulnerabilidad CVE-2024-23897
 brutelogic/unkover
Bash 403/401 access bypass tester that probes a URL with header spoofing, method tampering, path normalization, and encoding techniques, returning a…
 quantika14/email-osint-ripper
EO-RIPPER.PY es una herramienta que nos permite hacer OSINT con un email o con una lista de emails.
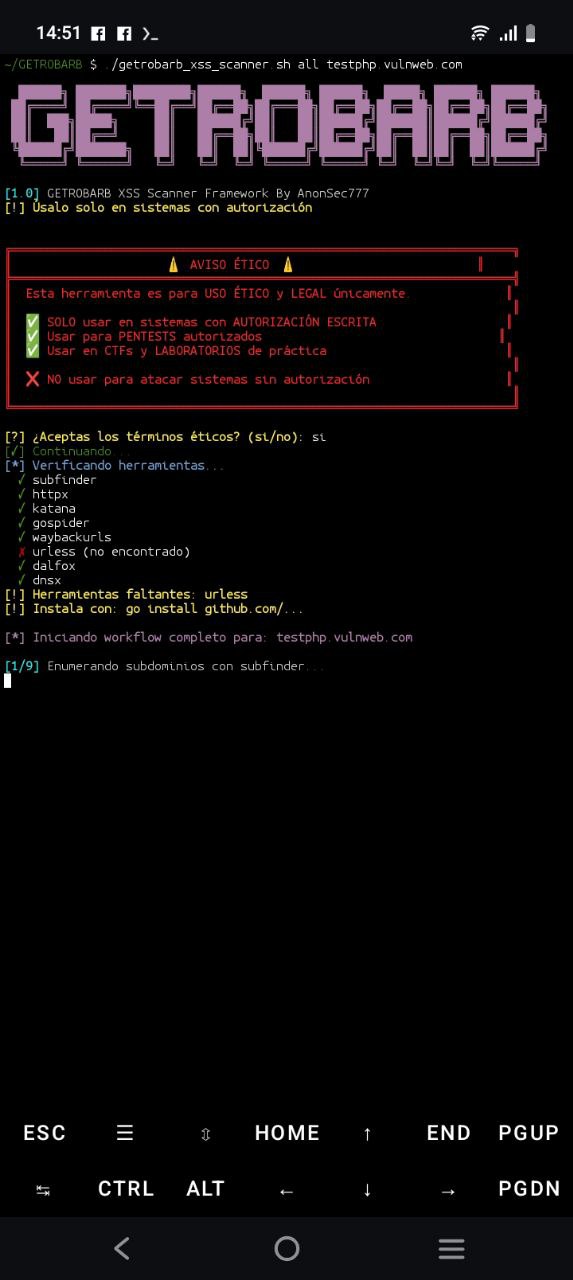 hackingteamoficial/getrobarb
Automated reconnaissance and XSS detection framework integrating subfinder, httpx, katana, gospider, waybackurls, and dalfox into a 9-stage pipeline…
 infobyte/emploleaks
An OSINT tool that helps detect members of a company with leaked credentials
 theresafewconors/sooty
The SOC Analysts all-in-one CLI tool to automate and speed up workflow.
 quantika14/osint-suite-tools
Repositorio del conjunto de herramientas para hacer OSINT y SOCMINT con Dante's Gates Minimal Version.
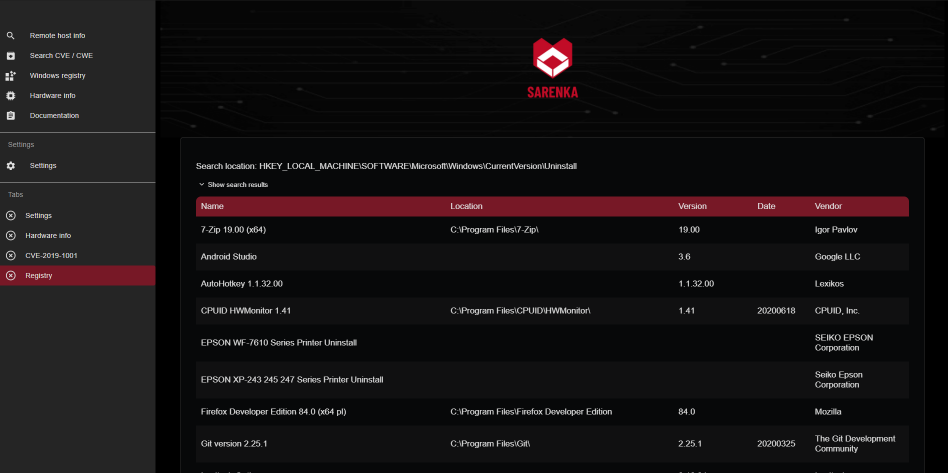 ktzgraph/sarenka
OSINT tool - gets data from services like shodan, censys etc. in one app
 tg12/phantomstars
Automated detection and tracking of fake engagement on GitHub — daily CI, zero infrastructure
 makavellik/poc-cve-2021-42013-exploit
Una herramienta avanzada de escaneo, explotación e interacción remota diseñada para detectar y aprovechar la vulnerabilidad Apache Path Traversal +…
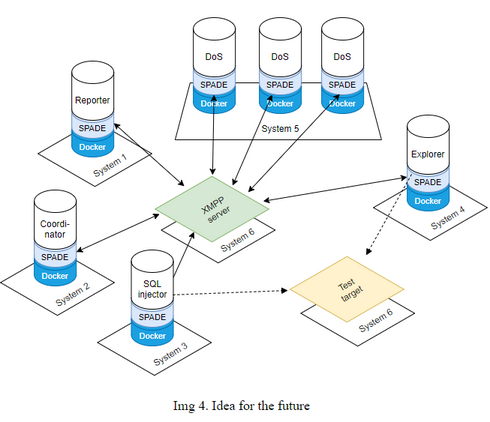 marzekan/masapt
Multi-Agent System for Automated Penetration Testing (MASAPT)
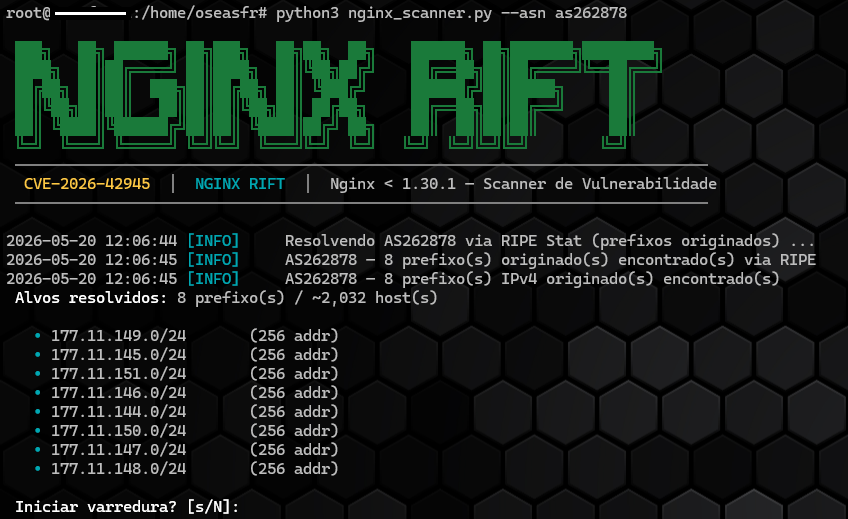 oseasfr/scanner_cve_2026-42945
Script Python para detecção de instâncias Nginx vulneráveis ao CVE-2026-42945 em IPs, CIDRs e ASNs.
 fevar54/marimo_cve-2026-39987_rce_poc
PoC de CVE-2026-39987: RCE pre-autenticacion via WebSocket en Marimo menor a 0.23.0 (CVSS 9.3).
 ccob/gssapi-abuse
A tool for enumerating potential hosts that are open to GSSAPI abuse within Active Directory networks
 jheeree/simple-cve-2021-41773-checker
Simple script realizado en bash, para revisión de múltiples hosts para CVE-2021-41773 (Apache)