
 oseasfr/scanner_cve_2026-42945
Script Python para detecção de instâncias Nginx vulneráveis ao CVE-2026-42945 em IPs, CIDRs e ASNs.


Scanner for detecting Nginx instances vulnerable to CVE-2026-42945 (NGINX RIFT).
Accepts individual IPs, CIDR ranges, and ASNs as input.
CVE-2026-42945 affects all Nginx versions prior to 1.30.1.
The tool probes HTTP and HTTPS on default ports, reads the Server header from the response, and classifies each host as vulnerable, safe, or potentially affected (hidden version).
Results are saved to a log, with a list of hosts vulnerable to the CVE and a detailed .CSV file at the end.
pip install requests packaging urllib3 dnspython
# Single IP
python nginx_scanner.py --ip 93.184.216.34

# CIDR range
python nginx_scanner.py --cidr 10.0.0.0/24

# Multiple CIDRs
python nginx_scanner.py --cidr 10.0.0.0/24 192.168.1.0/24

# ASN (originated prefixes resolved via RIPE Stat, fallback to bgp.tools)
python nginx_scanner.py --asn AS15169

# Combination of inputs
python nginx_scanner.py --asn AS13335 --cidr 10.0.0.0/8 --ip 1.2.3.4

# From a file (one IP, CIDR or ASN per line)
python nginx_scanner.py --file targets.txt
Example IP SCAN:

Example CIDR SCAN:

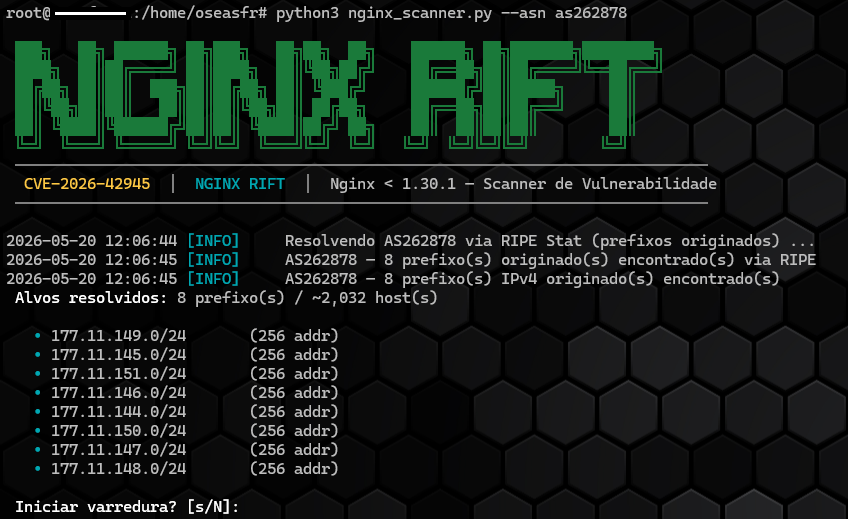
Example ASN SCAN:
| Parameter | Default | Description |
|---|---|---|
--workers | 60 | Number of simultaneous threads for the HTTP scan |
--timeout | 2.0 | HTTP request timeout in seconds |
--dns-workers | 200 | Number of simultaneous threads for reverse DNS resolution |
--dns-timeout | 1.5 | DNS query timeout in seconds |
--no-confirm | — | Skip confirmation before starting (useful in automation) |
DNS resolution is executed in batch before the HTTP scan, using a dedicated thread queue (
--dns-workers), preventing DNS latency from impacting scan performance.
All results are written to ./logs/:
| File | Content |
|---|---|
nginx_scan_<timestamp>.log | Full scan log |
nginx_scan_<timestamp>_vulneraveis.txt | Only vulnerable hosts |
nginx_scan_<timestamp>_resultados.csv | All hosts with status |
| Status | Meaning |
|---|---|
VULNERABLE | Confirmed version below 1.30.1 |
SAFE | Confirmed version 1.30.1 or higher |
WARNING (Hidden Version) | Nginx detected but version not exposed — not confirmed safe |
INDETERMINATE | Version could not be interpreted |
Update Nginx to version 1.30.1 or higher using the official nginx.org repository.
# Ubuntu / Debian
curl https://nginx.org/keys/nginx_signing.key | gpg --dearmor \
  | tee /usr/share/keyrings/nginx-archive-keyring.gpg >/dev/null

echo "deb [signed-by=/usr/share/keyrings/nginx-archive-keyring.gpg] \
http://nginx.org/packages/mainline/ubuntu $(lsb_release -cs) nginx" \
  | tee /etc/apt/sources.list.d/nginx.list

echo -e "Package: *\nPin: origin nginx.org\nPin-Priority: 900" \
  | tee /etc/apt/preferences.d/99nginx

apt update && apt install --only-upgrade nginx
nginx -v
For other distributions, consult the official Nginx documentation.
This script is intended for use on your own infrastructure or under explicit authorization.
Unauthorized scanning may violate various laws, so use with caution.
If you have any suggestions for feature improvements or bugs, feel free to open an issue and send me a Pull Request.
All contributions are welcome! 🚀🚀






