

custom-oscp-tooling
 wattocyber/custom-oscp-tooling
OSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…
database-securitydns-analysishash-analysis+9
wattocyber/custom-oscp-toolingOSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…

 s0md3v/sqlmate
A friend of SQLmap which will do what you always expected from SQLmap.
 trustedsec/ridenum
Rid_enum is a null session RID cycle attack for brute forcing domain controllers.
 nu11secur1ty/insect
High-performance web path discovery and directory brute-forcing tool. Discovers hidden files, directories, and endpoints using customizable…
 artemy-ccrsky/cve-2024-39211
User Enumeration vulnerability in Kaiten (workflow management system)

 theresafewconors/sooty
The SOC Analysts all-in-one CLI tool to automate and speed up workflow.
 n0kovo/domaindouche
OSINT tool abusing SecurityTrails domain suggestion API to find potentially related domains by keyword and brute force.
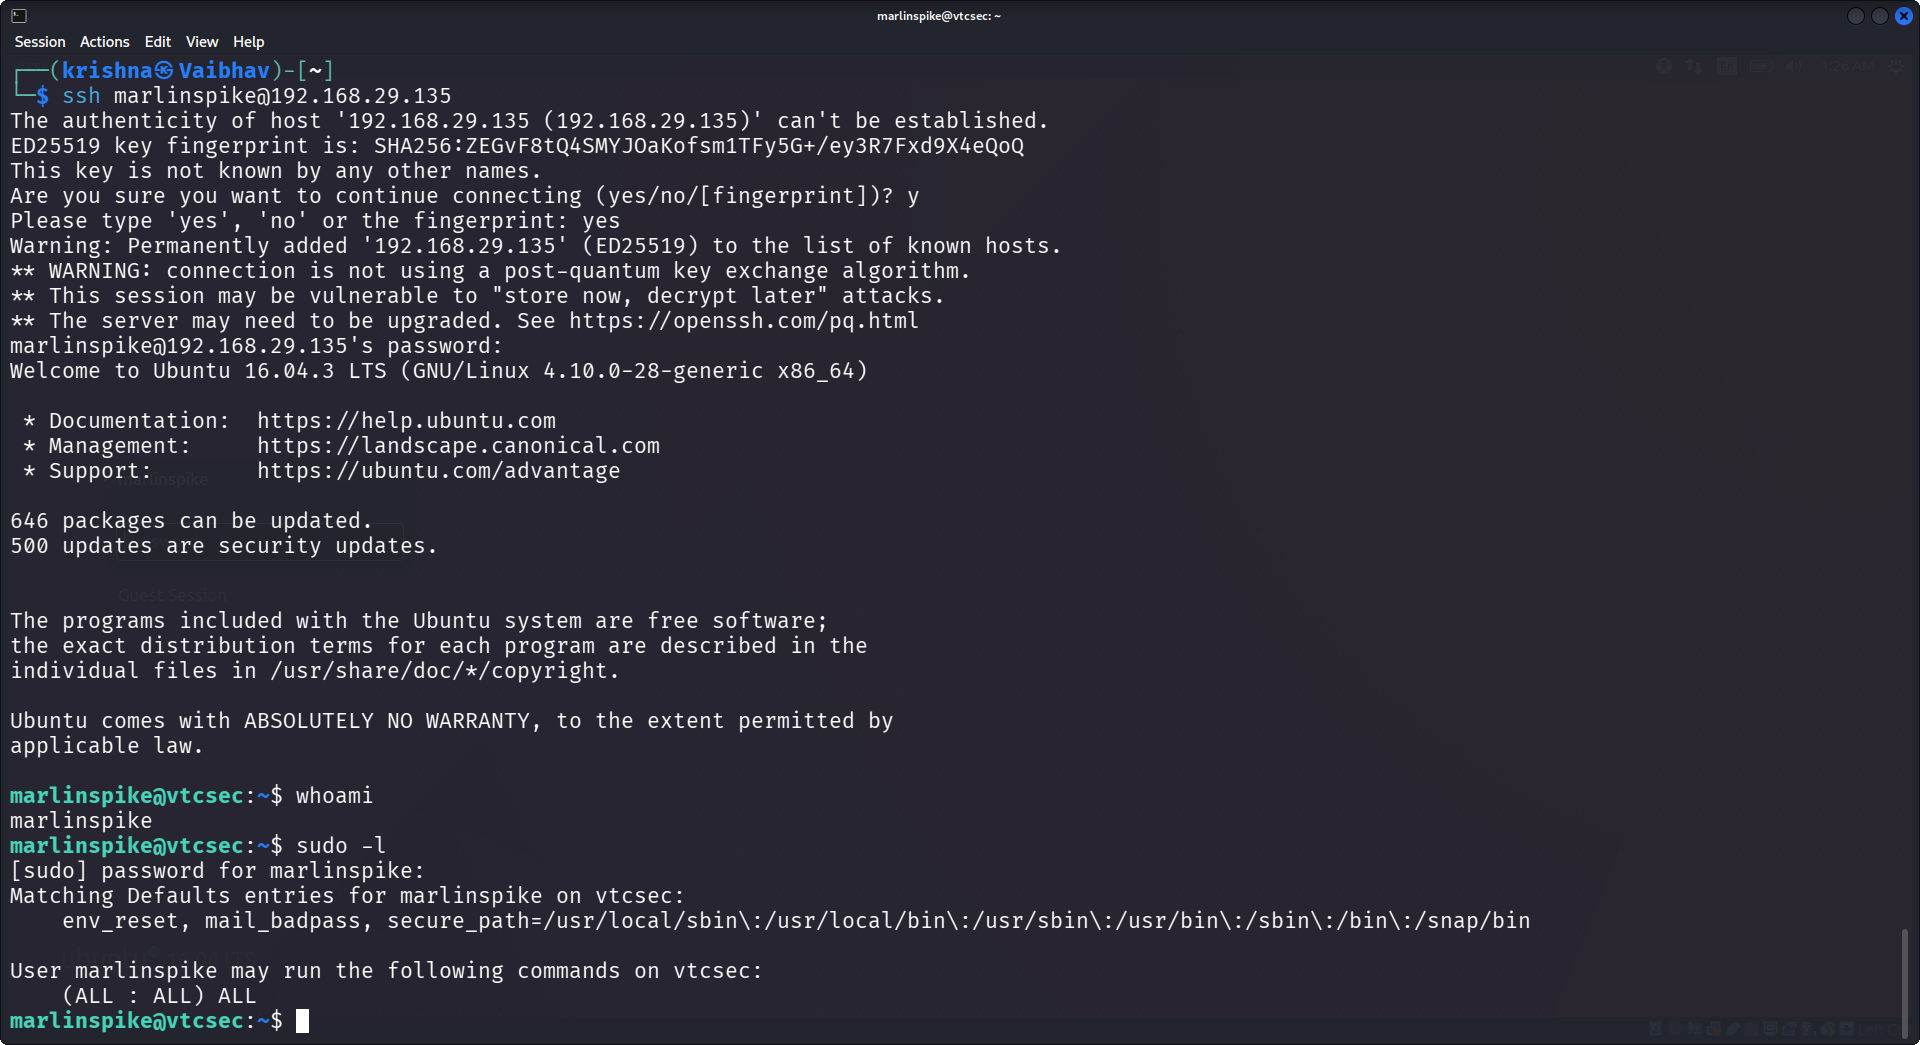 vaibhavkrishna12004/ubuntu-privesc-lab
Full penetration testing workflow: credential brute force, SSH access and privilege escalation (CVE-2021-4034)
 0xdea/tactical-exploitation
Modern tactical exploitation toolkit.
 guelfoweb/knockpy
Knock Subdomain Scan
 danmcinerney/icebreaker
Gets plaintext Active Directory credentials if you're on the internal network but outside the AD environment
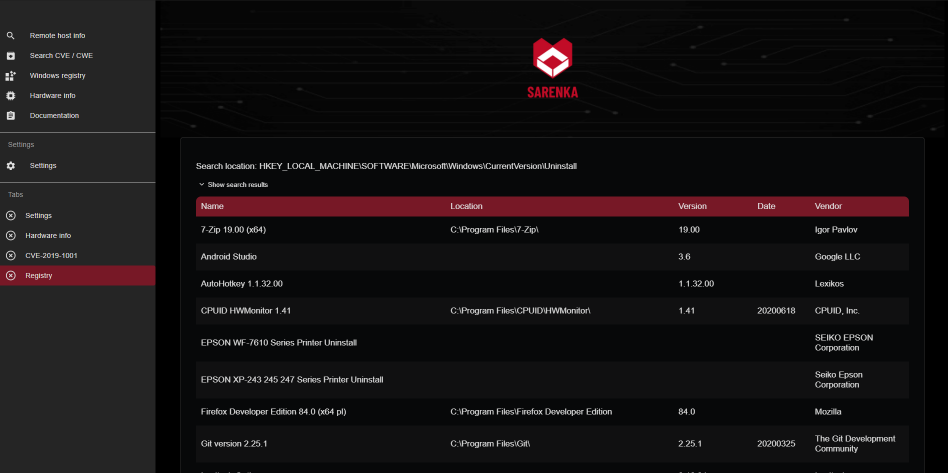 ktzgraph/sarenka
OSINT tool - gets data from services like shodan, censys etc. in one app
 darryllane/bluto
DNS Recon | Brute Forcer | DNS Zone Transfer | DNS Wild Card Checks | DNS Wild Card Brute Forcer | Email Enumeration | Staff Enumeration |…
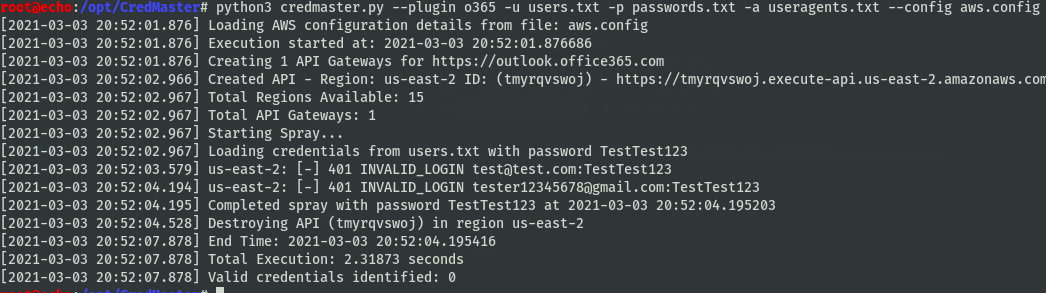 knavesec/credmaster
Refactored & improved CredKing password spraying tool, uses FireProx APIs to rotate IP addresses, stay anonymous, and beat throttling
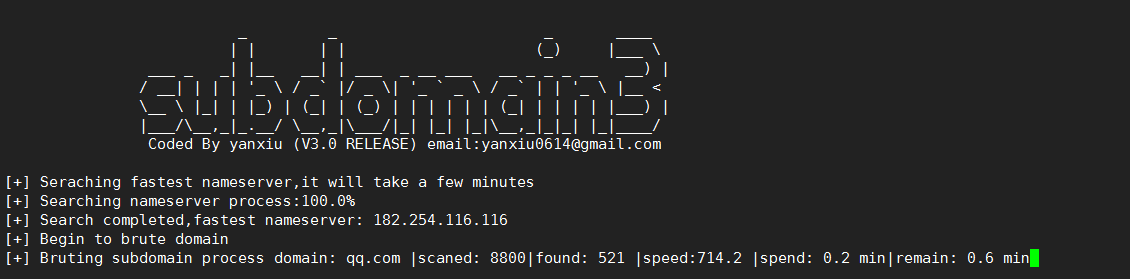 yanxiu0614/subdomain3
A new generation of tool for discovering subdomains( ip , cdn and so on)