

akca
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
api-security-testingdefensive-toolsdynamic-analysis-sandboxing+9
242
akha-security/akcaEvidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 vavkamil/awesome-bugbounty-tools
Curated directory of bug bounty tools organized by category: reconnaissance, subdomain enumeration, port scanning, content discovery, exploitation,…

 trustedsec/spoonmap
Python wrapper around masscan and nmap for large-scale port discovery, host discovery, banner grabbing, and NSE-based vulnerability scanning across…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 xalgorix/xalgorix
Autonomous AI pentesting agents — real-time reconnaissance, vulnerability detection, and exploitation orchestration. Go + TypeScript.
 blackhatexploitation/exploit-mikrotik-2026
CVE-2026-67276 MikroTik RouterOS SSH Authentication Bypass Exploit
 wpscanteam/wpscan
WordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…

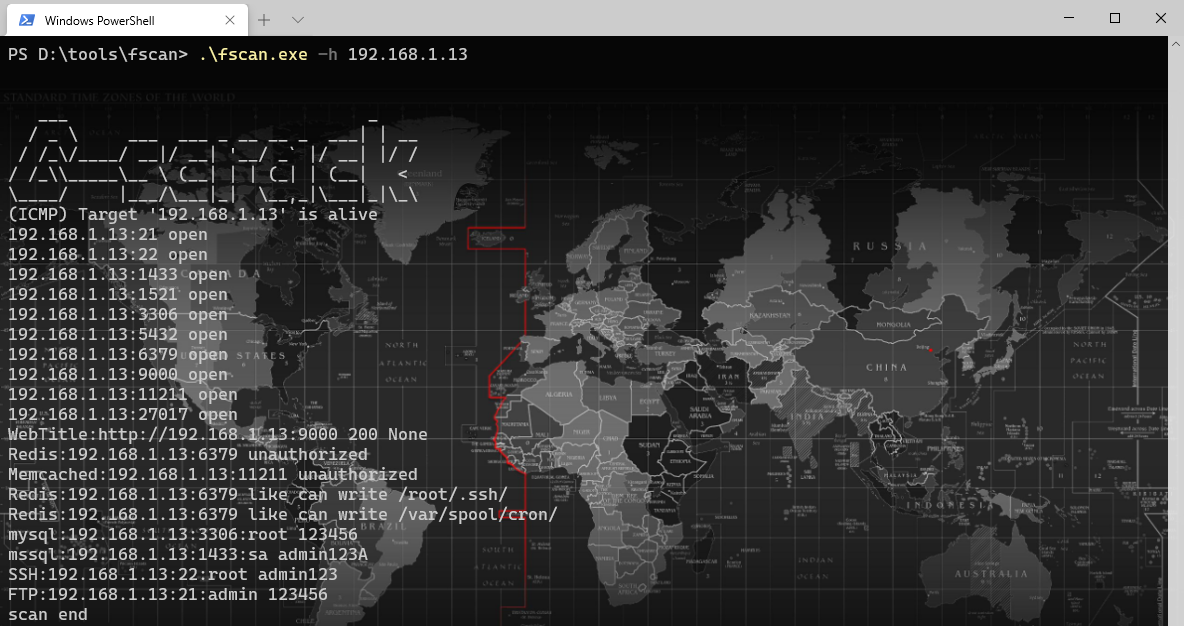 shadow1ng/fscan
一款内网综合扫描工具,方便一键自动化、全方位漏扫扫描。(An intranet comprehensive scanning tool, enabling one-click automated, all-round vulnerability scanning)
 sleepingbag945/dddd
Batch asset collection and vulnerability scanning tool for red teams. Pulls targets from Hunter, Fofa, and Quake, performs fingerprinting, subdomain…
 caybermods/cve-2026-22812-poc
Python tool to check and exploit CVE-2026-22812 in OpenCode, supporting command execution, file read, and multi-target scanning on ports 4095-4100.
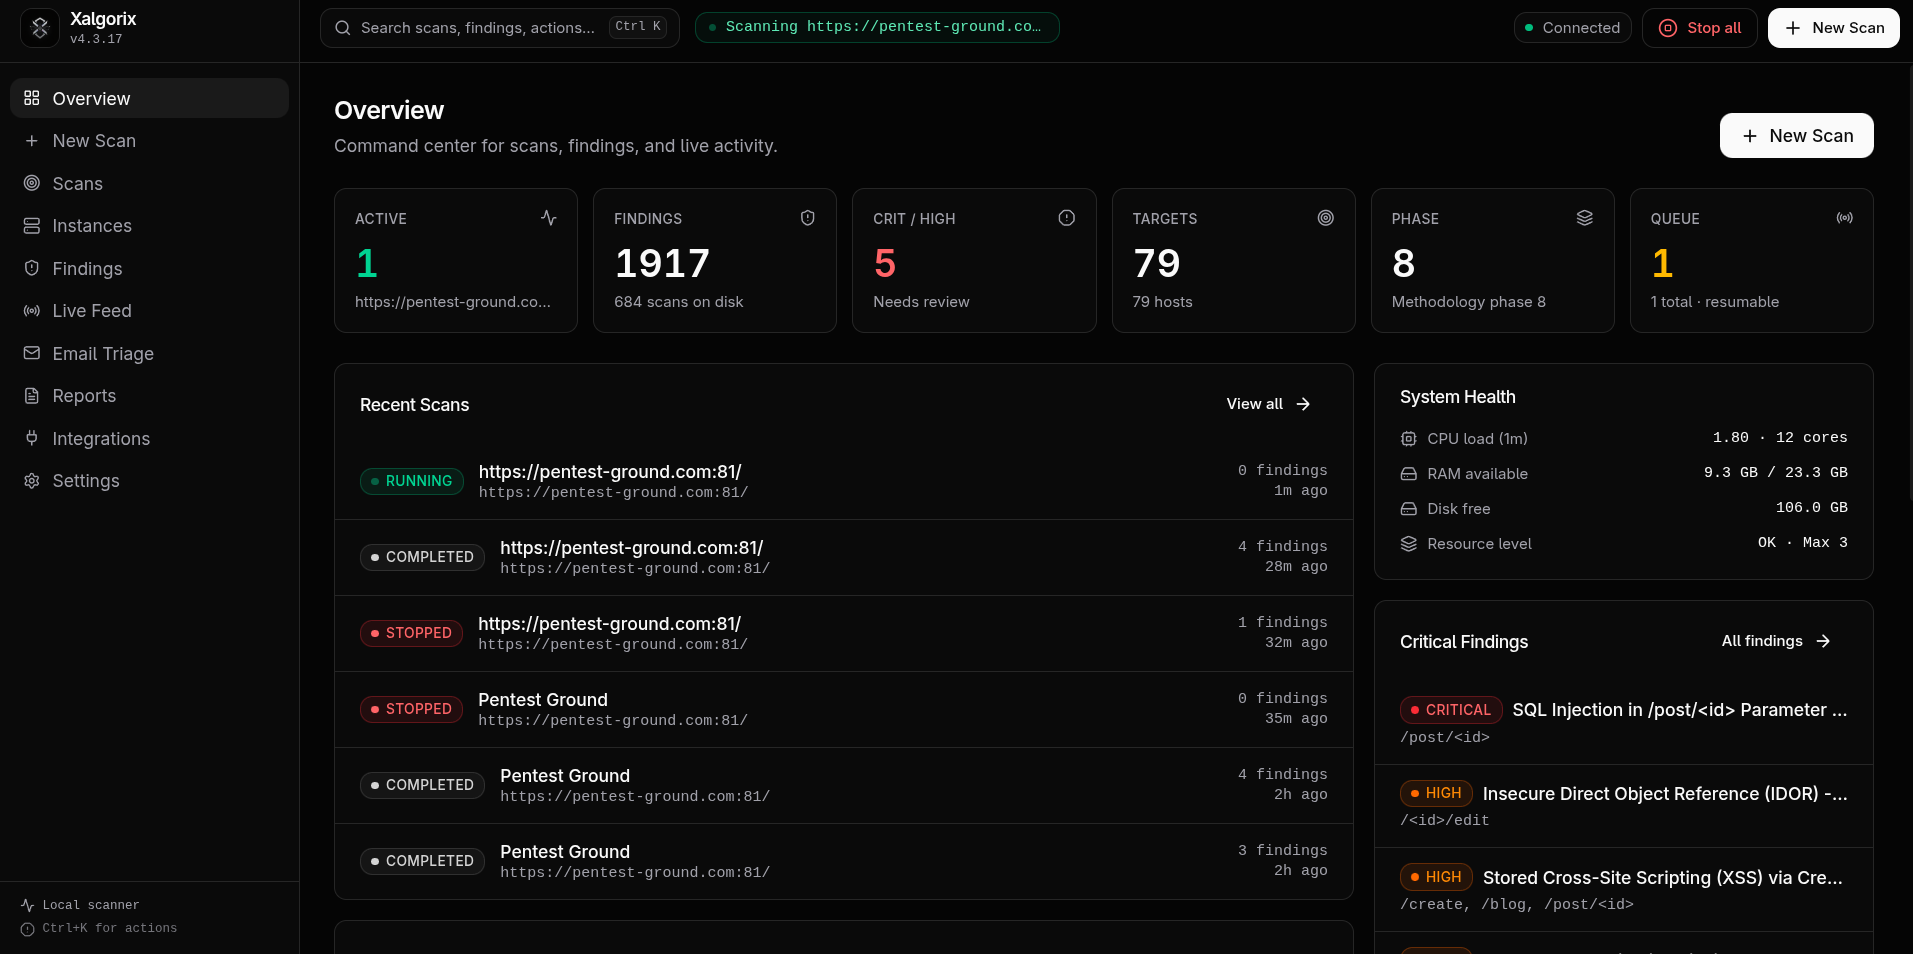 xalgord/xalgorix
Autonomous AI pentesting agents — real-time reconnaissance, vulnerability detection, and exploitation orchestration. Go + TypeScript.
 owasp/nettacker
Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management
 yashas-13/pentx-vapt-skill
Open-source AI-powered 5-phase VAPT pentest agent — recon/scan/vuln/exploit/report with PoC
 edoardottt/awesome-hacker-search-engines
A curated list of awesome search engines useful during Penetration testing, Vulnerability assessments, Red/Blue Team operations, Bug Bounty and more
 87achrafg-stack/cve-2026-6279
Proof-of-concept or exploit implementation for CVE-2026-6279, providing vulnerability validation for security researchers and penetration testers.
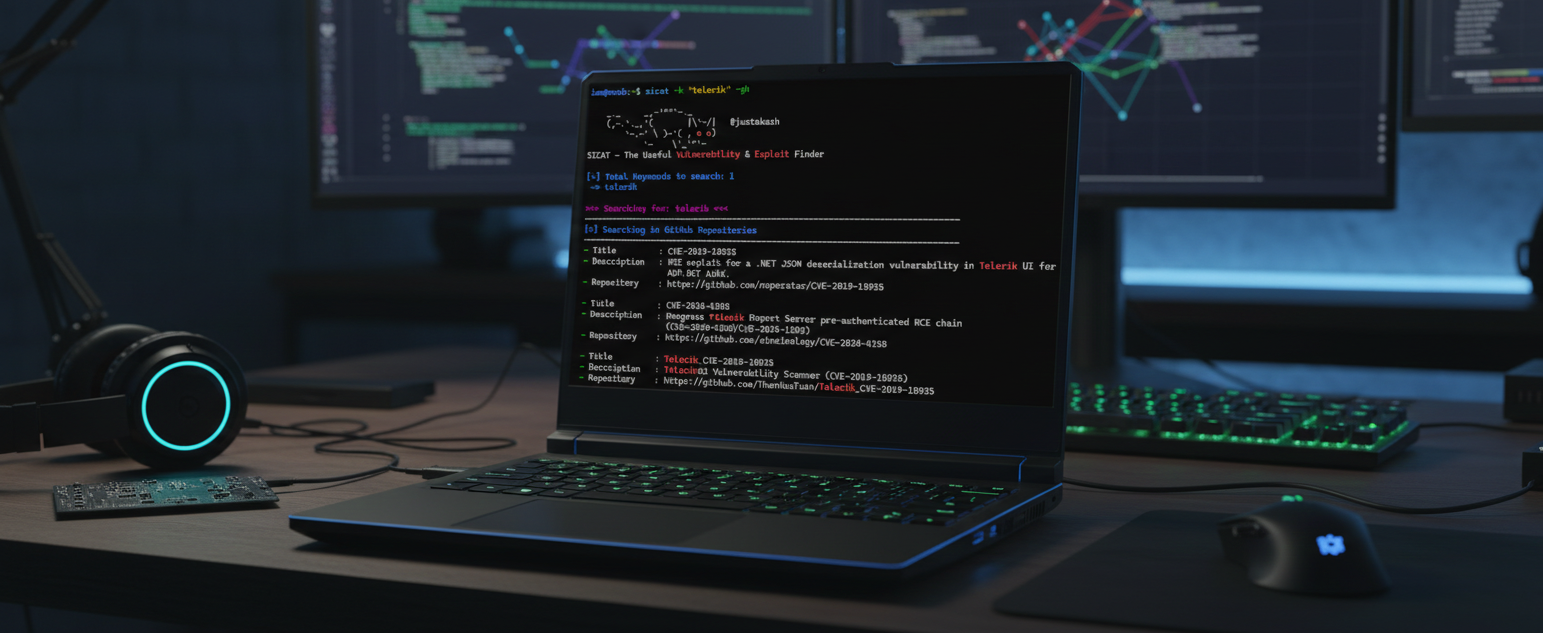 justakazh/sicat
Multi-source vulnerability and exploit aggregator with auto-discovery via Nmap and Wappalyzer, searching Exploit-DB, NVD, CVE.org, GitHub, Nuclei,…