
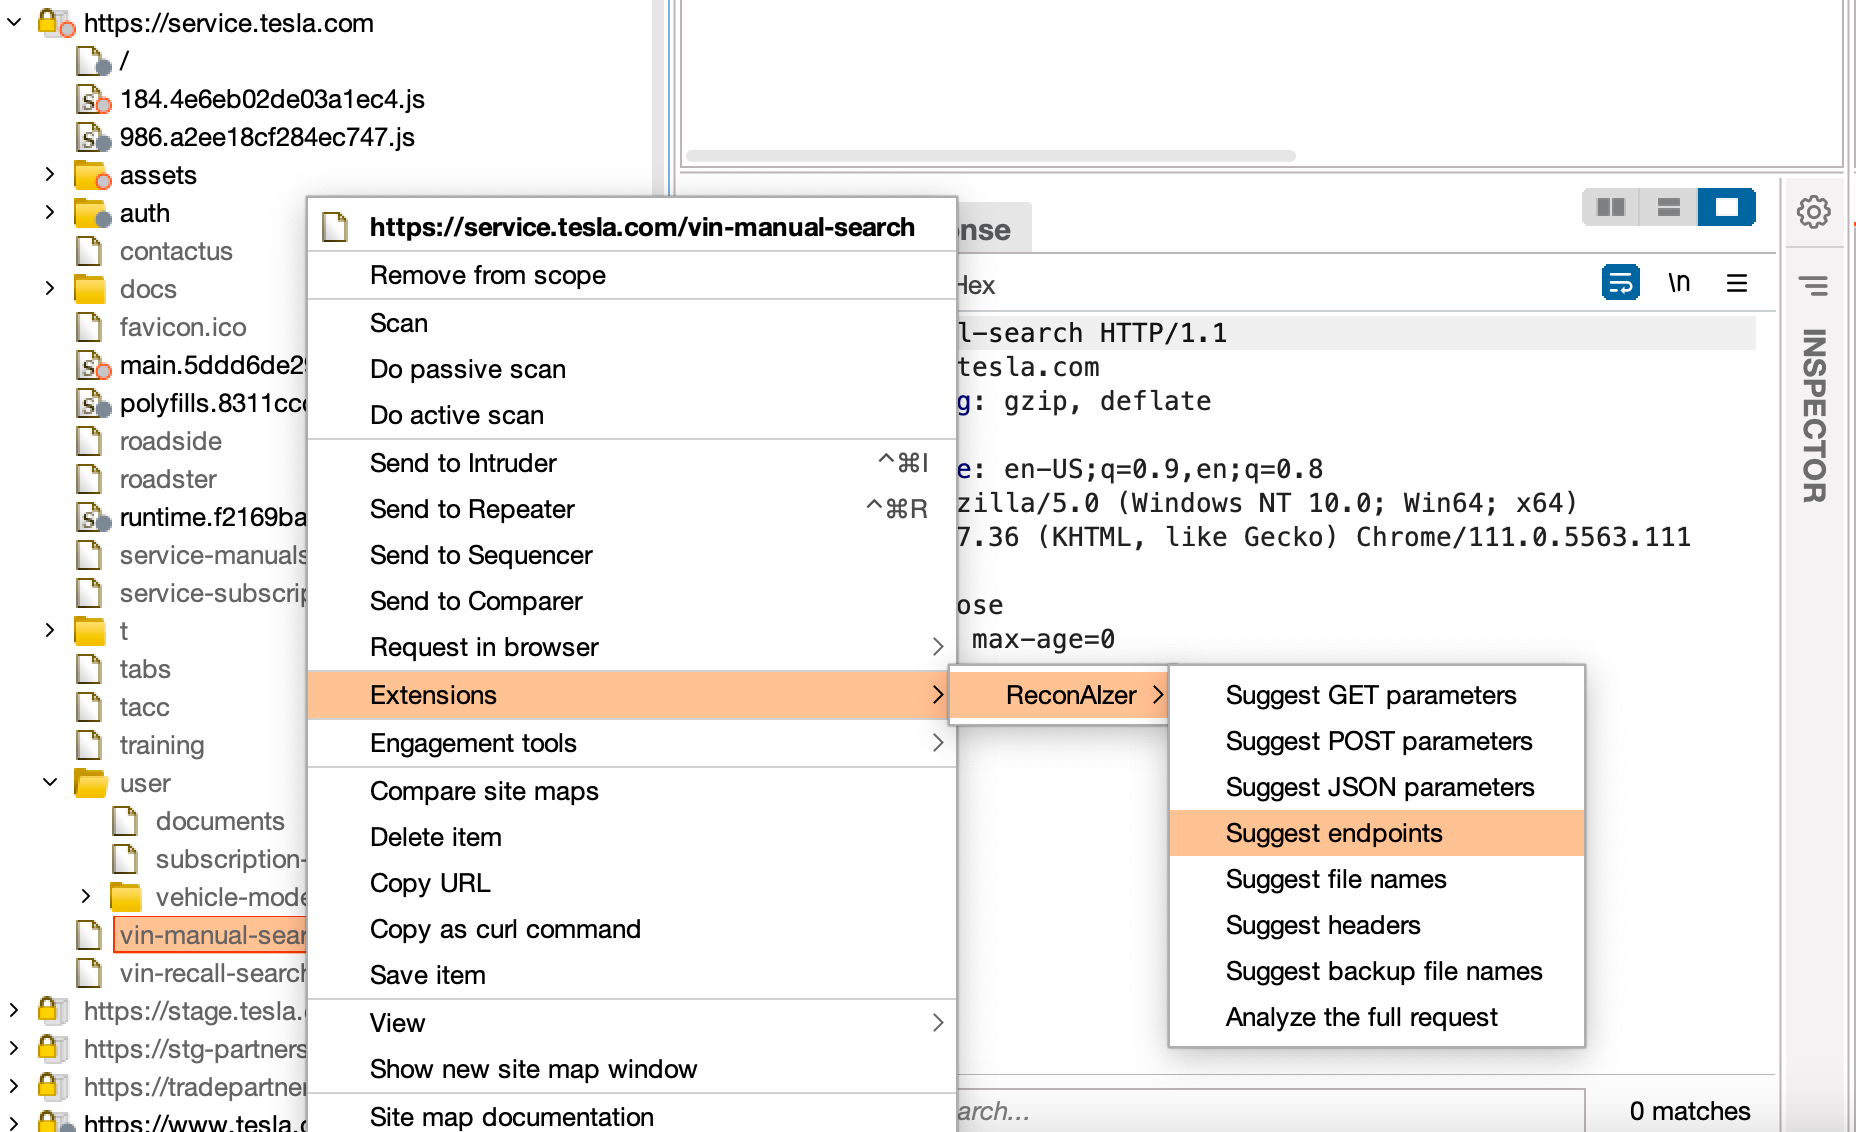
ReconAIzer
 hisxo/reconaizer
A Burp Suite extension to add OpenAI (GPT) on Burp and help you with your Bug Bounty recon to discover endpoints, params, URLs, subdomains and more!
ai-securityinformation-gatheringreconnaissance+1
907
hisxo/reconaizerA Burp Suite extension to add OpenAI (GPT) on Burp and help you with your Bug Bounty recon to discover endpoints, params, URLs, subdomains and more!
 moeinfatehi/admin-panel_finder
Burp Suite extension that finds exposed admin panels and login pages of web applications and infrastructure. 1,000+ payloads, OWASP WSTG-CONF-05.
 hoodoer/js-tap
JavaScript beacons and C2 to be used for XSS payload or post exploitation implants on webapp servers or desktop software to monitor users and…
 0x999-x/jsluicepp
jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice
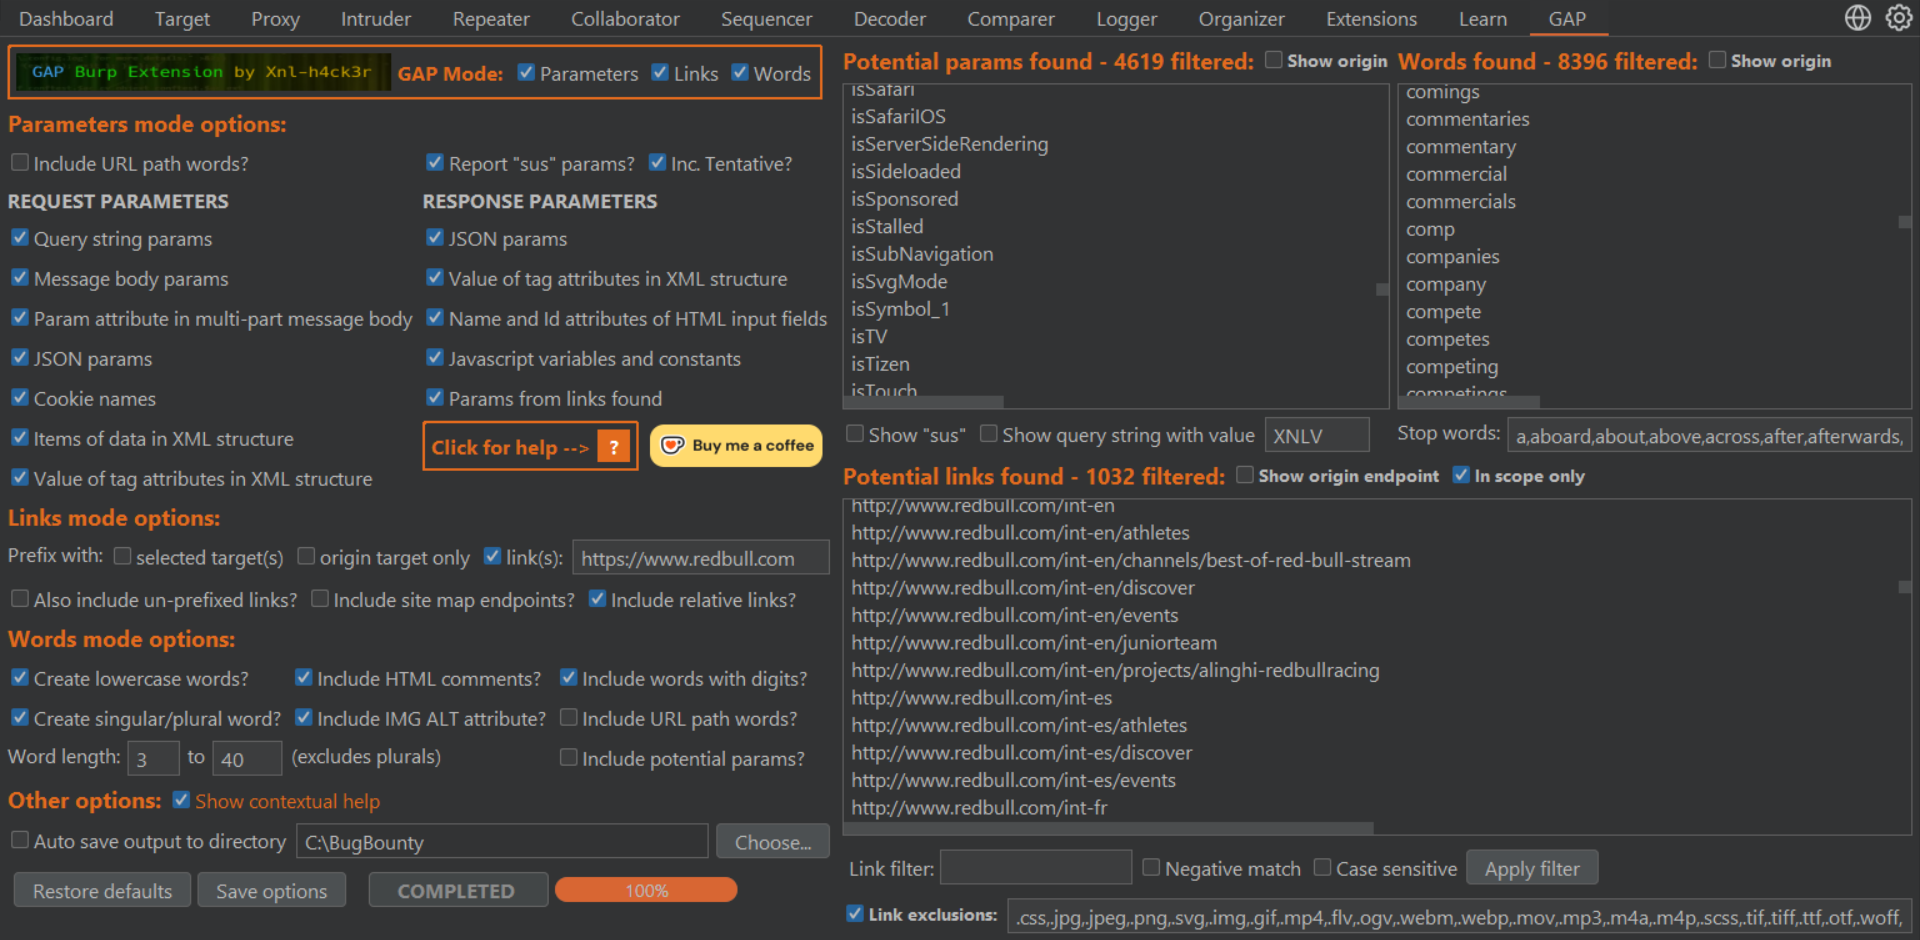 xnl-h4ck3r/gap-burp-extension
Burp Extension to find potential endpoints, parameters, and generate a custom target wordlist
 4ier/neo
Turn any web app into an API. Chrome extension captures browser traffic, auto-generates schemas, lets AI replay APIs directly. No official API needed.
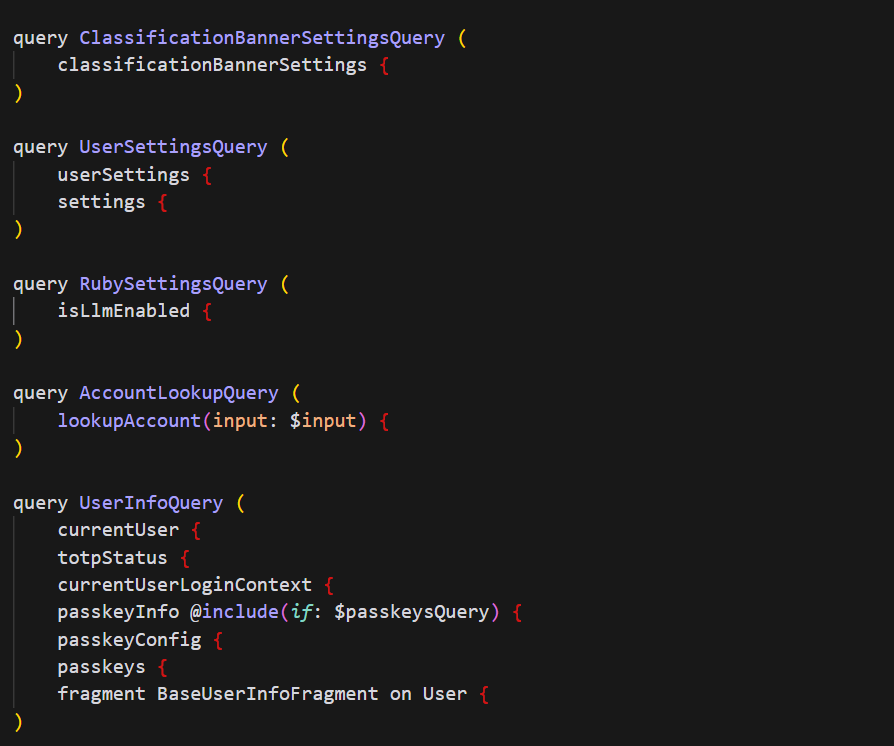 m19o/graphqlgrapper
Burp Suite extension to extract and collect GraphQL API endpoints from HTTP request history for security testing and reconnaissance.
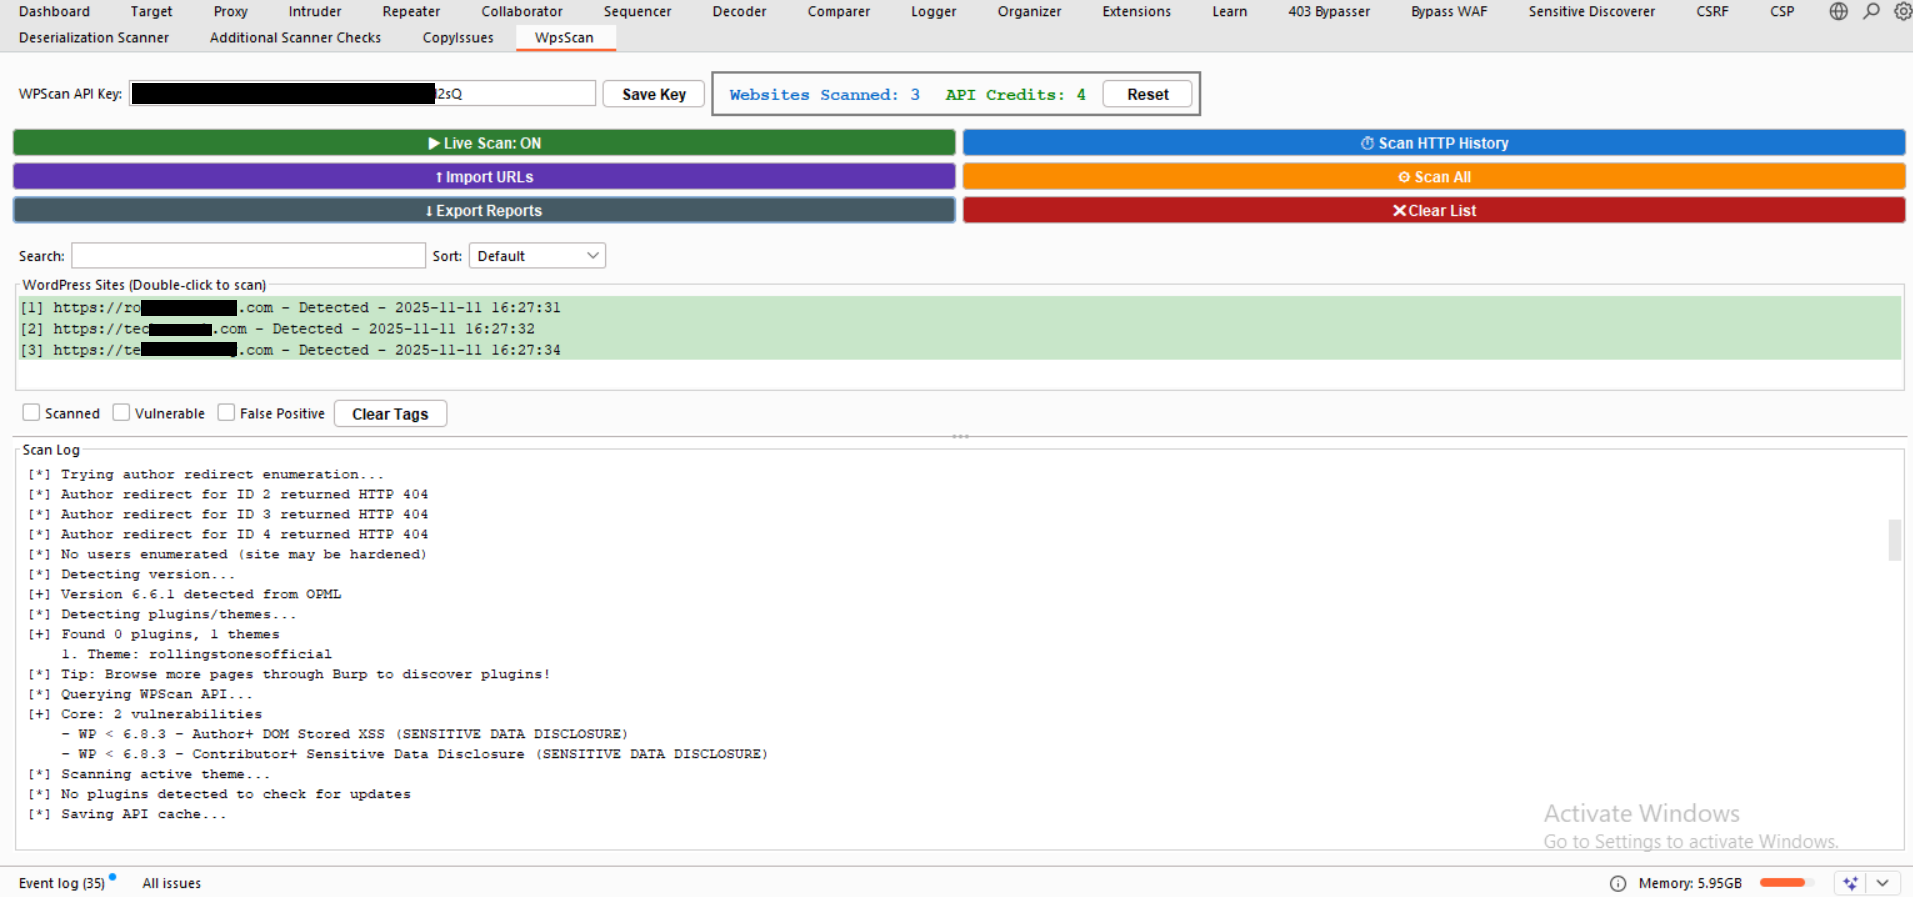 teycir/burpwpsscan
Burp extension for wordpress security scanning
 shinthink/pbck-exploit
📤 Mass exploitation framework for CVE-2026-56290 — Page Builder CK Joomla unauthenticated file upload to RCE
 oscar-mine/r2sae
Firefox extension for detecting and exploiting CVE-2025-55182 — Prototype Pollution RCE in Next.js React Server Actions
 alfazhossain/cve-2025-55182-exploiter
CVE-2025-55182-Exploiter Google Chrome Extension. nextjs vulnerability #nextjscve
 tiger-foxx/exploit-react-cve-2025-55182
This tool is a Proof of Concept (PoC) intended for security research and educational purposes only. Using this tool on systems without explicit…
 j0lt-github/react2shell-burp
Burp Suite extension for detecting CVE-2025-55182 (React2Shell) unsafe deserialization vulnerability. Features safe digest check, PoC redirect mode,…