

WinPwn
 s3cur3th1ssh1t/winpwn
Automation for internal Windows Penetrationtest / AD-Security
exploitationpenetration-testingpenetration-testing-frameworks+4
3.7k1 year ago
s3cur3th1ssh1t/winpwnAutomation for internal Windows Penetrationtest / AD-Security
 foxglovesec/potato
Windows local privilege escalation exploit using NBNS spoofing, fake WPAD proxy, and HTTP-to-SMB NTLM relay to gain NT AUTHORITY\SYSTEM access.
 yeeb1/socktail
Lightweight Go binary that joins a device to a Tailscale network and exposes a local SOCKS5 proxy for ephemeral red team access. Supports…
 mythicagents/medusa
Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…
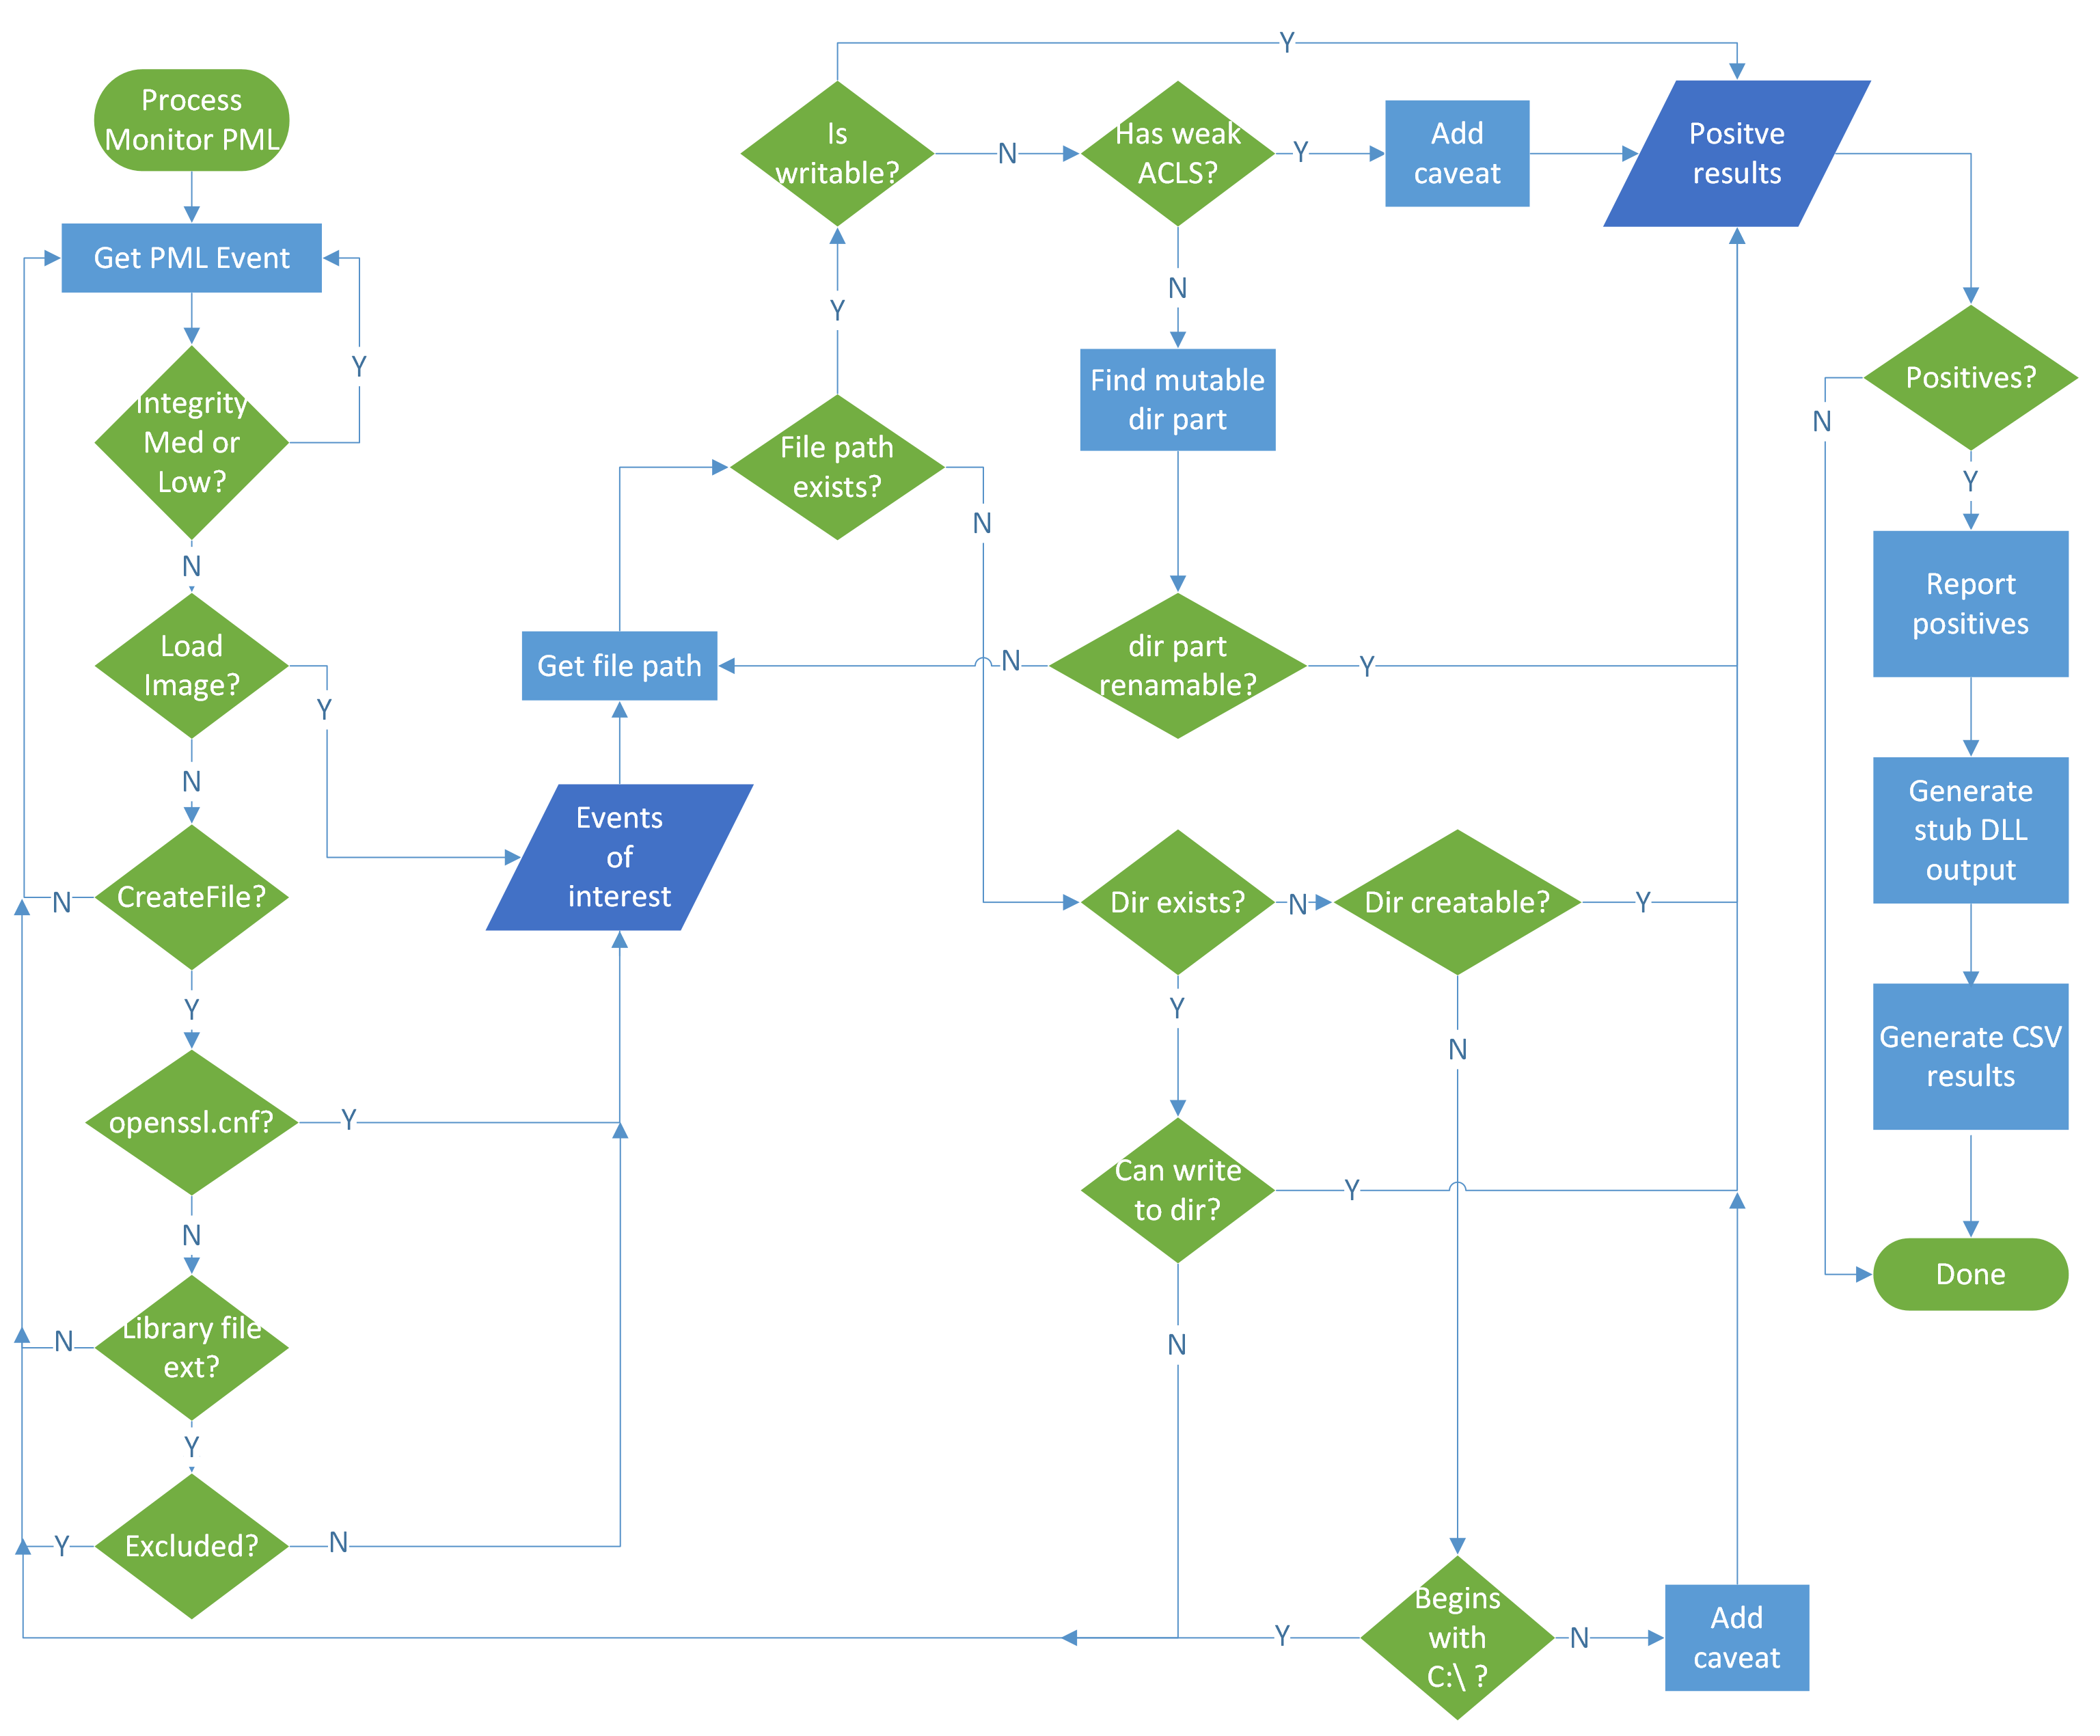 vu-ls/crassus
Windows privilege escalation discovery tool that parses Process Monitor boot logs to identify DLL hijacking, weak ACLs, and other elevation paths,…
 calligraf0/cve-2024-0311
Proof-of-concept exploit for CVE-2024-0311 bypassing Skyhigh Client Proxy policy via process injection and named pipe manipulation, with custom…
 gosecure/wsuspicious
Local privilege escalation tool exploiting insecure WSUS connections on Windows via a man-in-the-middle proxy, enabling command execution with SYSTEM…
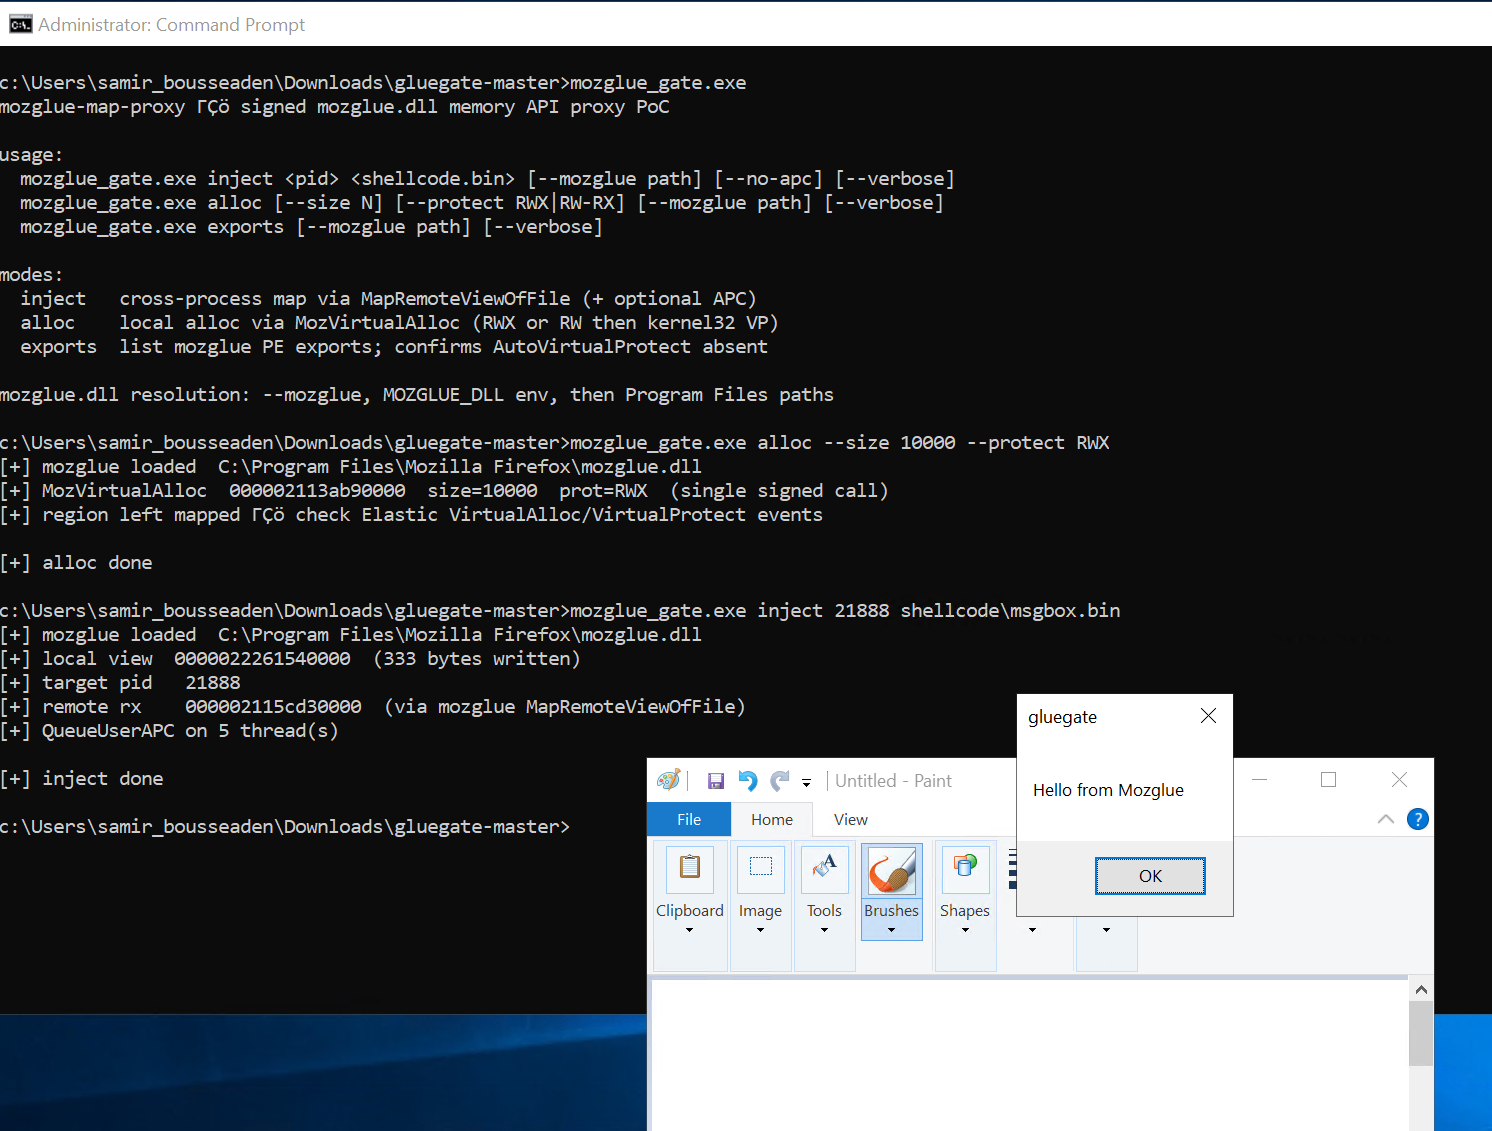 sbousseaden/gluegate
Memory API proxy via signed mozglue.dll
 sammyenigma/cve-2026-43499-s26
Android GKI 6.12 kernel exploit for CVE-2026-43499, chaining an rt_mutex rollback bug with pselect stack overwrite to gain root on Samsung and Pixel…
 cobbr/elite
Elite is the client-side component of the Covenant project. Covenant is a .NET command and control framework that aims to highlight the attack…
 7h30th3r0n3/cve-2026-53625-glpi-poc
GLPI Privilege Escalation via authtype Manipulation PoC - CVE-2026-53625. Ethical PoC for the GLPI vulnerability allowing a Technician to take full…
 filipegaudard/cve-2026-30944-poc
Python proof-of-concept for CVE-2026-30944, exploiting a BOLA vulnerability in StudioCMS to escalate privileges via insecure API token generation.
 google/path-auditor
Runtime libc function auditor that detects file access race conditions and symlink vulnerabilities by hooking filesystem syscalls via LD_PRELOAD,…
 ghostvectoracademy/dllhijackhunter
Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.
 abubakar-shahid/cve-2024-36886
Academic research on N-Day Linux kernel vulnerabilities, analyzing CVE-2024-36886 in the TIPC networking subsystem, lifecycle, impact, and mitigation…
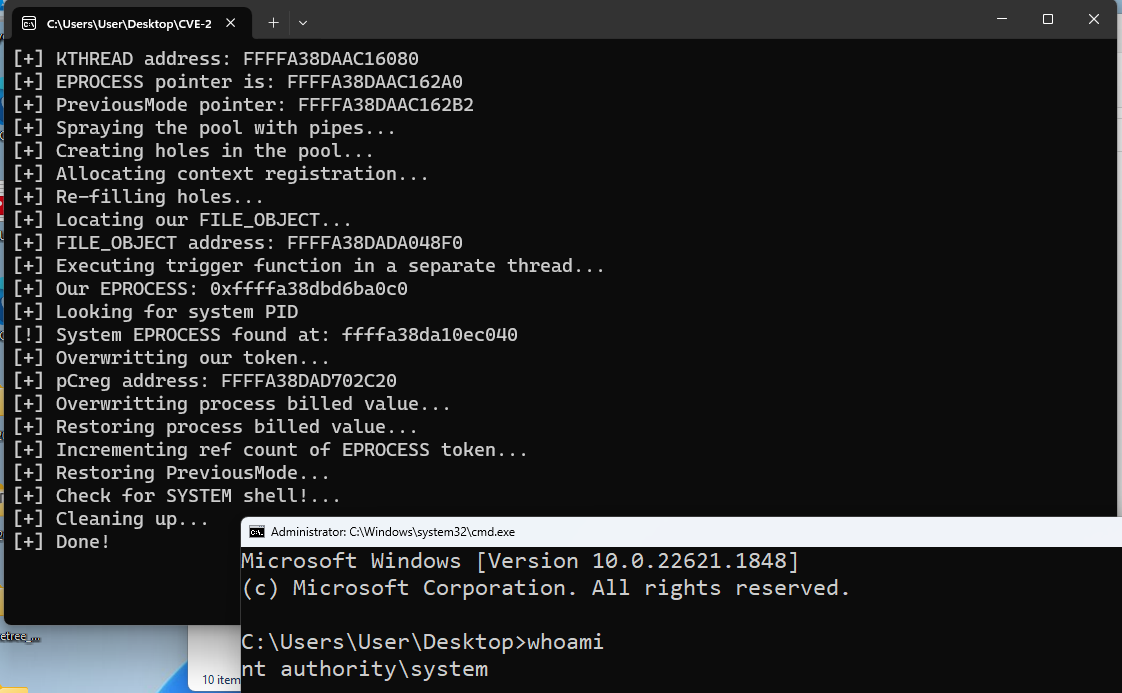 x0rb3l/cve-2023-36802-mskssrv-lpe
PoC for CVE-2023-36802 Microsoft Kernel Streaming Service Proxy
 4zur-0312/cve-2023-36802
CVE-2023-36802 ITW case
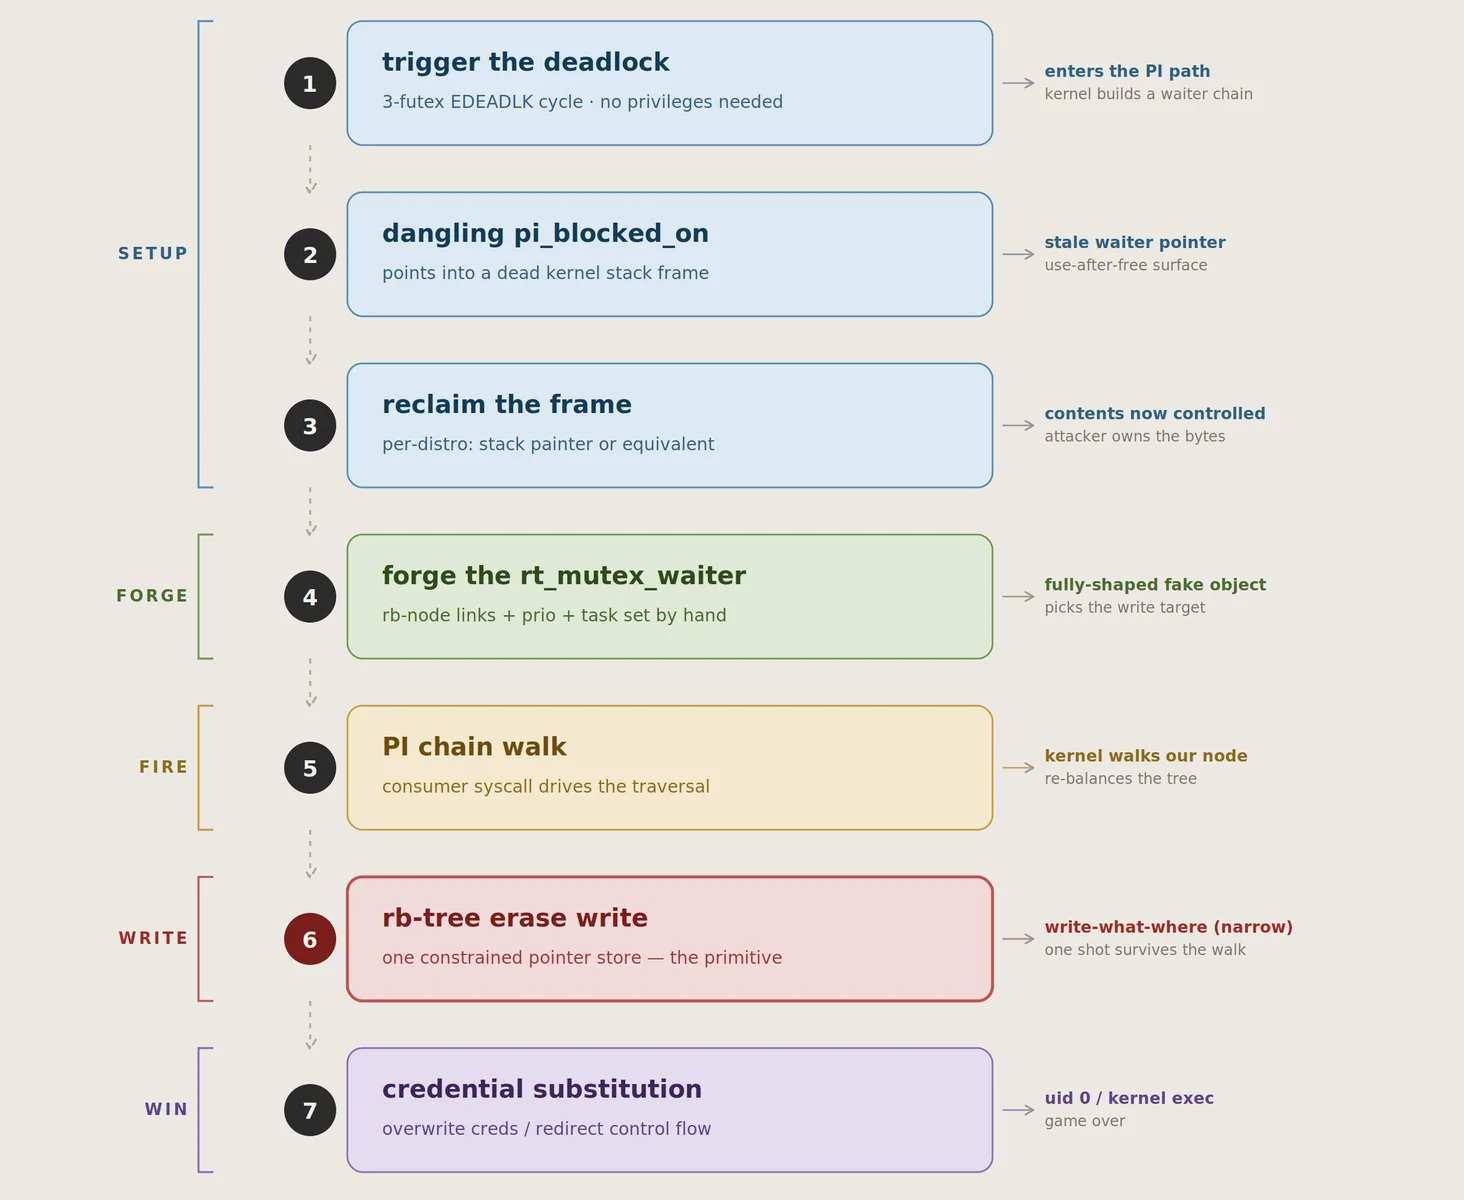 lkeld/cve-2026-43499-poc
Weaponized proof-of-concept for CVE-2026-43499 (GhostLock), a Linux kernel rtmutex bug enabling local privilege escalation. Includes per-distribution…