
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
25 results
Zapscape preview

Zapscape

GitHubv4bel/zapscape

PoC exploit for CVE-2026-64561, a KVM/x86 shadow MMU use-after-free enabling guest-to-host escape with kernel root code execution on the host.
binary-exploitationcloud-securityexploitation+3
166
1 month ago
windows_kernel_shadow_stack preview

windows_kernel_shadow_stack

GitHubsynacktiv/windows_kernel_shadow_stack

Proof of concepts demonstrating some aspects of the Windows kernel shadow stack mitigation.
binary-exploitationexploitationpapers-research+2
771 year ago
CVE-2021-36934-HiveNightmare-Lab preview

CVE-2021-36934-HiveNightmare-Lab

GitHubd4yon/cve-2021-36934-hivenightmare-lab

Educational lab demonstrating CVE-2021-36934 (HiveNightmare) - Windows LPE via shadow copy ACL misconfiguration.


binary-exploitationeducationexploitation+4
17 months ago
honda preview

honda

GitLabnu11secur1ty/0

Exploit for a Windows Defender race condition that escalates to SYSTEM via use-after-free, crashes MsMpEng.exe, spawns a hidden shell, and persists…
binary-exploitationexploitationpayload-development+3
3 months ago
CVE-2020-17382 preview

CVE-2020-17382

GitHubtypeconfused/cve-2020-17382

CVE-2020-17382 Windows 10 x64 2004 Build 19041.264 Exploit
binary-exploitationexploitationprivilege-escalation+1
13 years ago
shadow preview

shadow

GitHubjoaoviictorti/shadow

Windows Kernel Rootkit in Rust

educationprivilege-escalation
71011 months ago
AutoRDPwn preview

AutoRDPwn

GitHubjoelgmsec/autordpwn

The Shadow Attack Framework
lateral-movementpassword-crackingpayload-generation+5
1.1k4 years ago
ACLight preview

ACLight

GitHubcyberark/aclight

A script for advanced discovery of Privileged Accounts - includes Shadow Admins
identity-access-managementprivilege-escalation
8307 years ago
Whisker preview

Whisker

GitHubeladshamir/whisker

Whisker is a C# tool for taking over Active Directory user and computer accounts by manipulating their msDS-KeyCredentialLink attribute, effectively…
authenticationexploitationpenetration-testing+4
9551 year ago
pywhisker preview

pywhisker

GitHubshutdownrepo/pywhisker

Python version of the C# tool for "Shadow Credentials" attacks
authenticationexploitationpenetration-testing+1
9413 months ago
ldap_shell preview

ldap_shell

GitHubpshlyundin/ldap_shell

Interactive shell for Active Directory enumeration and ACL abuse via LDAP/LDAPS. Supports DCSync, RBCD, Shadow Credentials, password changes, and…

authenticationinformation-gatheringpenetration-testing+1
41319 days ago
SAMDump preview

SAMDump

GitHubricardojoserf/samdump

Extract the SAM and SYSTEM hives using the Volume Shadow Copy (VSS) API. With exfiltration and XOR obfuscation options. In C#, C++, Crystal, Python,…
data-exfiltrationencryption-decryption-toolspost-exploitation+3
3861 month ago
ShadowSpray preview

ShadowSpray

GitHubdec0ne/shadowspray

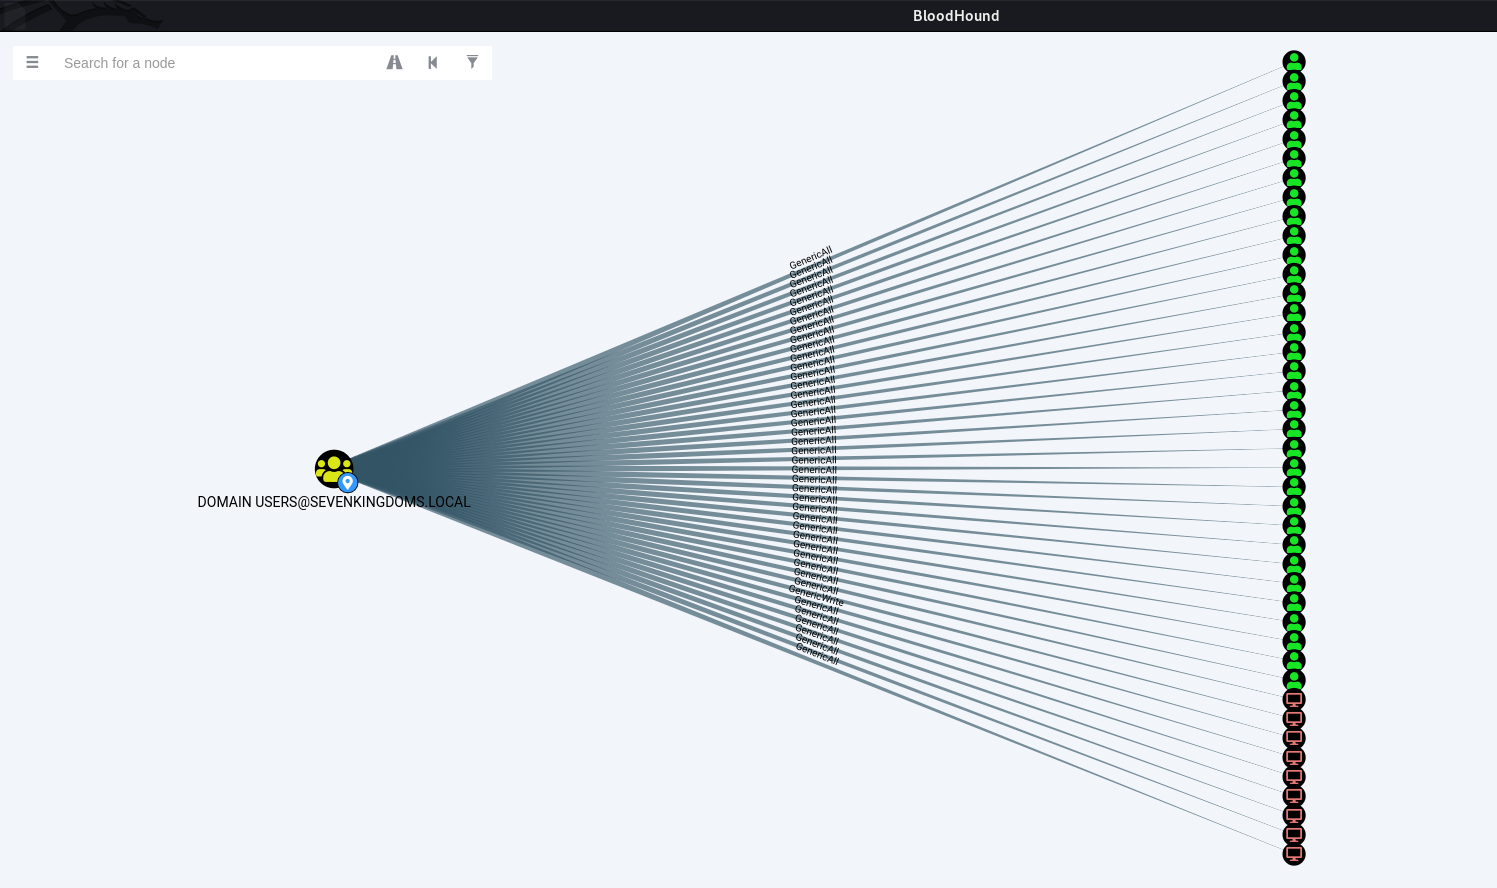
A tool to spray Shadow Credentials across an entire domain in hopes of abusing long forgotten GenericWrite/GenericAll DACLs over other objects in the…
authenticationexploitationpenetration-testing+3
4973 years ago
ad-autopwn preview

ad-autopwn

GitHubjonaslejon/ad-autopwn

Automated Active Directory attack chain from zero-auth to Domain Admin. Chains 25+ techniques including Kerberoast, AD CS ESC1-16, Shadow…
command-and-controlexploitationlateral-movement+7
2089 days ago
zBang preview

zBang

GitHubcyberark/zbang

Active Directory risk assessment tool that scans for privileged account threats, shadow admins, Skeleton Key malware, SID history abuse, risky SPNs,…

penetration-testingprivilege-escalationvulnerability-analysis
3434 years ago
poc_CVE-2021-36934 preview

poc_CVE-2021-36934

GitHubgrishinpv/poc_cve-2021-36934

POC experiments with Volume Shadow copy Service (VSS)
data-recoveryexploitationforensics+2
25 years ago
ESCepcion preview

ESCepcion

GitHubhackwarts12/escepcion

Passive AD CS auditor detecting ESC1–ESC16 and Shadow Credentials via read-only LDAP/ACL/registry checks, with prioritized remediation and SIEM-ready…
configuration-auditingdefensive-toolsmisconfiguration+4
23 months ago
CVE-2021-36934 preview

CVE-2021-36934

GitHubirissentinel/cve-2021-36934

PowerShell script to detect and remediate the CVE-2021-36934 HiveNightmare privilege escalation vulnerability on Windows 10 by checking SAM hive…

configuration-auditingincident-responseprivilege-escalation+2
15 years ago
Previous12Next