
Dirty-Pipe-CVE-2022-0847
 pmihsan/dirty-pipe-cve-2022-0847
Dirty Pipe Kernel Vulnerability Exploit
binary-exploitationexploitationprivilege-escalation+1
pmihsan/dirty-pipe-cve-2022-0847Dirty Pipe Kernel Vulnerability Exploit
 mutur4/cve-2019-2215
This is a critical UAF vulnerability exploit that affected the android binder IPC system used in the wild and discovered by P0
 caspy123/cve-2026-43499
Linux kernel rtmutex vulnerability exploit with CVSS 7.8, providing proof-of-concept code for privilege escalation via improper waiter task handling…
 dulanjaya23/dirty-cow-cve-2016-5195-
Exploit for CVE-2016-5195 (Dirty Cow) local privilege escalation vulnerability in Linux kernel, enabling race condition-based root access.
 emmmmllll/copy-fail-zig
Zig implementation of the Copy Fail Linux LPE (CVE-2026-31431) providing a standalone binary to exploit the vulnerability for security research and…
 bridgeralderson/cve-2025-9074-poc
A vulnerability has been identified in Docker Desktop. A remote attacker could exploit this vulnerability to trigger security restriction bypass on…
 boro03/cve-2021-4034
Academic study project analyzing CVE-2021-4034 (PwnKit), a local privilege escalation in polkit's pkexec, including vulnerability analysis, exploit…
 tuancui22/zerologonwithimpacket-cve2020-1472
A practical proof-of-concept for CVE-2020-1472 (Zerologon) using the Impacket library to exploit Netlogon vulnerability and perform unauthorized…
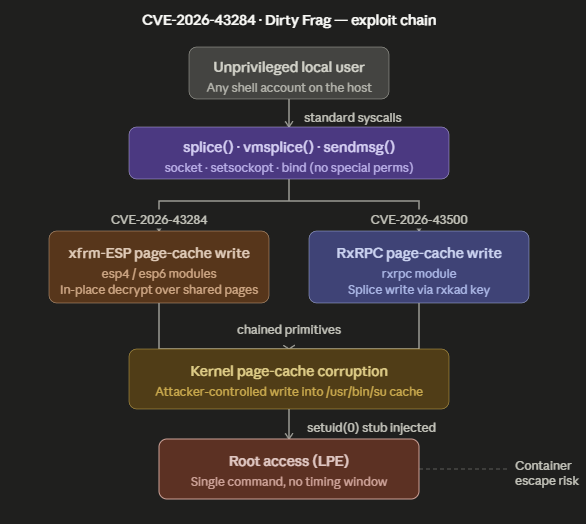 lucaspdiniz/cve-2026-43284
Dirty Frag - kernel Linux critical Vulnerability
 charlesgargasson/cve-2024-32002
Exploit for CVE-2024-32002, a Git RCE vulnerability that uses recursive submodule cloning and symlinks to execute arbitrary commands on Windows and…
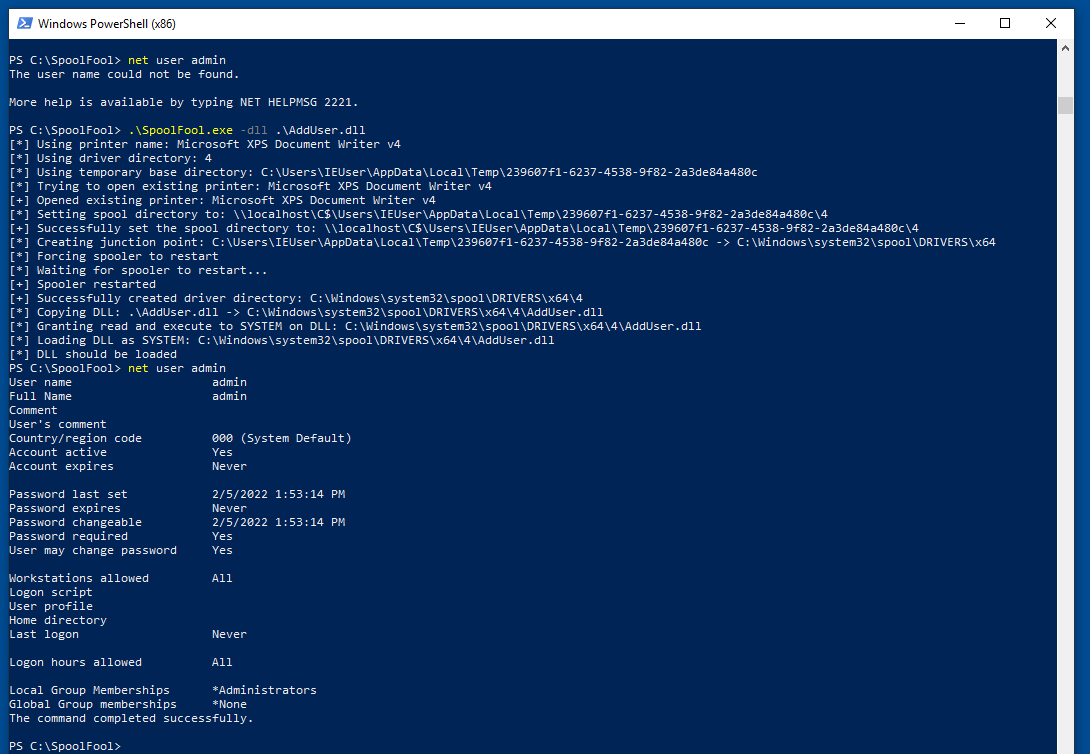 ly4k/spoolfool
Exploit for CVE-2022-21999 - Windows Print Spooler Elevation of Privilege Vulnerability (LPE)
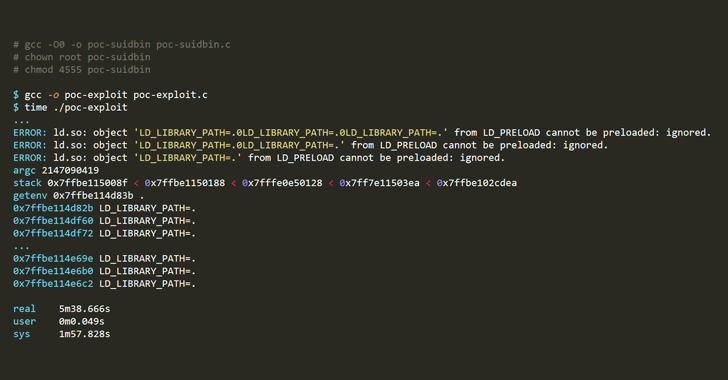 luan0ap/cve-2018-14634
proof-of-concept (PoC) for linux dists based on Debian, CentOS and RedHat - exploit 1
 0dayninja/cve-2021-3560
Polkit D-Bus Authentication Bypass Exploit
 n1et/cve-2019-18634
An Python Exploit for Sudo vulnerability CVE-2019-18634
 ashutoshrohilla/cve-2021-4034
Exploit for CVE-2021-4034, a local privilege escalation vulnerability in polkit's pkexec, allowing unprivileged users to gain root access.
 athos-zago/cve-2024-30973
POC VIDEO - https://youtu.be/hNzmkJj-ImM?si=NF0yoSL578rNy7wN
 nu11secur1ty/windows11exploits
Collection of Windows 11 exploit proof-of-concepts and vulnerability demonstrations for security research and penetration testing.
 ireshchaminda1/android-privilege-escalation-remote-access-vulnerability-cve-2015-1805
AndroRAT is a capability that can be used to inject a root exploit as a silent installation to perform a malicious task on the device. This AndroRAT…