
CVE-2019-12889
 nulsect0r/cve-2019-12889
Proof-of-concept exploit for CVE-2019-12889, demonstrating unauthenticated privilege escalation from Windows logon screen to NT AUTHORITY\System via…
exploitationpenetration-testingprivilege-escalation+2
3
nulsect0r/cve-2019-12889Proof-of-concept exploit for CVE-2019-12889, demonstrating unauthenticated privilege escalation from Windows logon screen to NT AUTHORITY\System via…
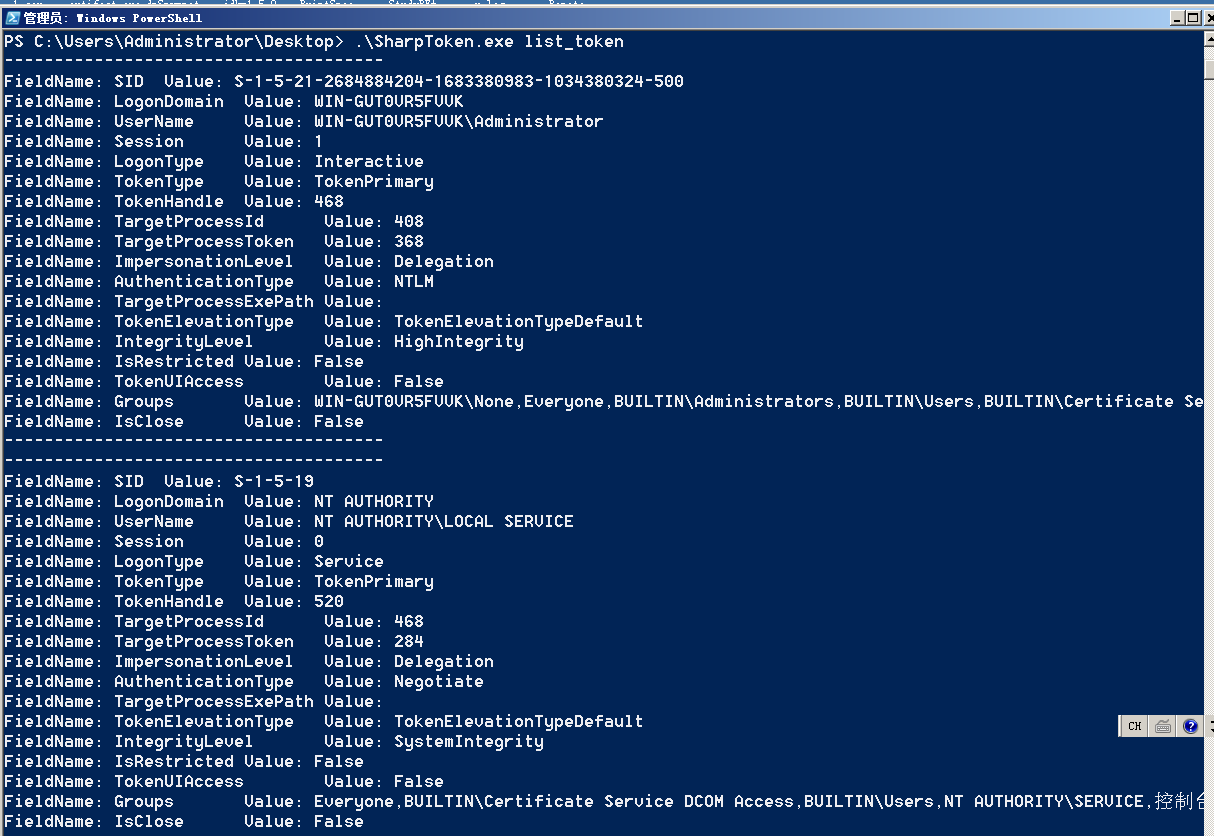 beichendream/sharptoken
Windows token theft and privilege escalation tool that steals leaked tokens from processes, enables SYSTEM-level access, user impersonation, and…
 mr-in4inci3le/sliver-gui
A desktop operator console for Sliver C2, built with Wails. Provides a native, lightweight GUI interface for Sliver by directly interfacing with its…
 impalabs/cve-2023-27326
VM Escape for Parallels Desktop <18.1.1
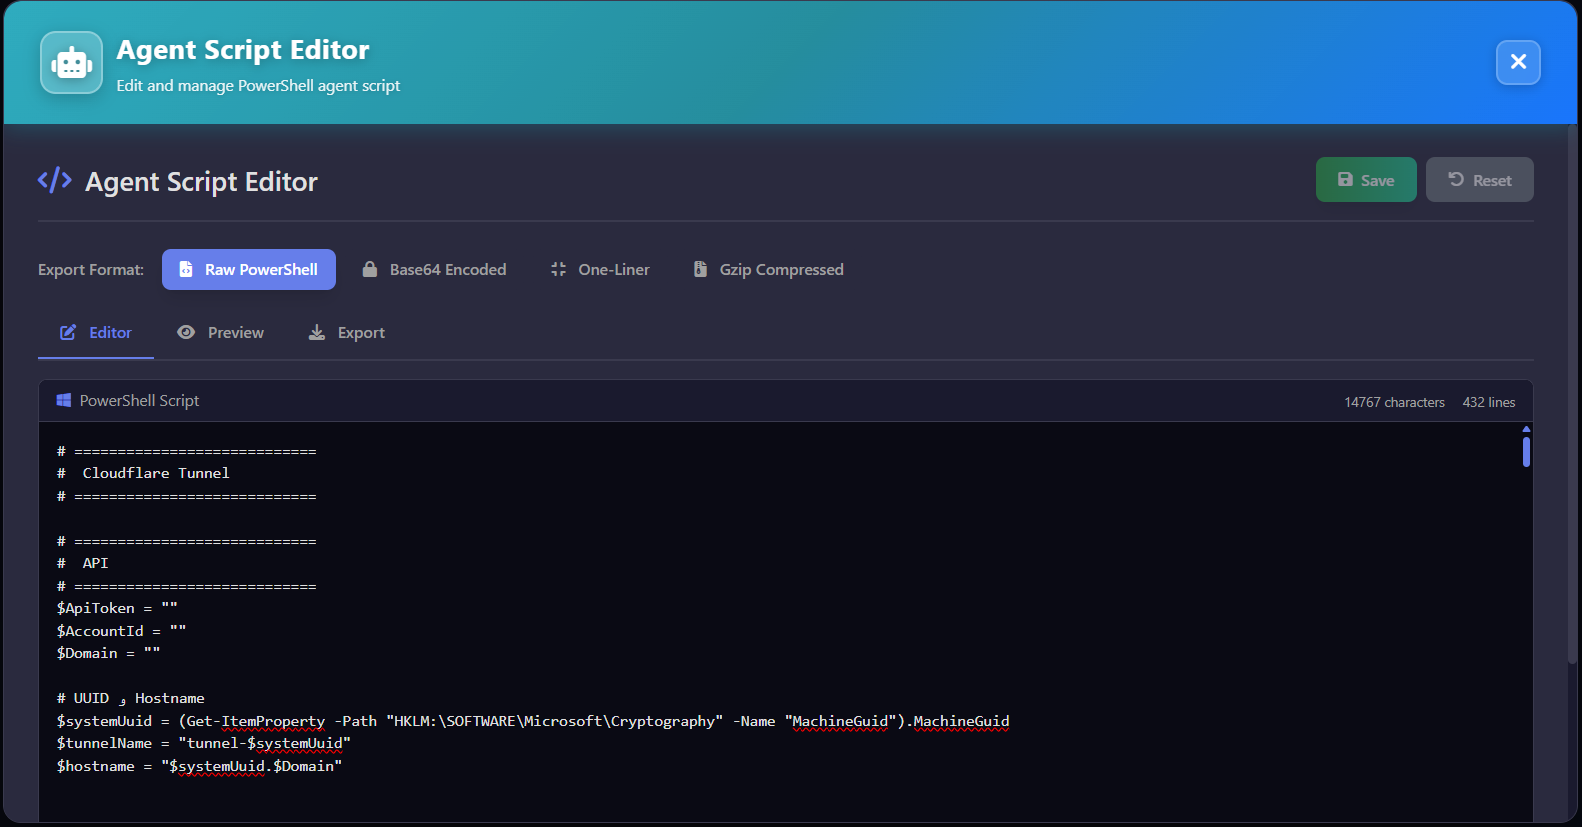 jxroot/zeropulse
🔒 Modern C2 Platform with Cloudflare Tunnel Integration | WinRM & SSH Remote Management | Real-time Terminal & Remote Desktop | Built with FastAPI &…
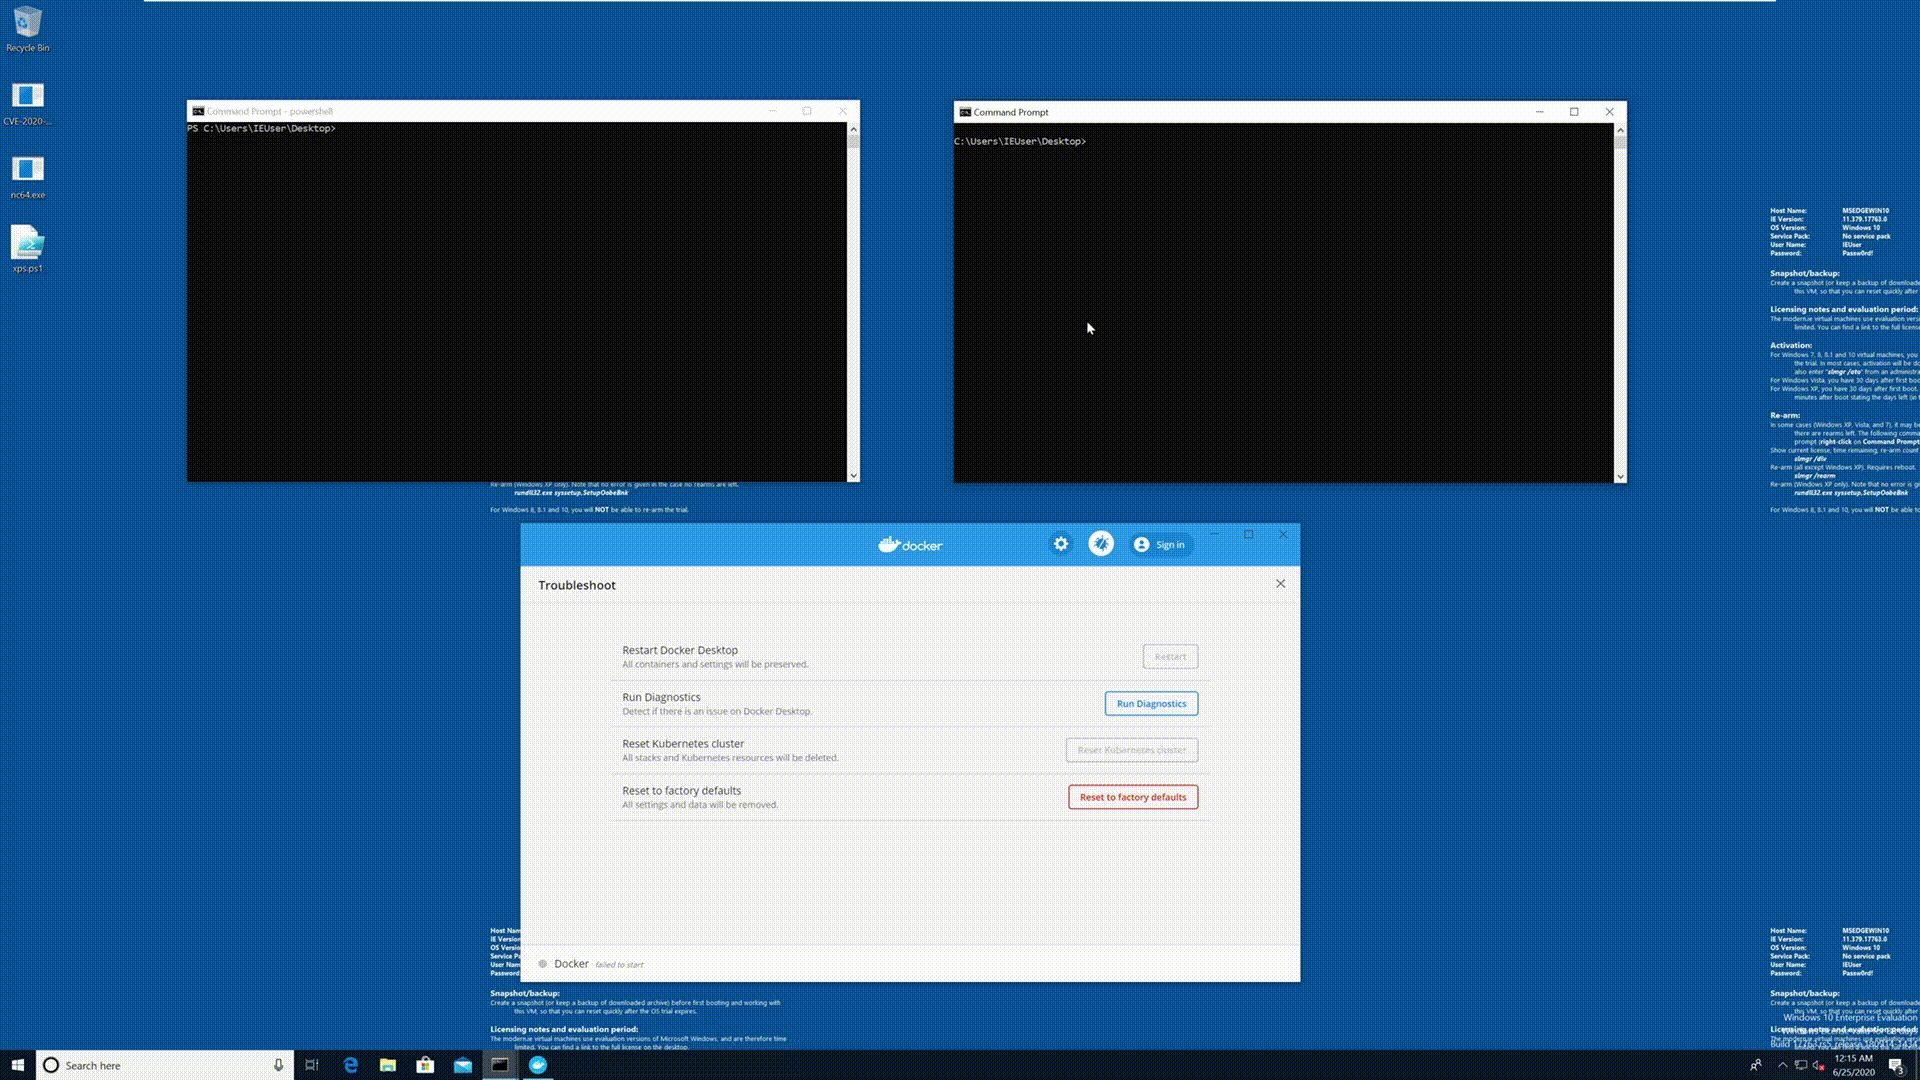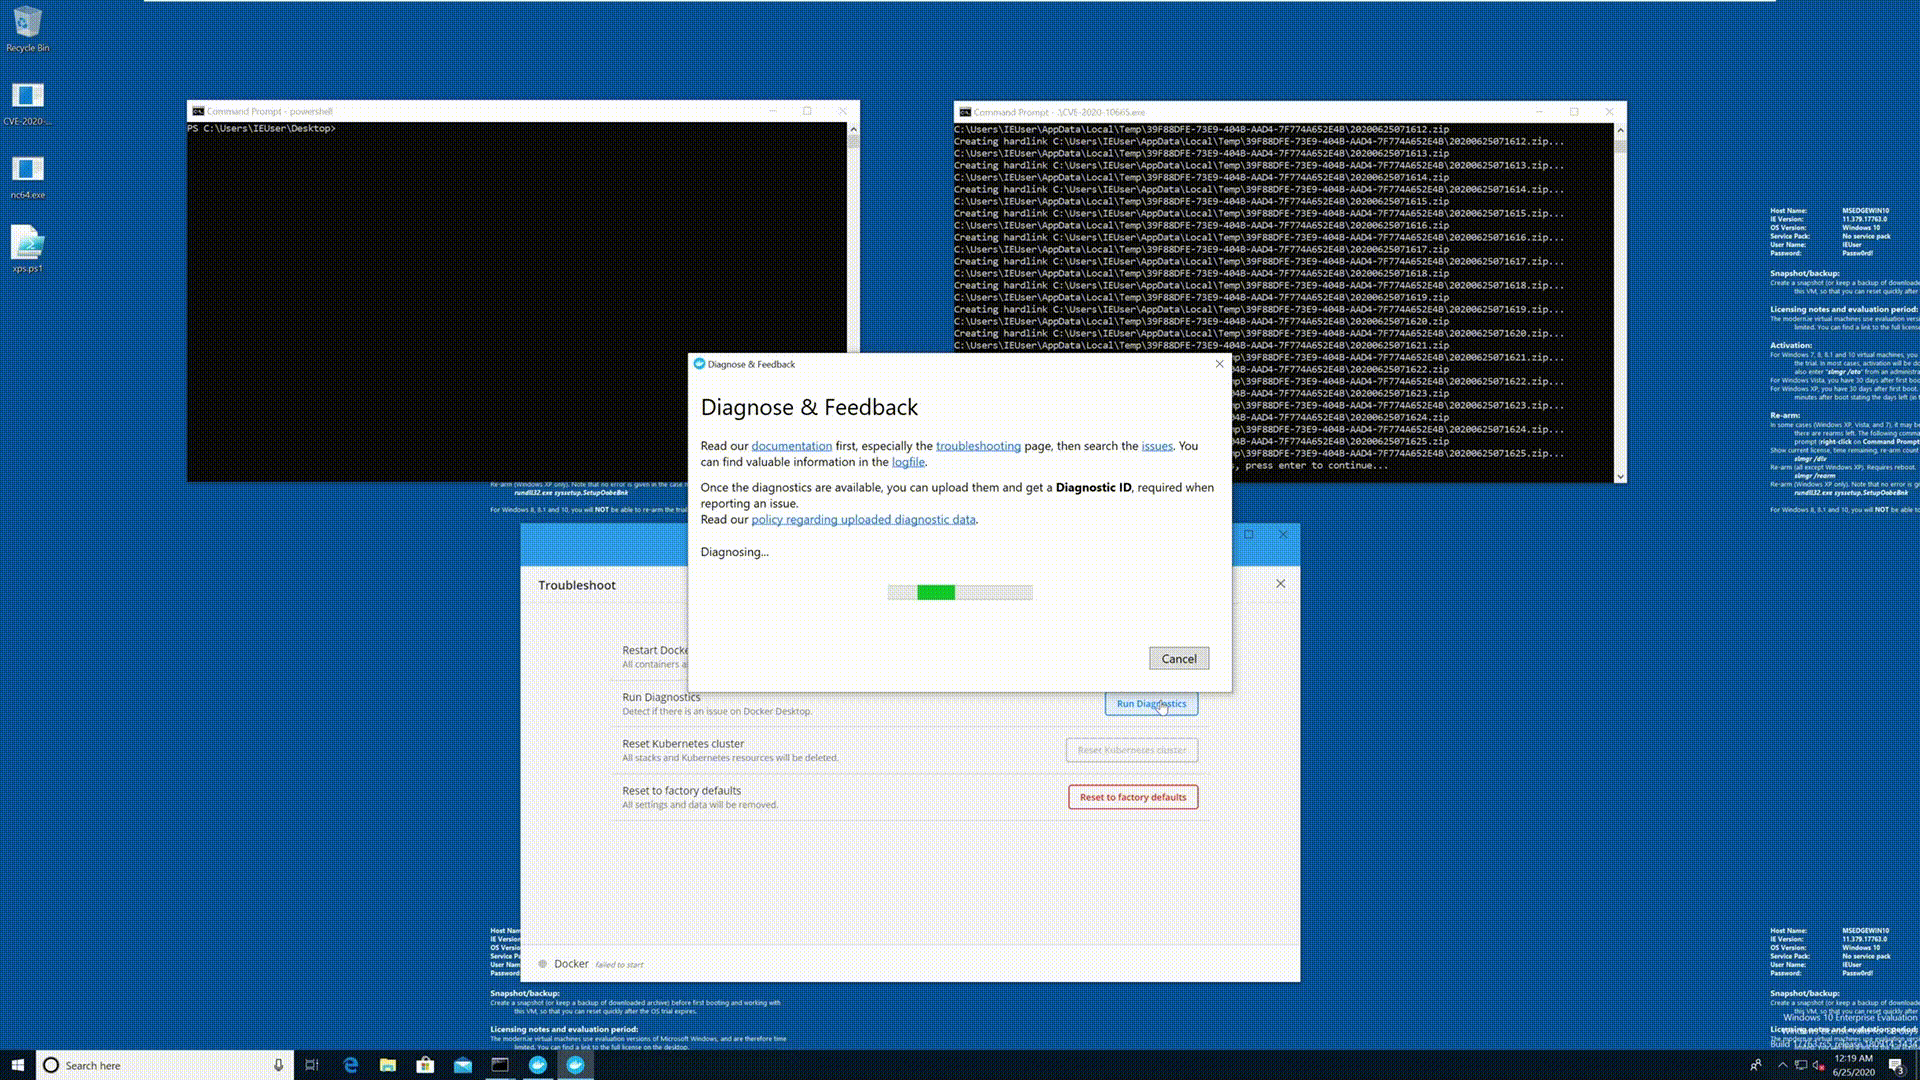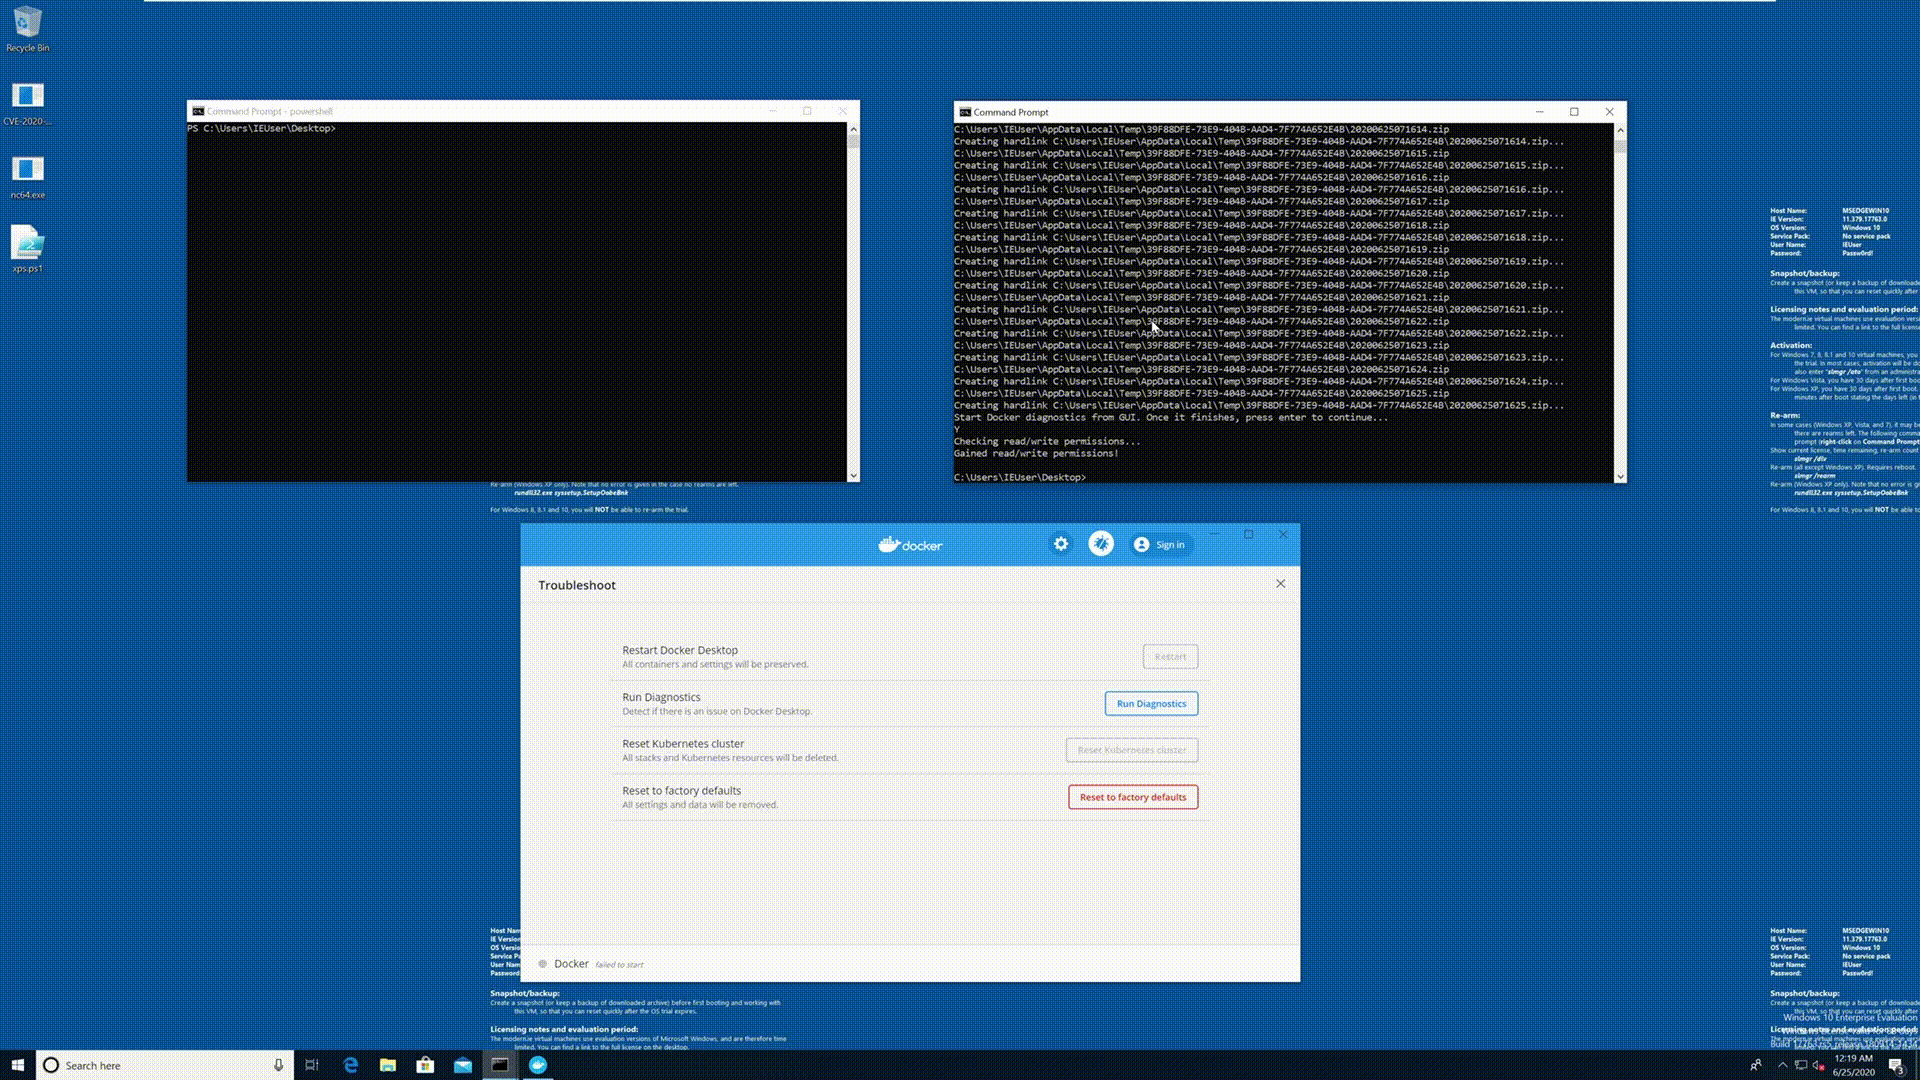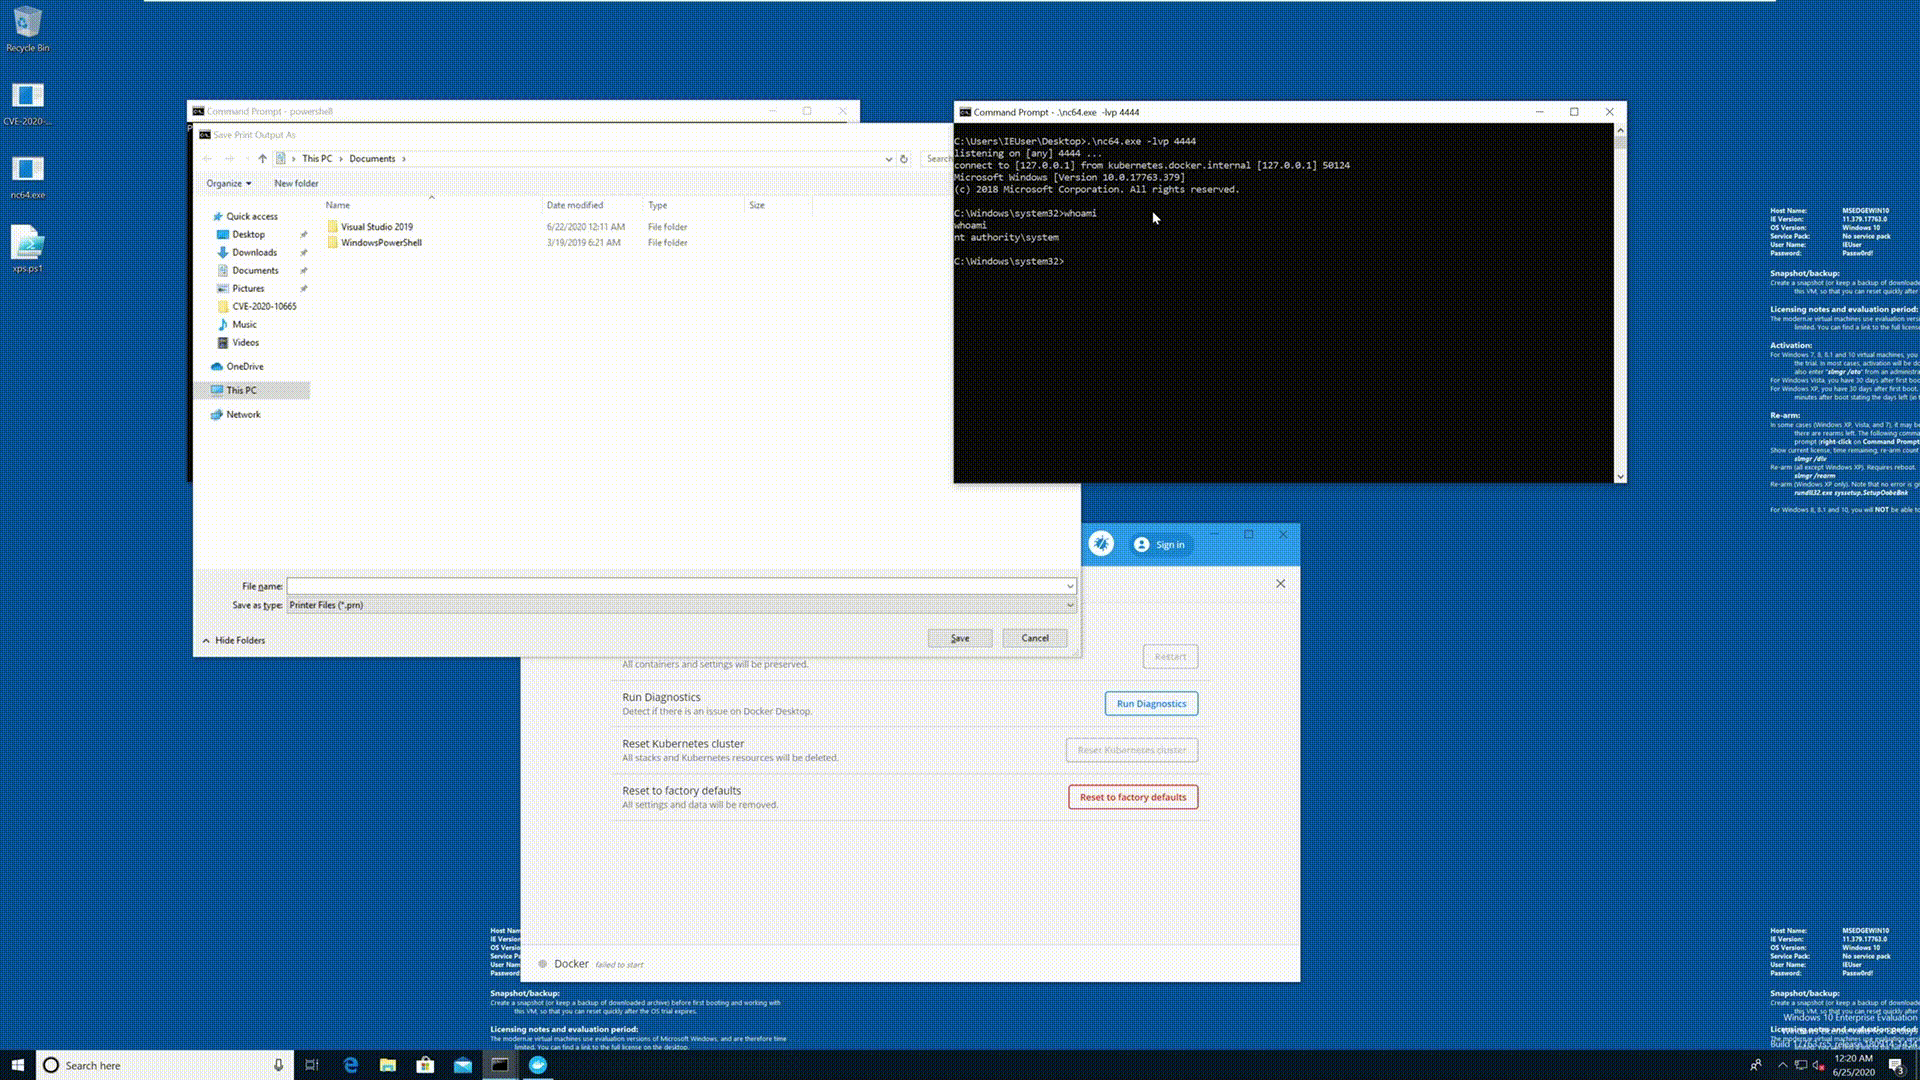 spaceraccoon/cve-2020-10665
POC for CVE-2020-10665 Docker Desktop Local Privilege Escalation
 bridgeralderson/cve-2025-9074-poc
A vulnerability has been identified in Docker Desktop. A remote attacker could exploit this vulnerability to trigger security restriction bypass on…
 u53rw4r3/remotekeystrokes
A script to automate keystrokes through a graphical desktop program.
 xct/cve-2024-27460
Plantronics Desktop Hub LPE
 malwareman007/cve-2023-27326
VM Escape for Parallels Desktop <18.1.1
 kn32/parallels-file-move-privesc
Parallels Desktop privilege escalation - CVE-2023-50226 / ZDI-CAN-21227
 sincan2/rce-cve-2025-32710
Windows Remote Desktop Services Vulnerability Allows Remote Code Execution
 davidcarliez/cve-2019-9702_symantec_encryption_desktop_lpe_poc
Local Privilege Escalation PoC to pop a SYSTEM shell for CVE-2019-9702 in Symantec Encryption Desktop.
 crackercat/cve-2020-11492
Proof-of-concept exploit for Docker Desktop for Windows privilege escalation (CVE-2020-11492). Uses named pipe impersonation to steal SYSTEM token…
 fengjixuchui/cve-2020-11493
Proof-of-concept for Docker Desktop for Windows privilege escalation (CVE-2020-11492). Exploits named pipe impersonation to achieve SYSTEM-level…
 devianntsec/cve-2024-30051
Master's Thesis research on CVE-2024-30051 (Windows DWM Heap Overflow). Features a high-reliability exploit with automated heap spray optimization,…
 simoesctt/-sctt-2026-33-0002-dwm-visual-field-singularity
Weaponizes a Visual-Field Singularity in Windows Desktop Window Manager to achieve local privilege escalation to SYSTEM, bypassing Graphics Isolation…
 followboy1999/cve-2022-25365
Proof-of-concept exploit for CVE-2022-25365, a privilege escalation vulnerability in Docker Desktop for Windows via named pipe impersonation.