
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
57 results
CVE-2026-64468 preview

CVE-2026-64468

GitHubaramosf/cve-2026-64468

Unprivileged proof-of-concept and x86_64 local privilege escalation for a Linux kernel Binder use-after-free (CVE-2026-64468), with KASAN lab and…
binary-exploitationeducationexploitation+3
23
27 days ago
XeytanWin32-RAT preview

XeytanWin32-RAT

GitHubmelardev/xeytanwin32-rat

WORK IN PROGRESS. RAT written in C++ using Win32 API
command-and-controldata-exfiltrationexploitation+8
207 years ago
CVE-2026-46242 preview

CVE-2026-46242

GitHub0xblackash/cve-2026-46242

CVE-2026-46242

binary-exploitationeducationexploitation+3
202 months ago
root-sonim-xp3800 preview

root-sonim-xp3800

GitHubflipphoneguy/root-sonim-xp3800

app that ports CVE-2019-2215 to arm32 and mounts a su binary to /sbin with denylist + root app installer. firehose/Magisk guide included
android-securitybinary-exploitationeducation+5
112 months ago
CVE-2026-52943 preview

CVE-2026-52943

GitHubvn-lazyming/cve-2026-52943

This is a Linux Kernel Local Privilege Escalation PoC code for CVE-2026-52943 a use-after-free in skbuff.c, my first 0day found by me in linux kernel
binary-exploitationeducationexploitation+3
82 months ago
CVE-2026-68398 preview

CVE-2026-68398

GitHubaramosf/cve-2026-68398

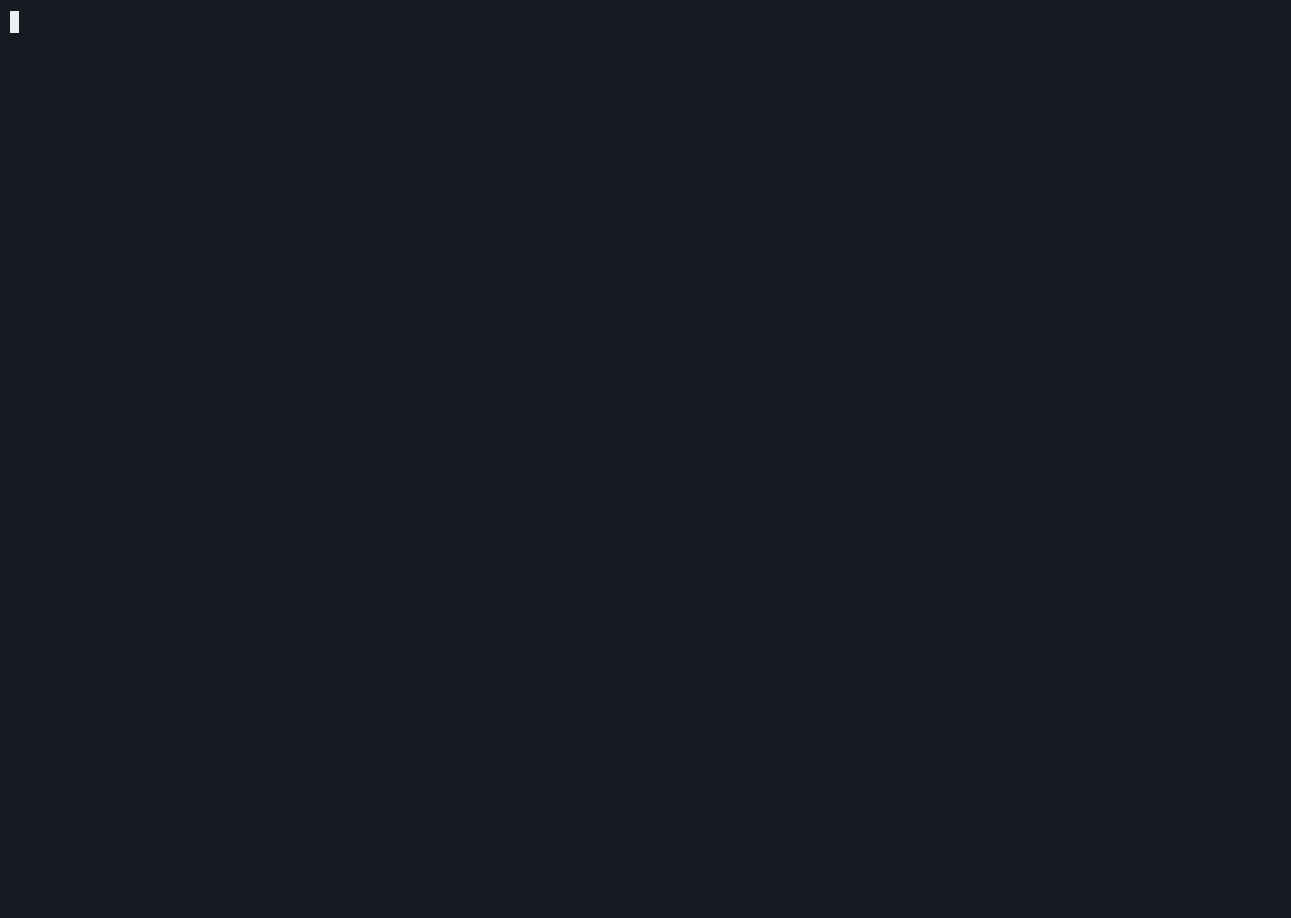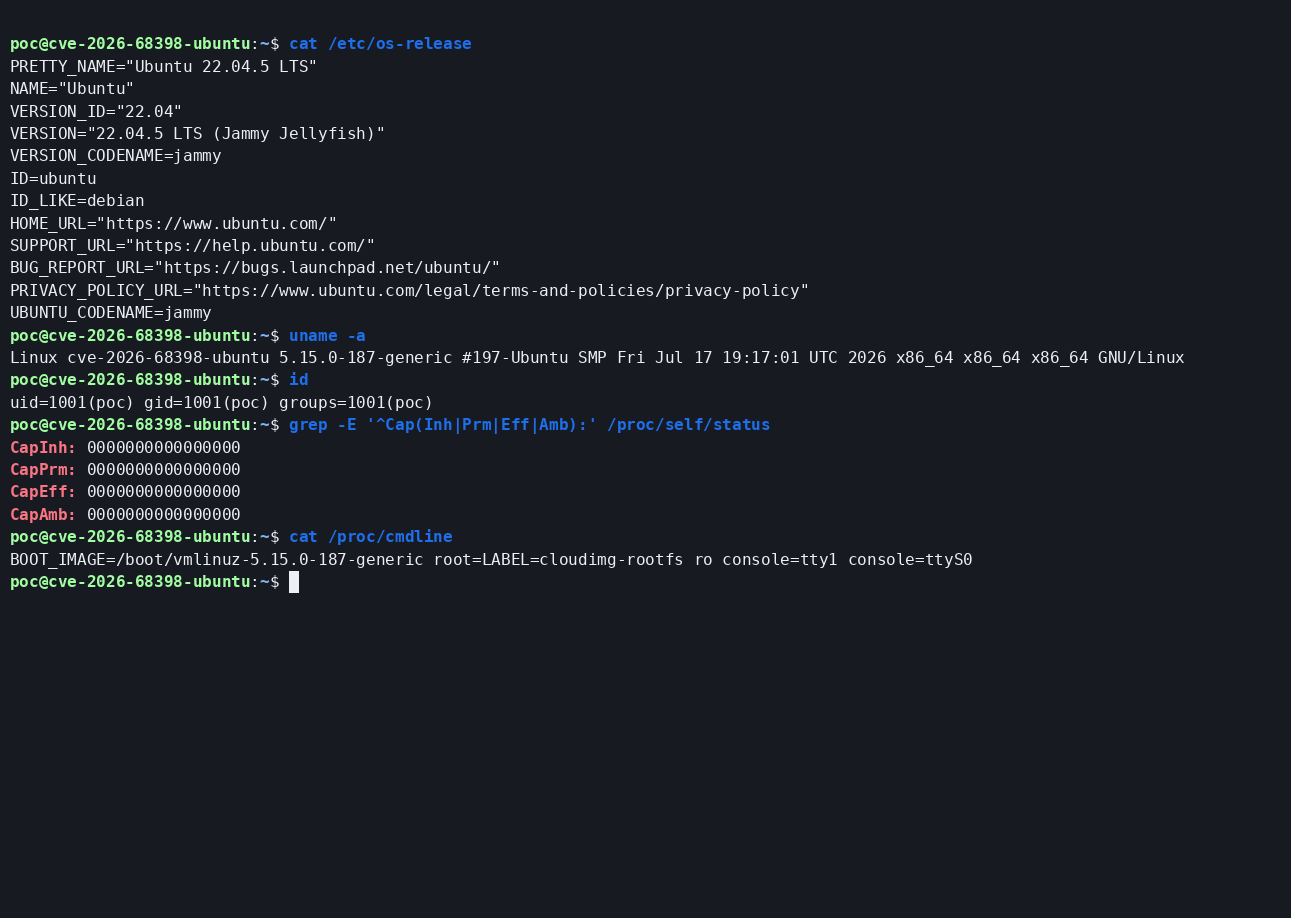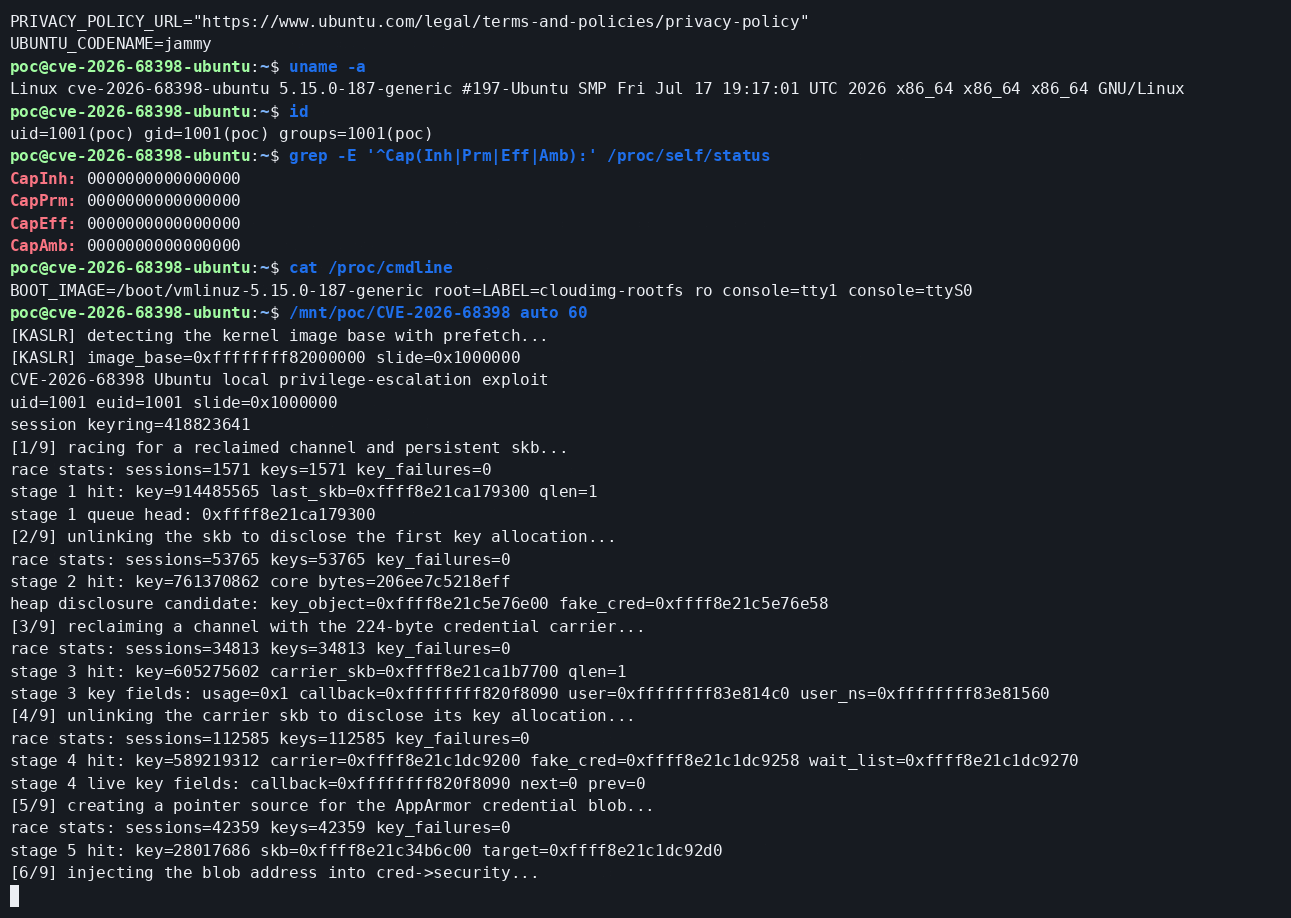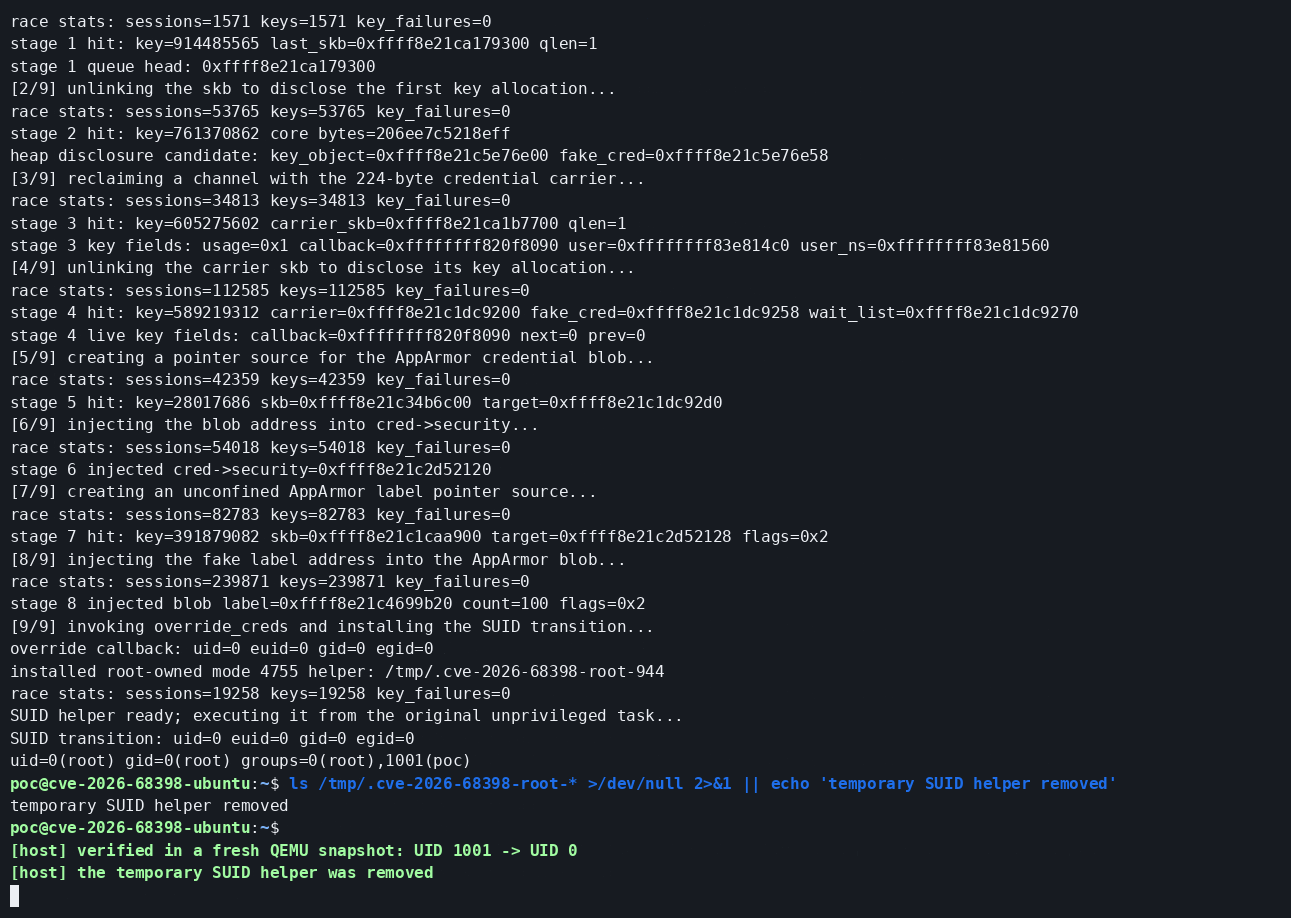
CVE-2026-68398 Ubuntu PPPoL2TP use-after-free local privilege escalation
binary-exploitationexploitationprivilege-escalation
101 month ago
ghostlock-emerald preview

ghostlock-emerald

GitHubdatfooldive/ghostlock-emerald

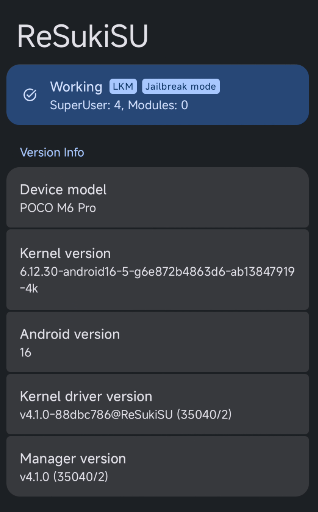
GhostLock (CVE-2026-43499) kernel exploit for Poco M6 Pro (emerald) with locked bootloader
android-securitybinary-exploitationexploitation+3
131 month ago
CVE-2026-46215-POC preview

CVE-2026-46215-POC

GitHub0xcyberstan/cve-2026-46215-poc

Exploit for CVE-2026-46215, a Linux kernel DRM GEM use-after-free local privilege escalation. Uses racing, slab spraying, and Dirty Pipe-style file…
binary-exploitationctfeducation+4
112 months ago
CVE-2026-23111 preview

CVE-2026-23111

GitHubbaba01hacker666/cve-2026-23111

Linux Kernel nf_tables Use-After-Free (CVE-2026-23111) — LPE PoC
binary-exploitationeducationexploitation+5
72 months ago
chronomaly-webos preview

chronomaly-webos

GitHubanalyticeth/chronomaly-webos

CVE-2025-38352 kernel exploit for LG webOS Smart TVs (ARM64). Achieves persistent root on real consumer hardware with novel exploitation techniques.…
binary-exploitationeducationembedded-systems-security+4
153 months ago
CVE-2025-8045 preview

CVE-2025-8045

GitHubkuzeyardabulut/cve-2025-8045

Dirty Pagetable Exploit for CVE-2025-8045

android-securitybinary-exploitationexploitation+1
61 month ago
CVE-2026-43499 preview

CVE-2026-43499

GitHub0xblackash/cve-2026-43499

CVE-2026-43499

binary-exploitationcontainer-escapeeducation+5
82 months ago
CVE-2020-28018 preview

CVE-2020-28018

GitHubdorkerdevil/cve-2020-28018

Exploit for Exim Use-After-Free (CVE-2020-28018) achieving remote code execution via memory corruption primitives, including arbitrary read/write and…
binary-exploitationexploitationmemory-forensics+4
75 years ago
CVE-2022-32250-LPE preview

CVE-2022-32250-LPE

GitHubysanatomic/cve-2022-32250-lpe

LPE PoC of a user-after-free vulnerability in the Linux netfilter subsystem.

binary-exploitationeducationexploitation+2
93 years ago
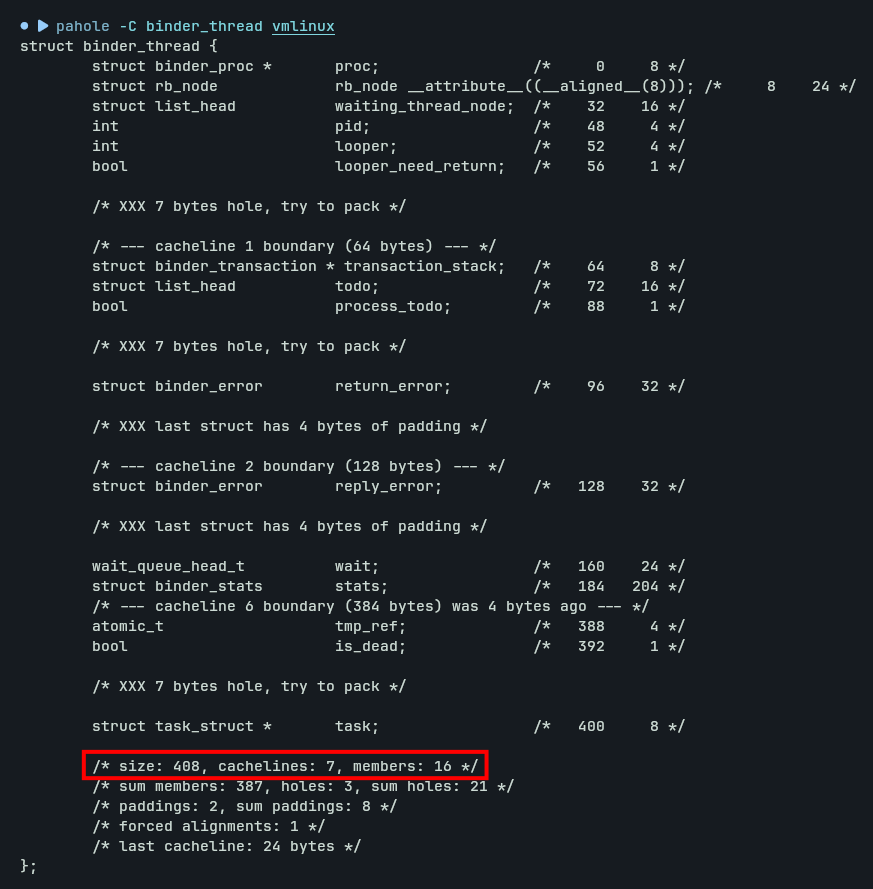
ghostlock-cve-2026-43499 preview

ghostlock-cve-2026-43499

GitHubgitchw/ghostlock-cve-2026-43499

CVE-2026-43499 (GhostLock) — Linux kernel futex PI rt_mutex UAF ARM32 privilege escalation research targeting Huawei Watch 4 Pro (kernel 5.4.210)
binary-exploitationembedded-systems-securityexploitation+5
224 days ago
CVE_2019_2215 preview

CVE_2019_2215

GitHub0xbinder/cve_2019_2215

Proof-of-concept LPE exploit for Android Binder UAF that uses iovec spraying and addr_limit overwrite to achieve arbitrary kernel read/write.

android-securitybinary-exploitationeducation+5
322 days ago
CVE-2023-52927 preview

CVE-2023-52927

GitHubseadragnol/cve-2023-52927

Local privilege escalation exploit for CVE-2023-52927, a Use-After-Free vulnerability in the Linux kernel netfilter subsystem, with a KASAN trigger…
binary-exploitationctfexploitation+2
91 year ago
GhostLock preview

GhostLock

GitHubwzhdgithub/ghostlock

CVE-2026-43499 futex PI stack UAF ???????? - Android GKI 6.1~6.12 ??????? pselect() + futex PI ????????????,??? root ??? SELinux??? OPPO Find…

android-securitybinary-exploitationexploitation+3
31 month ago
Previous1234Next