
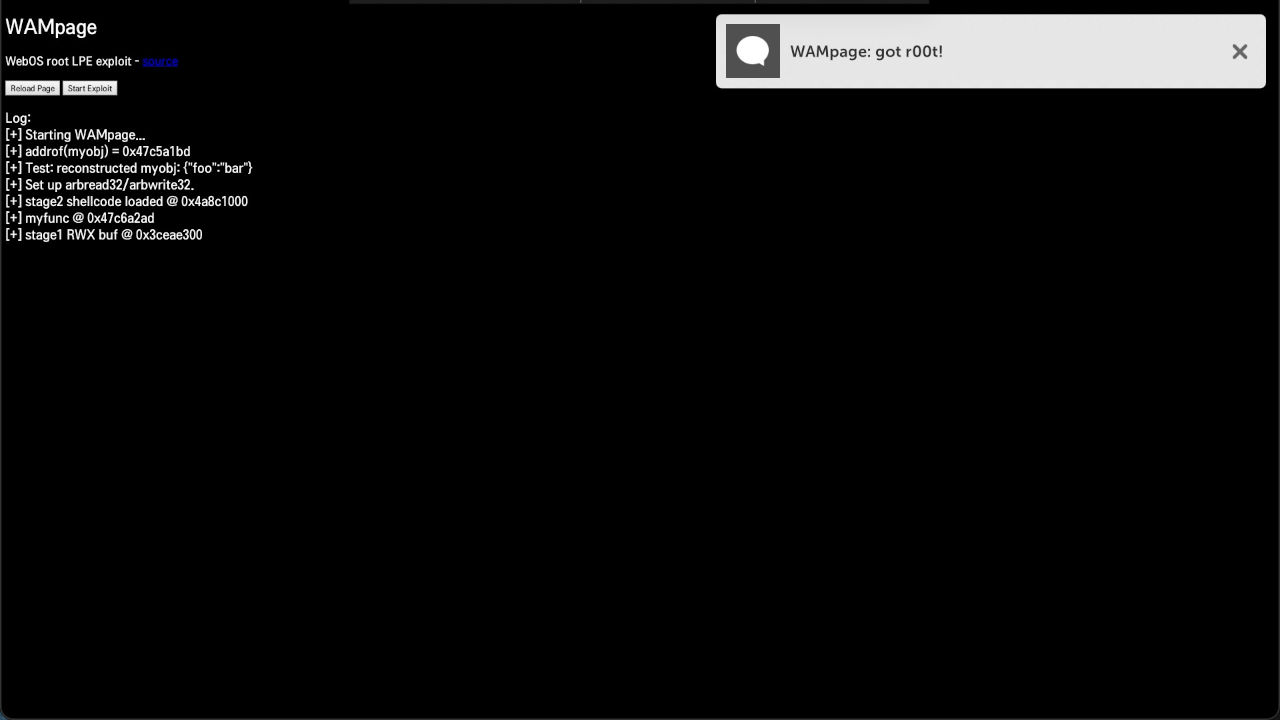
WAMpage
 davidbuchanan314/wampage
WAMpage - A WebOS root LPE exploit chain (CVE-2022-23731)
binary-exploitationembedded-systems-securityexploitation+5
494 years ago
davidbuchanan314/wampageWAMpage - A WebOS root LPE exploit chain (CVE-2022-23731)
 kpwn/ps4-5.05-kernel-exploit
A fully implemented kernel exploit for the PS4 on 5.05FW
 wack0/batondrop_armv7
An implementation of baton drop (CVE-2022-21894) for armv7 (MSM8960)
 gitchw/ghostlock-cve-2026-43499
CVE-2026-43499 (GhostLock) — Linux kernel futex PI rt_mutex UAF ARM32 privilege escalation research targeting Huawei Watch 4 Pro (kernel 5.4.210)
 hackspeak/cve-2026-67279
Python proof-of-concept scripts for the MikroTrick MikroTik RouterOS SSH takeover chain (CVE-2026-67279, CVE-2026-86060, CVE-2026-67276) for…
 saaedimam/sony-bravia-root-toolkit
CVE-2019-2215 & DirtyCOW exploit automation + post-root debloat + Magisk modules for Sony BRAVIA KDL-43W800C
 ivanglinkin/cve-2024-36821
The public reference that contains the minimum require information for the vulnerability covered by CVE-2024-36821
 voltaireyoung/cve-2024-31719----ami-aptio-5-vulnerability
Demonstrates a local access control bypass in AMI Aptio 5 NvLock module, allowing modification of NVRAM variables including administrator password,…
 jdbonfils/poc_cve-2025-48507
Proof of Concept of CVE-2025-48507. The security flaw can be leveraged by Non-Secure software (e.g., Linux) to break Trust Zone and gain access to…
 safelock-d2e/quiksand-cve-2023-24012
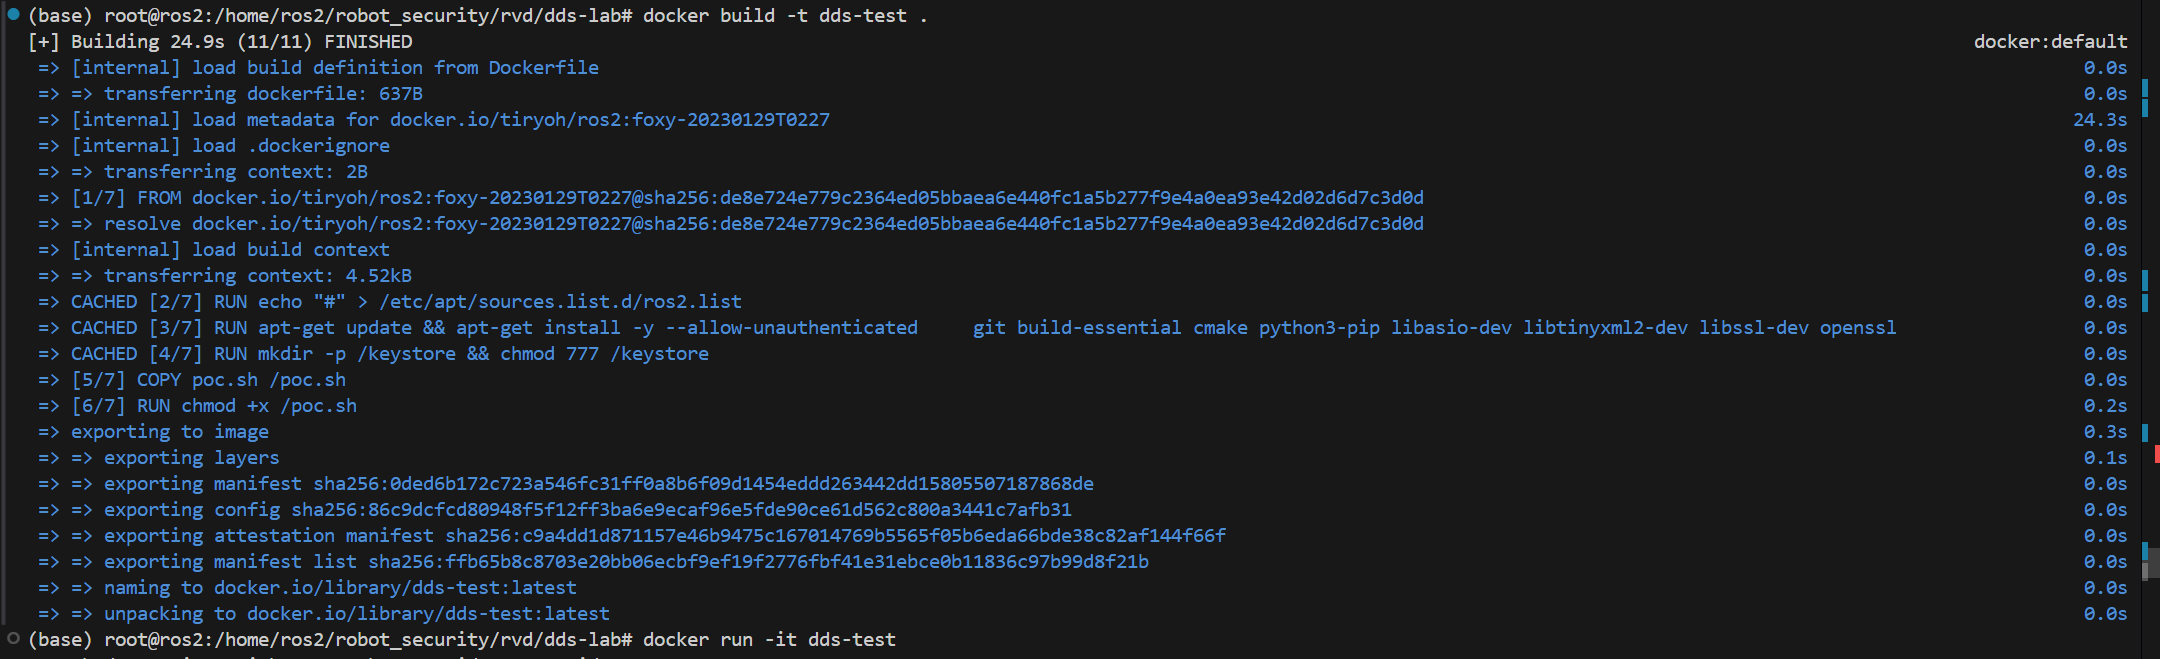
Proof-of-concept demonstrating a permission bypass in ROS 2 SROS2 security framework, allowing unauthorized topic subscription via modified…
 totekuh/cve-2026-36355
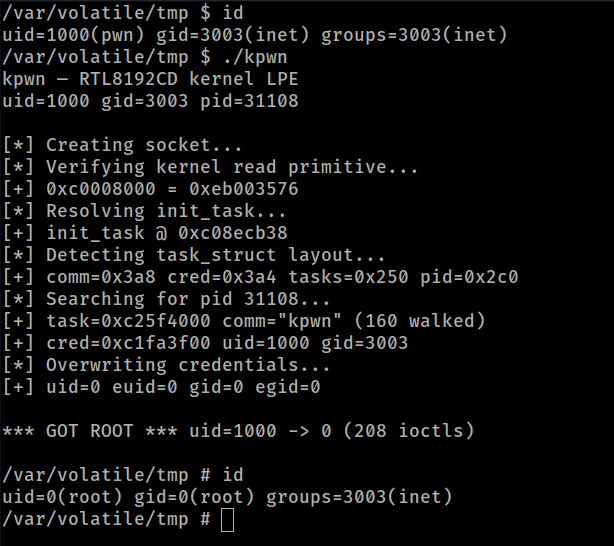
CVE-2026-36355: Realtek rtl819x Jungle SDK - Unauthenticated Kernel Memory Read/Write via Debug ioctls
 securifera/cve-2016-3962-exploit
CVE-2016-3962-Exploit
 proxystaffy/mediatrix-cve-2022-43096
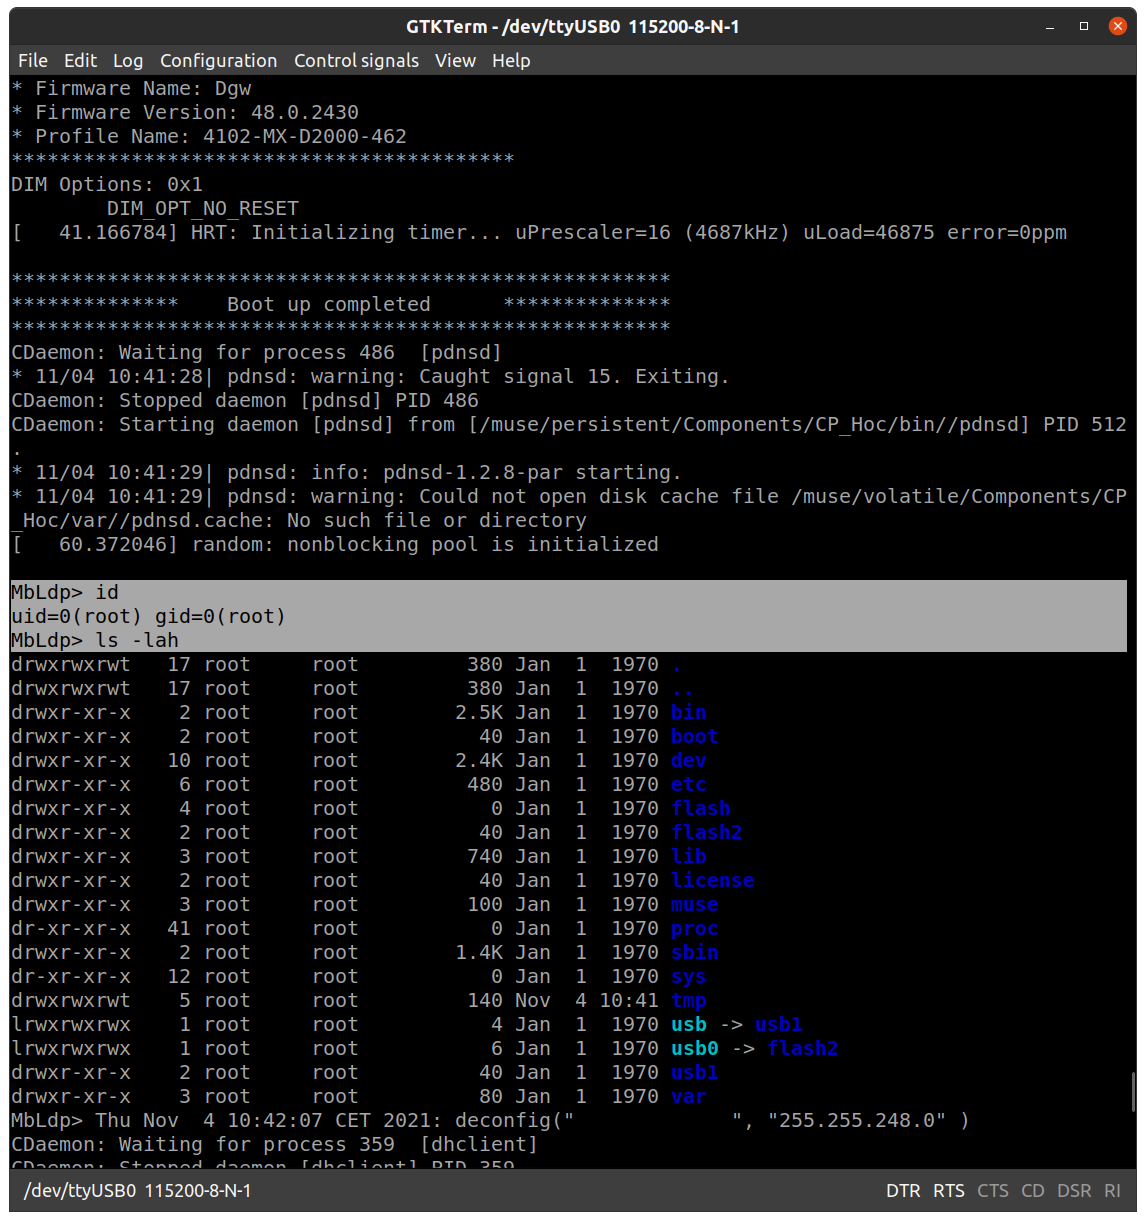
Proof-of-concept exploit for CVE-2022-43096, demonstrating local root access via UART port on Mediatrix 4102 devices before v48.5.2718.
 zgsnj123/cve-2025-45466
It is the details of CVE-2025-45466
 stigtsp/cve-2018-20162-digi-lr54-restricted-shell-escape
Proof-of-concept exploit for CVE-2018-20162: sandbox escape in Digi TransPort LR54 LTE router via SIGINT handling flaw, yielding root shell access.
 athos-zago/cve-2024-30973
POC VIDEO - https://youtu.be/hNzmkJj-ImM?si=NF0yoSL578rNy7wN
 kristof-mattei/gardyn-hack
CVE-2025-29628, CVE-2025-29629, CVE-2025-29630, CVE-2025-29631
 ethancunt/cve-2022-45600
Proof-of-concept exploit for command injection vulnerability in Aztech WMB250AC routers, enabling authenticated privilege escalation to root shell…