macOS-enterprise-privileges

This application gives Mac users in enterprise environments control over the administration of their machines by elevating their access level to…

This application gives Mac users in enterprise environments control over the administration of their machines by elevating their access level to…

Proof-of-concept exploit for Firefox BrowsingContext authorization bypass (CVE-2026-4692), demonstrating forged IPC messages to set InRDMPane and…

OSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…

PoC for CVE-2026-22015: malicious event injects environment variables into serverless functions, overwriting secrets and enabling privilege…

Determine privileges from cloud credentials via brute-force testing.

A tool uses the QoS Policy (Pacer.sys) to throttle Endpoint Detection and Response (EDR) agents from connecting to the server.

The User Registration & Membership WordPress plugin before 4.1.2 does not prevent users to set their account role when the Membership Addon is…

[First-Blood-XO] React Server Component endpoint vulnerable to CVE-2025-55182 (RCE) → enumerated SUID binaries → /usr/bin/perl had SUID set → used…

The AWS exploitation framework, designed for testing the security of Amazon Web Services environments.

Toolkit to weaponize Chromium vulnerabilities into reliable, cross-platform, full-chain exploits

Tarfile module directory traversal vulnerability ( with overflow crossed Directory ) --> Lead to Privilege escalation

CVE-2025-6018 + CVE-2025-6019 Privilege Escalation Exploit

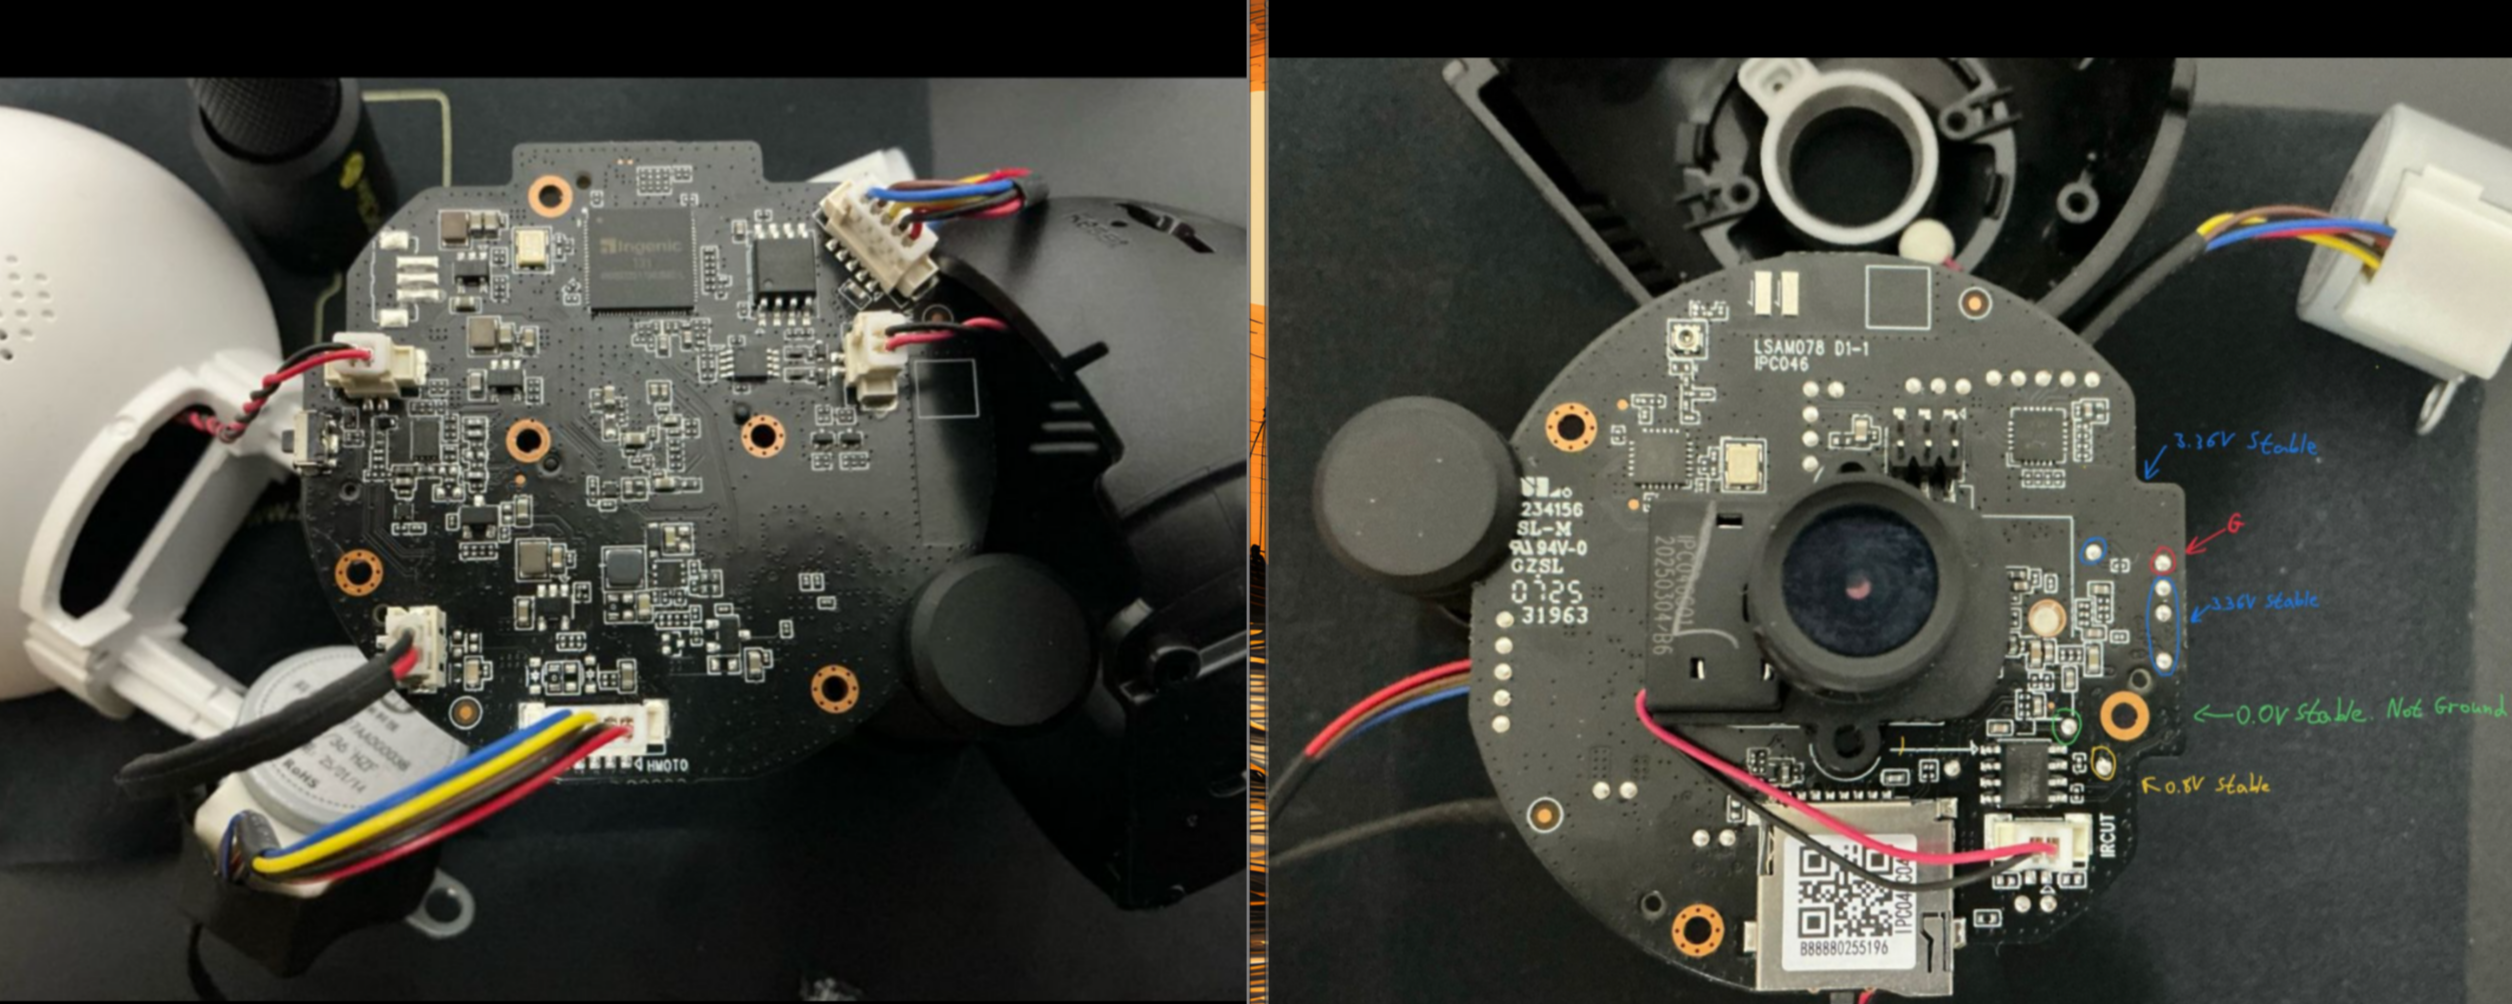
From UART to Root: Breaking Into the Xiaomi C200 via U-Boot

Bash script for Privilege Escalation via "ndsudo" (Netdata Local Exploit)

Set of tools to analyze Windows sandboxes for exposed attack surface.

Exploit scripts for CVE-2025-27581

Proof-of-concept exploit for CVE-2021-22911 targeting Rocket.Chat 3.12.1. Automates privilege escalation from low-privileged user to administrator…

Proof-of-concept exploit for CVE-2024-10793 targeting WordPress wp-security-audit-log plugin. Demonstrates account takeover, privileged user…