

Oihk-pentesting
 broskigx/oihk-pentesting
Autonomous multi-agent AI penetration-testing engine: a governed tool sandbox, an immutable evidence-and-validation gate, and a reproducible…
ai-securityeducationexploit-frameworks+7
4
broskigx/oihk-pentestingAutonomous multi-agent AI penetration-testing engine: a governed tool sandbox, an immutable evidence-and-validation gate, and a reproducible…
 liverwortenuresis371/copyfail-rs
Exploit and detect CVE-2026-31431 vulnerabilities using a static binary that monitors system integrity and bypasses PAM authentication.
 division-36/z-jail
A lightweight, multi-layer Linux sandbox combining namespaces, pivot_root, seccomp-bpf, capability dropping, and an evidence-based verdict engine…
 joehquak/mi8e5-unlocker-by-cve-2026-43499
Multi OS Support: Version for MacOS/Linux and Windows, Fully translated to English
 kaandemir993/advanced-loader-reverse-engineering
"In-depth reverse engineering analysis of an advanced multi-phase loader targeting Shellhost.exe, amsi.dll, mstscax.dll, and clbcatq.dll using module…
 portbuster1337/lpe-toolkit
Multi-architecture Linux privilege escalation toolkit with 24 pre-built and runtime-compilable exploits. Auto-detects kernel version, filters patched…
 madexploits/cve-2026-46300
CVE-2026-43284 - CVE-2026-43500 - CVE-2026-46300 Variant of dirtyfrag exploit
 amar-imamovic/cve-2023-2640-cve-2023-32629-interactive-poc
A clean, interactive multi-step Local Privilege Escalation (LPE) exploit for Ubuntu OverlayFS (GameOver(lay)) that escapes the user namespace sandbox…
 diemoeve/copyfail-rs
CopyFail (CVE-2026-31431): Linux kernel page-cache PrivEsc PoC + the only public detection tool. Novel PAM auth-bypass vector + Sigma/auditd/eBPF…
 voxcia-io/copy-fail
Tutorial Completo: Como Proteger seu contra a Vulnerabilidade CopyFail (CVE-2026-31431)
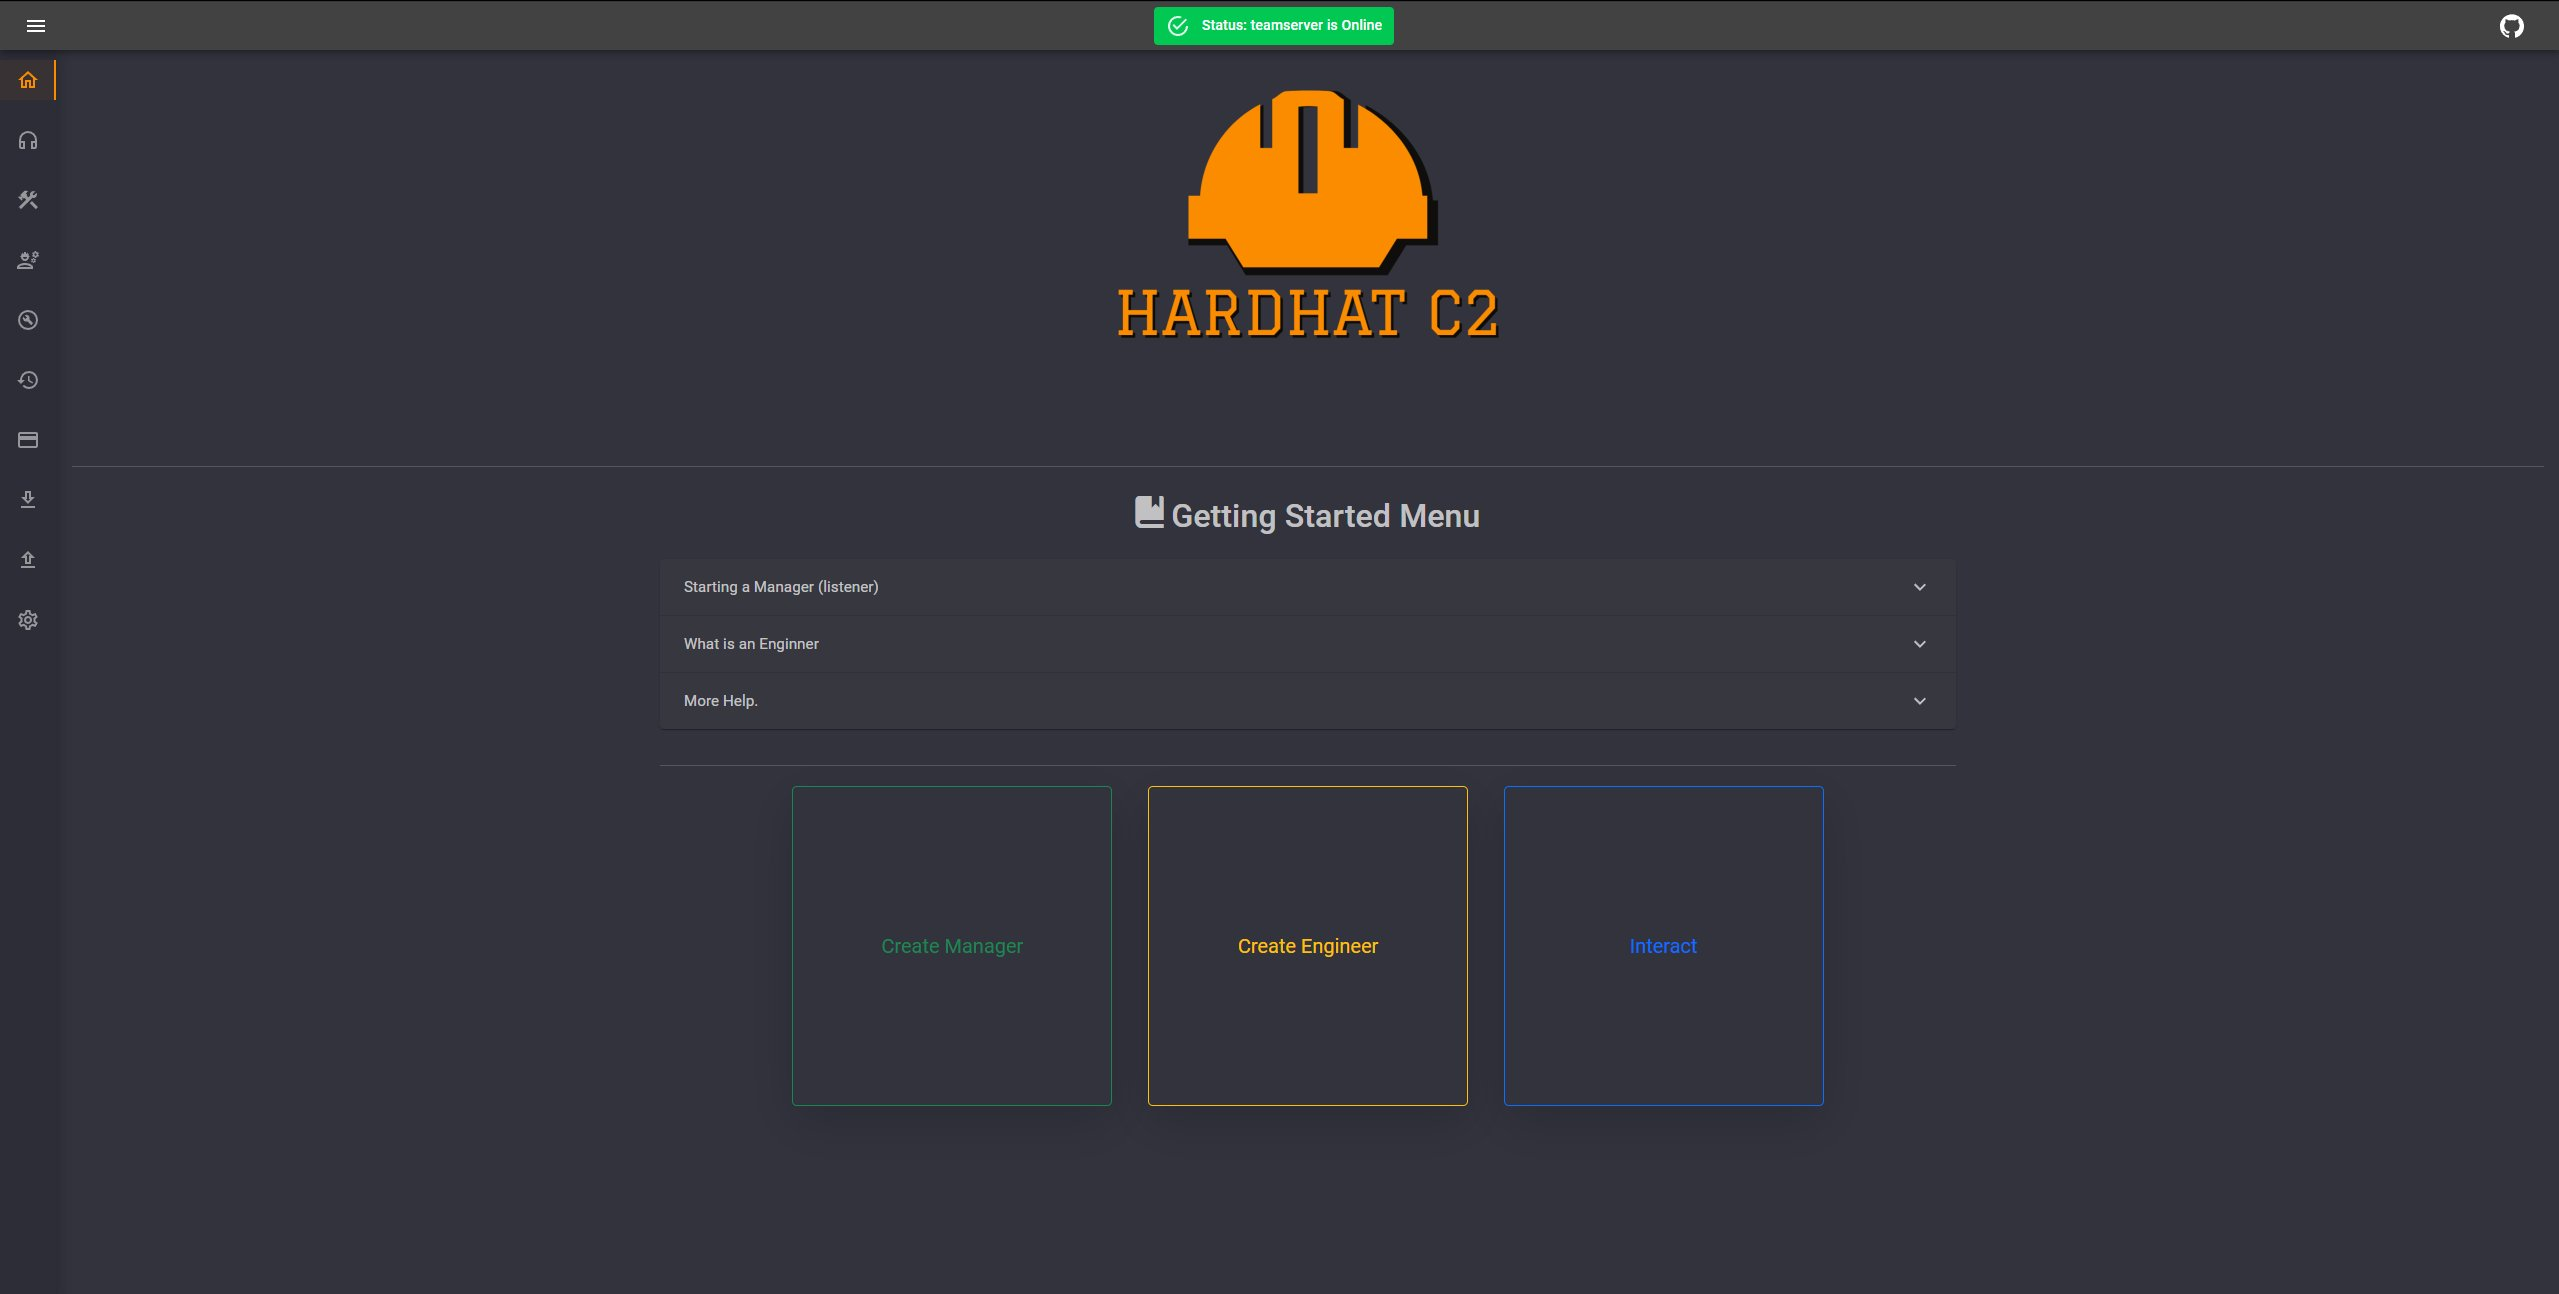 dragoqcc/cruciblec2
A C# Command & Control framework
 n1nj4sec/pupy
Pupy is an opensource, cross-platform (Windows, Linux, OSX, Android) C2 and post-exploitation framework written in python and C
 moscowchill/lstar-en
LSTAR - CobaltStrike Translated to EN
 pinarsadioglu/cve-2023-23192
CVE-2023-23192
 trickster0/offensiverust
Rust Weaponization for Red Team Engagements.
 alessandroz/pupy
Pupy is an opensource, multi-platform (Windows, Linux, OSX, Android), multi function RAT (Remote Administration Tool) mainly written in python. It…
 droidvoider/dirtycow-replacer
CVE-2016-5195 dirtycow by timwr automated multi file patch tool