
CVE-2026-19598-
 0xcyp1337/cve-2026-19598-
Exploits CVE-2026-19598 in WordPress Pods plugin to create admin accounts or overwrite passwords via unauthenticated AJAX request, with mass scanning…
exploitationpenetration-testingprivilege-escalation+2
2
0xcyp1337/cve-2026-19598-Exploits CVE-2026-19598 in WordPress Pods plugin to create admin accounts or overwrite passwords via unauthenticated AJAX request, with mass scanning…
 principlecheck/kslkatzbof
Beacon Object File for in-line LSASS credential extraction using the KslD.sys BYOVD technique. Extracts NT hashes and cleartext passwords from…
 iqbalx7/wp2shell
unauthenticated RCE in WordPress core (CVE-2026-63030 + CVE-2026-60137)
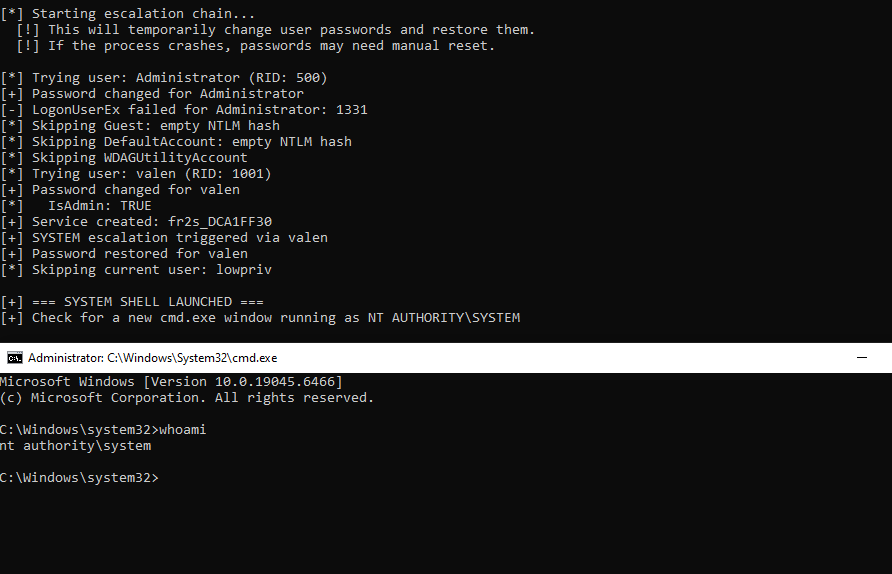
 parrotsec/mimikatz
Tool for extracting Windows credentials (passwords, hashes, Kerberos tickets) from memory and performing pass-the-hash, pass-the-ticket, and golden…
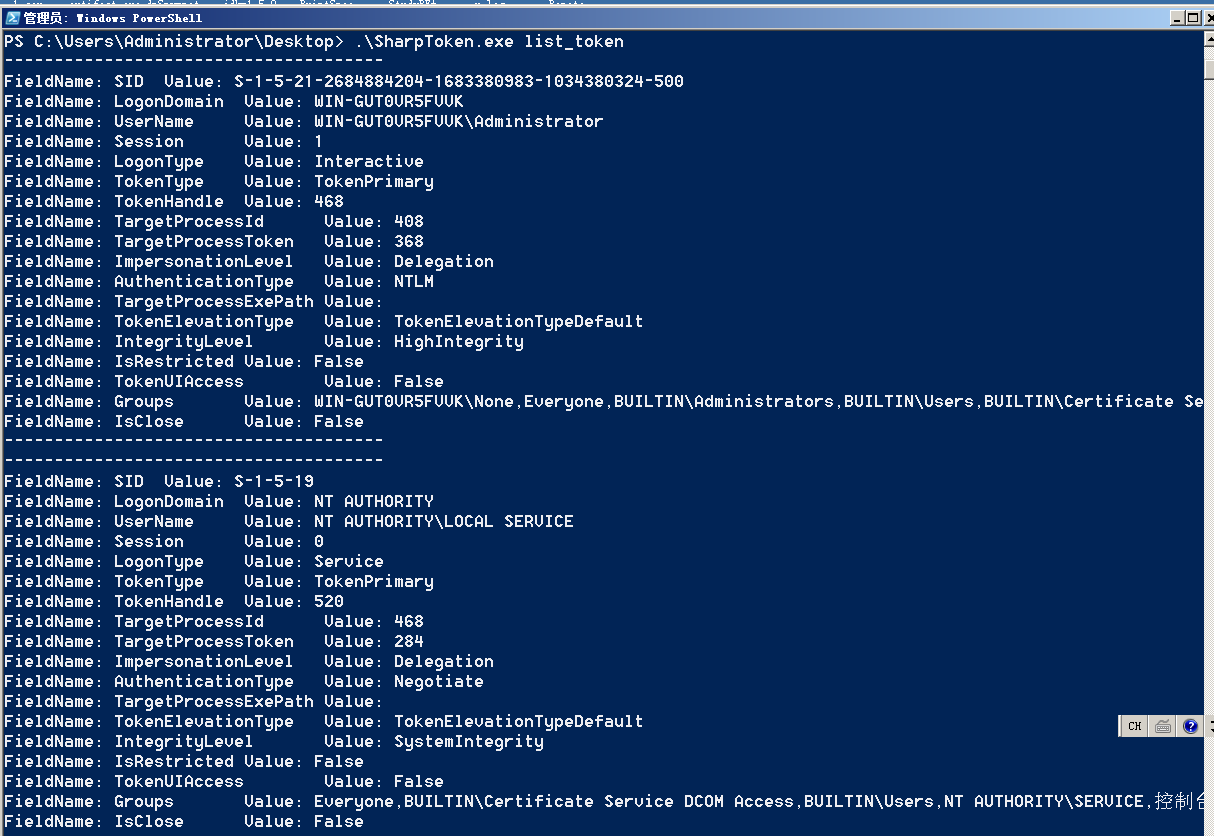 beichendream/sharptoken
Windows token theft and privilege escalation tool that steals leaked tokens from processes, enables SYSTEM-level access, user impersonation, and…
 fadi002/unshackle
Open-source tool to bypass windows and linux passwords from bootable usb
 darkcodersc/win-brute-logon
Crack any Microsoft Windows users password without any privilege (Guest account included)
 c3rrberu5/zerologon-to-shell
Automated exploit script combining CVE-2020-1472 (ZeroLogon) with evil-winrm to gain a remote shell on vulnerable Windows Domain Controllers.
 mwr-cybersec/pxethief
PXEThief is a set of tooling that can extract passwords from the Operating System Deployment functionality in Microsoft Endpoint Configuration Manager
 bypazs/cve-2023-26984
An issue in the password reset function of Peppermint v0.2.4 allows attackers to access the emails and passwords of the Tickets page via a crafted…
 sleventyeleven/linuxprivchecker
Local Linux enumeration script that identifies privilege escalation vectors including misconfigurations, world-writable files, clear-text passwords,…
 midpipps/cve-2020-1472-easy
A simple implementation/code smash of a bunch of other repos
 mstxq17/cve-2020-1472
cve-2020-1472 复现利用及其exp
 0xcccc666/cve-2020-1472_tool-collection
cve-2020-1472_Tool collection
 screetsec/brutal
Payload for teensy like a rubber ducky but the syntax is different. this Human interfaes device ( HID attacks ). Penetration With Teensy . Brutal is…
 samratashok/kautilya
Kautilya - Tool for easy use of Human Interface Devices for offensive security and penetration testing.
 cyberark/riskyspn
Detect and abuse risky SPNs