

AdStrike
 capture0x/adstrike
AI-powered modular Active Directory red-team framework for authorized penetration testing, AD enumeration, attack-path analysis, Kerberos/ADCS…
ai-securitycommand-and-controlexploitation+7
403
capture0x/adstrikeAI-powered modular Active Directory red-team framework for authorized penetration testing, AD enumeration, attack-path analysis, Kerberos/ADCS…
 karmanya03/overthrone
All-Rust Active Directory exploitation framework: LDAP/SMB/Kerberos enumeration, attack-graph pathfinding, Kerberoasting, NTLM relay, ticket forging,…
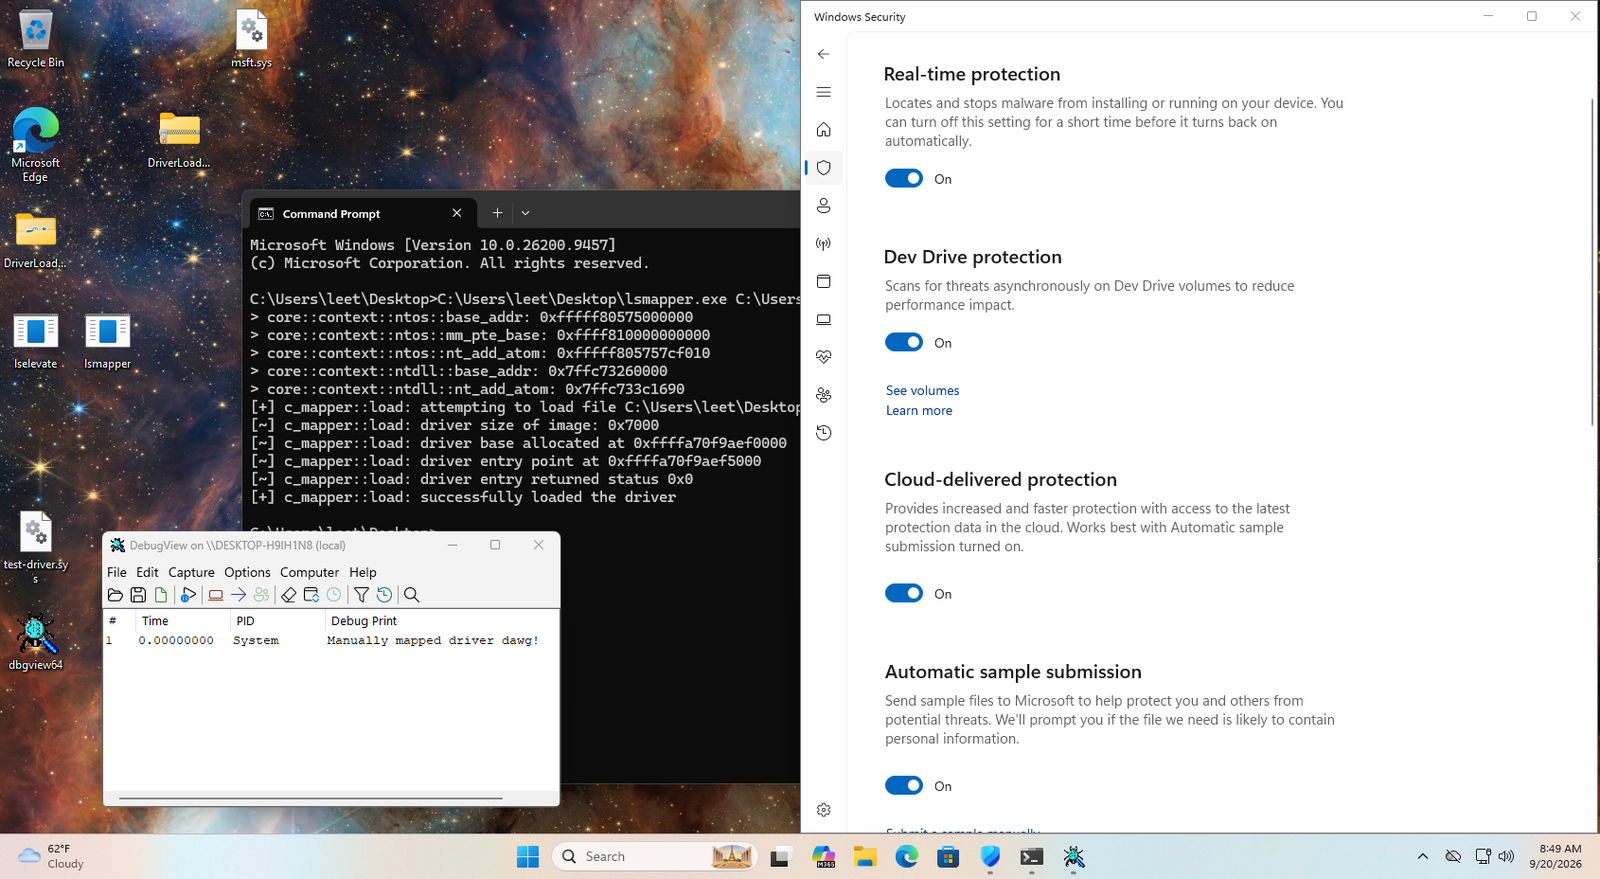 nbs32k/localstranger
PoC for WinNotify, demonstrated through a driver mapper, and local privilege escalation.
 mandiant/gopacket
A complete Go port of Impacket - 63 CLI tools and 24 libraries for Windows & Active Directory protocol attacks, compiled to a single dependency-free…
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 teamn4c/sg-2026-0024
CVE-2026-43284 and CVE-2026-43500 Dirty Frag PoC and exploit
 s1eezer/cve-2026-8069
Technical write-up and proof-of-concept for CVE-2026-8069, a local privilege escalation in Acer NitroSense and PredatorSense services, exploiting a…
 dbgbgtf1/cve-2026-40369-exploit
Exploit for CVE-2026-40369 that leverages kernel address leak and token forging to achieve privilege escalation in a browser sandbox environment.
 0b0111100/2004
Linux kernel privilege escalation exploits targeting CVE-2004-0077 and CVE-2004-1235, including caps_to_root technique for gaining root access.
 ethanevans92/cve-2025-32463
Proof-of-concept exploit for CVE-2025-32463, a local privilege escalation in sudo. Demonstrates chroot-based NSS manipulation to load a malicious…
 hackspeak/cve-2026-62735
Local privilege escalation exploit for Windows HTTP.sys integer overflow (CVE-2026-62735), demonstrating crash and full SYSTEM shell via nonpaged…
 ximerag/dast
Exploit for CVE-2026-0828 targeting Safetica ProcessMonitorDriver.sys to terminate processes and spawn a SYSTEM shell.
 lkeld/cve-2026-43499-poc
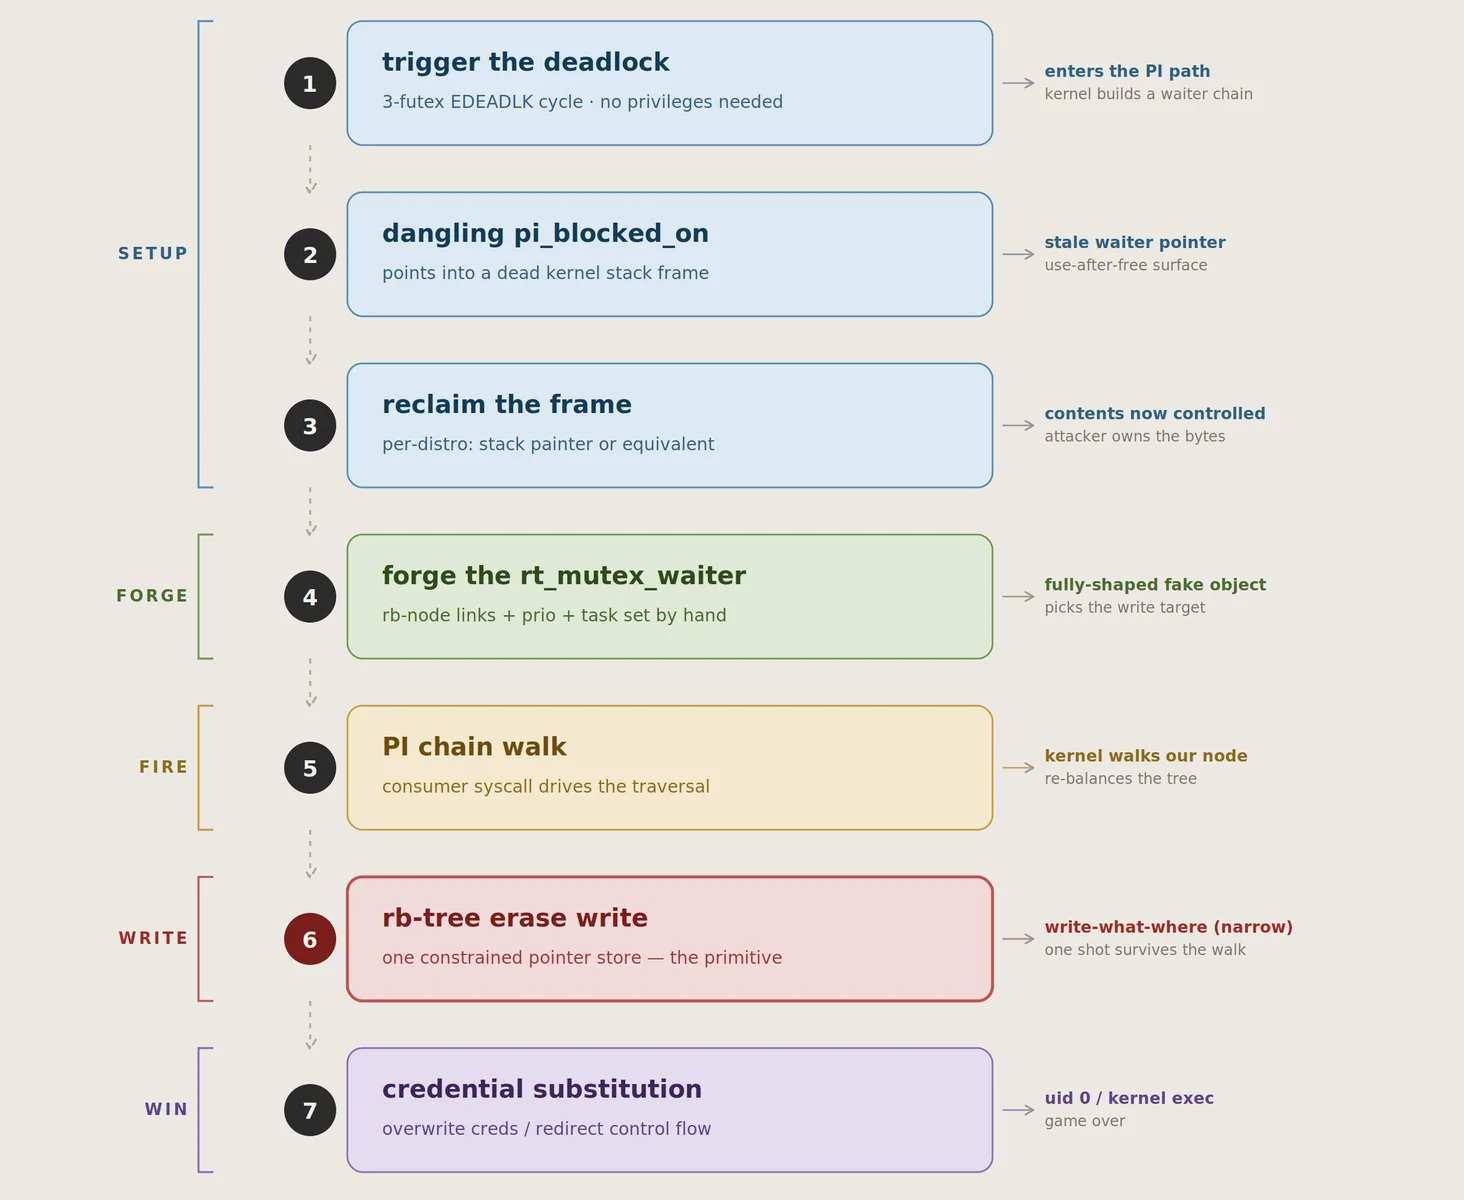
Weaponized proof-of-concept for CVE-2026-43499 (GhostLock), a Linux kernel rtmutex bug enabling local privilege escalation. Includes per-distribution…
 r3dw4n48m3d/cve-2021-3493-exploit
C-based local privilege escalation exploit for CVE-2021-3493, targeting OverlayFS in Linux kernels prior to 5.11. Provides compilation and usage…
 cyghtinc/cve-2024-30088-binary-lpe-privielege-escalation-cyght-toctou
Compiled proof-of-concept binary for local privilege escalation exploiting CVE-2024-30088, a TOCTOU vulnerability, targeting Windows systems.
 mindsflee/winflesher
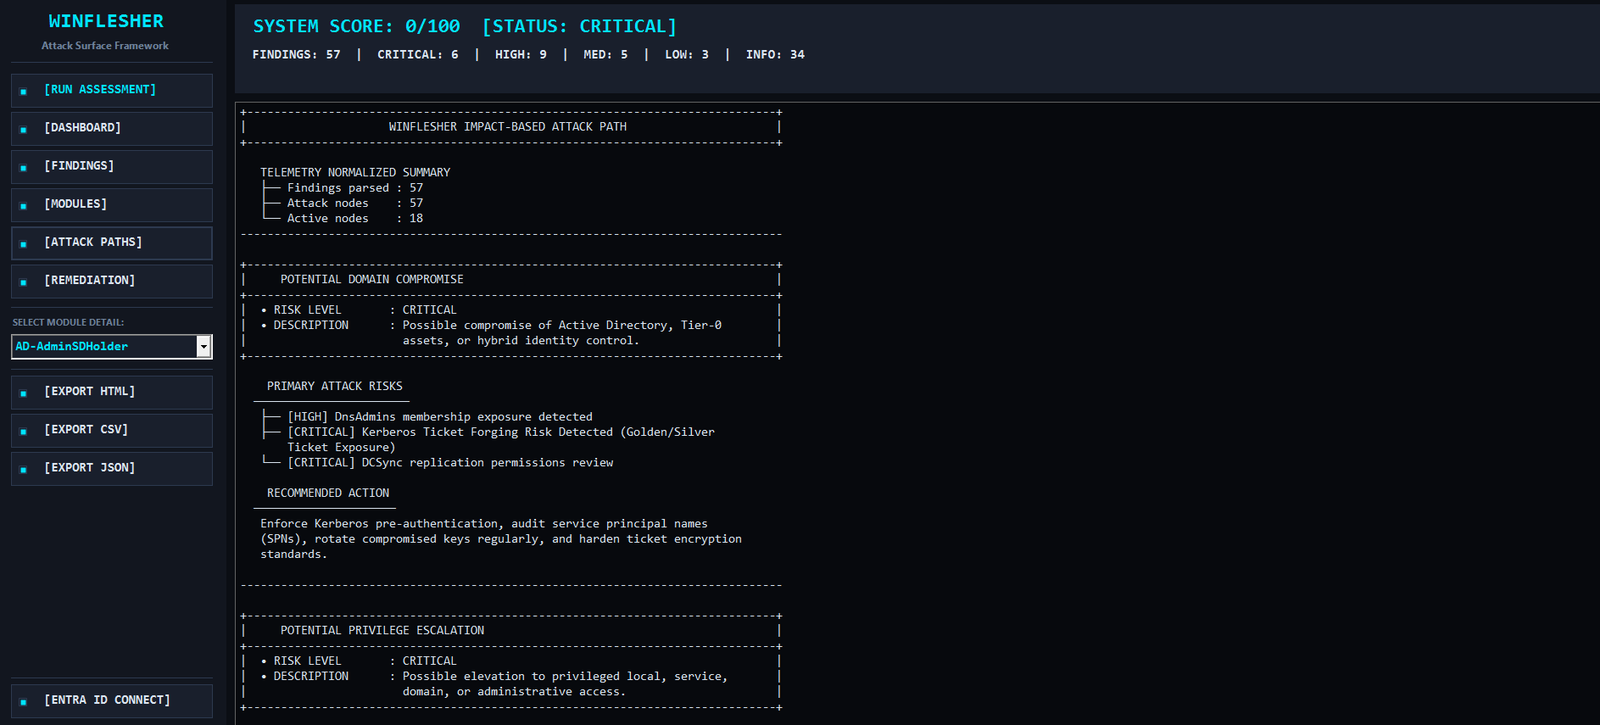
Automated attack surface assessment framework for Active Directory and local infrastructures, correlating vulnerabilities with attack paths to domain…
 xd20111/cve-2026-31431
Documentation and analysis of a local privilege escalation vulnerability in the Linux kernel's authencesn template via AF_ALG and splice(), including…
 vyahello/cve-2026-31431
Linux local privilege escalation exploit for CVE-2026-31431, abusing the AF_ALG crypto API with splice() to modify page cache and spawn a root shell.