

Overthrone
 karmanya03/overthrone
All-Rust Active Directory exploitation framework: LDAP/SMB/Kerberos enumeration, attack-graph pathfinding, Kerberoasting, NTLM relay, ticket forging,…
command-and-controlexploit-frameworksinformation-gathering+8
31
karmanya03/overthroneAll-Rust Active Directory exploitation framework: LDAP/SMB/Kerberos enumeration, attack-graph pathfinding, Kerberoasting, NTLM relay, ticket forging,…
 itm4n/privesccheck
Privilege Escalation Enumeration Script for Windows
 omar-tamerr/horuseye
AI-Powered Active Directory Attack Platform
 peass-ng/peass-ng
PEASS - Privilege Escalation Awesome Scripts SUITE (with colors)
 capture0x/adstrike
AI-powered modular Active Directory red-team framework for authorized penetration testing, AD enumeration, attack-path analysis, Kerberos/ADCS…
 swisskyrepo/payloadsallthethings
A list of useful payloads and bypass for Web Application Security and Pentest/CTF
 mitsu-bis/security-portfolio
Security portfolio of original responsible-disclosure findings, CTF and lab write-ups, methodology notes, and purpose-built pentest tooling covering…
 61106960/adpeas
Powershell tool to automate Active Directory enumeration.
 owasp/owasp-cstg
Vendor-neutral cloud security testing guide with structured phases for enumeration, privilege escalation, lateral movement, and post-exploitation…
 wattocyber/custom-oscp-tooling
OSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…
 ly4k/certipy
Tool for Active Directory Certificate Services enumeration and abuse
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 ghostpack/seatbelt
Seatbelt is a C# project that performs a number of security oriented host-survey "safety checks" relevant from both offensive and defensive security…
 mwr-cybersec/pxethief
PXEThief is a set of tooling that can extract passwords from the Operating System Deployment functionality in Microsoft Endpoint Configuration Manager
 kr0no/bloodhound-shell
An interactive command-line shell for BloodHound API.
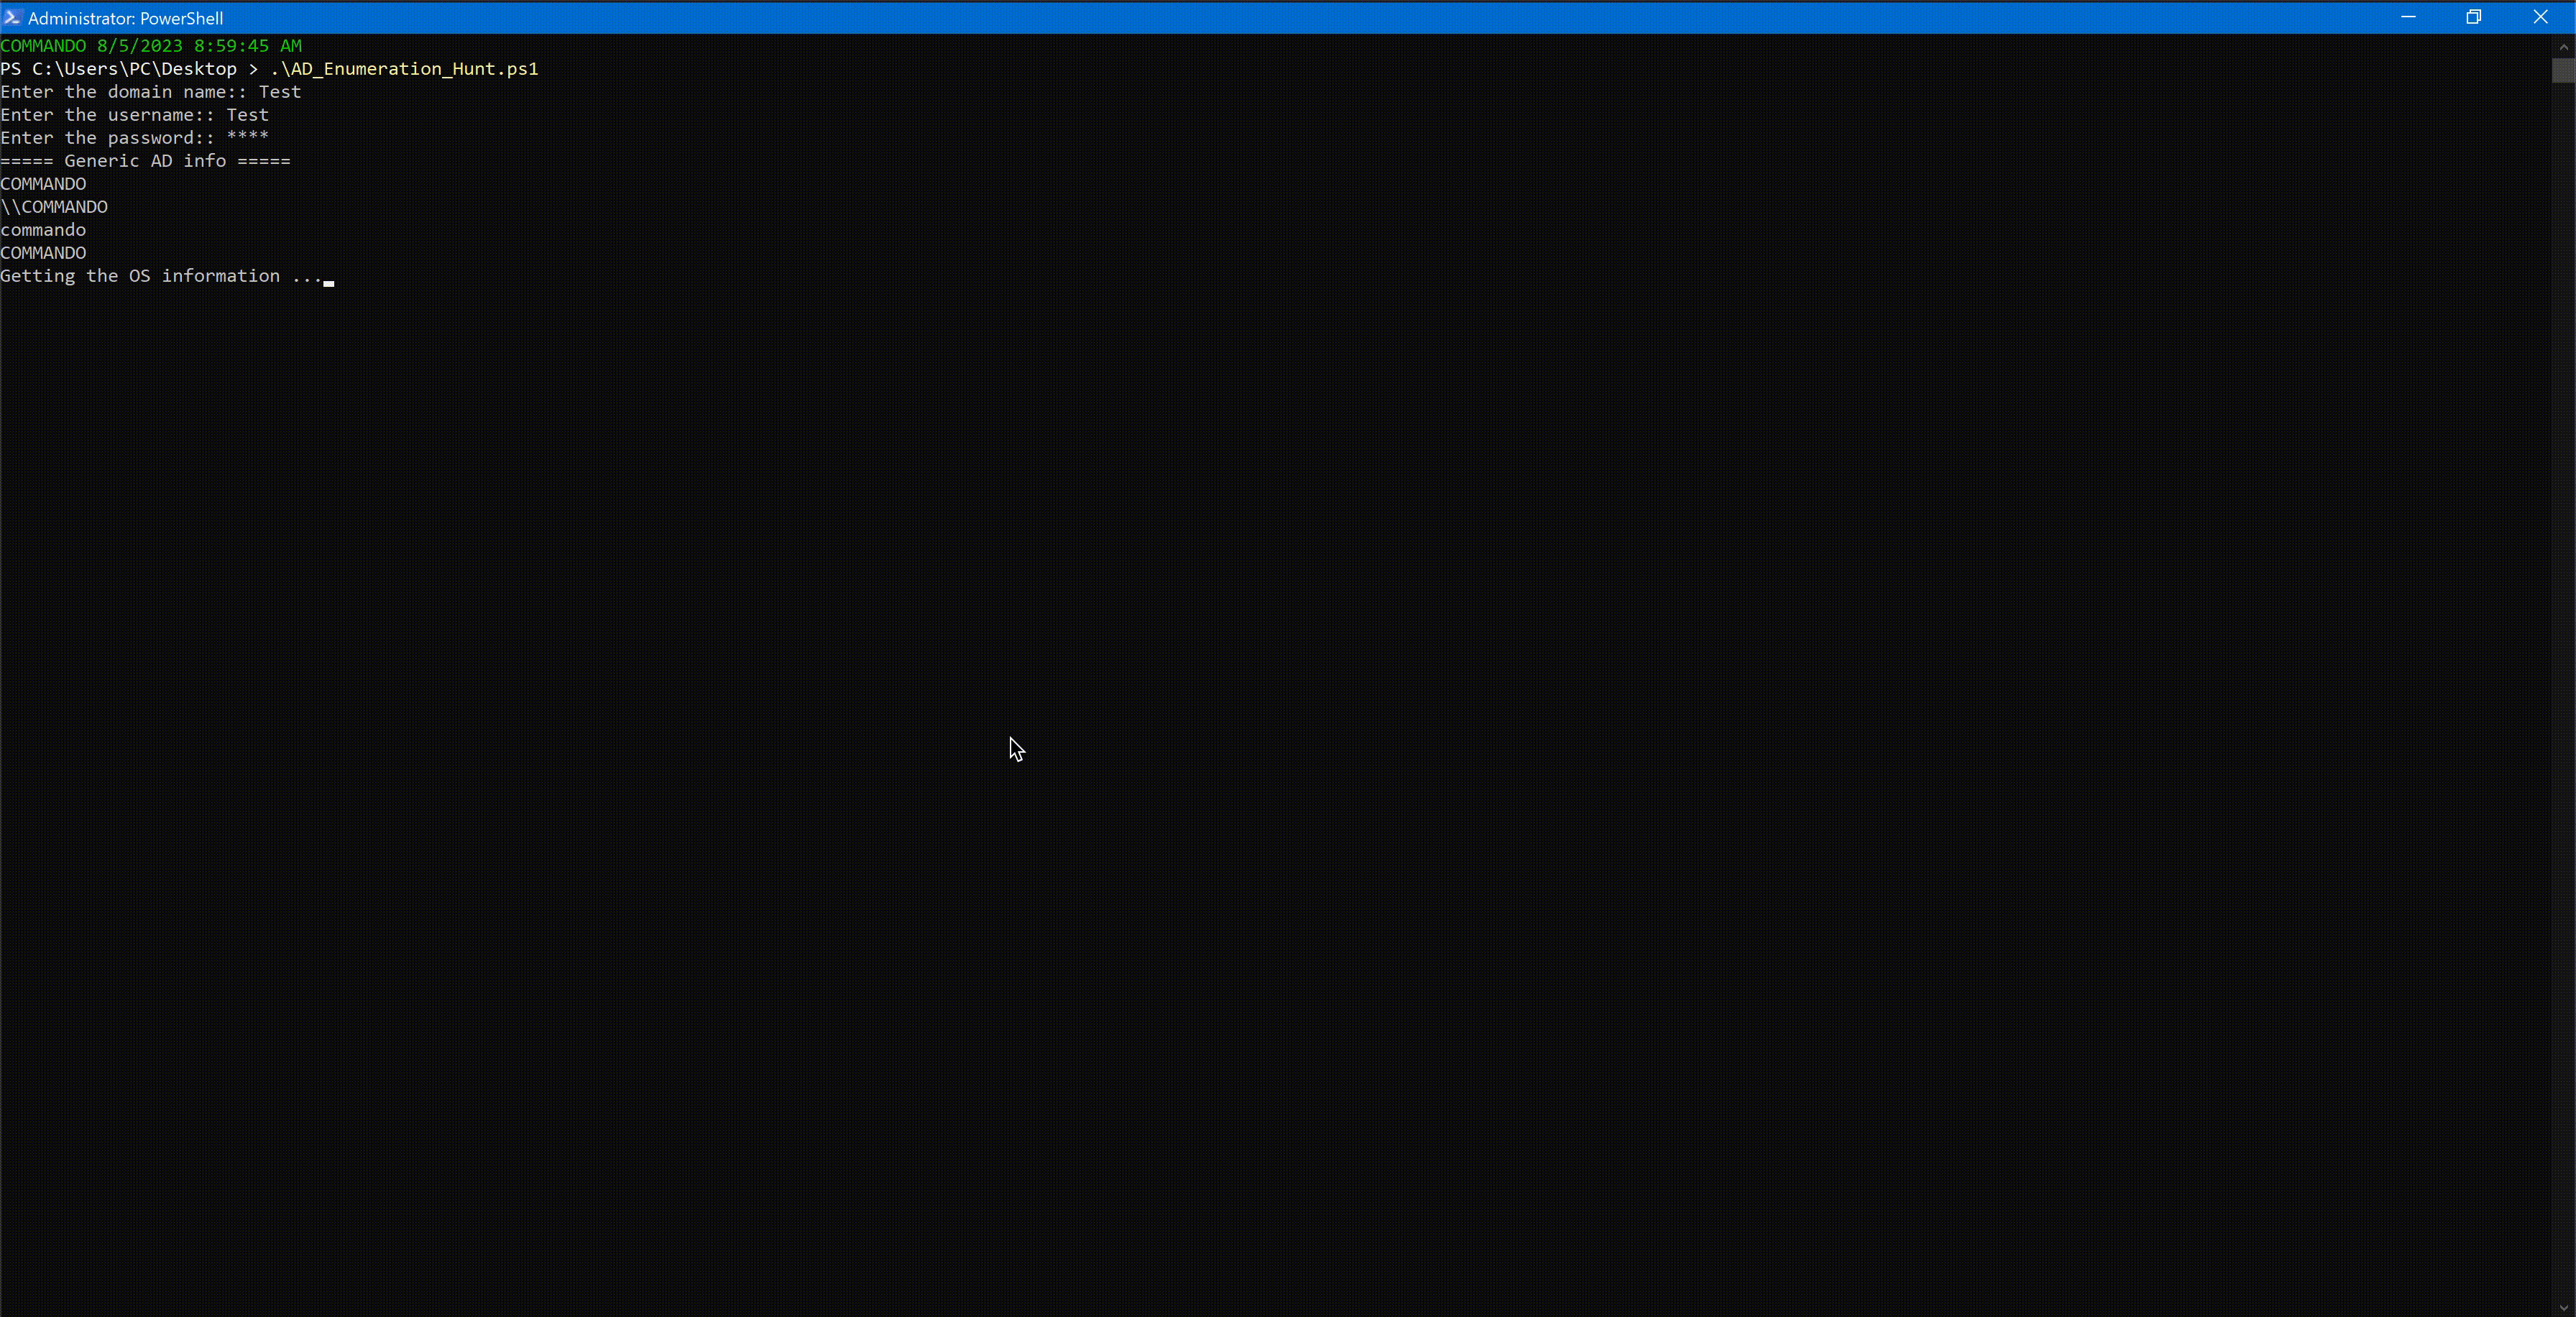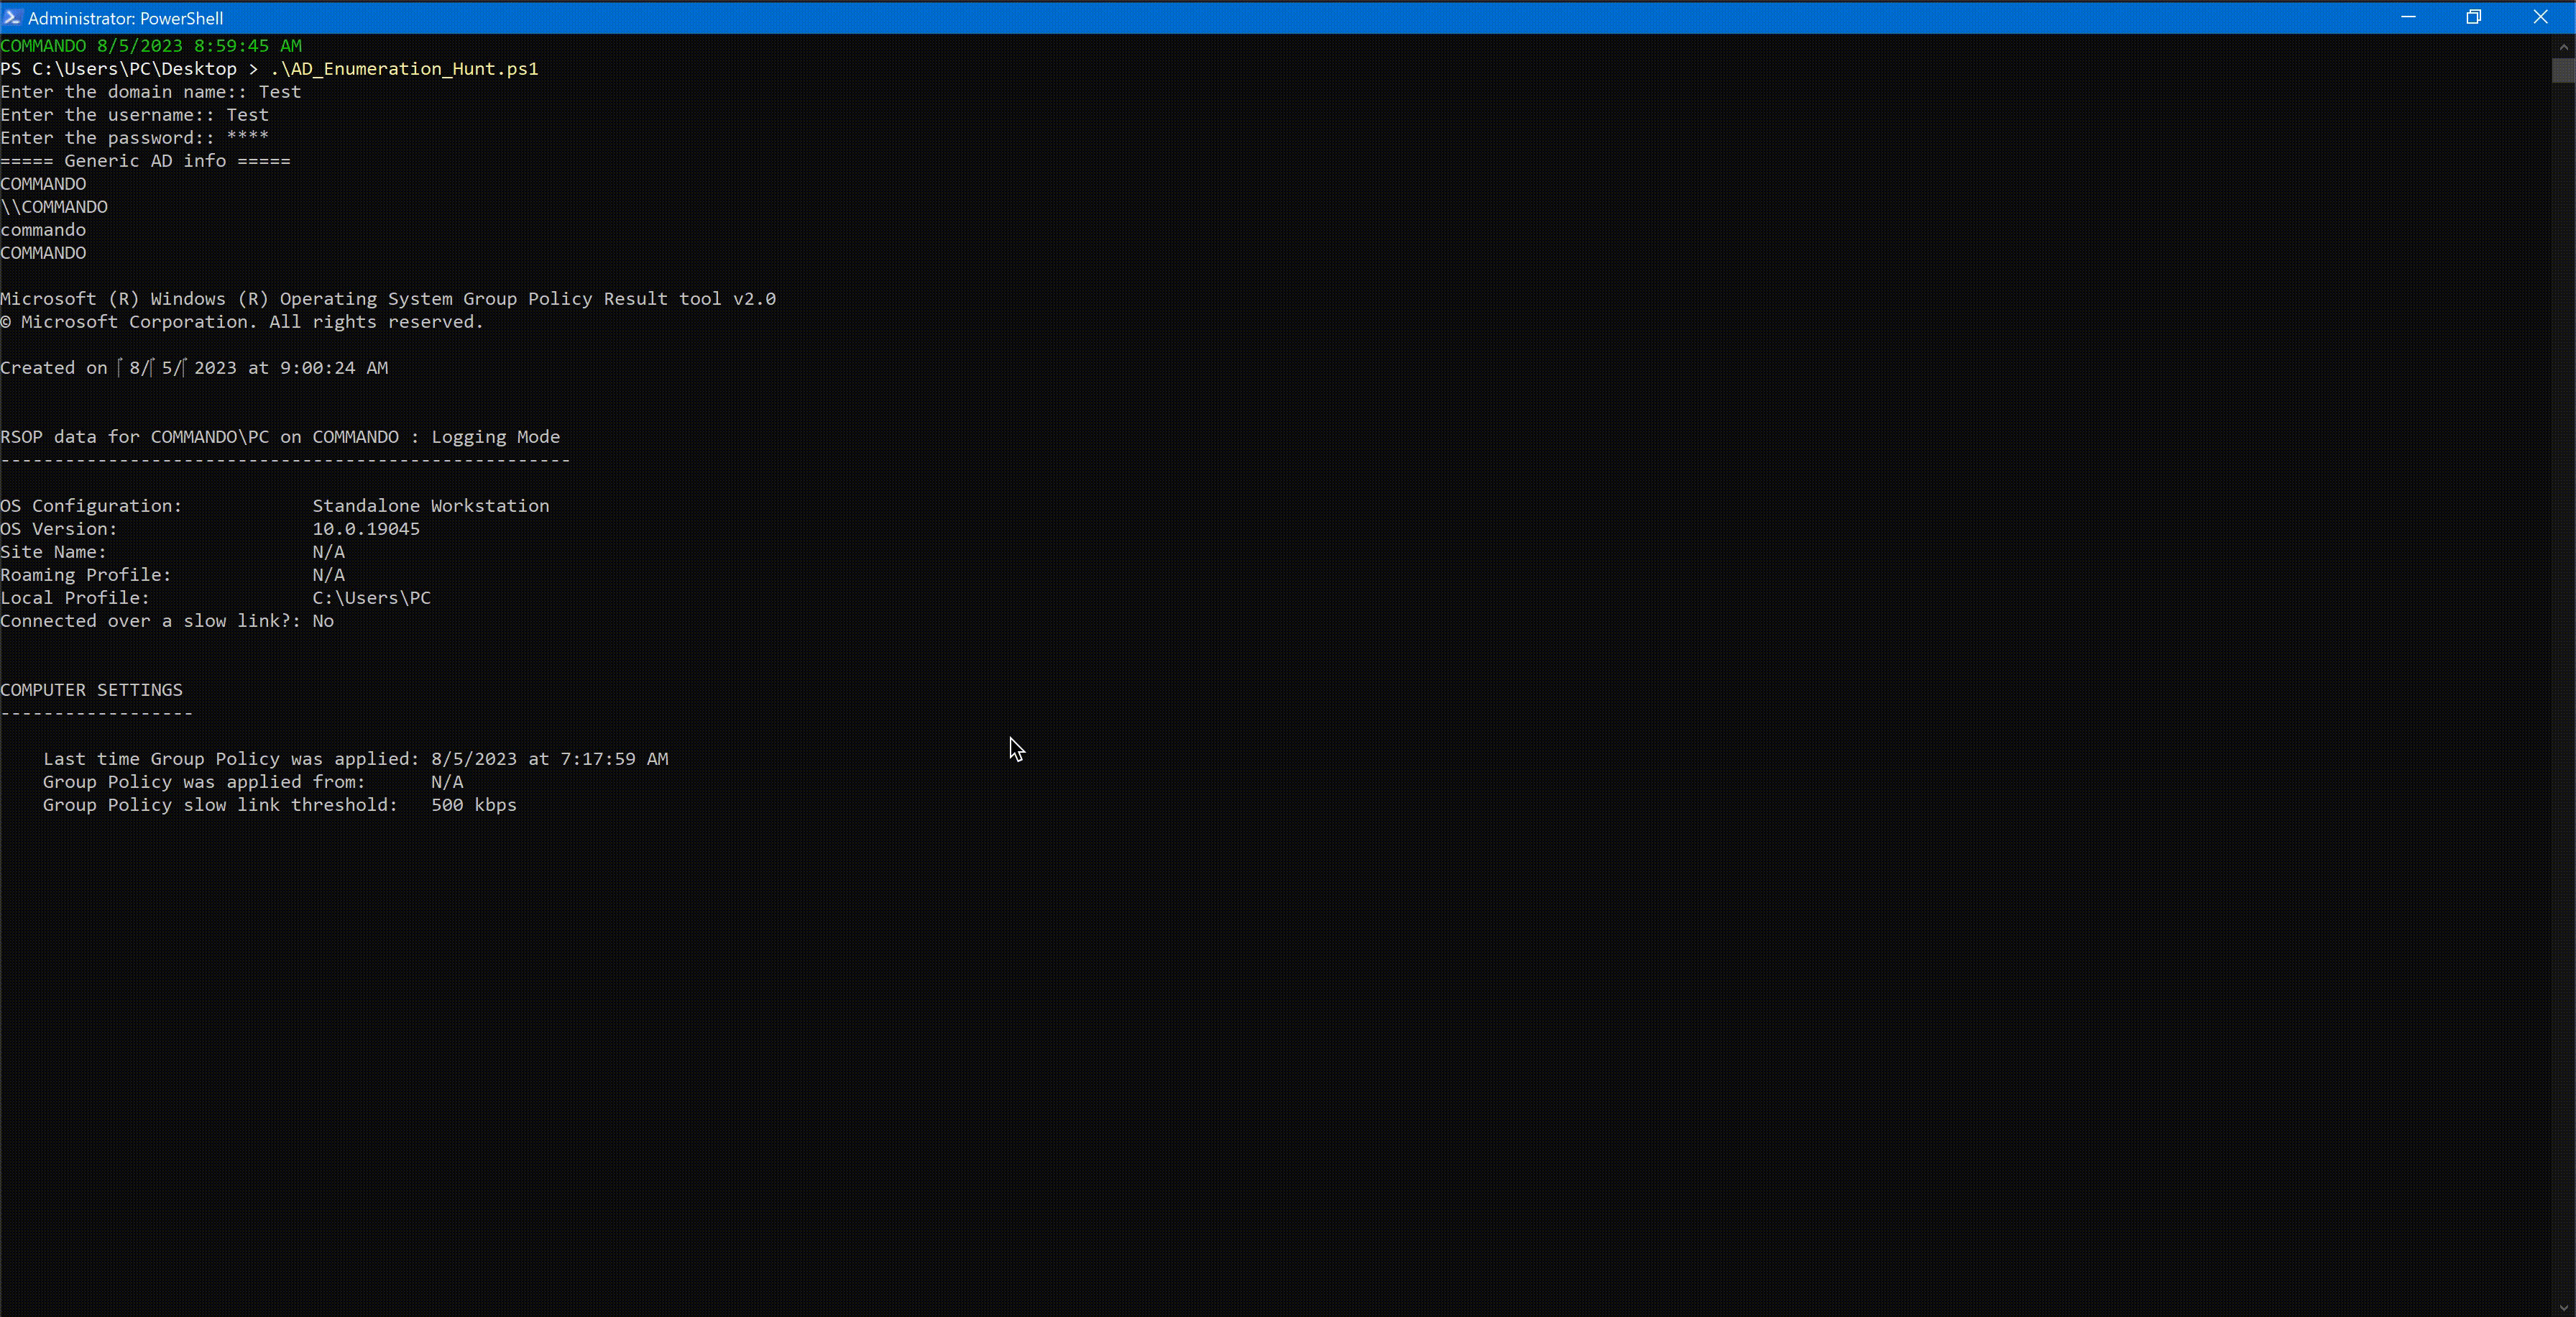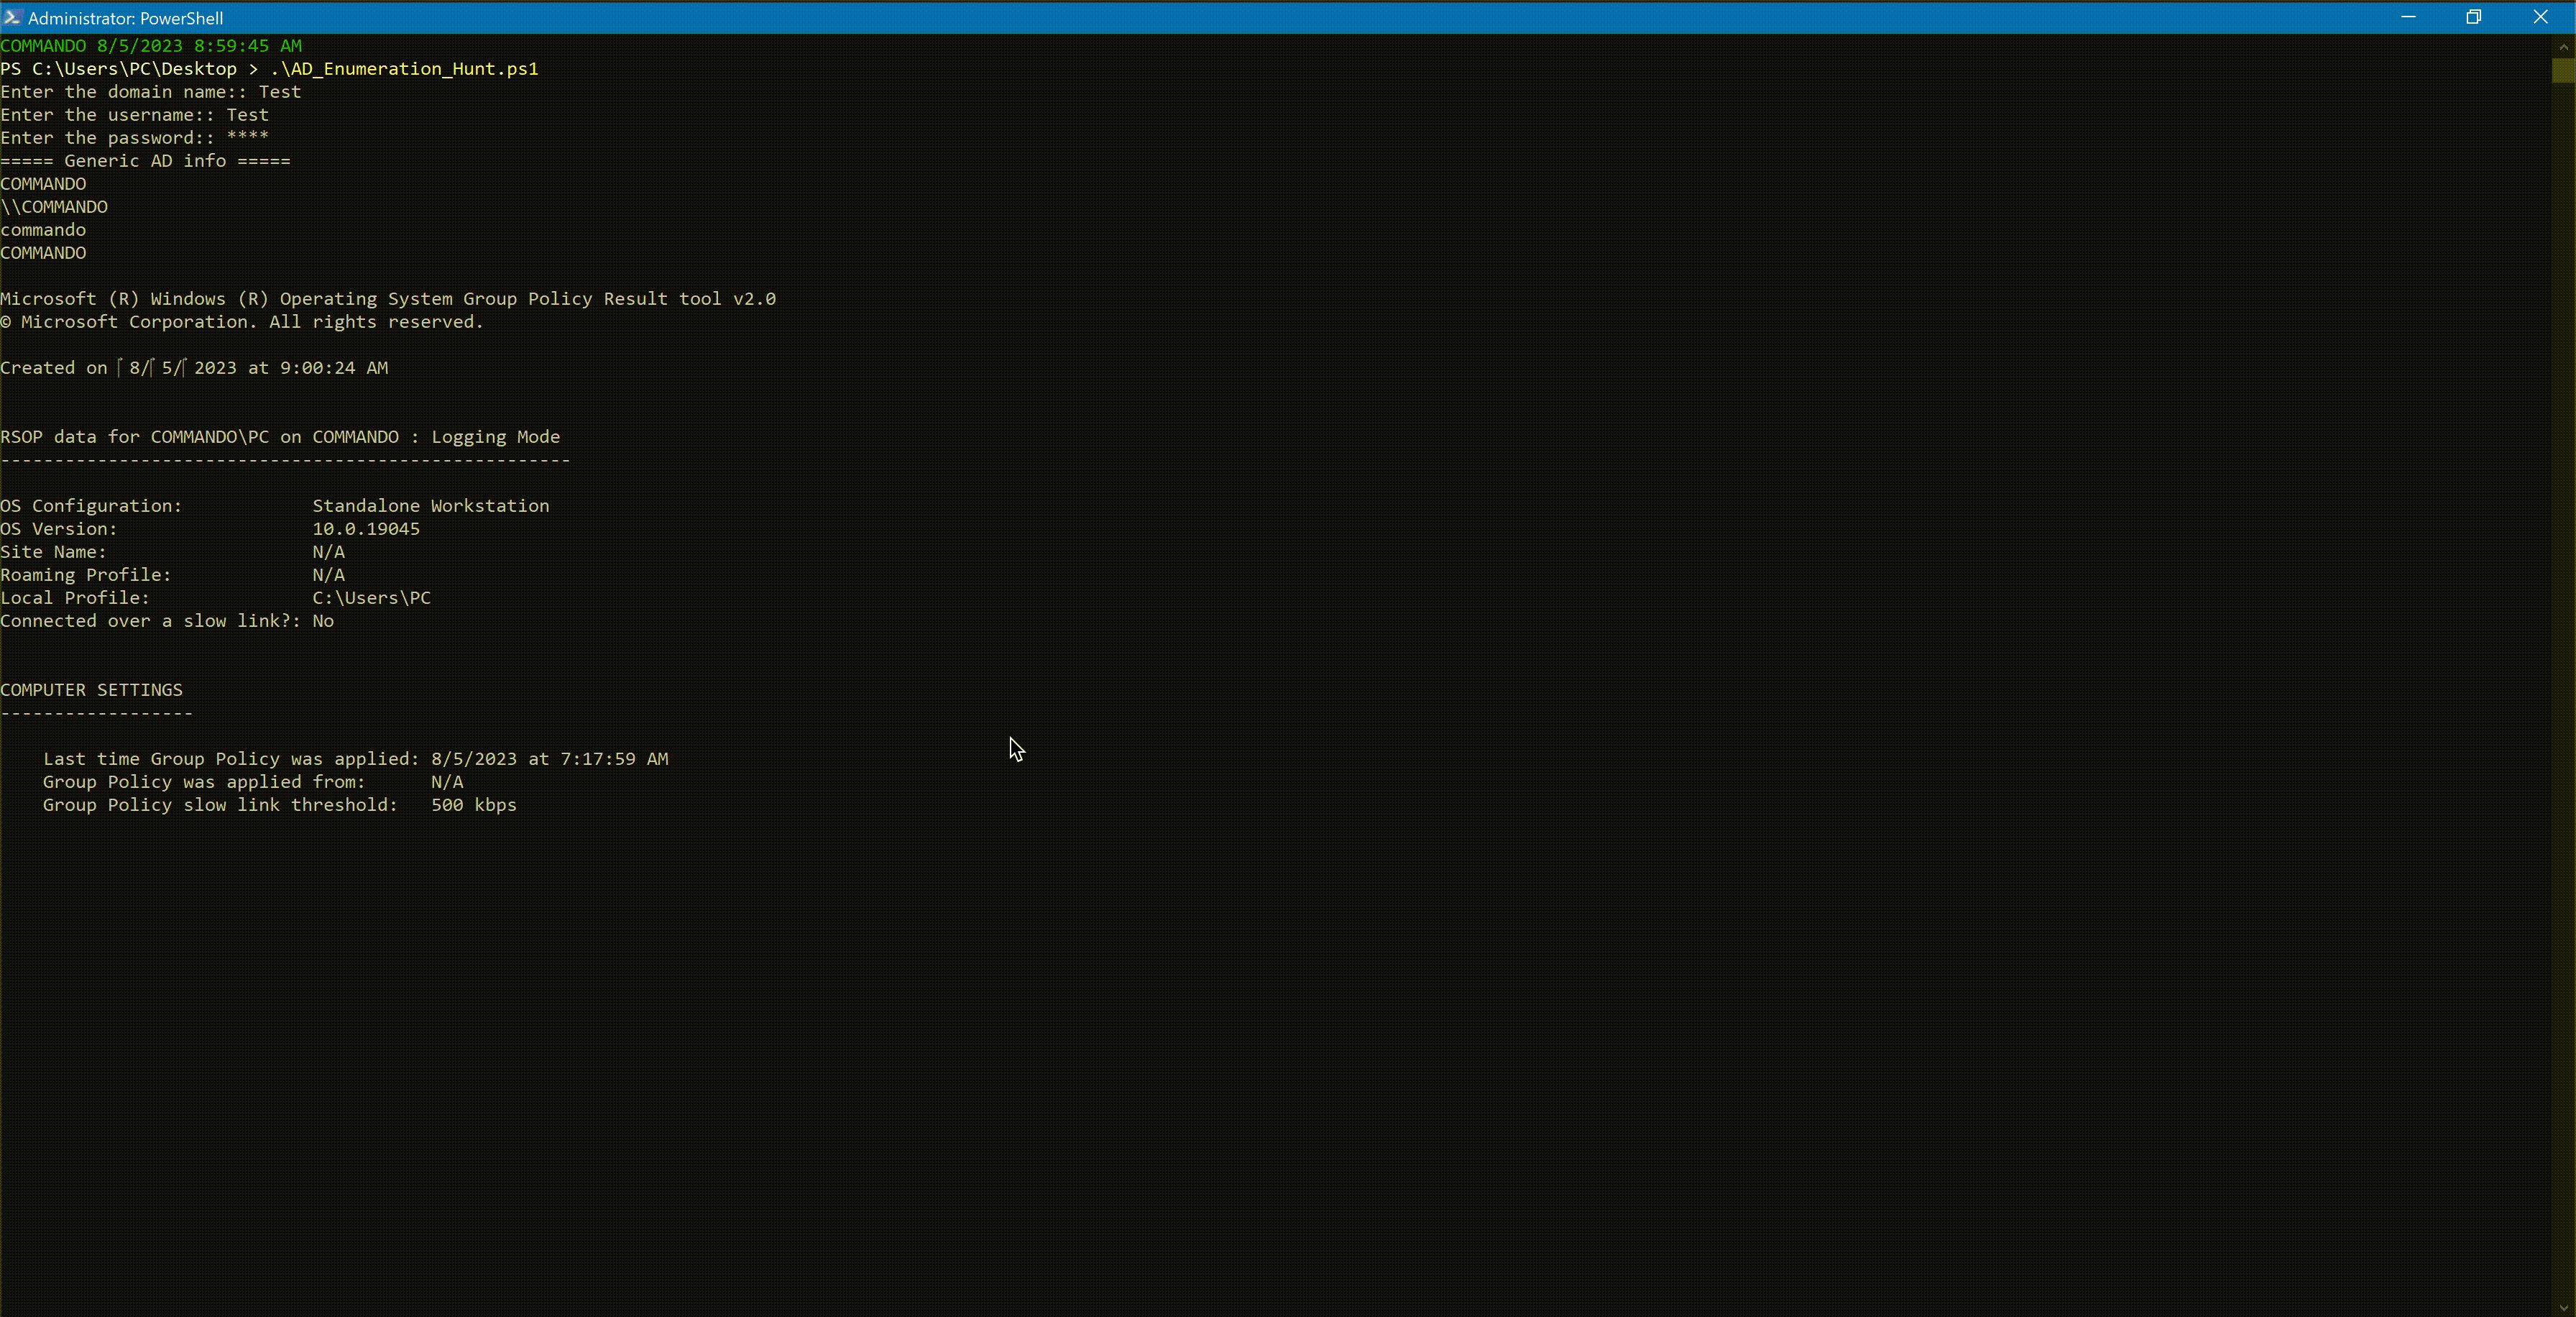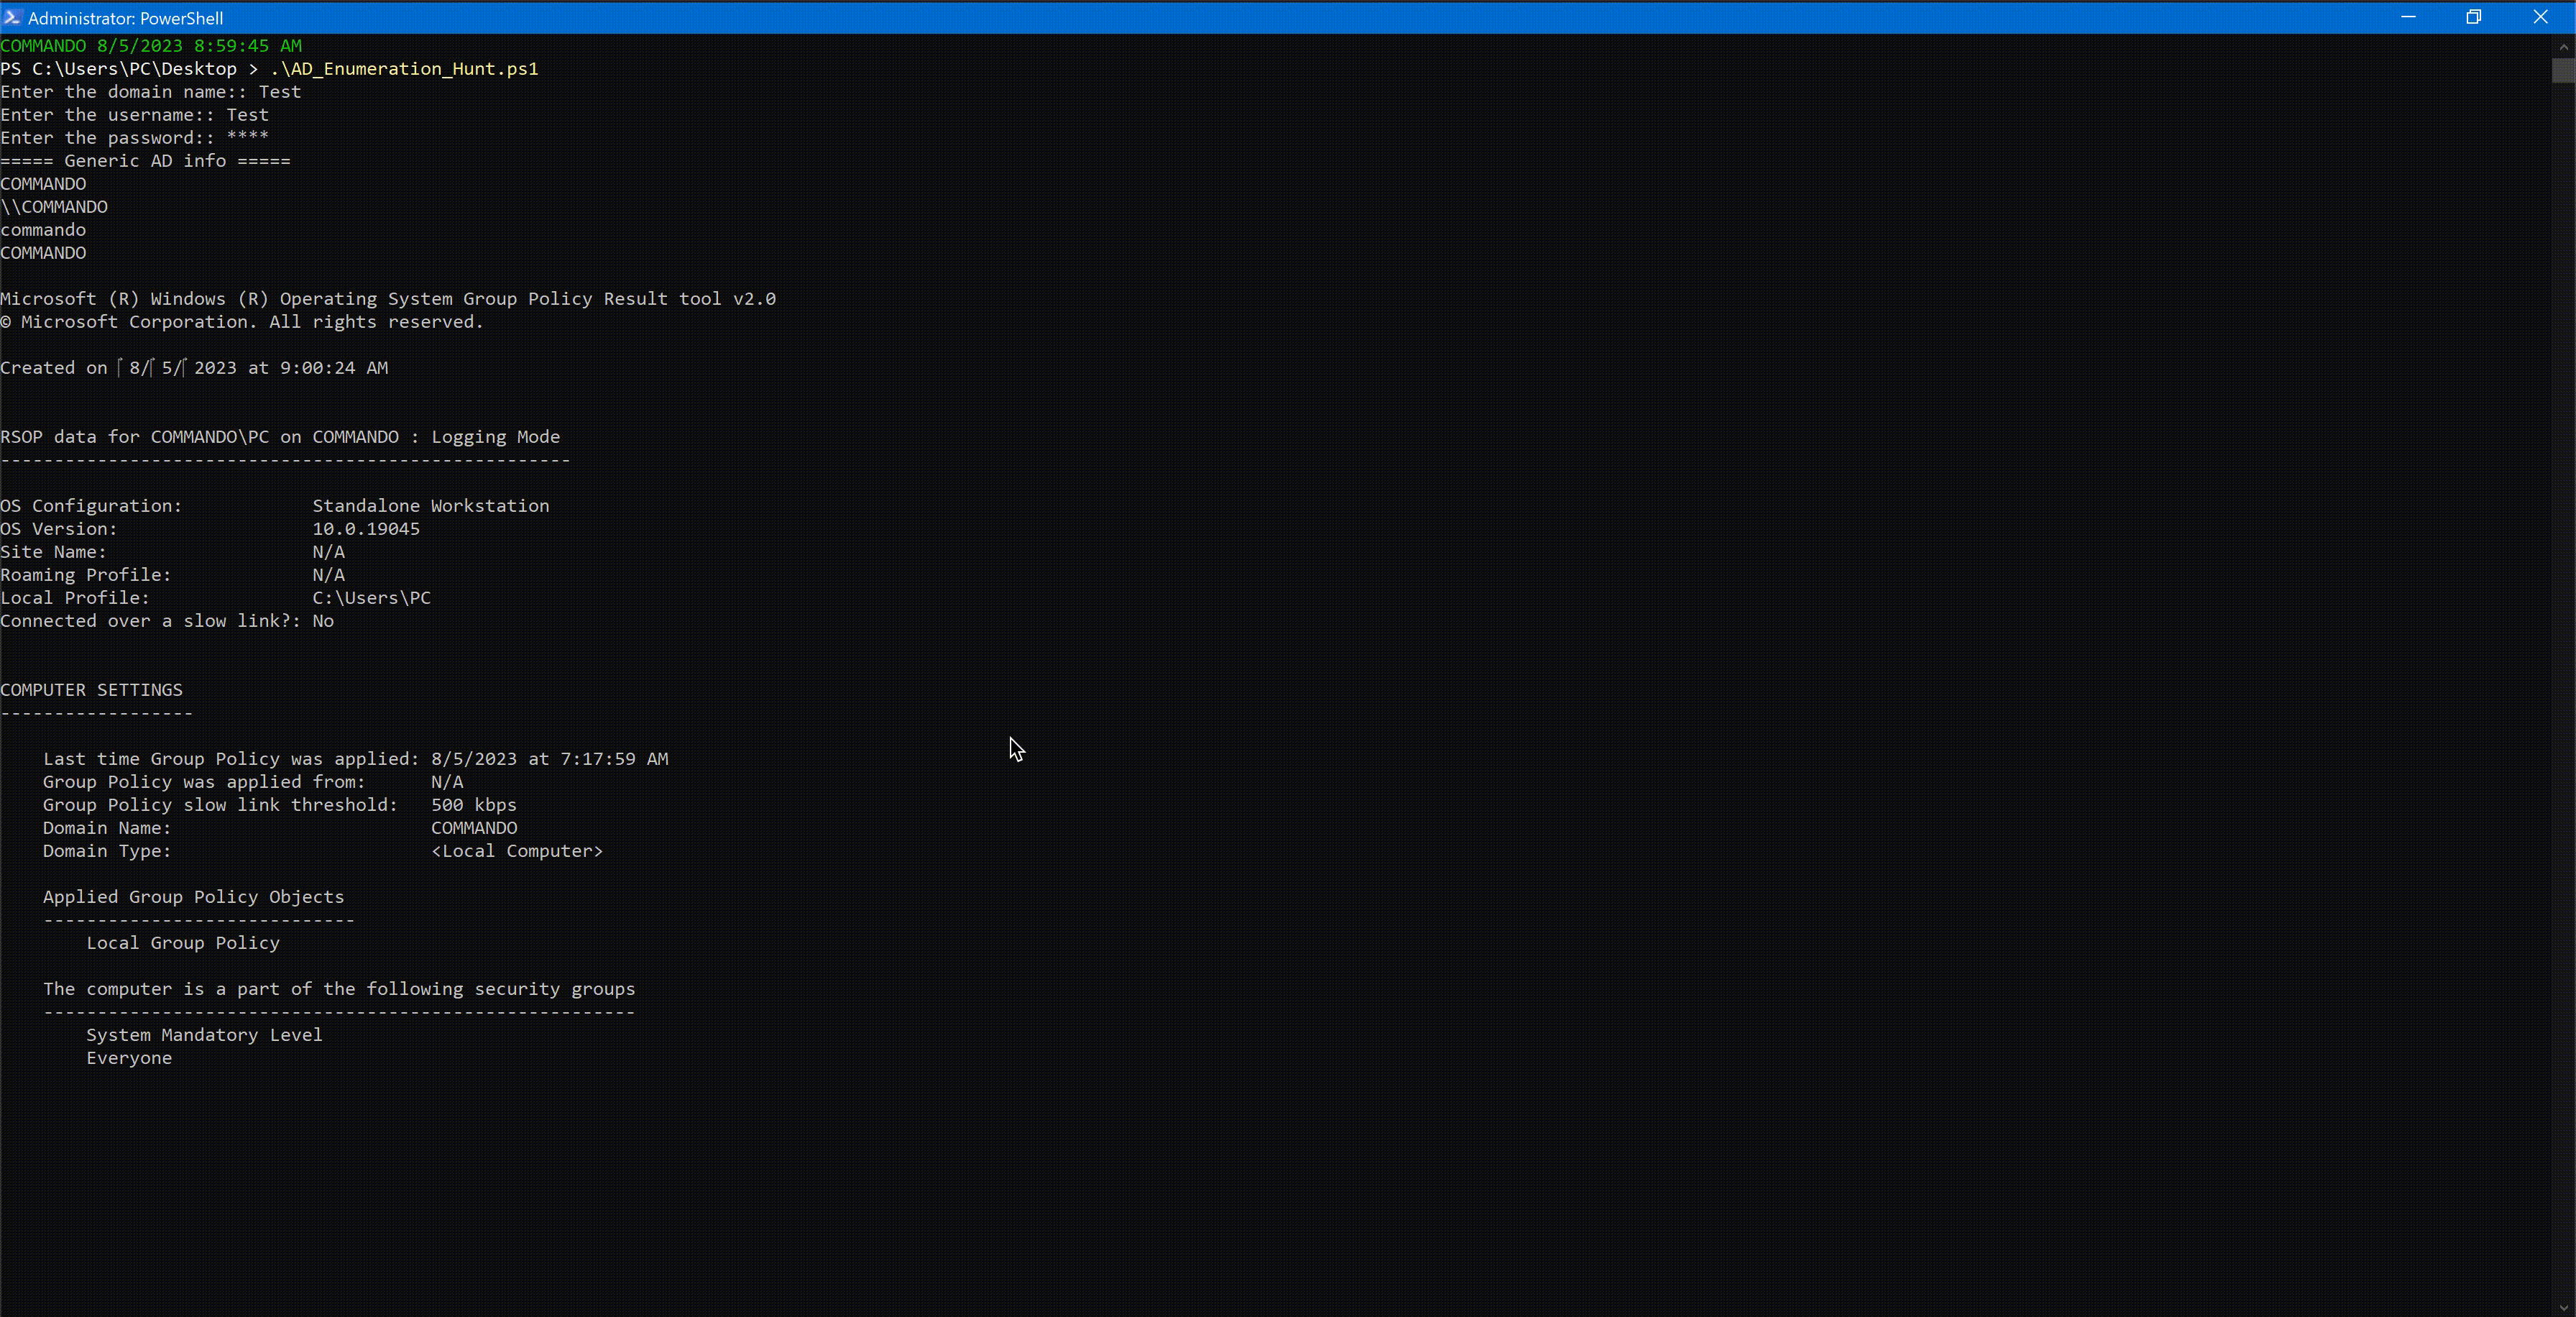 alperenugurlu/ad_enumeration_hunt
PowerShell toolkit for Active Directory penetration testing, featuring domain/user/group enumeration, trust relationship analysis, RDP configuration,…
 a-poc/redteam-tools
Tools and Techniques for Red Team / Penetration Testing
 gianlucaborello/libprocesshider
LD_PRELOAD shared library that hides a Linux process from tools like ps and lsof by intercepting readdir and proc filesystem calls.