
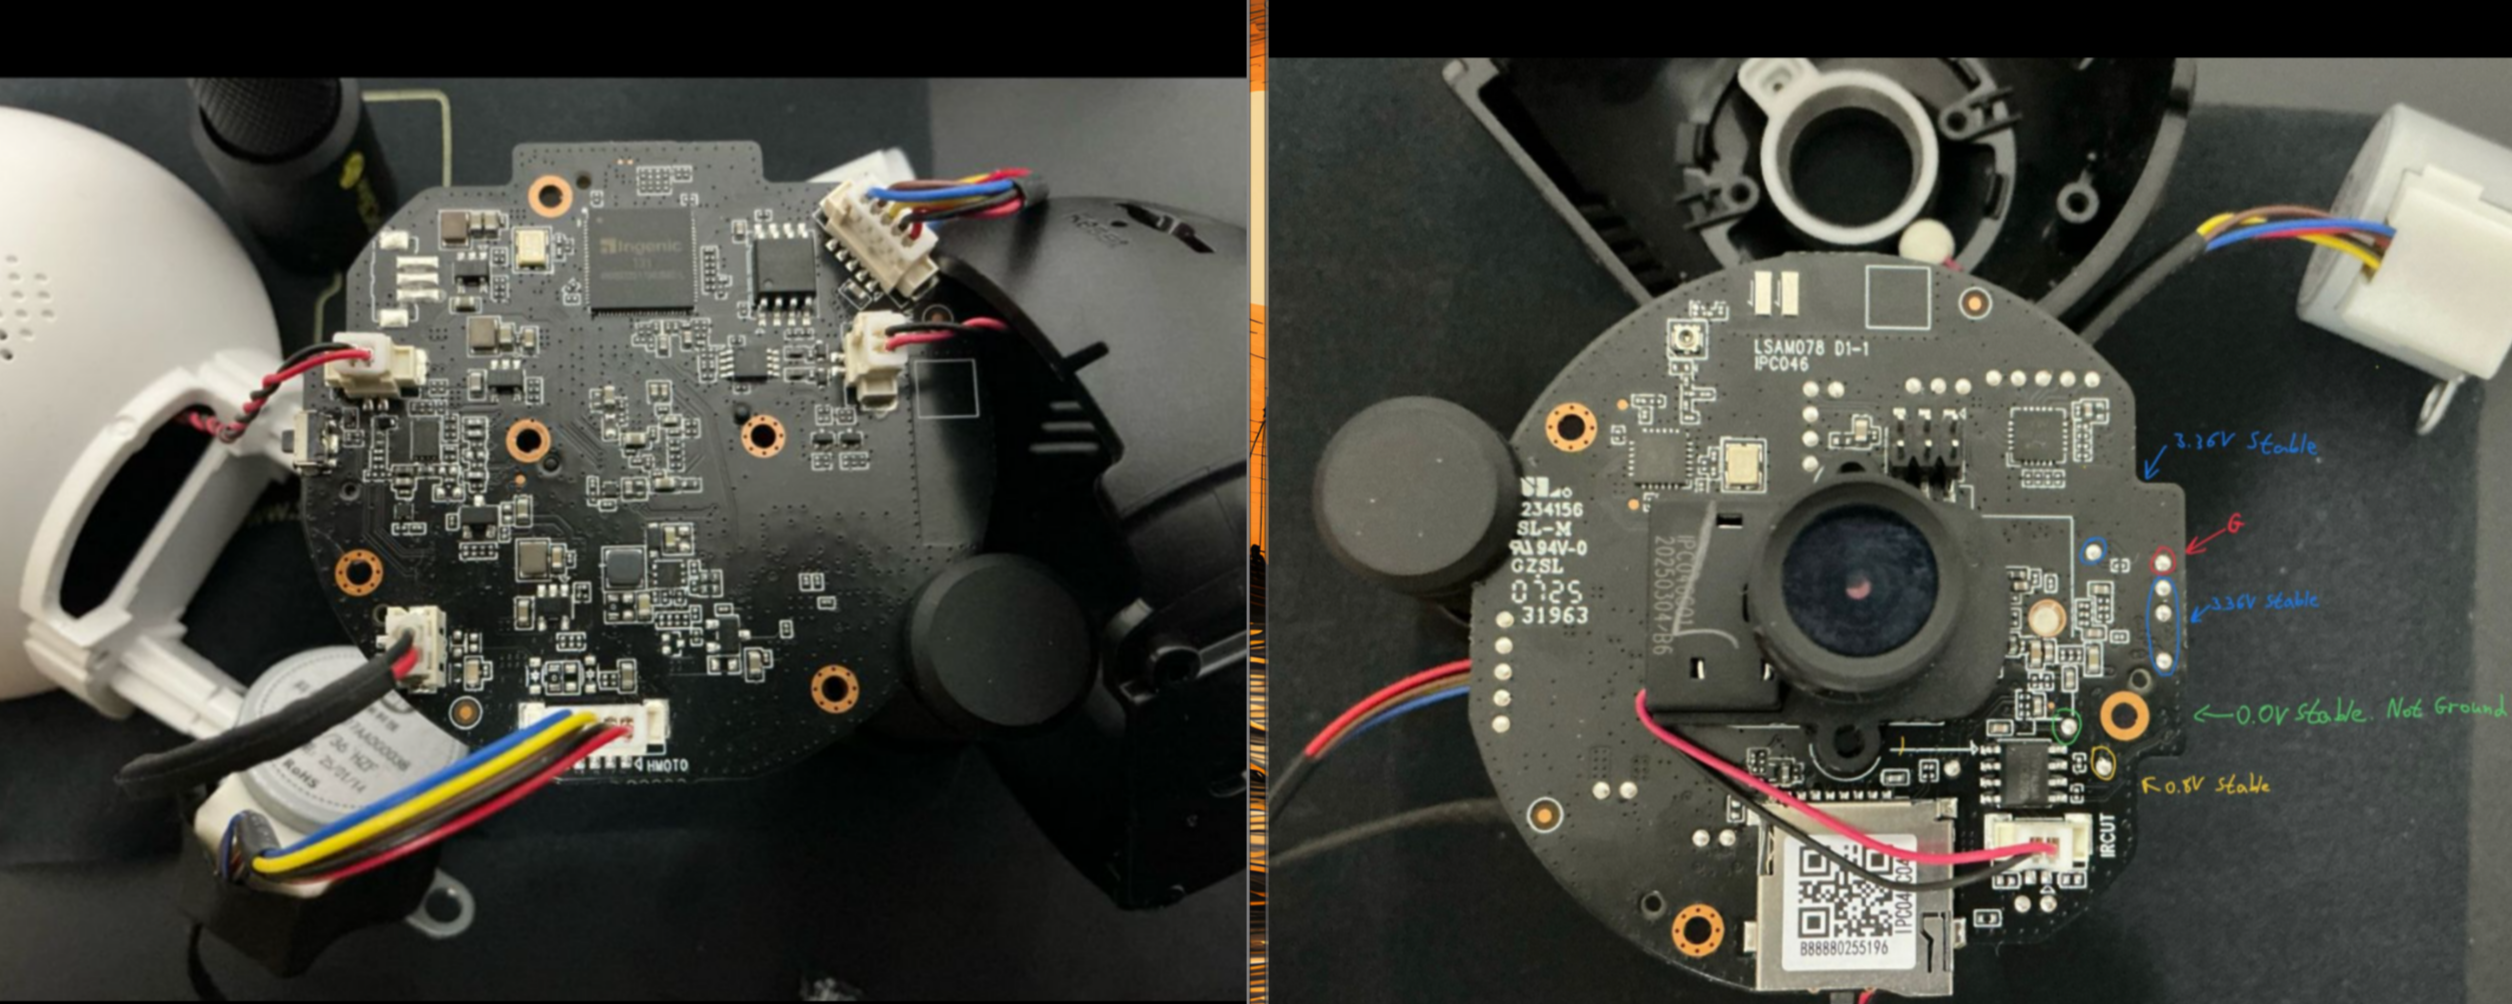
Xiaomi-C200-Firmware-Analysis
 h3xdum/xiaomi-c200-firmware-analysis
From UART to Root: Breaking Into the Xiaomi C200 via U-Boot
data-recoveryembedded-systems-securityexploitation+6
11
h3xdum/xiaomi-c200-firmware-analysisFrom UART to Root: Breaking Into the Xiaomi C200 via U-Boot
 nbs32k/localstranger
PoC for WinNotify, demonstrated through a driver mapper, and local privilege escalation.
 irsl/php-bypass-disable-functions
Demo project how to bypass the disable_functions security control of PHP on Linux
 trustedsec/titanis
Windows protocol library, including SMB and RPC implementations, among others.
 percivalll/dirty-frag-kubernetes-poc
Proof-of-concept demonstrating container escape on Amazon EKS by exploiting Dirty Frag (CVE-2026-43284) kernel page-cache corruption via shared image…
 nyan-x-cat/lime-rat
LimeRAT | Simple, yet powerful remote administration tool for Windows (RAT)
 thundergunexpress/badministration
Offensive tool for exploiting management applications (SolarWinds Orion, McAfee ePO) via non-technical vulnerabilities. Enables client enumeration,…
 blacksnufkin/byovd
BYOVD research use cases featuring vulnerable driver discovery and reverse engineering methodology. (CVE-2025-52915, CVE-2025-1055, CVE-2026-3609,…
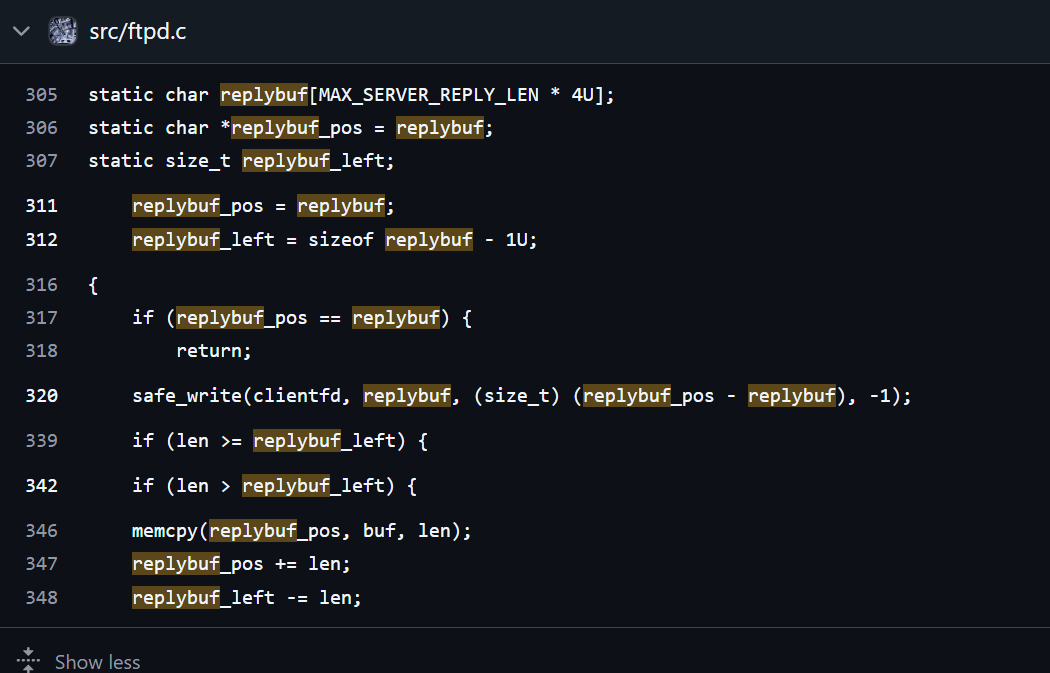 rohilchaudhry/cve-2024-48208
This repo contains all the work surrounding the development of the PoC for CVE-2024-48208, and how a simple OOB(Out-of-bound) read can result in jail…
 0x4d31/awesome-oscp
A curated list of awesome OSCP resources
 0ca/boxpwnr
A modular framework for benchmarking LLMs and agentic strategies on security challenges across HackTheBox, TryHackMe, PortSwigger Labs, Cybench,…
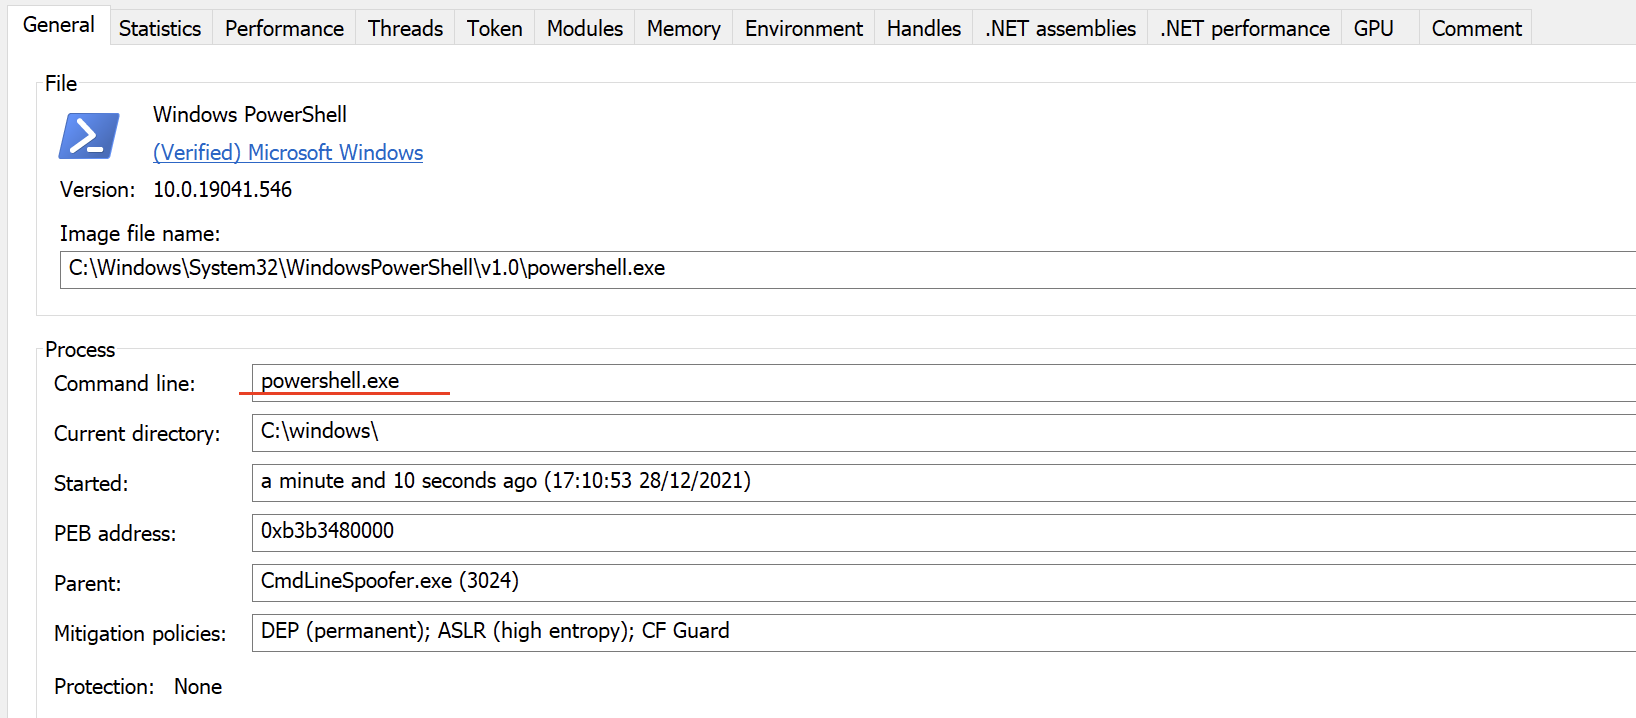 plackyhacker/cmdlinespoofer
How to spoof the command line when spawning a new process from C#.
 ally-petitt/cve-2024-48990-exploit
My exploit for CVE-2024-48990. Full details of how I made this are on my blog.
 fuzzlove/sparstanboogie
Exploit chain utilizing directory traversal and iOS restore to overwrite protected files.
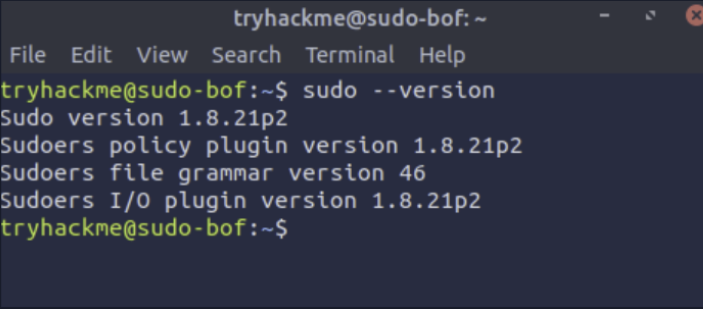 devteam6rabbit/cve-2019-18634-writeup
analysis of the sudo buffer overflow affect sudo version <1.8.26 and how to use GCC to compile publicly availible exploits
 foxglovesec/potato
Windows local privilege escalation exploit using NBNS spoofing, fake WPAD proxy, and HTTP-to-SMB NTLM relay to gain NT AUTHORITY\SYSTEM access.
 xm0kht4r/av-edr-killer
AV/EDR processes termination by exploiting a vulnerable driver (BYOVD)
 daem0nc0re/privfu
Kernel mode WinDbg extension and PoCs for token privilege investigation.