

TOP
 ghosttroops/top
TOP All bugbounty pentesting CVE-2023- POC Exp RCE example payload Things
curated-resourcesexploitationpenetration-testing+4
ghosttroops/topTOP All bugbounty pentesting CVE-2023- POC Exp RCE example payload Things
 chenaotian/cve-2022-0847
Proof-of-concept exploit and detailed analysis of CVE-2022-0847 (Dirty Pipe) Linux kernel privilege escalation vulnerability, including Docker…
 faisalfs10x/webmin-cve-2022-0824-revshell
Post-authentication reverse shell exploit for Webmin <=1.984 leveraging CVE-2022-0824 File Manager privilege escalation. Downloads and executes a CGI…
 shotokhan/cve_2022_0847_shellcode
Implementation of CVE-2022-0847 as a shellcode
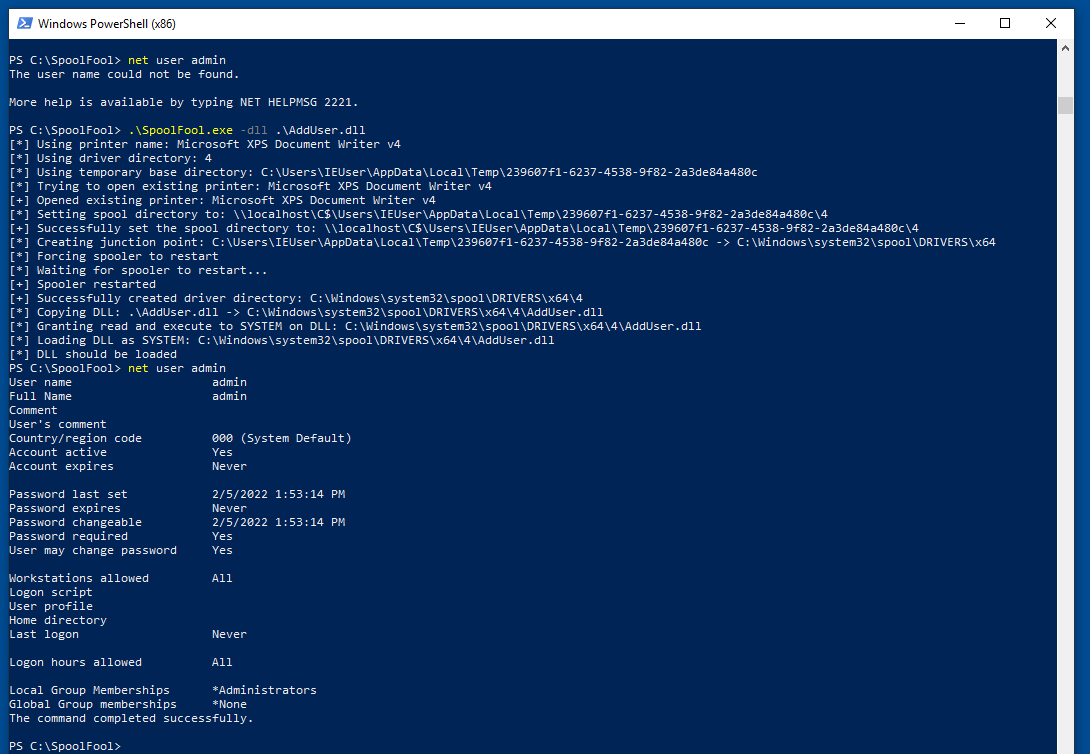 ly4k/spoolfool
Exploit for CVE-2022-21999 - Windows Print Spooler Elevation of Privilege Vulnerability (LPE)
 uname1able/cve-2022-24481
C++ exploit for CVE-2022-24481 targeting Windows 10/11 local privilege escalation via kernel vulnerability. Compiled with Visual Studio 2022 and…
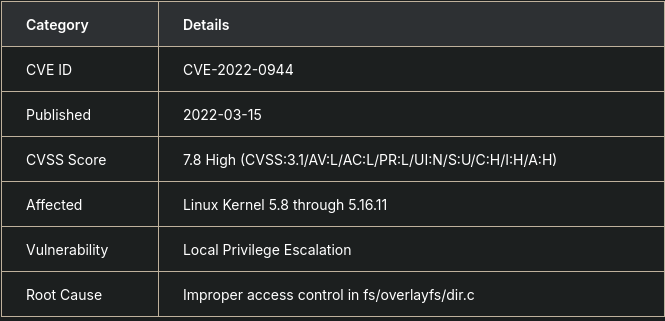 neoartemis37/overlayfs-privesc-cve-2022-0944
Educational exploit for CVE-2022-0944 OverlayFS privilege escalation with reverse shell payload delivery and kernel version detection scripts.
 eliasdekiniweek/cve-2022-26923
Exploitation de CVE-2022-26923
 d3ndr1t30x/cve-2022-37706
Privilege escaltion exploit script for Boardlight machine on HackTheBox. I had access as the Larissa user and ran this script from the /tmp…
 0xkol/badspin
Bad Spin: Android Binder Privilege Escalation Exploit (CVE-2022-20421)
 grisuno/cve-2022-22077
BYOVD exploitation framework for CVE-2022-22077 targeting RTCore64.sys. Demonstrates kernel token theft, privilege escalation to SYSTEM, and C2…
 vinukalana/dirtypipe-cve-2022-0847
This repository is developed to analysis and understand DirtyPipe exploit CVE-2022-0847
 vportal/cve-2022-22715
Exploit code for CVE-2022-22715 (Windows Dirty Pipe), a sandbox escape and privilege escalation via named pipe TOKEN object corruption, with a linked…
 crusaders-of-rust/cve-2022-0185
CVE-2022-0185
 bluedragonsecurity/linux-kernel-dirty-pipe-exploitation-logic-bug-
Exploiting CVE-2022-0847 - written by : Antonius (w1sdom)
 chenaotian/cve-2022-0185
CVE-2022-0185 POC and Docker and Analysis write up
 prabeershakya/cve-2022-0185-poc
Proof-of-concept exploit for CVE-2022-0185, a Linux kernel heap buffer overflow enabling local privilege escalation and container escape via FUSE and…
 sofianehamlaoui/cve-2022-0492-checker
A script to check if a container environment is vulnerable to container escapes via CVE-2022-0492