 chenaotian/cve-2022-0185
CVE-2022-0185 POC and Docker and Analysis write up

[toc]
Vulnerability ID: CVE-2022-0185
CVSS Score:
Affected Product: linux kernel - fsconfig syscall
Affected Versions: linux kernel 5.1-rc1 ~ 5.16.2
Exploitation Requirements: Linux local; requires CAP_SYS_ADMIN capability (can be obtained directly via unshare, effectively no restriction)
Impact: Local privilege escalation; container escape
Source Code: git clone git://kernel.ubuntu.com/ubuntu/ubuntu-focal.git -b Ubuntu-hwe-5.11-5.11.0-27.29_20.04.1 --depth 1
or https://mirrors.edge.kernel.org/pub/linux/kernel/v5.x/
5.X kernel compilation environment docker: chenaotian/kernelcompile
Vulnerability analysis docker: chenaotian/cve-2022-0185
Two kernels prepared: one distribution kernel and one self-compiled kernel
Install qemu, gdb, gdb-peda, etc.
Vulnerability-related files in /root/cve-2022-0185
boot_exp.sh for starting the exploit verification/debug environment, distribution 5.11.0-44 unsigned kernelboot_poc.sh for starting the poc verification environment, can crash the kernel but cannot run the exploit, self-compiled 5.13 signed kernelexp directory, exp source code (author: BitsByWill), directly compile exploit_fuseqemu environment: https://github.com/chenaotian/CVE-2022-0185/tree/main/qemuANDexp
Ubuntu 20.04 virtual machine exploit runtime environment using the original author's exp
Prepare an Ubuntu 20.04 virtual machine, then replace the kernel:```shell apt-get install linux-image-5.11.0-44-generic
grep menuentry /boot/grub/grub.cfg vim /etc/default/grub #修改 GRUB_DEFAULT 选项为上面结果中想要启动内核的下标 update-grub #如果不生效的话则直接进入/boot 目录将之前的内核相关文件(带之前内核编号的文件)全部删掉,然后启动时候报找不到内核,然后手动选择内核启动也可以
#编译exp make fuse ./exploit
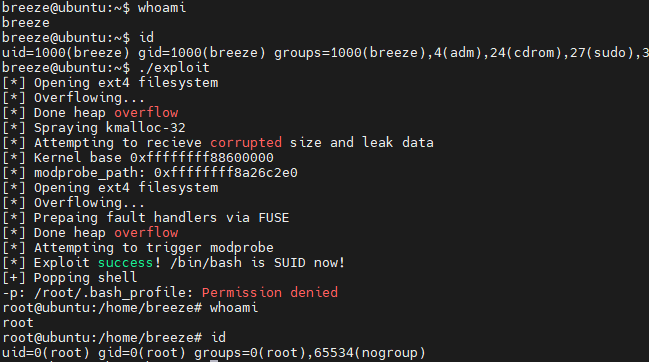
Privilege escalation effect
## Vulnerability principle
The system call where the vulnerability occurs is the `FSCONFIG_SET_STRING` operation option in `fsconfig`. This system call is used to configure an already opened filesystem context. **The prerequisite is the `CAP_SYS_ADMIN` capability**:
> The main purpose of `fsopen` is to create a filesystem context and associate it with a file descriptor, returning the file descriptor. After `fsopen`, `fsconfig` follows. From the literal meaning, it can be guessed that we created a filesystem context via `fsopen` above, and `fsconfig` below might be used to configure the content within the filesystem context. In fact, `fsconfig` is indeed mainly used for this configuration work. In addition to the filesystem context, it also supports other tasks.
### Vulnerability point
First, the vulnerability appears in the `legacy_parse_param` function:
linux-5.11\fs\fs_context.c : 502 : legacy_parse_param```c
static int legacy_parse_param(struct fs_context *fc, struct fs_parameter *param)
{
struct legacy_fs_context *ctx = fc->fs_private;
unsigned int size = ctx->data_size;
size_t len = 0;
··· ···
··· ···
switch (param->type) {
case fs_value_is_string:
len = 1 + param->size;
fallthrough;
··· ···
}
if (len > PAGE_SIZE - 2 - size) //此处边界检查有问题
return invalf(fc, "VFS: Legacy: Cumulative options too large");
if (strchr(param->key, ',') ||
(param->type == fs_value_is_string &&
memchr(param->string, ',', param->size)))
return invalf(fc, "VFS: Legacy: Option '%s' contained comma",
param->key);
if (!ctx->legacy_data) {
ctx->legacy_data = kmalloc(PAGE_SIZE, GFP_KERNEL); //在第一次时会分配一页大小
if (!ctx->legacy_data)
return -ENOMEM;
}
ctx->legacy_data[size++] = ',';
len = strlen(param->key);
memcpy(ctx->legacy_data + size, param->key, len);
size += len;
if (param->type == fs_value_is_string) {
ctx->legacy_data[size++] = '=';
memcpy(ctx->legacy_data + size, param->string, param->size); //拷贝,可能越界
size += param->size;
}
ctx->legacy_data[size] = '\0';
ctx->data_size = size;
ctx->param_type = LEGACY_FS_INDIVIDUAL_PARAMS;
return 0;
}
The key is the subsequent memcpy, which copies the param->string we passed into ctx->legacy_data. The check for out-of-bounds copy is the preceding (len > PAGE_SIZE - 2 - size) check. This check is flawed: the comparison type is size_t, i.e. unsigned int. If size > PAGE_SIZE - 2, an integer overflow and wrap-around will occur, resulting in len < PAGE_SIZE - 2 - size, thus passing the check. Then during the copy, size is greater than PAGE_SIZE - 2, causing an out-of-bounds copy.
Some data structures used:```c struct fs_context { const struct fs_context_operations ops; struct mutex uapi_mutex; / Userspace access mutex */ struct file_system_type *fs_type; void fs_private; / The filesystem's context */ void *sget_key; struct dentry root; / The root and superblock */ struct user_namespace user_ns; / The user namespace for this mount */ struct net net_ns; / The network namespace for this mount */ const struct cred cred; / The mounter's credentials / struct p_log log; / Logging buffer */ const char source; / The source name (eg. dev path) */ void security; / Linux S&M options / void s_fs_info; / Proposed s_fs_info / unsigned int sb_flags; / Proposed superblock flags (SB_) / unsigned int sb_flags_mask; / Superblock flags that were changed / unsigned int s_iflags; / OR'd with sb->s_iflags / unsigned int lsm_flags; / Information flags from the fs to the LSM / enum fs_context_purpose purpose:8; enum fs_context_phase phase:8; / The phase the context is in / bool need_free:1; / Need to call ops->free() / bool global:1; / Goes into &init_user_ns / bool oldapi:1; / Coming from mount(2) */ };
struct legacy_fs_context { char legacy_data; / Data page for legacy filesystems */ size_t data_size; enum legacy_fs_param param_type; };
struct fs_parameter { const char key; / Parameter name / enum fs_value_type type:8; / The type of value here */ union { char *string; void *blob; struct filename *name; struct file *file; }; size_t size; int dirfd; };
### Call Path
Below, we analyze the function call stack. First, the entry point is definitely the `fsconfig` system call:
linux-5.11\fs\fsopen.c : 314 : SYSCALL_DEFINE5(fsconfig,...```c
SYSCALL_DEFINE5(fsconfig,
int, fd,
unsigned int, cmd,
const char __user *, _key,
const void __user *, _value,
int, aux)
{
struct fs_context *fc;
struct fd f;
int ret;
int lookup_flags = 0;
struct fs_parameter param = {
.type = fs_value_is_undefined,
};
··· ···
f = fdget(fd);
if (!f.file)
return -EBADF;
ret = -EINVAL;
if (f.file->f_op != &fscontext_fops)
goto out_f;
fc = f.file->private_data; //设置fc
··· ···
switch (cmd) {
··· ···
case FSCONFIG_SET_STRING:
param.type = fs_value_is_string;
//初始化结构体中的联合体中的string成员为用户传入的字符串
param.string = strndup_user(_value, 256);
if (IS_ERR(param.string)) {
ret = PTR_ERR(param.string);
goto out_key;
}
param.size = strlen(param.string);//设置size
break;
··· ···
··· ···
}
ret = mutex_lock_interruptible(&fc->uapi_mutex);
if (ret == 0) {
ret = vfs_fsconfig_locked(fc, cmd, ¶m);
mutex_unlock(&fc->uapi_mutex);
}
