

MalDev
 captmag/maldev
Creation of multiple Malware tools consisting of evasion, enumeration and exploitation
anti-boteducationencryption-decryption-tools+9
captmag/maldevCreation of multiple Malware tools consisting of evasion, enumeration and exploitation
 jm33-m0/emp3r0r
Linux post-exploitation C2 framework with gossip mesh networking, memory-only operations, modular payloads, and OPSEC-focused transport for red team…
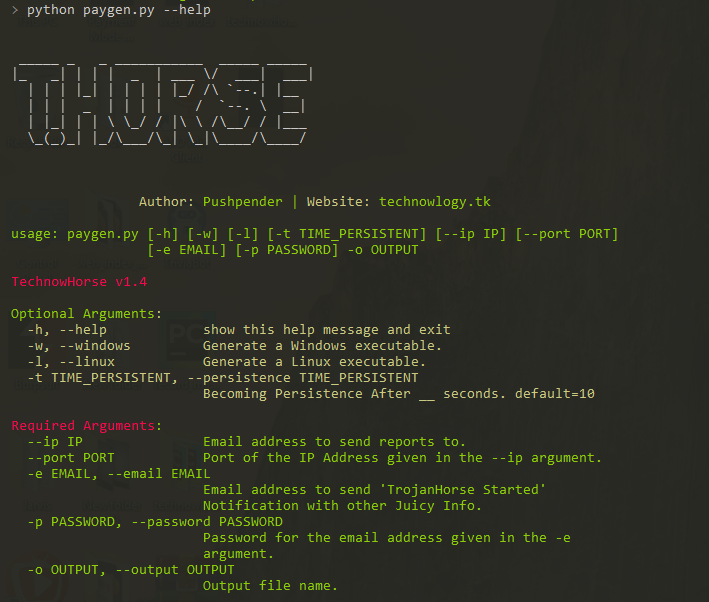 pushpenderindia/thorse
THorse is a RAT (Remote Administrator Trojan) Generator for Windows/Linux systems written in Python 3.
 twosevenonet/edr-redir
Redirects EDR working folders using a Bind Filter (bindflt.sys) to bypass endpoint detection, corrupt EDR services, or replace with…
 rek7/postshell
PostShell - Post Exploitation Bind/Backconnect Shell
 duhirsch/moveedr
Permanently disable EDRs as local admin
 eshlomo1/cloudsec
Master the art of cloud exploitation. A specialized resource for offensive security researchers and red teamers focused on weaponizing…

 rek7/ddoor
DDoor - cross platform backdoor using dns txt records
 kiexitdispatcher/goredops
🦫 | GoRedOps is a repository dedicated to gathering and sharing advanced techniques and offensive malware for Red Team, with a specific focus on…
 shadow1ng/fscan
一款内网综合扫描工具,方便一键自动化、全方位漏扫扫描。(An intranet comprehensive scanning tool, enabling one-click automated, all-round vulnerability scanning)
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 spellshift/realm
Cross-platform adversary emulation framework with a Rust implant, GraphQL teamserver, and Eldritch DSL for automated, scalable red team operations…
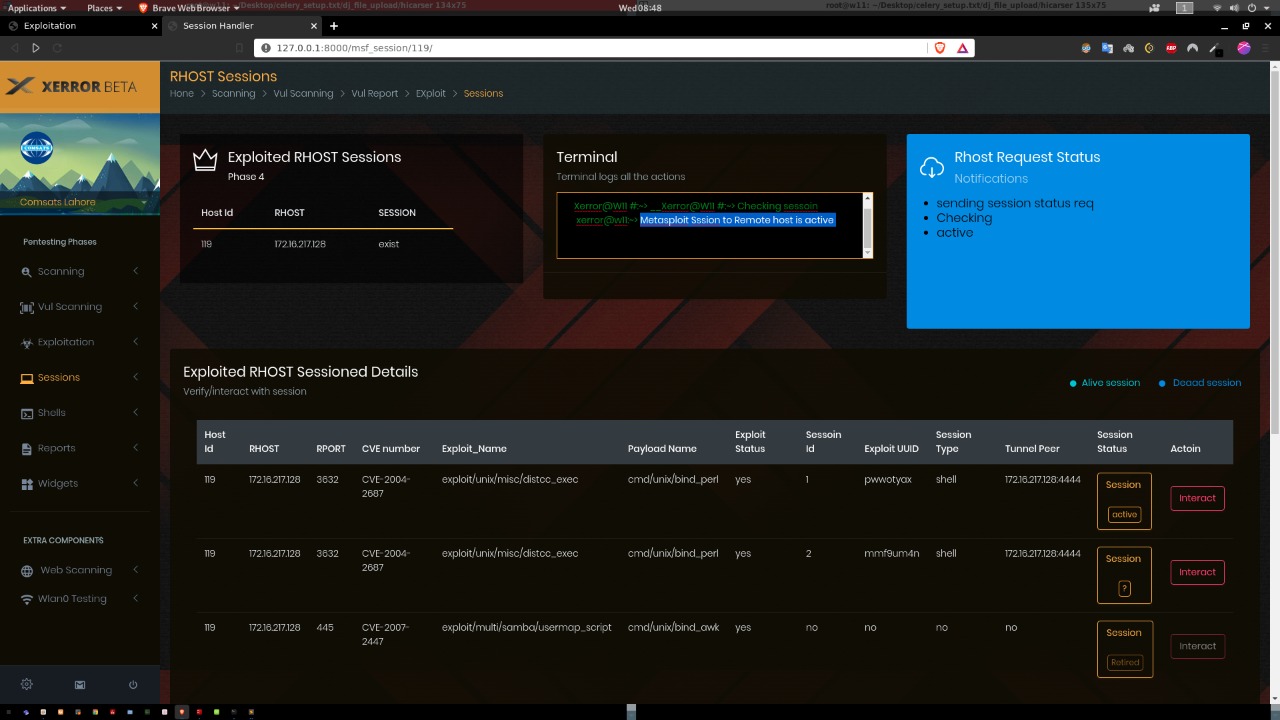 chudry/xerror
fully automated pentesting tool
 jonaslejon/ad-autopwn
Automated Active Directory attack chain from zero-auth to Domain Admin. Chains 25+ techniques including Kerberoast, AD CS ESC1-16, Shadow…
 jymcheong/autottp
Automated Tactics Techniques & Procedures
 nccgroup/chuckle
An automated SMB relay exploitation script.