

SyscallRevenant
 silentisvox/syscallrevenant
Clean Indirect Syscalls with Syscall Tampering.
binary-exploitationexploitationids-ips-evasion+6
1
silentisvox/syscallrevenantClean Indirect Syscalls with Syscall Tampering.
 asdfugil/haxx
Untethered + Unsandboxed code execution haxx as root on iOS 14 - iOS 14.8.1.
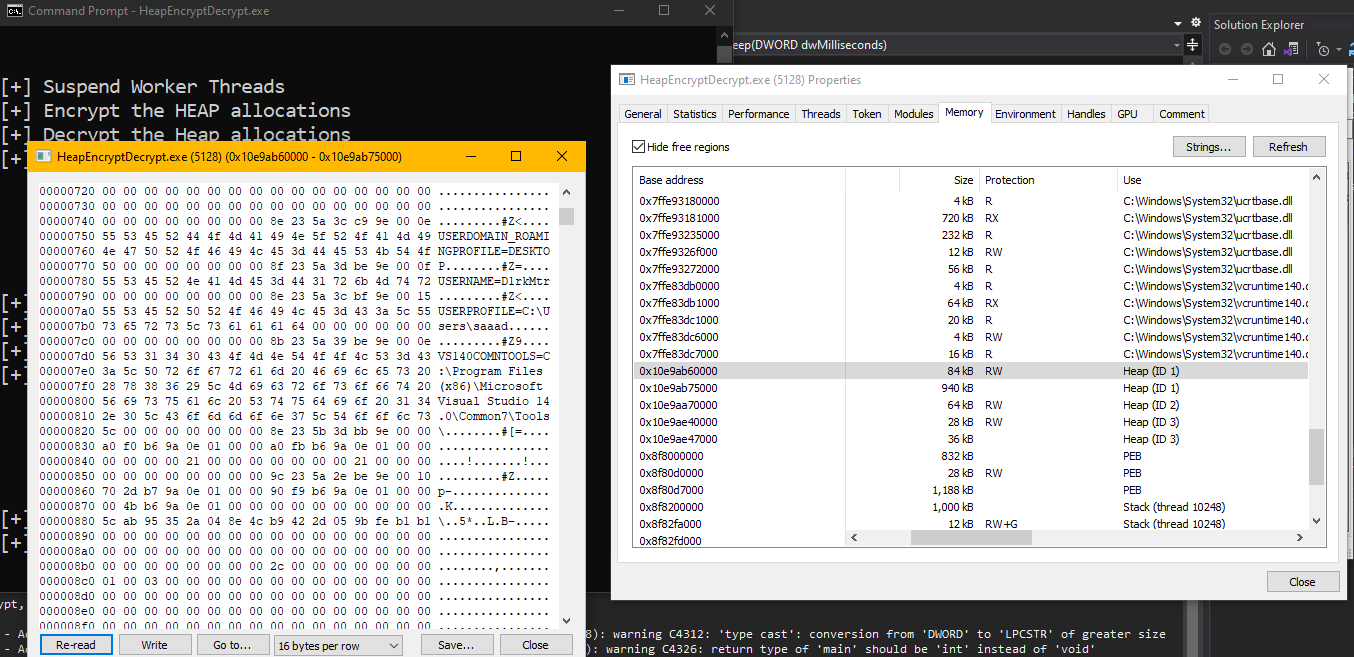 saadahla/heapcrypt
Encypting the Heap while sleeping by hooking and modifying Sleep with our own sleep that encrypts the heap
 byt3bl33d3r/offensivenim
My experiments in weaponizing Nim (https://nim-lang.org/)
 trickster0/offensiverust
Rust Weaponization for Red Team Engagements.
 bignerd95/chimay-red
Working POC of Mikrotik exploit from Vault 7 CIA Leaks
 egebalci/amber
Reflective PE packer.
 secretsquirrel/bdfproxy
Patch Binaries via MITM: BackdoorFactory + mitmProxy.
 cryptogenic/ps5-ipv6-kernel-exploit
An experimental webkit-based kernel exploit (Arb. R/W) for the PS5 on <= 4.51FW
 0x00pf/0x00sec_code
Educational repository of offensive security source code: remote shells, ELF injectors, crypters, memory injection, and droppers for Linux,…
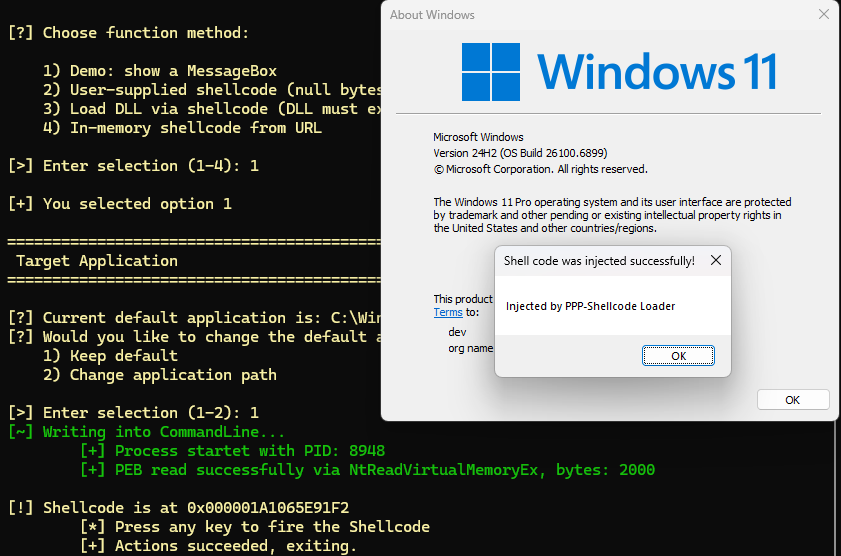 orange-cyberdefense/p3-loader
P³-Shellcode Loader is a loader that implements a code injection technique which leverages the Process Parameters structure as an execution and…
 itm4n/pentest-windows
Collection of Windows internals research and exploitation techniques covering privilege escalation, token abuse, and post-exploitation tricks for red…
 jgoyd/ios-attack-chain-cve-2025-31200-cve-2025-31201
CVE-2025-31200 is a zero-day, zero-click RCE in iOS CoreAudio’s AudioConverterService, triggered by a malicious audio file via iMessage/SMS.…
 ntdallas/bof_executeassembly
Beacon Object File for Cobalt Strike that executes .NET assemblies in beacon with evasion techniques.
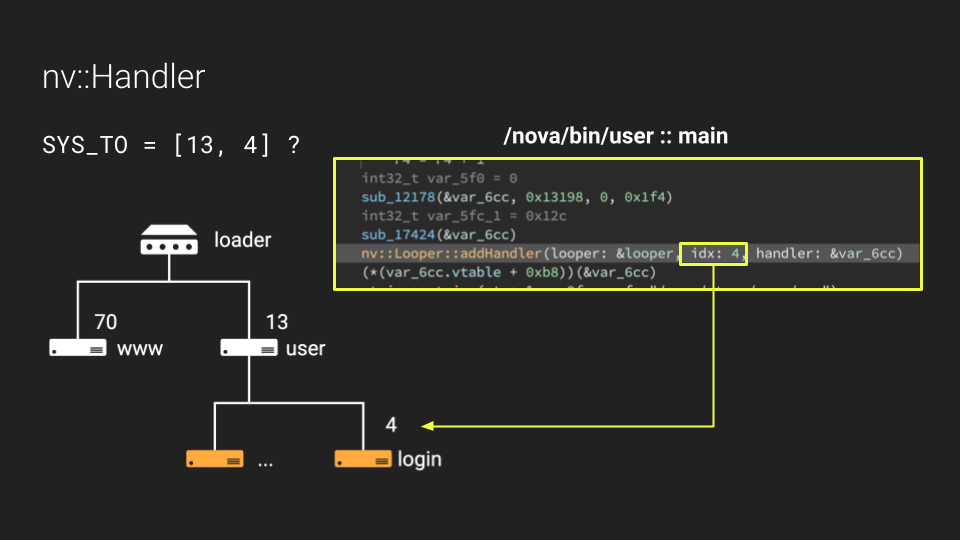 marginresearch/foisted
MikroTik remote jailbreak for v6.x.x
 pard0p/remote-bof-runner
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
 karkas66/lacuna-rs
Rust crate for ghost-frame call-stack spoofing, runtime indirect syscalls, and APC injection on Windows x64. Provides SSN resolution, JIT stub…
 kpwn/ps4-5.05-kernel-exploit
A fully implemented kernel exploit for the PS4 on 5.05FW