
AirBorne-PoC
 ekomssavior/airborne-poc
poc for CVE-2025-24252 & CVE-2025-24132
binary-exploitationcommand-and-controlexploitation+6
16410 months ago
ekomssavior/airborne-pocpoc for CVE-2025-24252 & CVE-2025-24132
 tijme/amd-ryzen-master-driver-v17-exploit
Cobalt Strike (CS) Beacon Object File (BOF) for kernel exploitation using AMD's Ryzen Master Driver (version 17).
 s3n4t0r-0x0/rustywater-shellcode-dropper
RustyWater represents the main payload and the backbone of the entire adversarial operation in Static Kitten group attacks.
 iilegacyyii/datainject-bof
Hijacks code execution via overwriting Control Flow Guard pointers in combase.dll
 ustayready/wnfexec
WNF Code Execution Library Using C#
 silentisvox/syscallrevenant
Clean Indirect Syscalls with Syscall Tampering.
 sgkdev/page_inject
CVE-2026-31431-killed page-cache exploit — code exec into containers sharing the same image layer
 rsmudge/cve-2020-0796-bof
Cobalt Strike Beacon Object File implementing CVE-2020-0796 SMBGhost local privilege escalation with dual weaponization paths for token theft and…
 klezvirus/koppeling-p
Adaptive DLL hijacking / dynamic export forwarding - EAT preserve
 sgkdev/ipv6_frag_escape
Linux LPE - Reliable Jail/Container Escape
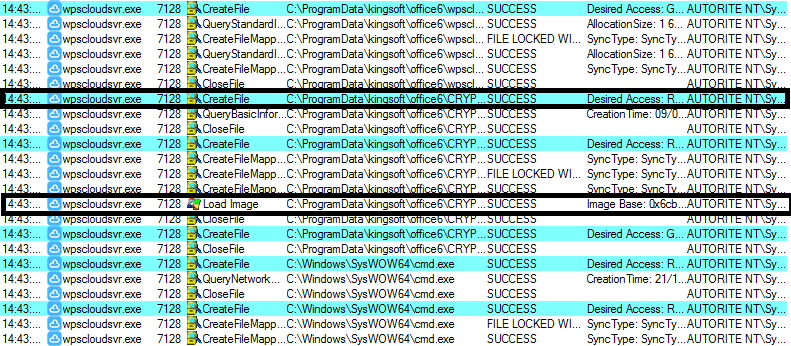 hadimed/kingsoft-wps-office-lpe
CVE-2022-25943
 thoxy67/zig-pe
Reflective PE loader written in Zig. Loads and executes native and .NET PE files directly from memory.
 blacksnufkin/axhunter
PoCs for Wellbia XIGNCODE3 anti-cheat xhunter driver family - xhunter1.sys v2023.12.7.78 and xhunter2.sys v2026.6.1.192 (CVE-2026-15430,…
 carsonchan12345/cve-2024-37726-msi-center-local-privilege-escalation
Proof-of-concept for CVE-2024-37726: local privilege escalation in MSI Center via arbitrary file overwrite using symlink/junction attacks and OpLock…
 jymcheong/injection
Windows process injection methods
 neofito/cve-2020-1337
CVE-2020-1048 bypass: binary planting PoC
 ycdxsb/cve-2020-0668
Make CVE-2020-0668 exploit work for version < win10 v1903 and version >= win10 v1903
 paradoxis/cve-2026-57239
Proof of concept exploit for CVE-2026-3775/CVE-2026-3780 and CVE-2026-57239 which lets you obtain NT AUTHORITY\SYSTEM rights via the Foxit PDF Reader…